
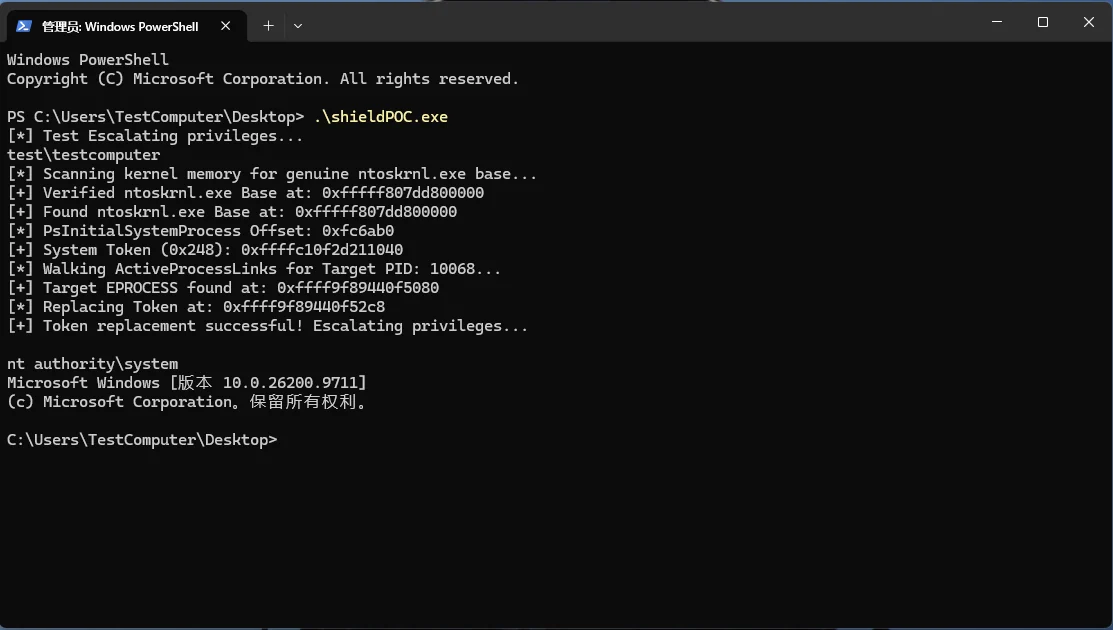
CVE-2026-120232
 element2023h/cve-2026-120232
Proof-of-concept for a local privilege escalation in Horizon DataSys Reboot Restore Standard shield.sys, exploiting an unvalidated IOCTL to gain…
binary-exploitationexploitationprivilege-escalation+2
2
element2023h/cve-2026-120232Proof-of-concept for a local privilege escalation in Horizon DataSys Reboot Restore Standard shield.sys, exploiting an unvalidated IOCTL to gain…
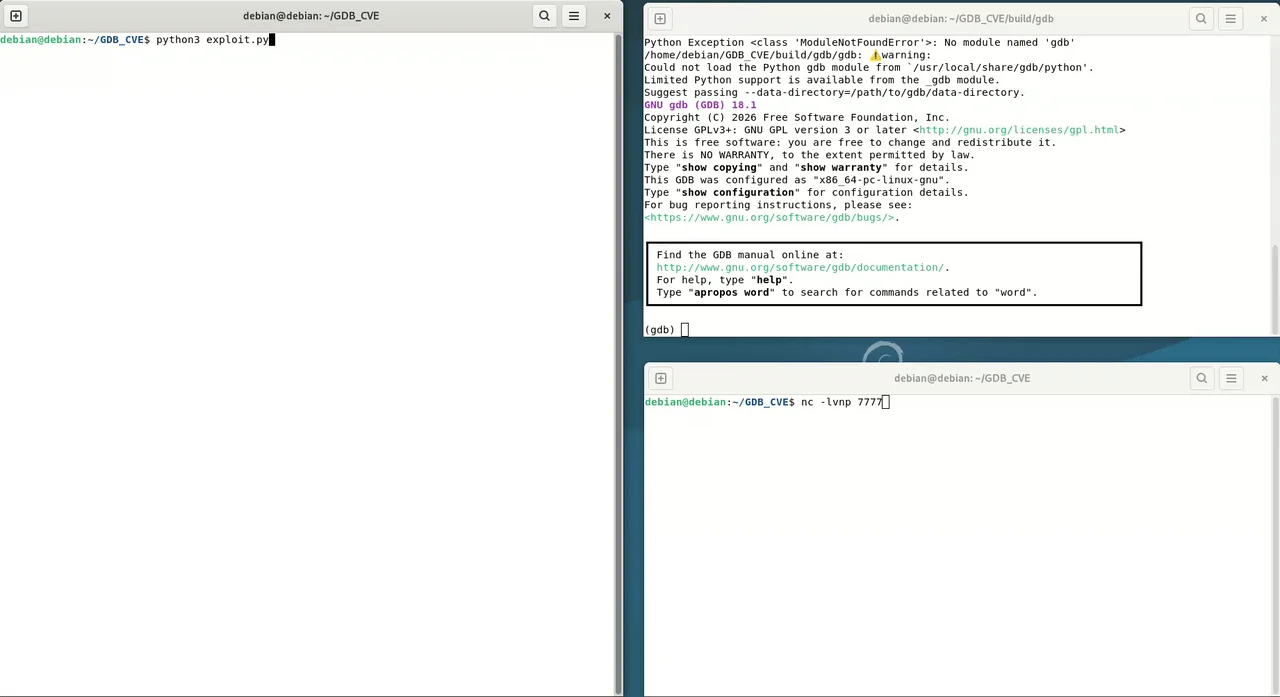 deebumg/cve-2026-121994-poc
Weaponized proof-of-concept for CVE-2026-121994: a fake GDB remote debug stub that sends a malicious p-packet to trigger memory corruption and a…
 zeetee1235/cve-2026-126497
Proof-of-concept and analysis for CVE-2026-126497, a heap out-of-bounds write in LibreCAD/libdxfrw R2004 DWG section-page parsing, with ASan…
 googlesky/cve-2026-129351
Reproduces CVE-2026-129351, a pre-auth out-of-bounds write in TRENDnet TEW-657BRM mini_httpd, running the hash-verified MIPS firmware under qemu with…
 googlesky/cve-2026-129352
TRENDnet TEW-657BRM 1.00.1 upgrade_flash.cgi: strncpy of the multipart first line into a 128-byte frame buffer (ra +192), delimiter unchecked ->…
 googlesky/cve-2026-129353
Proof-of-concept and QEMU-mipsel lab for CVE-2026-129353, a pre-auth stack overflow in D-Link DIR-600L authentication.cgi, with crash and saved-RA…
 googlesky/cve-2026-129354
Reproduction lab and PoC for CVE-2026-129354, a pre-auth stack overflow in D-Link DIR-600L HNAP hnap_main via the SOAPAction header, with qemu-mipsel…
 themalwareguardian/cve-2026-13043
Proof-of-concept for CVE-2026-13043: bypasses the Panda/WatchGuard pskmad.sys authentication handshake to reach privileged IOCTLs for MSR reads and…
 googlesky/cve-2026-131873
Proof-of-concept and exploit for CVE-2026-131873, a stack buffer overflow in Gargoyle's Plus interpreter ReadAction(), with an ASan/UBSan…
 nuf1p/loaderville
A collection of initial access loaders to use inside enterprise hardened enviroments
 wantenmn/cve-2026-98260-adb
ADB/Termux runner for a CVE-2026-98260 Android kernel UAF exploit: KASLR calibration, fake cred injection, root verification, and optional KernelSU…
 alt3kx/cve-2026-114938
Proof-of-concept and lab tooling for CVE-2026-114938 (Java4Shell), an OpenJDK HotSpot Base64 intrinsic heap overflow, with remote trigger, heap…
 blkph0x/cve-2026-109619-zendpipelinelab
PHP CVE-2026-109619 stale session state: calibrated mod_php lab reproduction, evidence, and solver
 al123xiaaaa/cve-2026-98260-gt7pro-rmx5010
真我 GT7 Pro (RMX5010) 免解BL临时Root · CVE-2026-98260 机型适配 · KernelSU 晚加载 · Temporary root for realme GT7 Pro without bootloader unlock
 googlesky/cve-2026-114550
Podman lab and PoC reproducing the libwebsockets MQTT PUBACK out-of-bounds write (ZDI-CAN-31039), with a malicious broker, ASan test matrix, and heap…
 hidra0x/hidra
Research jailbreak project for A12 iOS 18.7.2 devices, chaining the AppleJPEGDriver UAF (CVE-2026-20687) toward a kernel read/write primitive. No…
 syrex1013/cve-2026-2031226
Proof-of-concept exploits for a PHP Fiber callable use-after-free (CVE-2026-2031226) enabling heap reclaim, type confusion, info leak, and…
 cracked5pider/ldrlibraryex
A small x64 library to load dll's into memory.