
CTFs
 adamkadaban/ctfs
CTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
binary-exploitationcryptographyctf+9
85210 months ago
adamkadaban/ctfsCTF Cheat Sheet + Writeups / Files for some of the Security CTFs that I've done
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 hanakim3945/bl_sbx
itunesstored & bookassetd sbx escape
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
 ioallocate/immapper
Demonstration of Abusing the Vulnerable driver AmdTools64.sys for Physical R/W.
 zznop/sploit
Go package that aids in binary analysis and exploitation
 liznzn/cve-2019-2215
Temproot for Bravia TV via CVE-2019-2215.
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 io12/pwninit
Automates setup of binary exploitation challenges by patching ELF binaries, fetching matching linkers, unstripping libc, and generating pwntools…
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 heathen42/ctf
Curated collection of CTF challenge solutions covering binary exploitation, reverse engineering, and system security with detailed write-ups.
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 impost0r/rie
Kernel exploit for CVE-2026-43724 targeting Apple macOS/iOS systems. Provides proof-of-concept code for the disclosed vulnerability.
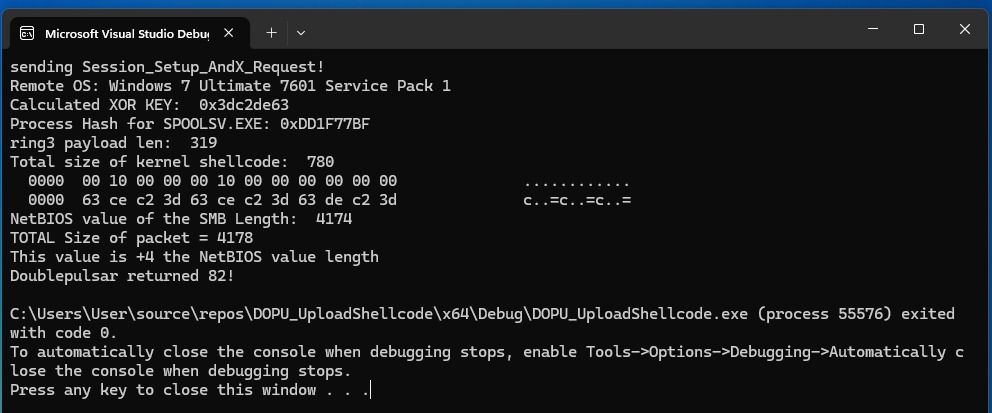 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…