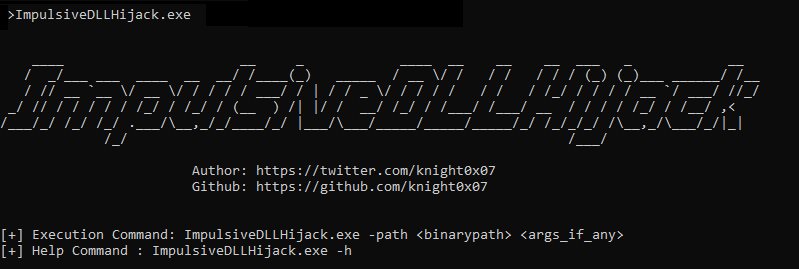

ImpulsiveDLLHijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
binary-exploitationexploitationpersistence-mechanisms+2
555
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

Educational lab environment for CVE-2021-3156 (Baron Samedit) with a Dockerized vulnerable sudo target, exploit scaffold, canary test, root-cause…

Modified .NET deserialization payload for CVE-2021-42321, based on ysoserial.net, that writes files and bypasses Windows Defender to target Microsoft…