
Archived
ghostlock-apk
 oopnv70-lab/ghostlock-apk
独立 APK:CVE-2026-43499 GhostLock 提权 + Shizuku shell 身份执行
android-securitybinary-exploitationexploitation+3
8
oopnv70-lab/ghostlock-apk独立 APK:CVE-2026-43499 GhostLock 提权 + Shizuku shell 身份执行
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 oopnv70-lab/ghostlock-aak-apk
GhostLock AAK Launcher - CVE-2026-43499 Linux kernel rtmutex stack UAF local privilege escalation trigger (GPLv3)
 satheesh575555/linux-4.19.72_cve-2023-0386
Kernel exploit for CVE-2023-0386, a Linux kernel privilege escalation vulnerability, providing a proof-of-concept for security research and testing.
 v4bel/dirtyfrag
Linux kernel privilege escalation exploit chaining two page-cache write vulnerabilities (CVE-2026-43284, CVE-2026-43500) for deterministic root…
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
Android kernel root exploit for iQOO Neo9 (CVE-2025-21479, Adreno GPU SDS) providing arbitrary physical write, kernel cap bypass, and root daemon/su…
 google/kernel-research
Linux kernel exploitation toolkit providing an exploit-building library, ROP chain and stack pivot generators, kernel image runners, and a target…
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 aureliusivan/ubl-itel-s23
Unlock Bootloader for Itel S23 (S665L) / Unisoc T606 using CVE-2022-38694
 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader
 xiaobailovesstirring/ghostlock-k419-adapter
GhostLock (CVE-2026-43499) adapter for 4.19.152-perf+ Android kernel
 cuteaplane/ghostlock-for-oneplus15t
(CVE-2026-43499)内核漏洞利用程序,适用于未解锁 Bootloader 的一加15T.
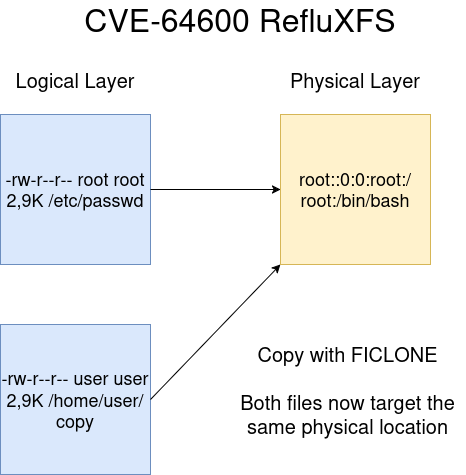 litosmartin/cve-2026-64600-refluxfs-poc
A POC for the recently discovered Qualys bug on COW with XFS
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 zznop/sploit
Go package that aids in binary analysis and exploitation