hazel-cve-2026-43499

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…

Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…

Local privilege escalation exploit targeting a Linux kernel io_uring AF_VSOCK reference-count bug, using page-cache manipulation to overwrite…

Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…

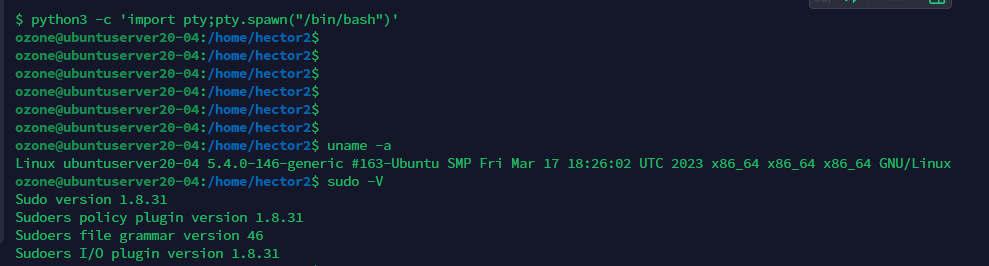
Exploit for Ubuntu 20.04 using CVE-2021-3156 enhanced with post-exploitation scripts

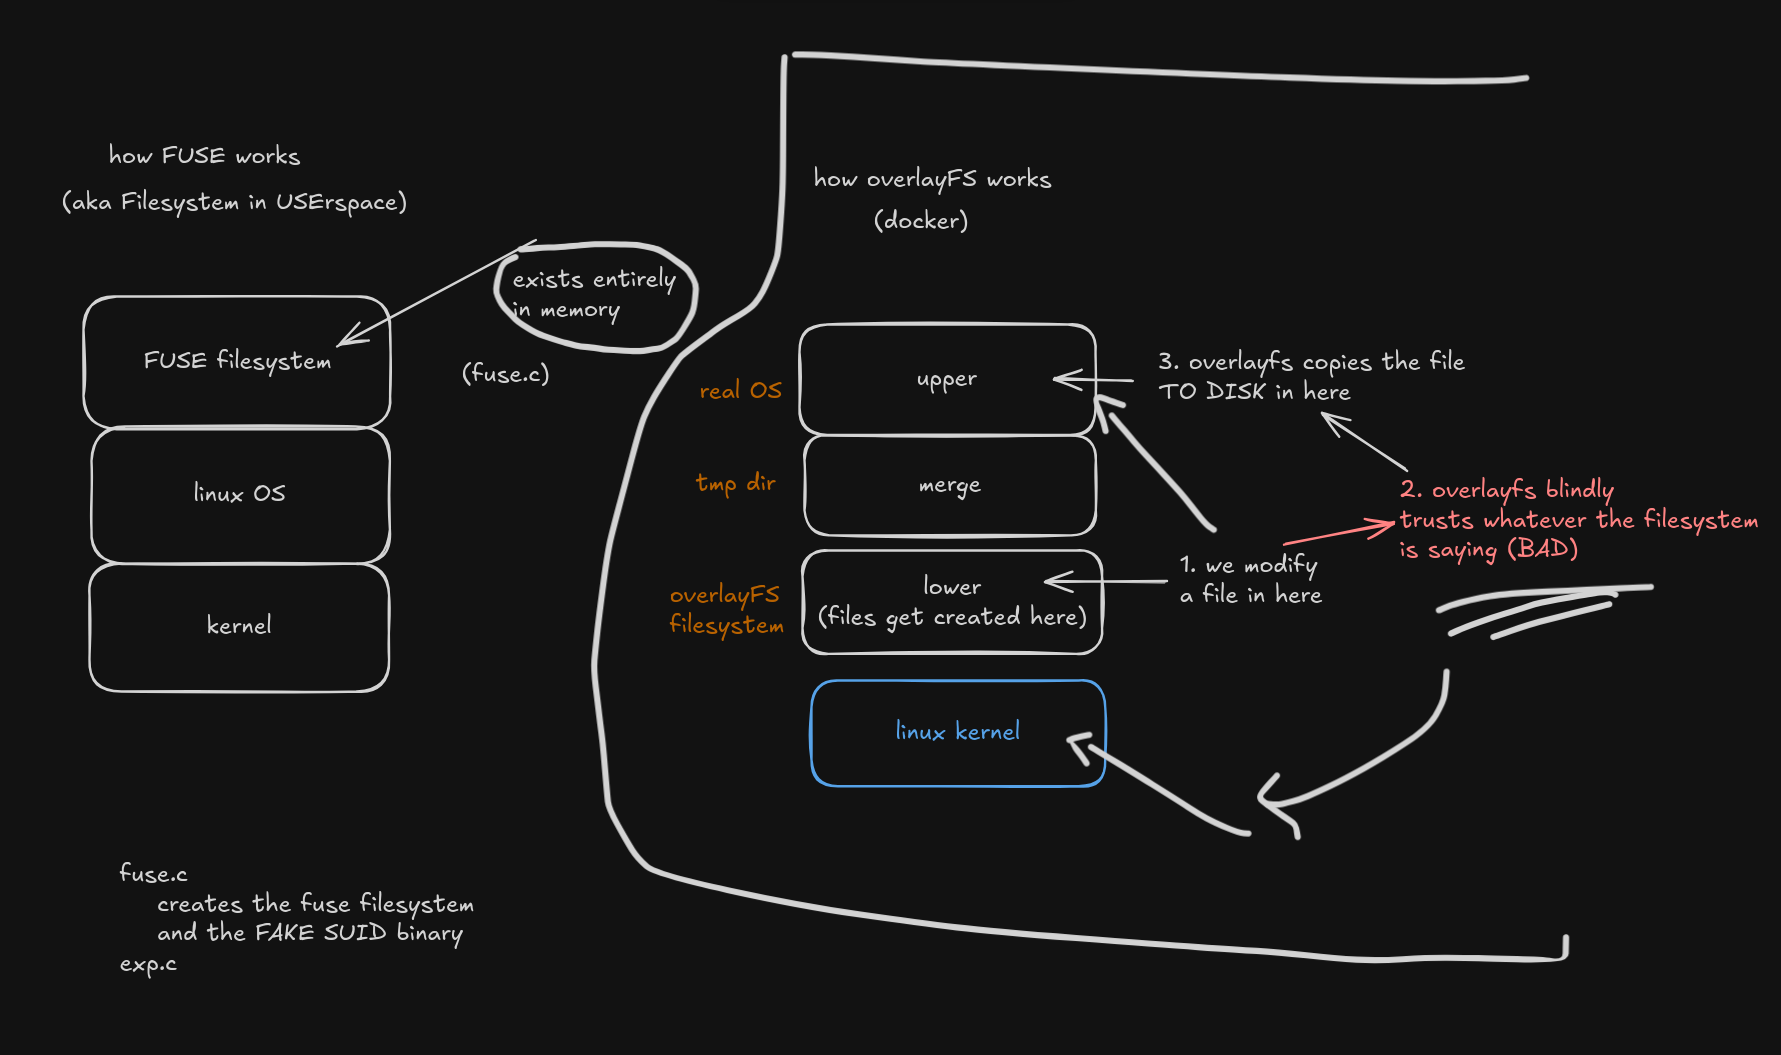
Copy fake in-memory files to disk using overlayFS

Local privilege escalation exploit for CVE-2025-6019 using crafted XFS filesystem images to gain root shell access on Linux systems.

Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…

Weaponized local privilege escalation exploit for CVE-2026-7867 in udisks2, using as-user mount spoofing to bypass PolicyKit and gain a root shell.

Python proof-of-concept for CVE-2026-43503 Linux kernel local privilege escalation via page-cache corruption using cloned socket buffers. Overwrites…

Using CVE-2022-0847, "Dirty Pipe Exploit", to pop a reverse bash shell for arbitrary code execution on a foreign machine.