
Archived
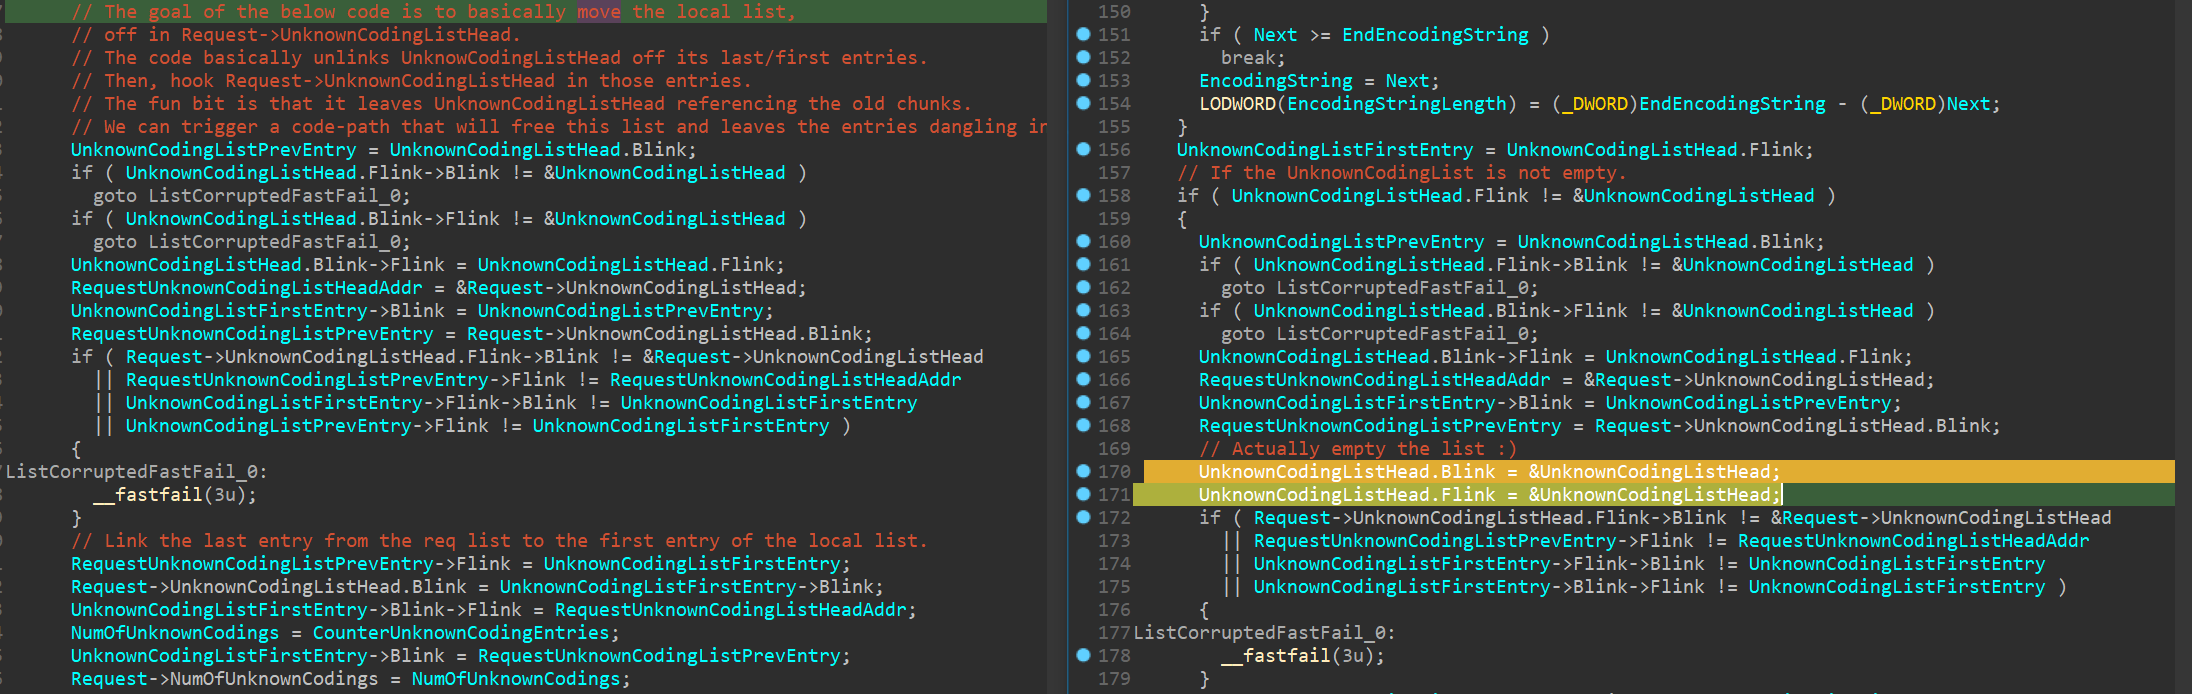
CVE-2021-31166
 0vercl0k/cve-2021-31166
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
binary-exploitationexploitationremote-access-tool+2
0vercl0k/cve-2021-31166Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
 luel-4013/misfortune-cookie
Interactive PoC suite for CVE-2014-9222 (Misfortune Cookie) and related router exploits, featuring detection, auth bypass, DoS, and RCE modules with…
 badmonkey7/cve-2021-34730
Cisco RV110w UPnP stack overflow
 orangetw/my-presentation-slides
Collections of Orange Tsai's public presentation slides.
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 12lie20/cve-2026-23918-test
This repository contains a Proof of Concept (PoC) demonstrating the Double Free vulnerability (CVE-2026-23918) in Apache HTTP Server 2.4.66…
 chamsbouzaiene/ai-vuln-rediscovery-nginx-cve-2026-42945
Reproducible AI-assisted vulnerability rediscovery of CVE-2026-42945 in nginx, including technical analysis, PoC trigger, and patch validation for…
 3nou9h/cve-2026-9256-poc
Demonstrates CVE-2026-9256 heap buffer overflow in nginx's ngx_http_rewrite_module with PoC scripts for heap/libc leaks and worker crash.
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 jelasin/cve-2026-42533
Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 liaoziqi-gzfls/cve-2026-42945
CVE-2026-42945 Nginx Rift
 aratane/cve-2026-42945
A flaw was found in NGINX, specifically within the ngx_http_rewrite_module. An unauthenticated attacker can exploit this vulnerability by sending…
 themalwareguardian/cve-2020-13768
Stack-based buffer overflow in MiniShare 1.4.1 reachable through a single HTTP PUT request.
 spiralbl0ck/iot_hacking_camera_0day
Iot Camera 0day
 themalwareguardian/cve-2002-1120
Classic stack-based buffer overflow in Savant Web Server 3.1 demonstrating early-2000s remote memory corruption through a crafted HTTP request.
 fzbacon/cve-2023-25234_tenda_ac6_stack_overflow
Proof-of-concept exploit for CVE-2023-25234, a stack overflow vulnerability in Tenda AC6 routers, enabling remote code execution via crafted HTTP…
 str0ng4le/cve-2022-30114
Proof-of-concept exploit for CVE-2022-30114, a heap-based buffer overflow in Fastweb FastGate routers. Sends a crafted HTTP Authorization header to…