
log4j2-rce
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
binary-exploitationexploitationpayload-development+2
39
hypnguyen1209/log4j2-rcePre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
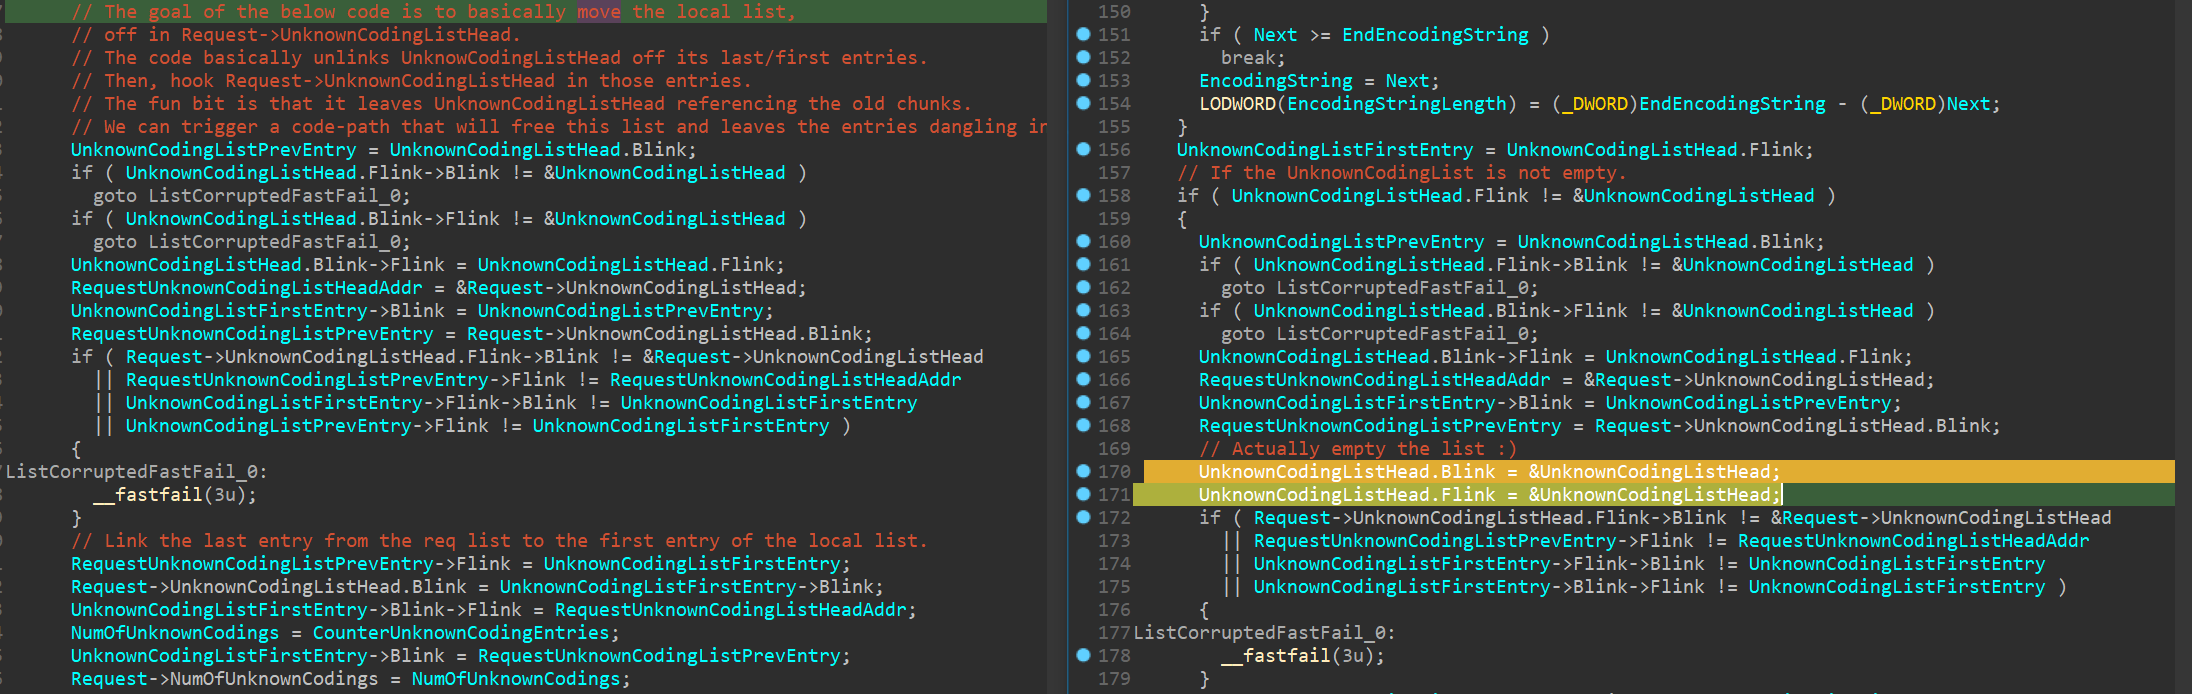 0vercl0k/cve-2021-31166
Proof of concept for CVE-2021-31166, a remote HTTP.sys use-after-free triggered remotely.
 06-ux/cve-2026-9256-poc
CVE-2026-9256 Nginx heap buffer overflow POC
 ignis-sec/cve-2025-6218
Proof-of-concept exploit for WinRAR path traversal vulnerability (CVE-2025-6218) enabling remote code execution via crafted archive files. Includes…
 actorexpose/cve-2017-11882
Exploit code targeting CVE-2017-11882, a Microsoft Office Equation Editor remote code execution vulnerability.
 opa334/darksword-kexploit
iOS <=26.0.1 DarkSword Kernel Exploit reimplemented in Objective-C
 brahmstaedt/libxml2-exploit
An example exploit for CVE-2017-7376
 jonpichel/cve-2017-7358
Proof-of-concept exploit for CVE-2017-7358, demonstrating a specific vulnerability in a software application. Intended for security research and…
 0xjohnnydev/webkit-uaf-angle-oob-analysis
Analysis of CVE-2025-43529 (WebKit UAF) + CVE-2025-14174 (ANGLE OOB) exploit chain - iOS Safari
 matlink/evince-cve-2017-1000083
Exploit for CVE-2017-1000083 targeting Evince document viewer. Provides a proof-of-concept for binary exploitation via crafted documents.
 danghvu/nginx-1.4.0
For the analysis of CVE-2013-2028
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 qassam-315/pan-os-user-id-buffer-overflow-poc
A research-grade Proof-of-Concept (PoC) for CVE-2026-0300, targeting the Buffer Overflow vulnerability in Palo Alto Networks PAN-OS User-ID™…
 jsherman212/iomfb-exploit
iOS 14 kernel exploit for CVE-2021-30807 targeting IOMobileFramebuffer, with tunable memory allocation for jailbreak development on A11+ devices.
 eddinos2/cve-2026-78938
Root-cause analysis and working exploit for CVE-2026-78938, a V8 TurboFan type confusion leading to arbitrary read/write within the compressed heap.…
 sandi-go/ps-2018-002---cve-2018-14442
Proof-of-concept exploit for CVE-2018-14442, a use-after-free vulnerability in Foxit Reader and PhantomPDF, enabling remote code execution via a…
 bi-zone/cve-2024-7965
This repository contains PoC for CVE-2024-7965. This is the vulnerability in the V8 that occurs only within ARM64.
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.