
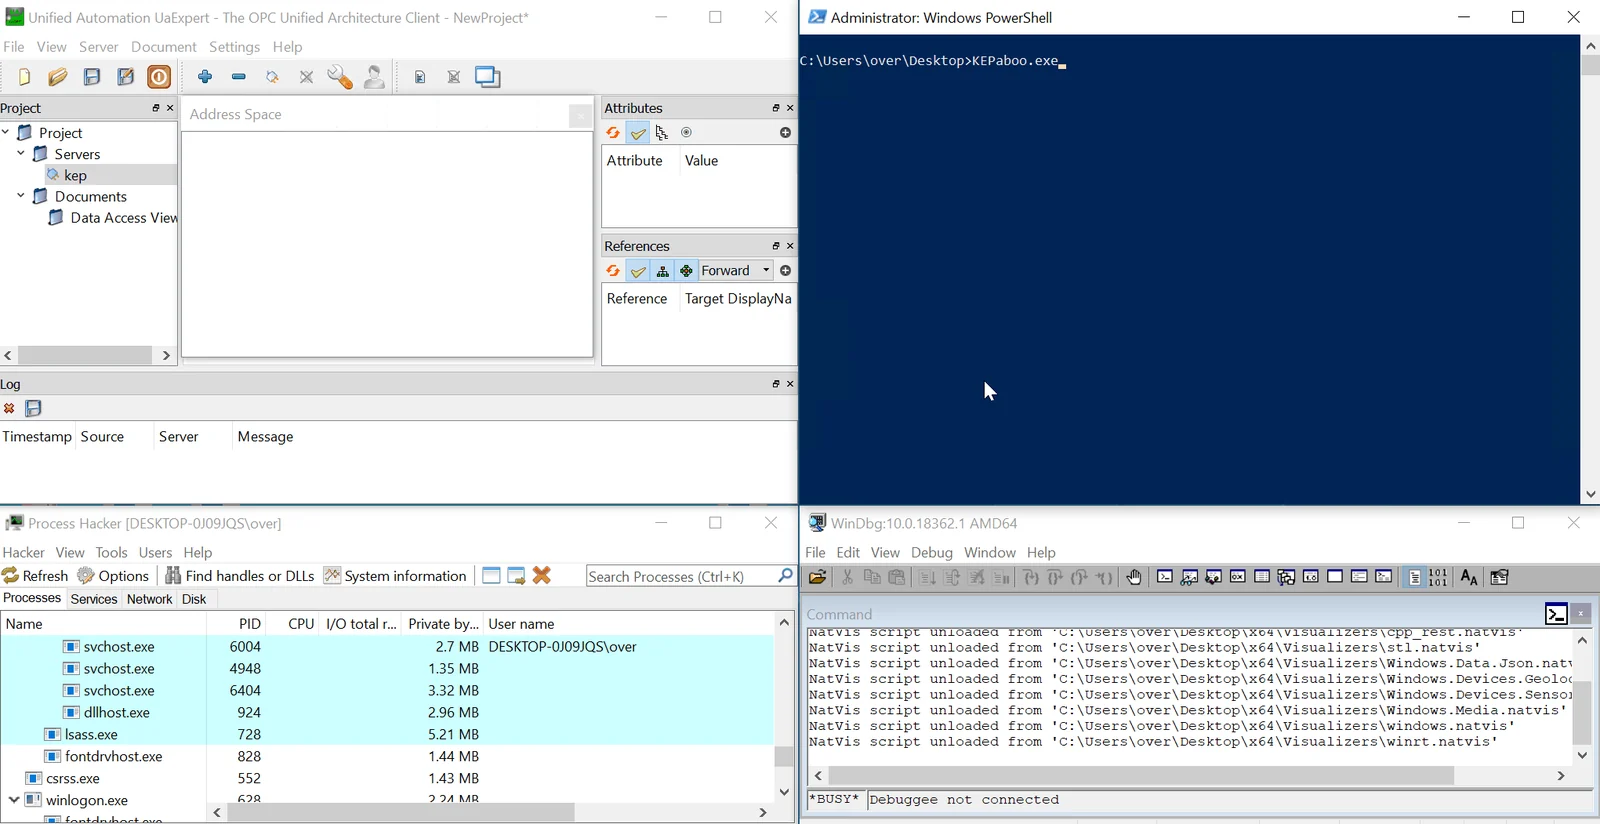
KEPaboo
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
anti-botbinary-analysisbinary-exploitation+5
0vercl0k/kepabooNeutralize KEPServerEX anti-debugging techniques
 orsuprasad/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwrite and SUID binary hijacking,…
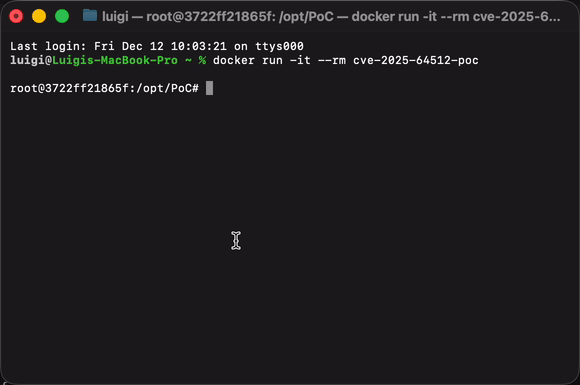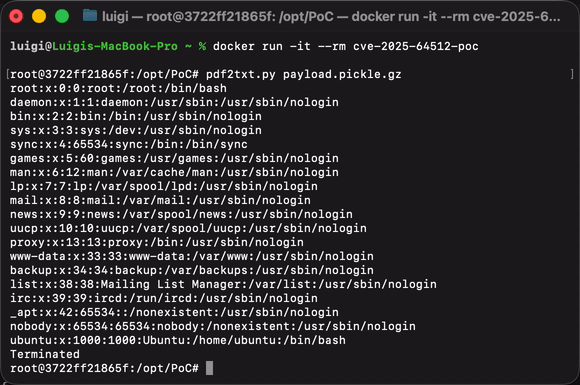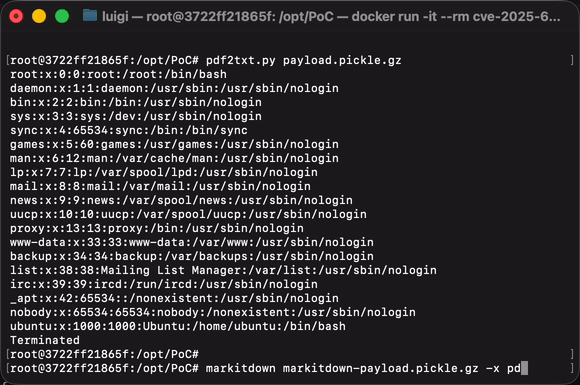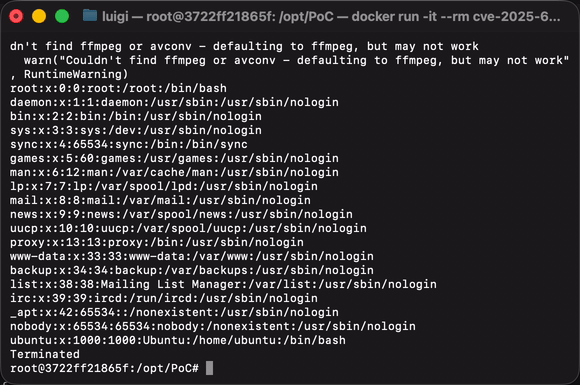 luigigubello/cve-2025-64512-polyglot-poc
A Proof-of-Concept for CVE-2025-64512 using a polyglot file.
 abdullahmaqbool22/explosive-as-hell-mcs-qualifer-web-500
[First-Blood-XO] React Server Component endpoint vulnerable to CVE-2025-55182 (RCE) → enumerated SUID binaries → /usr/bin/perl had SUID set → used…
 risuxx/cve-2023-34853
Disclosure of CVE-2023-34853: a stack overflow vulnerability in Supermicro X12DPG-QR BIOS firmware allowing local privilege escalation to DXE Runtime…
 crixpwn/cve-2026-8389
Technical analysis and proof-of-concept exploit for CVE-2026-8389, a SpiderMonkey BaselineJIT type confusion vulnerability in Firefox, demonstrated…
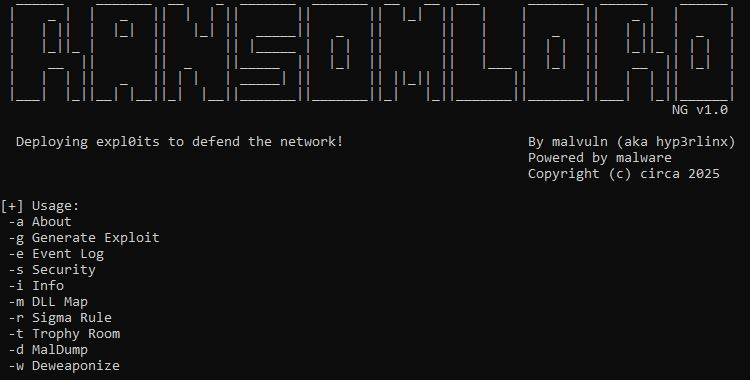 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 quarkslab/cve-2020-0069_poc
Proof-of-concept exploit for CVE-2020-0069 on Mediatek Android devices, enabling kernel memory read/write and syscall hooking for privilege…
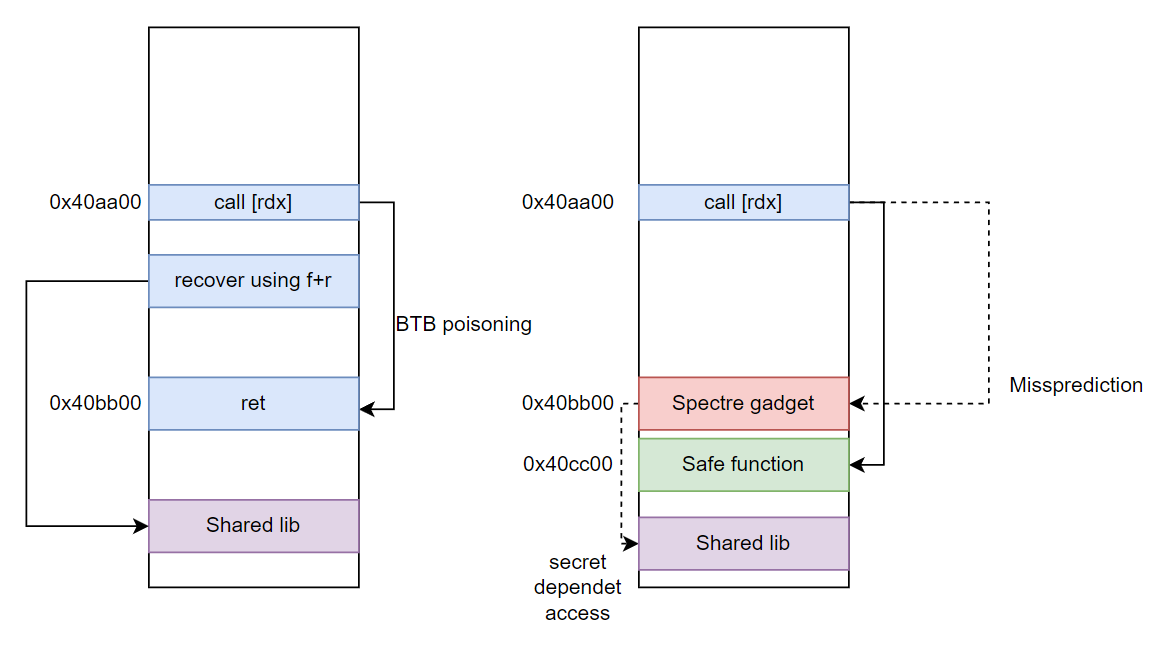 es0j/execaslr-ekoparty
Proof-of-concept exploit that bypasses ASLR on Intel CPUs by abusing branch target buffer and speculative execution to leak randomized addresses via…
 themalwareguardian/cve-2025-70330
Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
 ashemery/exploitation-course
Offensive Software Exploitation Course
 diego-altf4/pwnctftool
Automated ret2win exploit tool for CTF challenges. Finds stack offset, generates payloads, supports remote exploitation, and attaches GDB for…
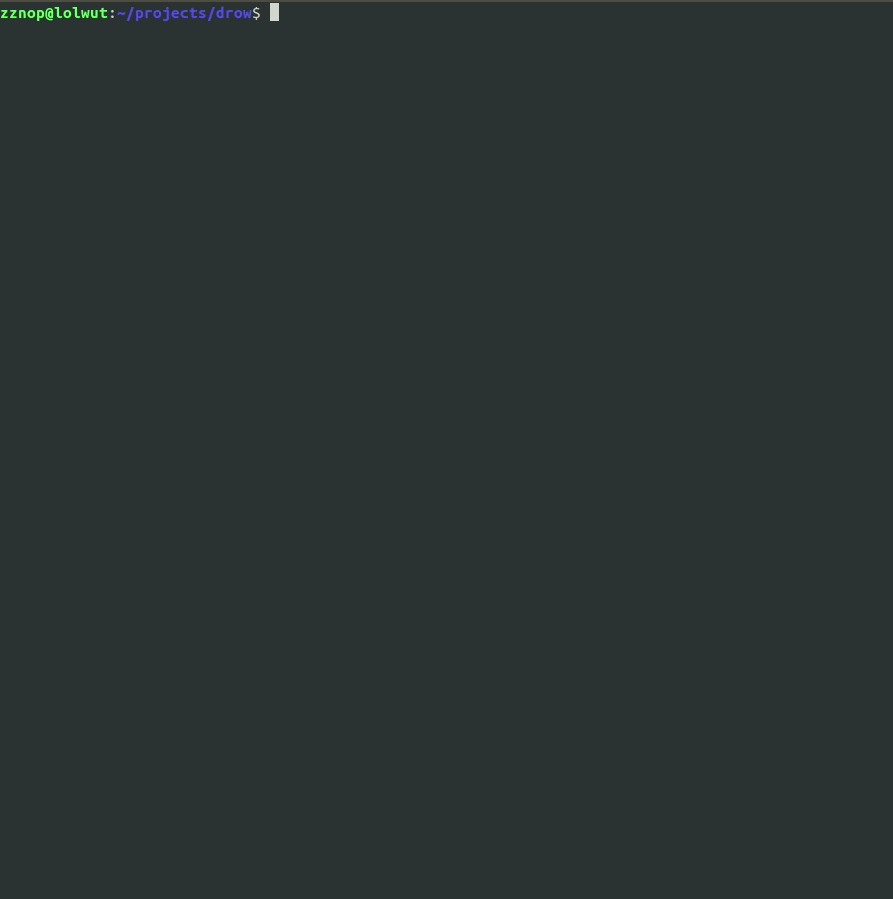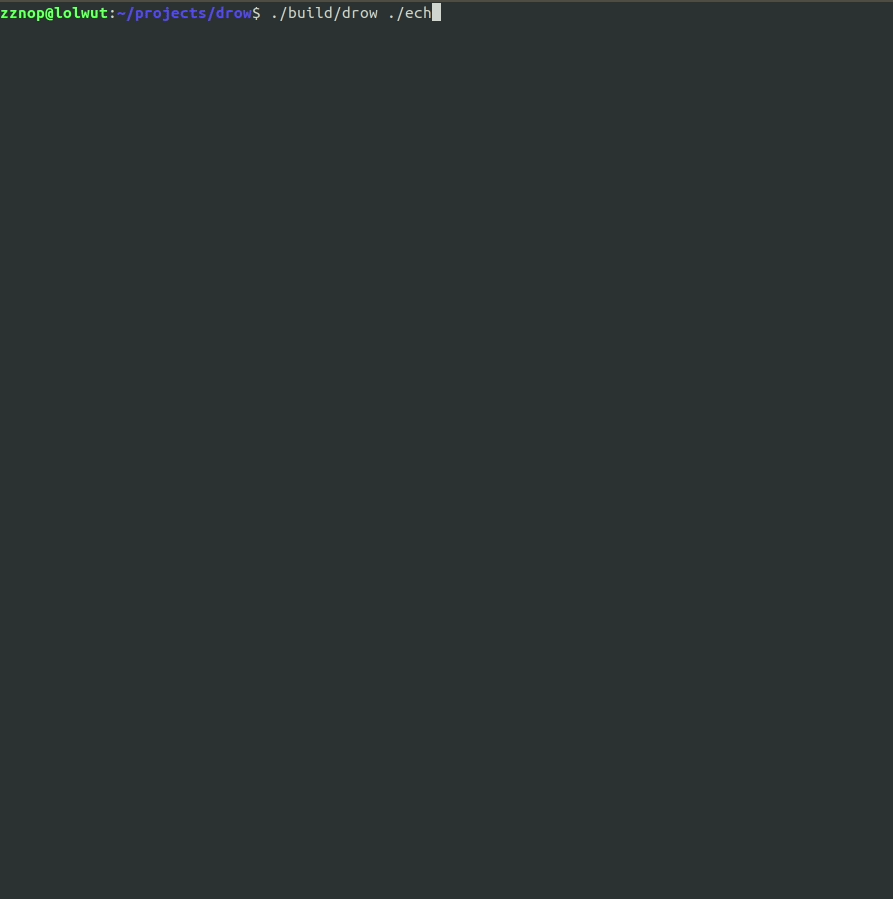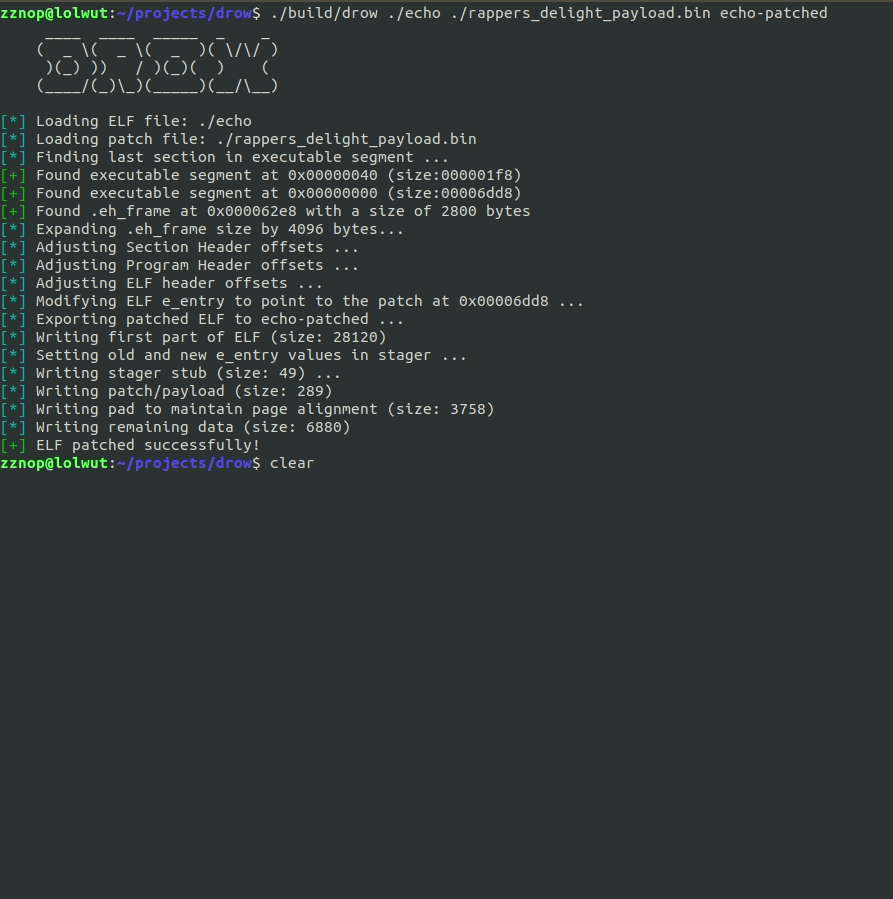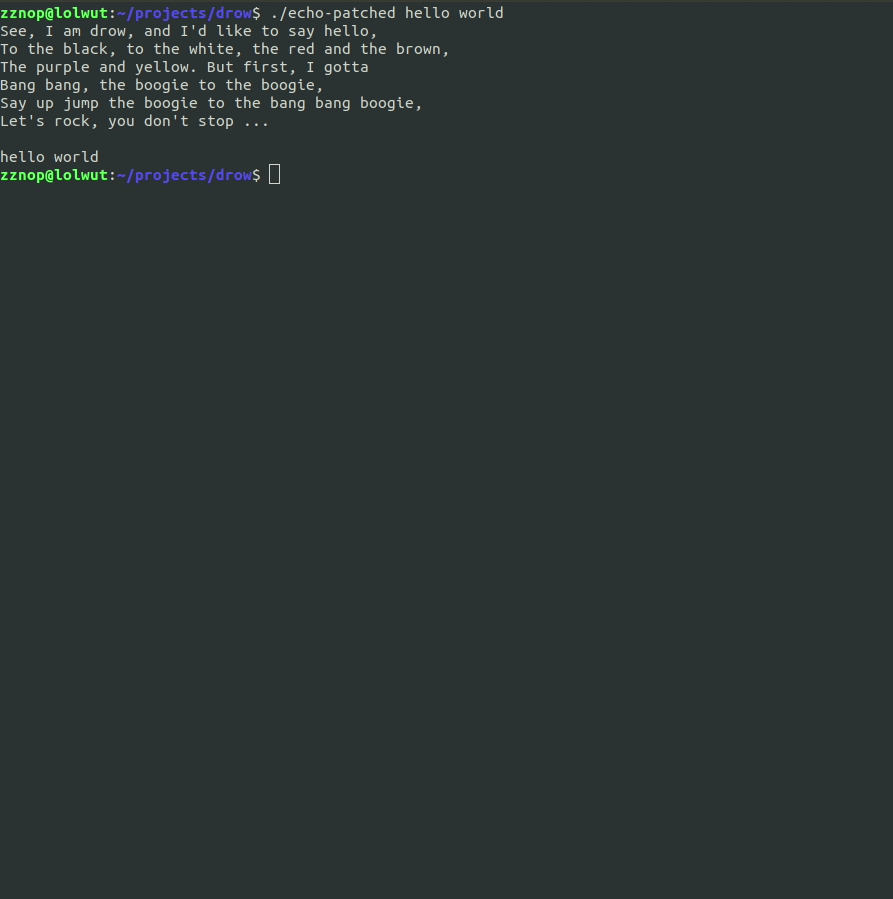 zznop/drow
Injects code into ELF executables post-build
 mainframed/dc30_workshop
DEFCON 30 Mainframe buffer overlow workshop container
 bazad/x18-leak
CVE-2018-4185: iOS 11.2-11.2.6 kernel pointer disclosure introduced by Apple's Meltdown mitigation.
 sh4den/cve-2022-23093
The FreeBSD ICMP buffer overflow, freebsd buffer overflow poc
 synacktiv/netgear_pwn2own2021
Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021