

vscode-frida
 chichou/vscode-frida
Unofficial frida extension for VSCode
android-securitybinary-analysisdebuggers+5
chichou/vscode-fridaUnofficial frida extension for VSCode
 hunt-benito/rendering-code-outside-the-sandbox-cve-2026-76036-dawn-webgpu-buffer-overflow-in-chrome-on-android
Differential detection harness for CVE-2026-76036, a Dawn WebGPU heap buffer overflow in Chrome on Android. Probes vulnerable depth/stencil texture…
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
 atiilla/cve-2026-85046
Proof-of-concept and technical analysis for CVE-2026-85046, a V8 type confusion in inline Array.prototype.sort, including root cause, patch diff, and…
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 tomer8007/widevine-l3-decryptor
A Chrome extension that demonstrates bypassing Widevine L3 DRM
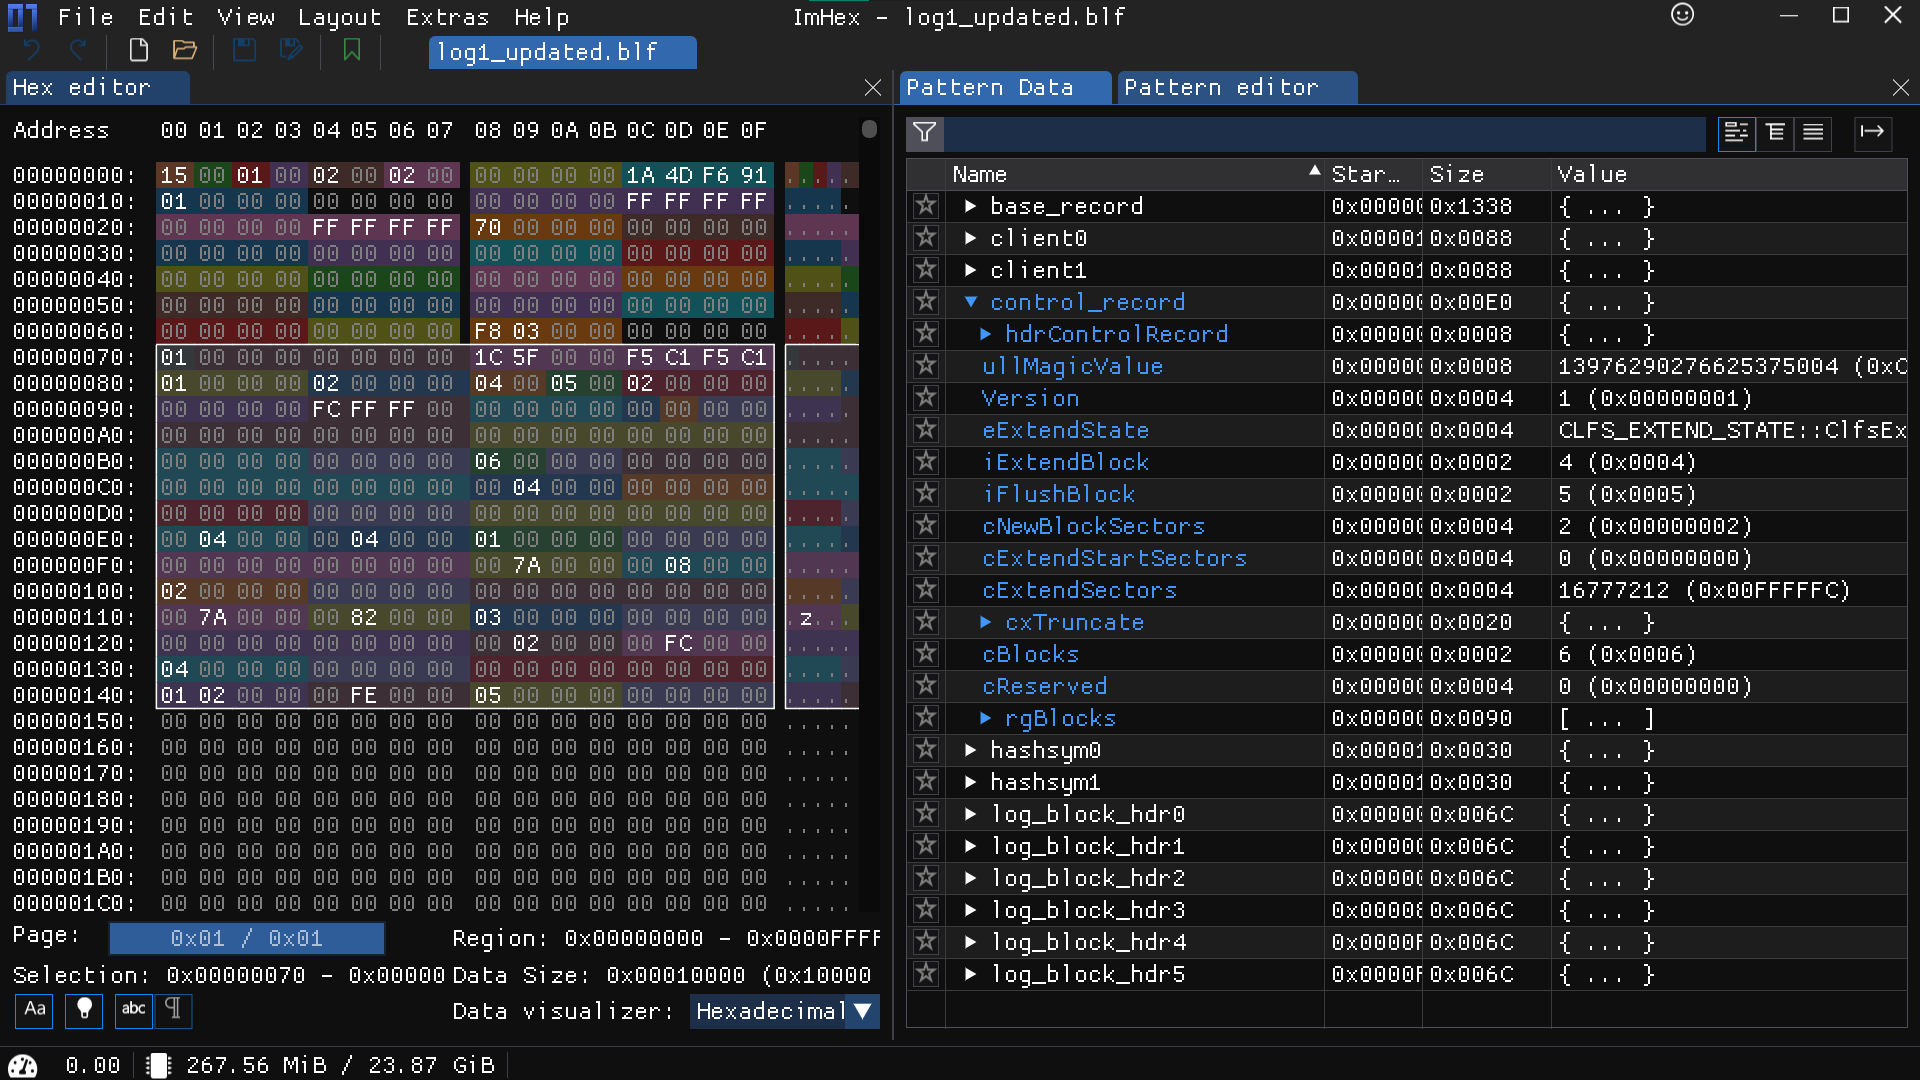 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 typeconfused/cve-2025-14174-analysis
Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 brnpl/flutter-reverse-engineering-labs
Hands-on challenges for learning how to reverse engineer Flutter applications.
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 frida/frida
Main repo for hosting release binaries
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
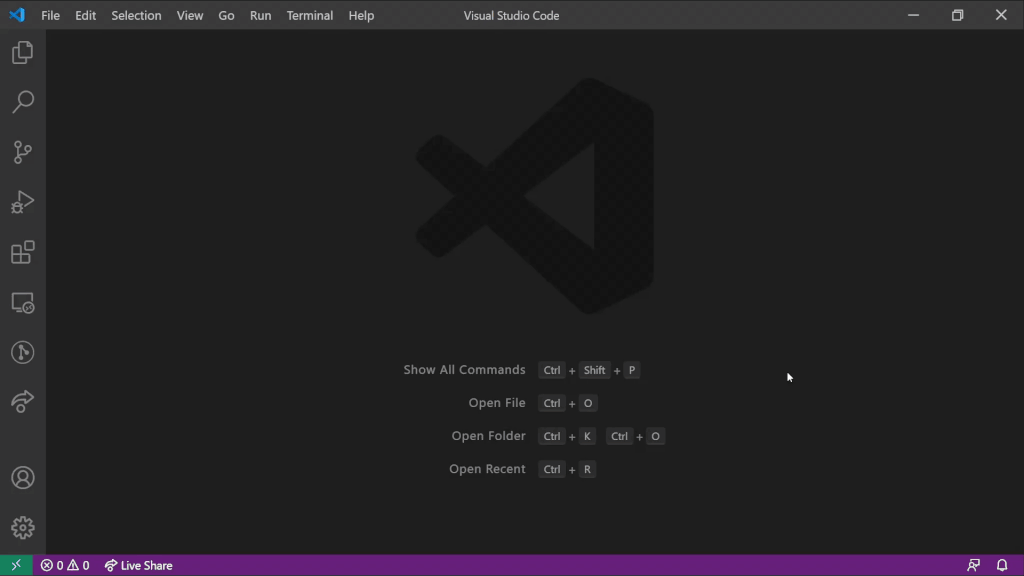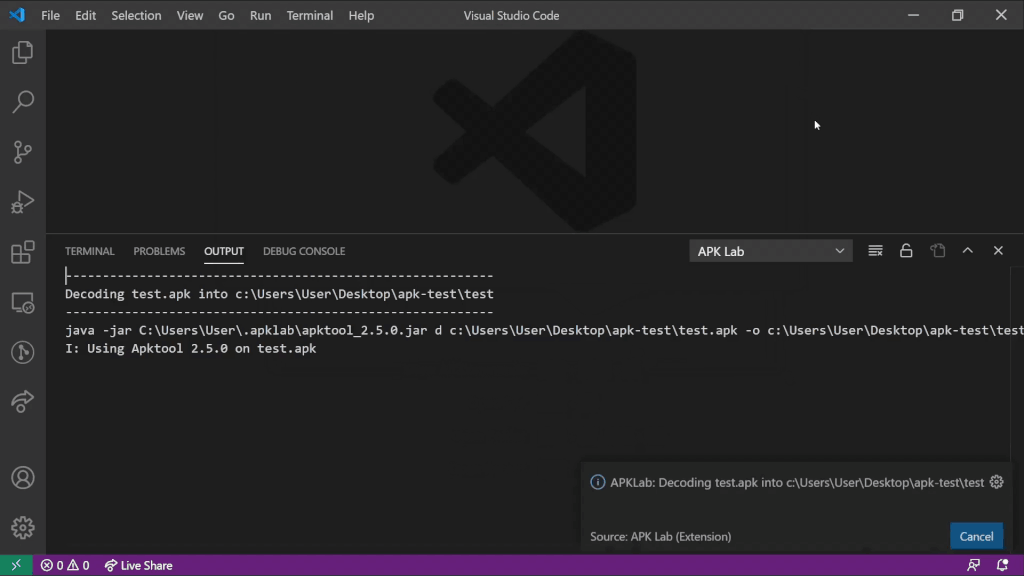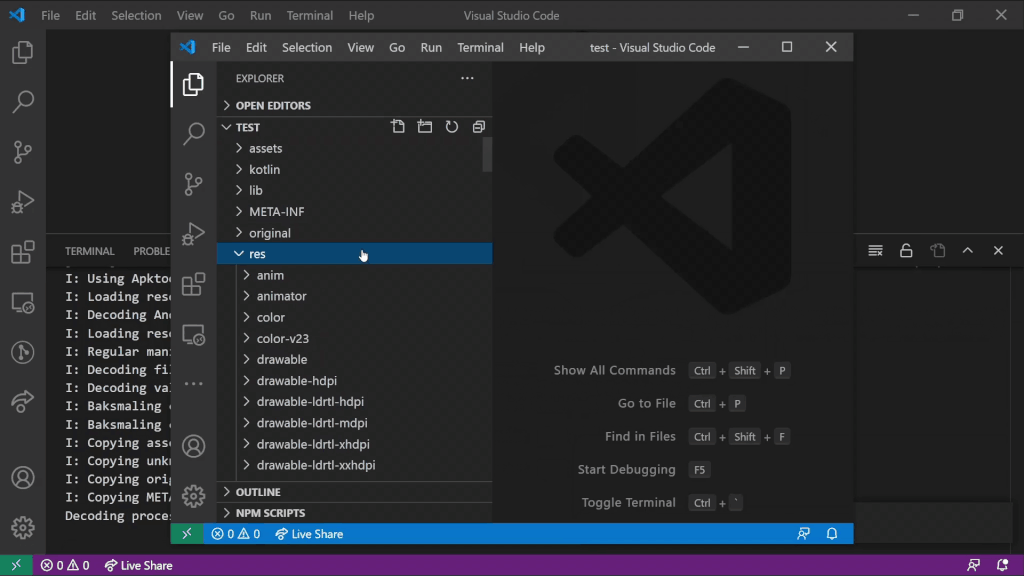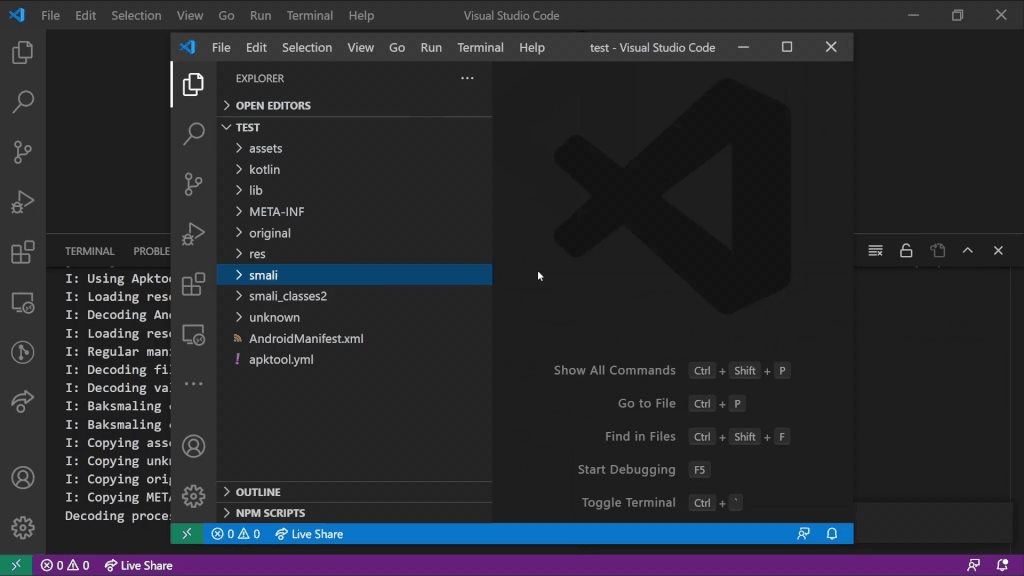 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
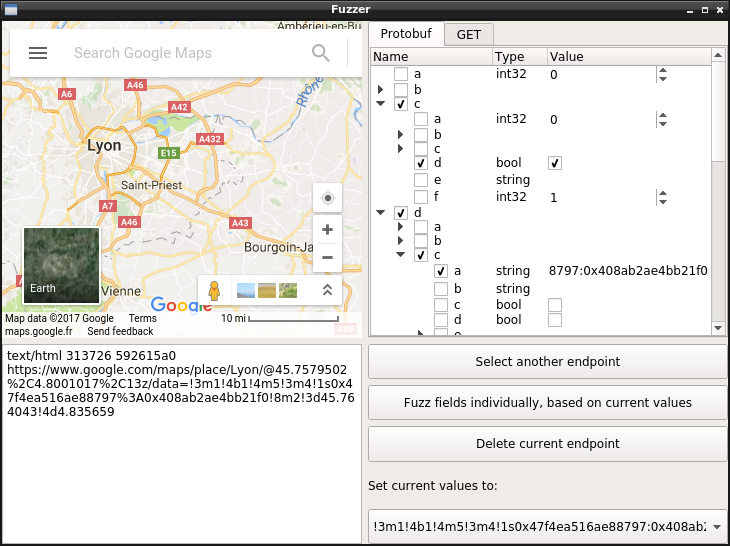 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit