apiscope
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
kaisonox/apiscopeAn API hooking framework for intercepting and monitoring Windows applications


 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
 corelight/zeek-elf
A Zeek ELF File Analyzer
 jm00nj/hpe-aruba-aos8-vulnerabilities
ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
 rohithronanki/cve-2026-34159-vulnerability-research-analysis-detection
Critical buffer validation bypass in deserialize_tensor() (llama.cpp < b8492). Null tensor buffer skips bounds check, enabling unauthenticated…
 personnumber3377/windows_tcpip_fuzz
This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…
 wildfootw/cve-2014-0160_openssl_1.0.1f_heartbleed
Exploit for the Heartbleed vulnerability (CVE-2014-0160) in OpenSSL 1.0.1f, allowing memory disclosure from vulnerable servers.
 0vercl0k/cve-2021-24086
Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
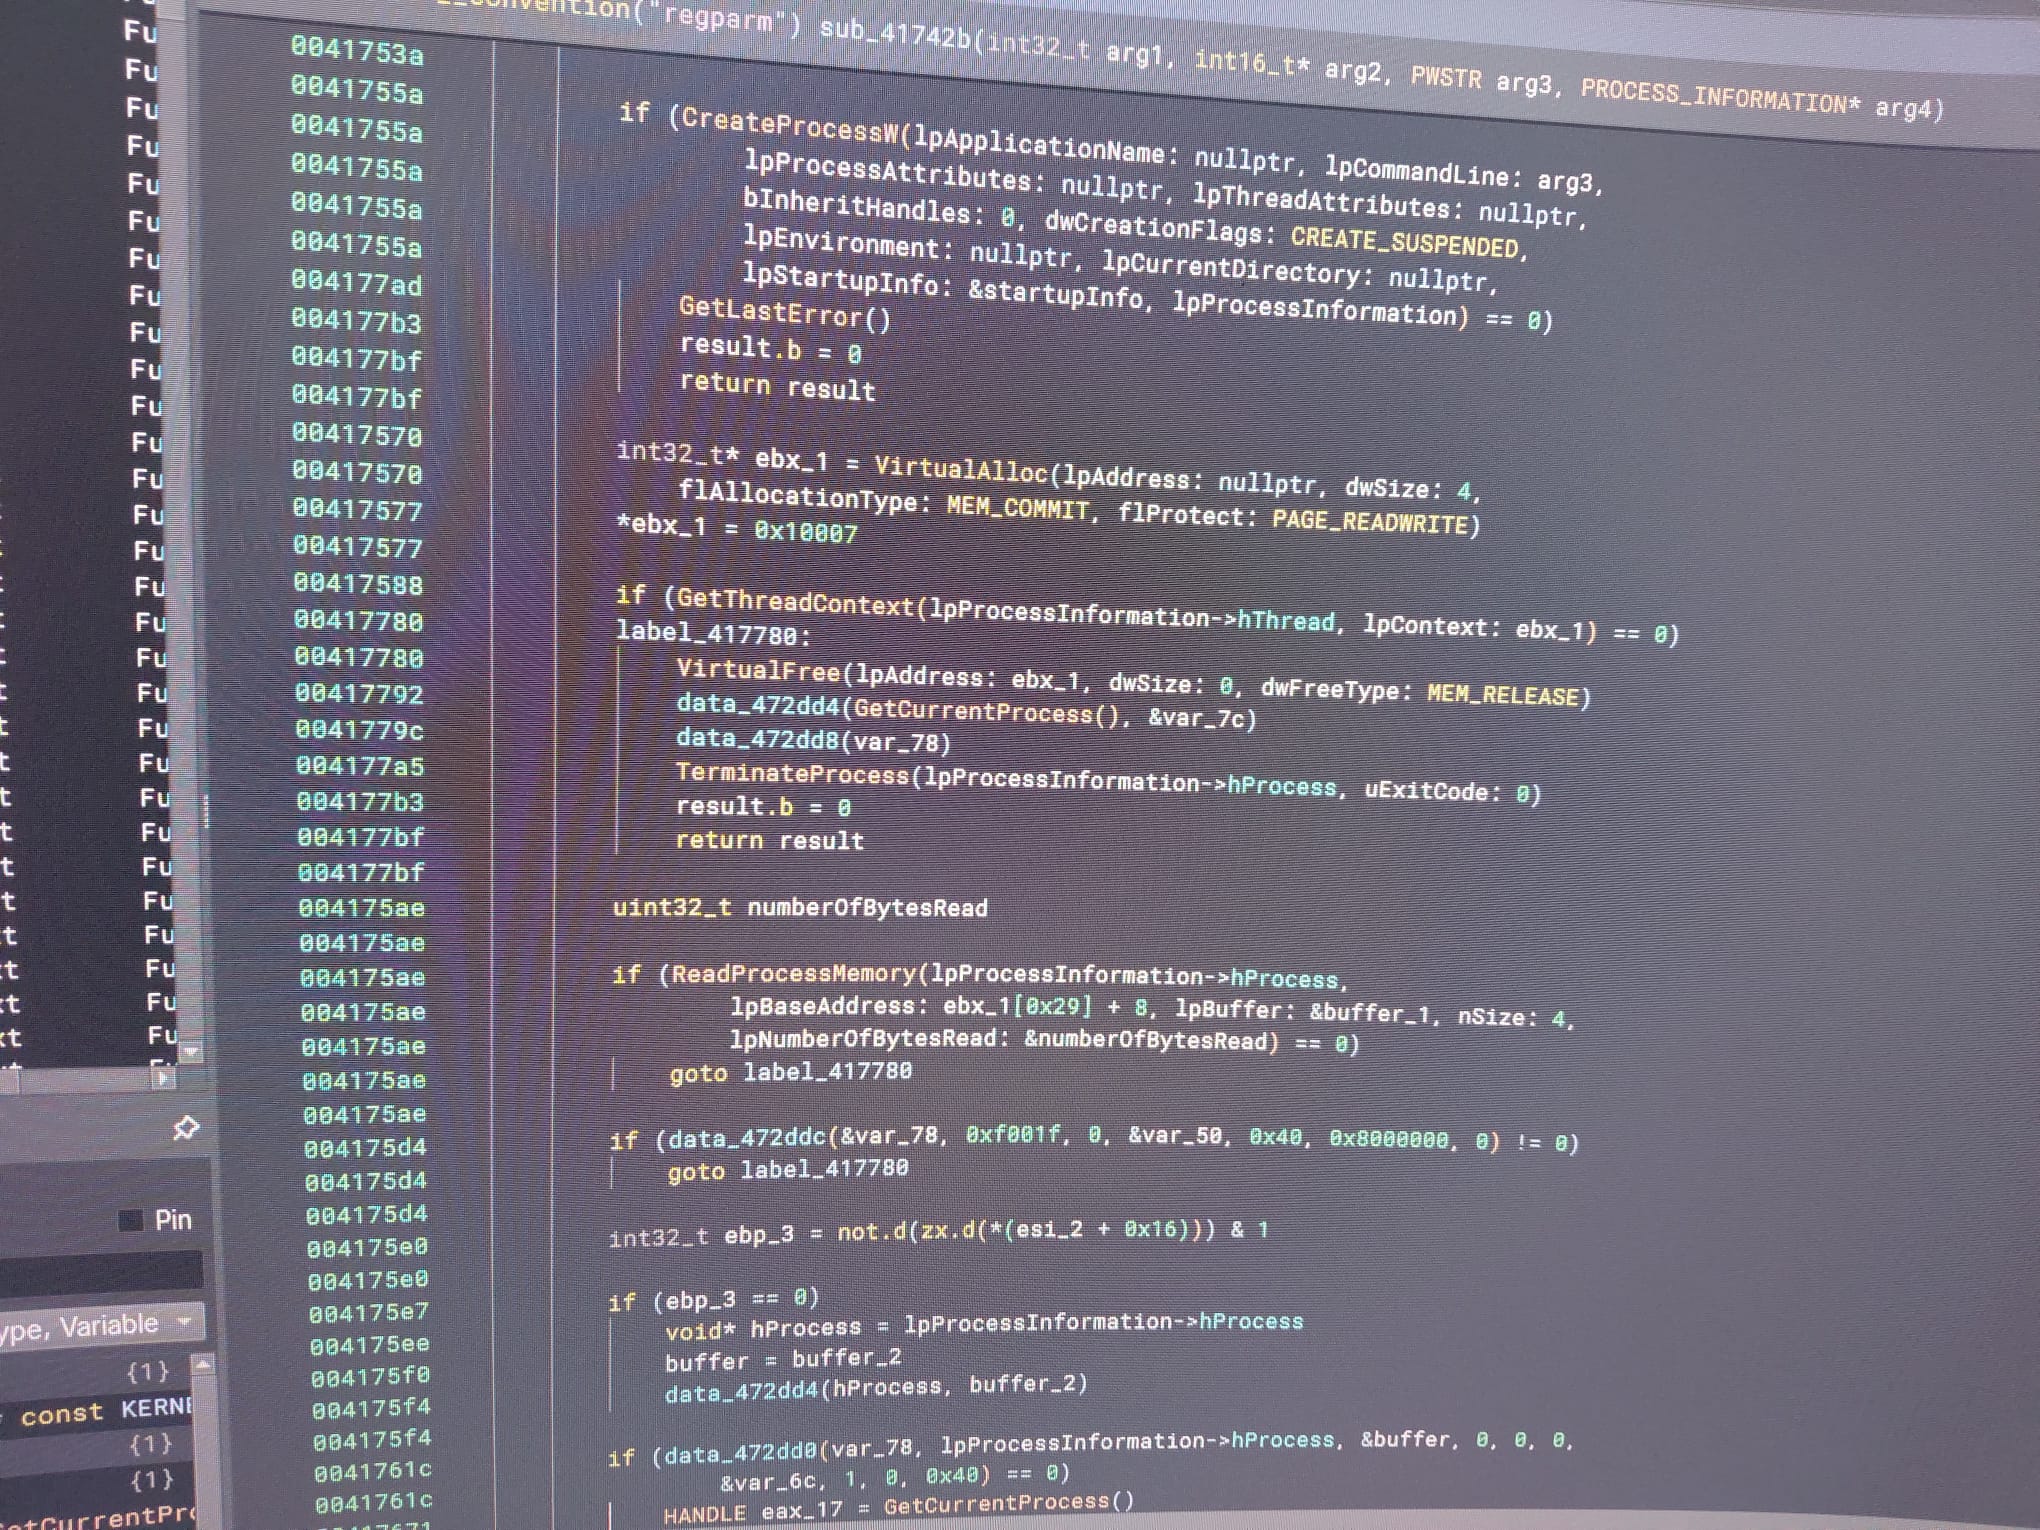 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
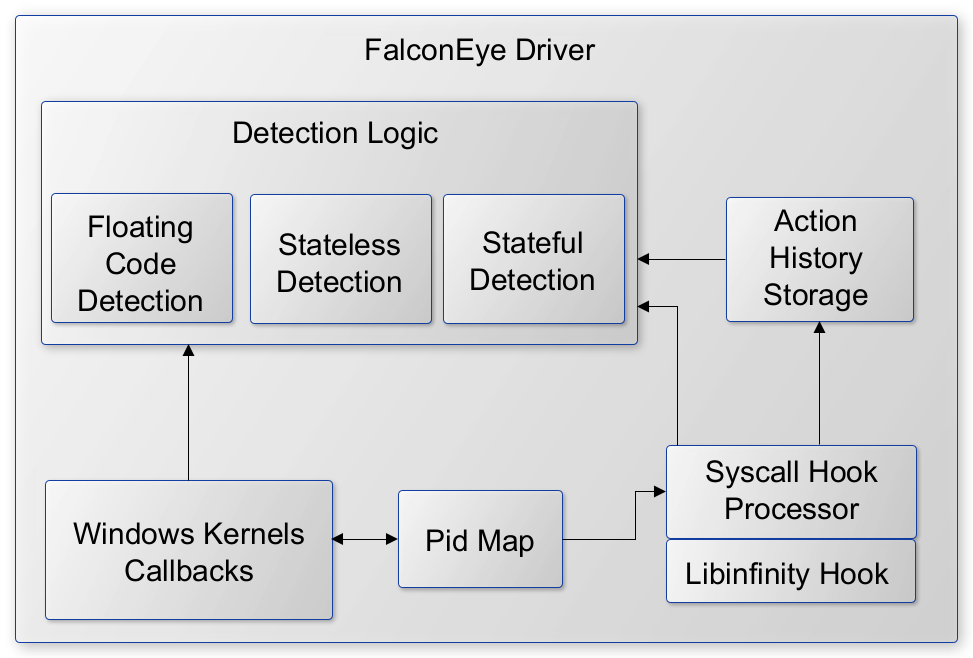 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…