
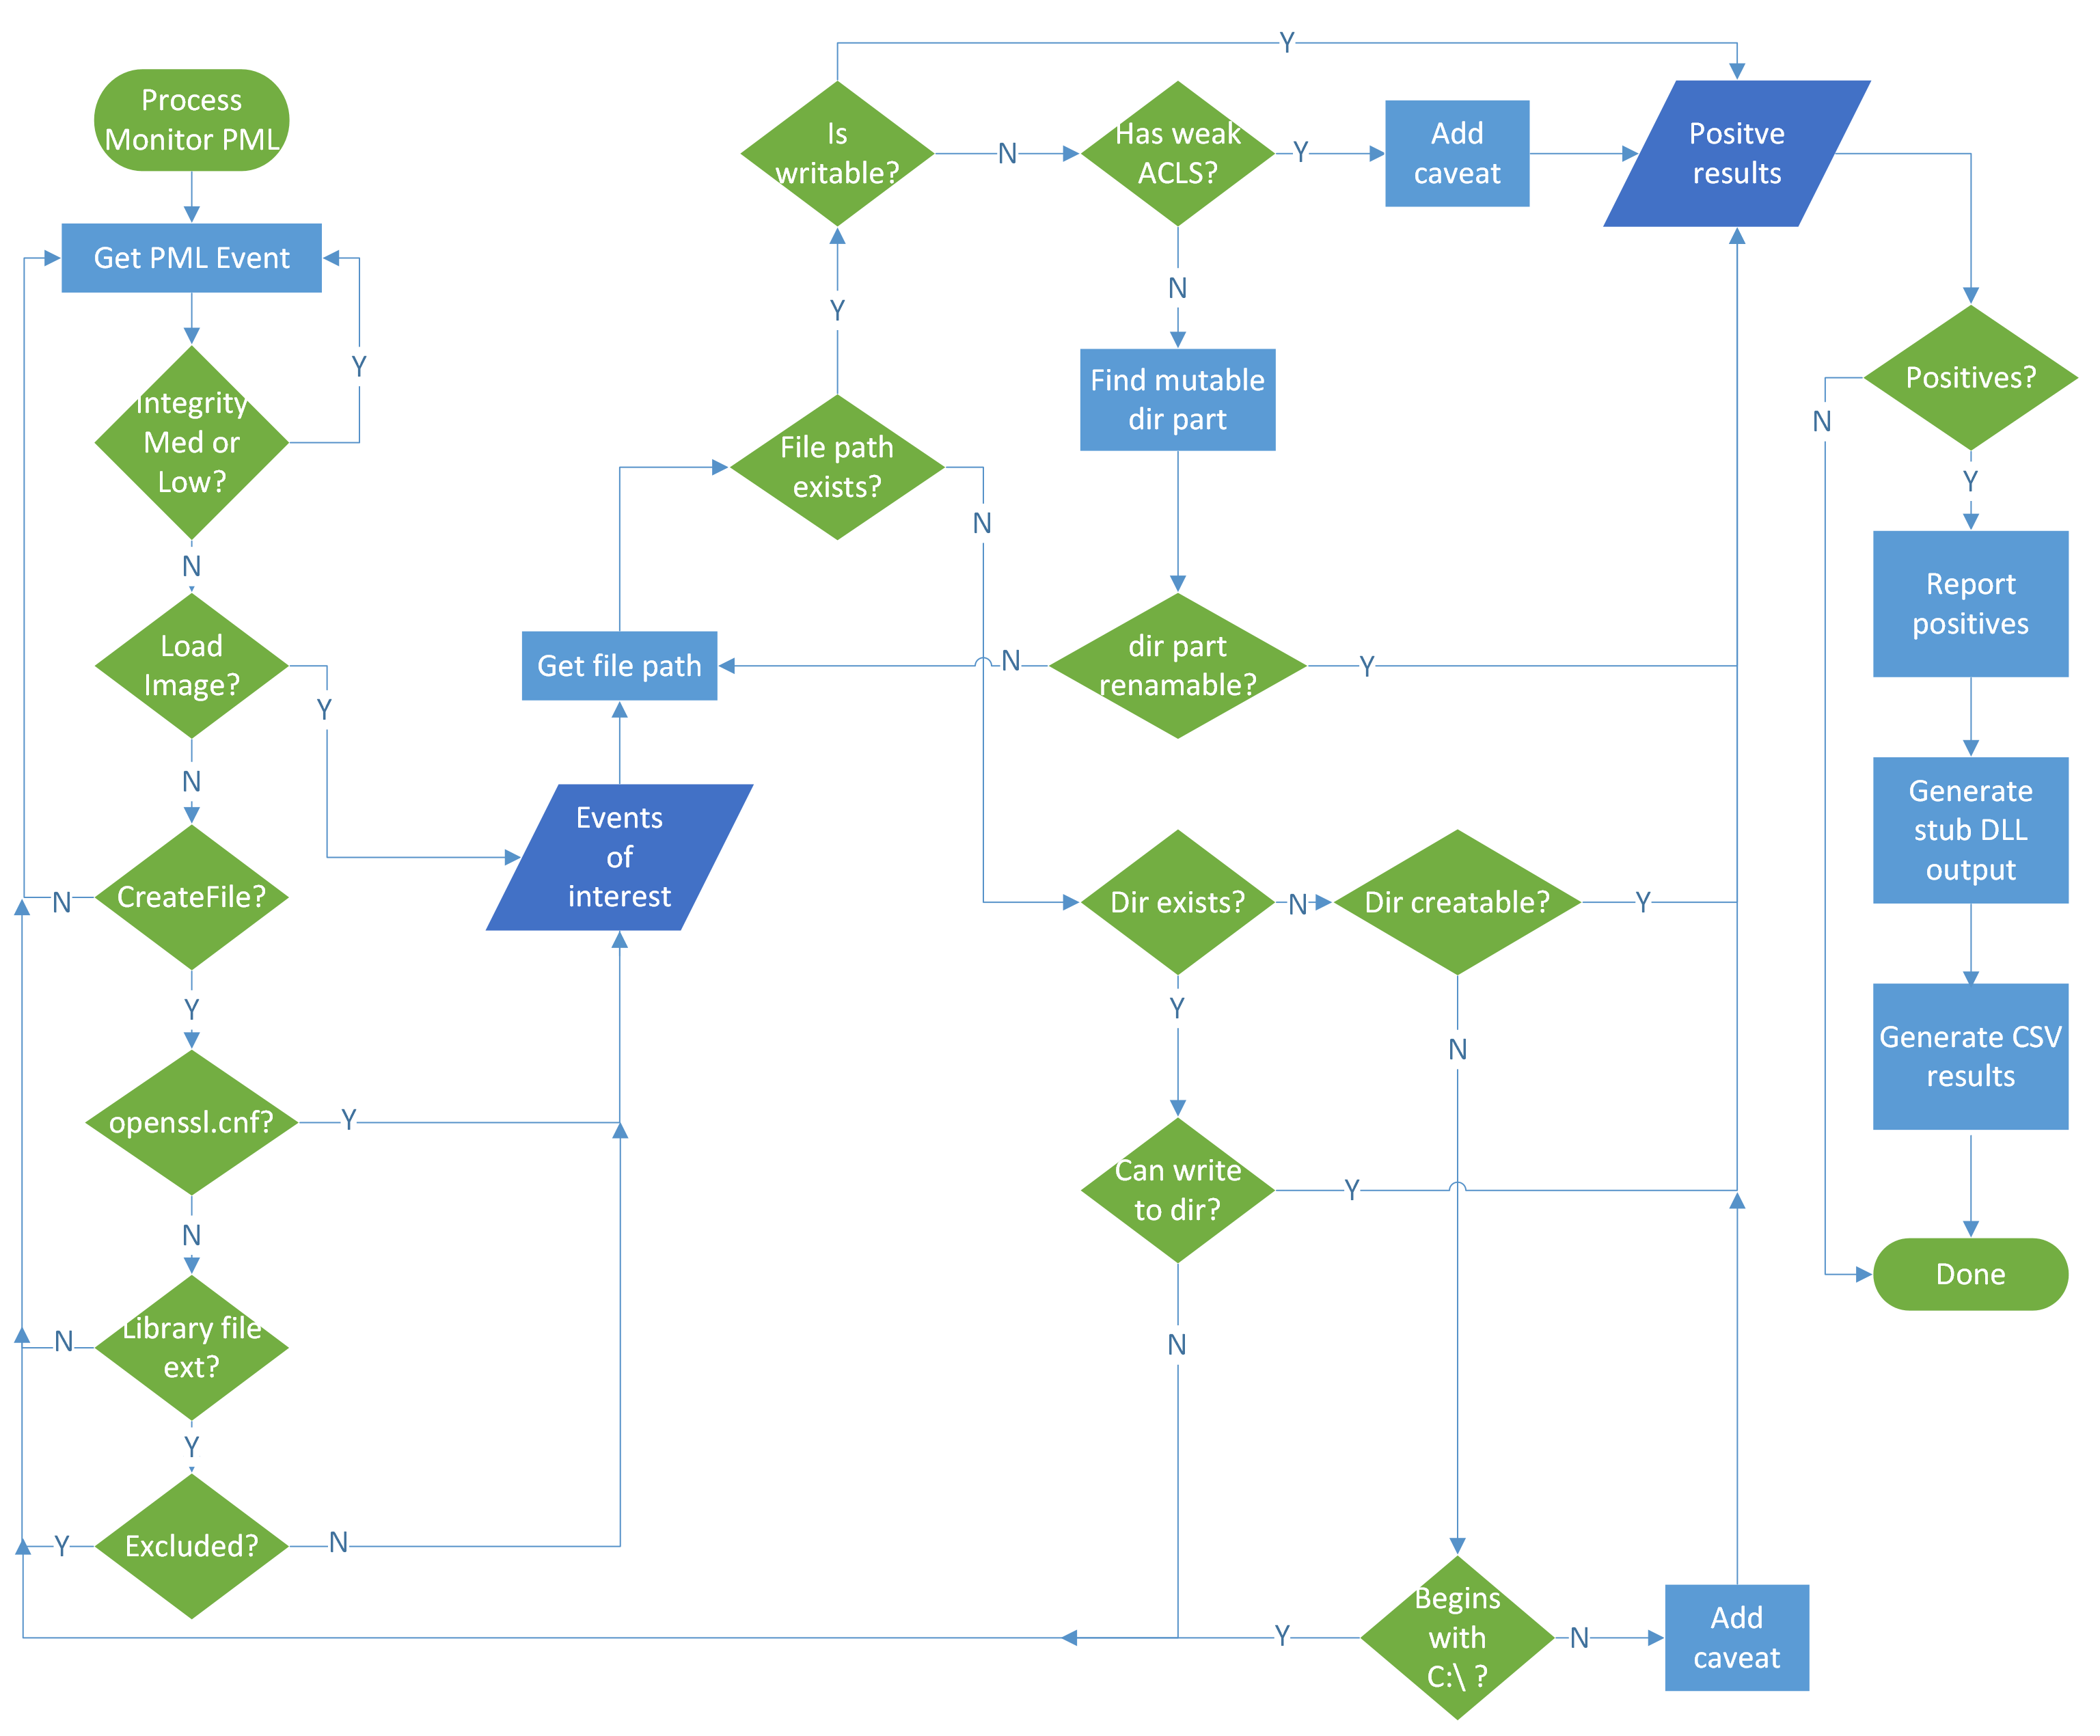
Crassus
 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
binary-analysisexploitationpenetration-testing+1
631
vu-ls/crassusWindows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 nam3lum/msi-central_privesc
CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application
 rjt-gupta/cve-2020-24089
Windows Privilege Escalation: IOBit Malware Fighter v8.0.2
 sahil3276/cve-2024-44346
Public Disclosure of CVE-2024-44346
 shauryae1337/cve-2024-44346
Public Disclosure
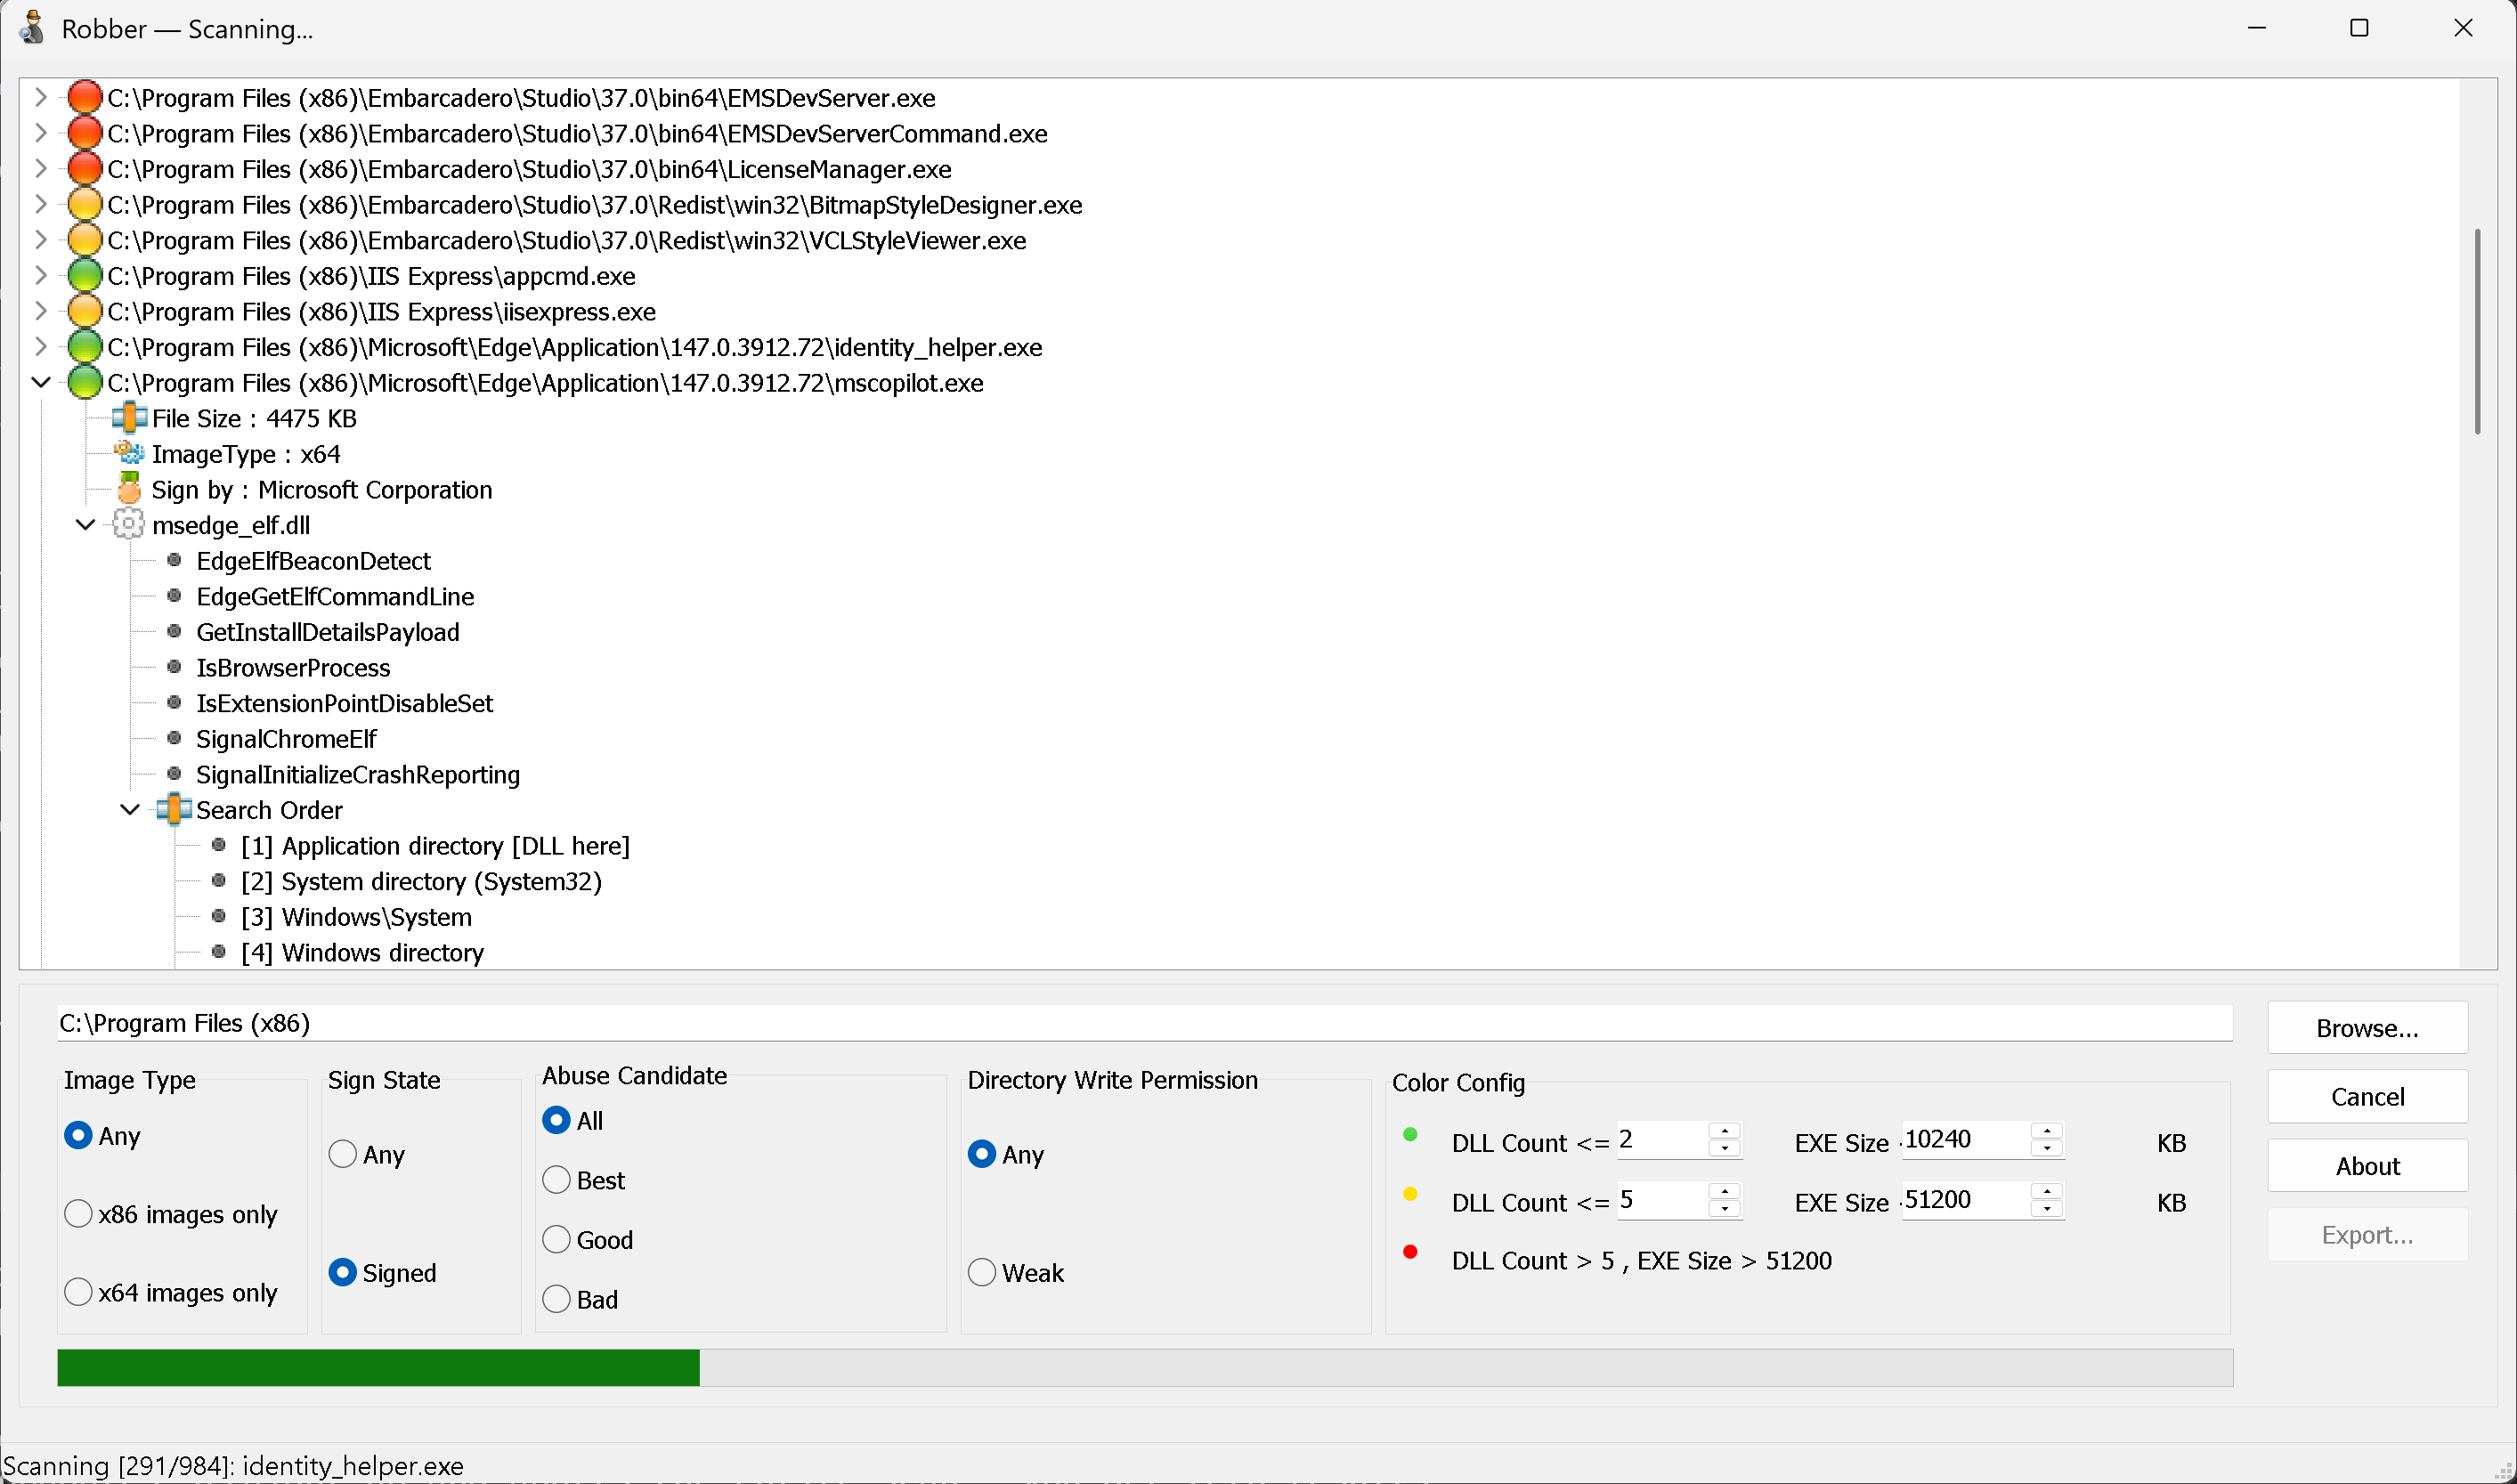 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
 lab52io/leakedhandlesfinder
Leaked Windows processes handles identification tool
 moiz-2x/cve-2025-21420_poc
Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)
 alfarom256/cve-2022-45451
PoC for Acronis Arbitrary File Read - CVE-2022-45451
 kernelm0de/cve-2018-8090
DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)
 d7ead/cve-2026-38765
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 ugvxb/cve-2026-9490
The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
 d7ead/cve-2026-38764
An issue in Unistal Systems Pvt. Ltd. Protegent 360 v2.0.0.4 allows a local attacker to escalate privileges via the kernel driver pgsecdl.sys
 wise-security/cve-2025-69599
Proof-of-concept exploit for CVE-2025-69599, demonstrating uncontrolled search path element in RayVentory Scan Engine's rvia and ndtrack binaries,…
 perlun/sudo-1.8.3p1-patched
Custom version of sudo 1.8.3p1 with CVE-2021-3156 patches applied
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…