

forensictools
 cristianzsh/forensictools
Collection of forensic tools
binary-analysisdata-recoverydigital-forensics+7
cristianzsh/forensictoolsCollection of forensic tools
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
 proteqtum/interactive-binary-structures
Interactive documentation and visual reference for binary formats and system memory layouts.
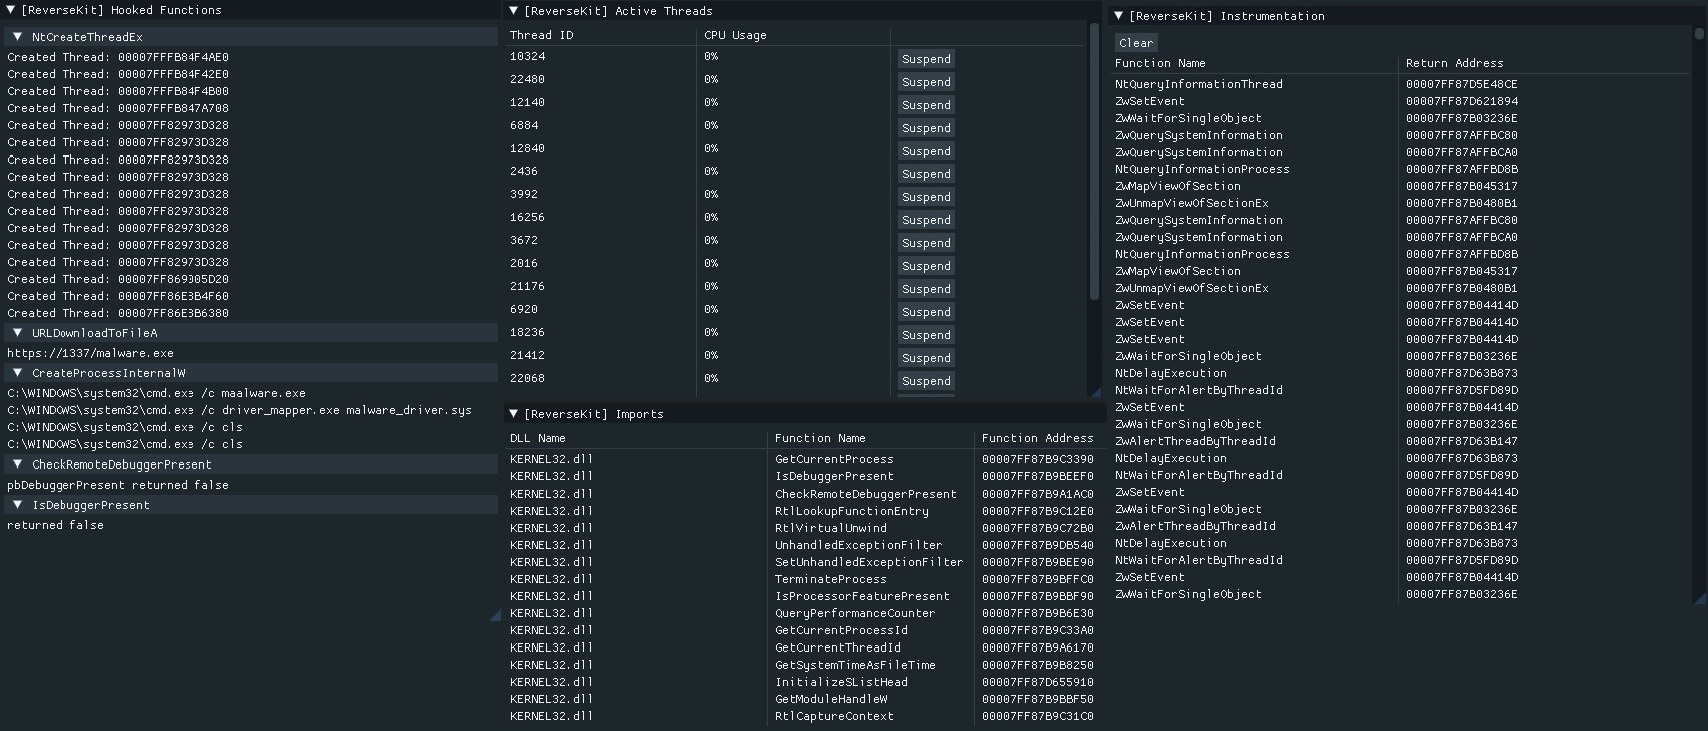 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.