
peCloakCapstone
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
binary-analysisids-ips-evasionmalware-analysis+2
10911 years ago
v-p-b/pecloakcapstonePlatform independent peCloak fork based on Capstone
 satheesh575555/linux-4.1.15_cve-2023-28772
Analyzes and demonstrates the Linux kernel vulnerability CVE-2023-28772, providing a patched or vulnerable kernel source for security research and…
 nanopathi/linux-4.19.72_cve-2020-25705
Linux kernel 4.19.72 source code with a focus on CVE-2020-25705, intended for vulnerability analysis, exploitation research, and educational study of…
 trinadh465/linux-4.1.15_cve-2023-4128
Linux kernel 4.1.15 source code with a focus on CVE-2023-4128, intended for vulnerability analysis and educational study of kernel security.
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
 chernstepanov/copyfail-for-dummies
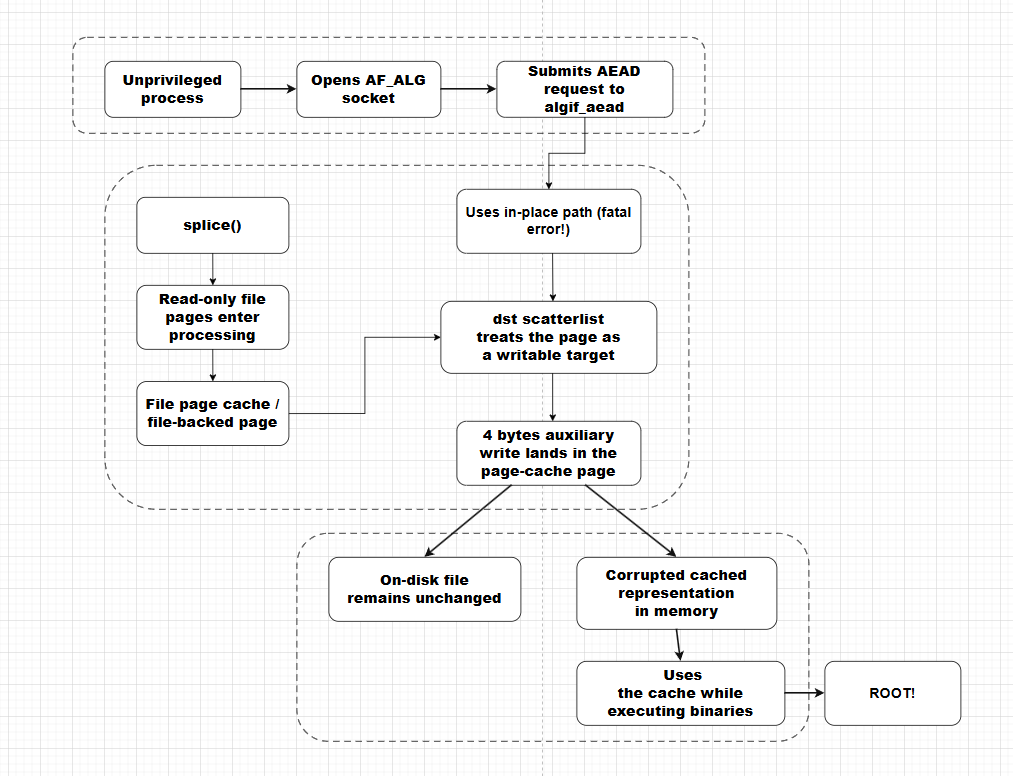
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 laachy/cve-2024-39930-ptrace-detection-mitigation
Rust-based tool to detect and mitigate CVE-2024-39930 ptrace exploitation, providing binary-level analysis and defensive countermeasures for Linux…
 trinadh465/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source tree with a patch for CVE-2022-45934, a use-after-free vulnerability in the netfilter subsystem, for analysis and testing.
 trinadh465/linux-4.1.15_cve-2022-3564
Linux kernel 4.1.15 source code snapshot for analyzing and studying CVE-2022-3564, a vulnerability in the kernel's network subsystem.
 trinadh465/linux-4.1.15_cve-2023-28772
Linux kernel 4.1.15 source tree with patches for CVE-2023-28772, providing a reference for vulnerability analysis and exploitation research.
 trinadh465/linux-3.0.35_cve-2019-10220
Linux kernel 3.0.35 source tree with a focus on CVE-2019-10220, providing a reference for vulnerability analysis and exploitation research.
 trinadh465/linux-4.1.15_cve-2023-26607
Linux kernel 4.1.15 source code with a focus on CVE-2023-26607, providing a reference for vulnerability analysis and understanding the affected code.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
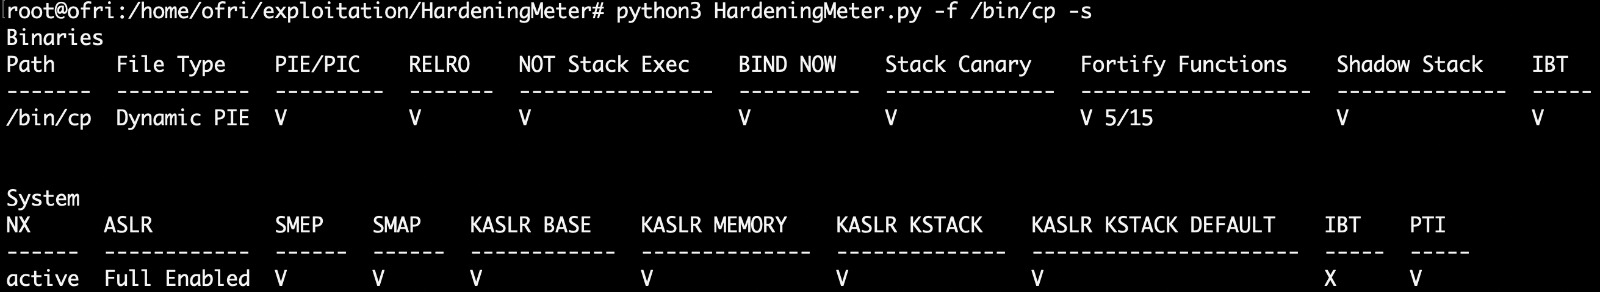 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 zimawhit3/bitmancer
Nim Library for Offensive Security Development