
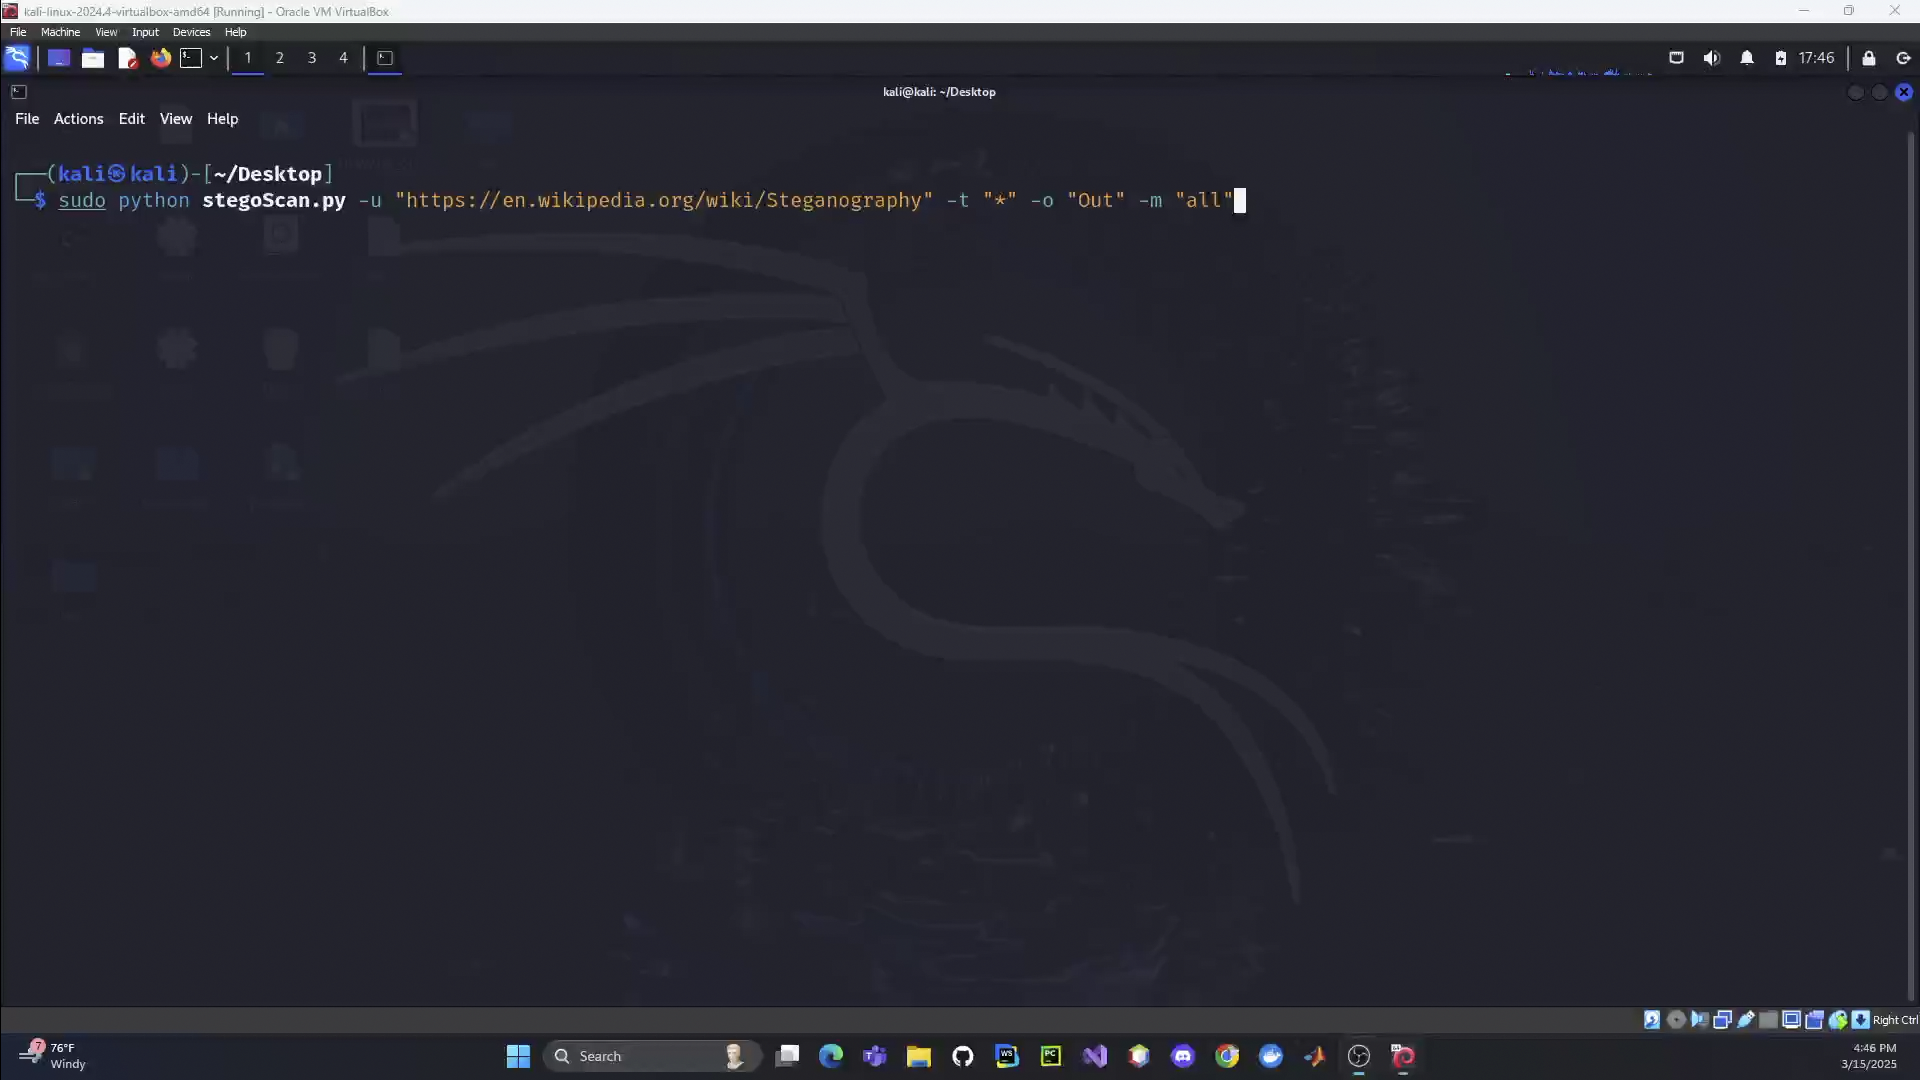
StegoScan
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
ai-securitybinary-analysiscrawler+7
109
lcbower33/stegoscanAutomated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 jianrongxiao-linksys/dnsmasq-cve-2026
Automated defect verification tool for 6 dnsmasq CVEs (CVE-2026-2291, 4890, 4891, 4892, 4893, 5172)
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
 cmu-sei/pharos
Automated static analysis tools for binary programs
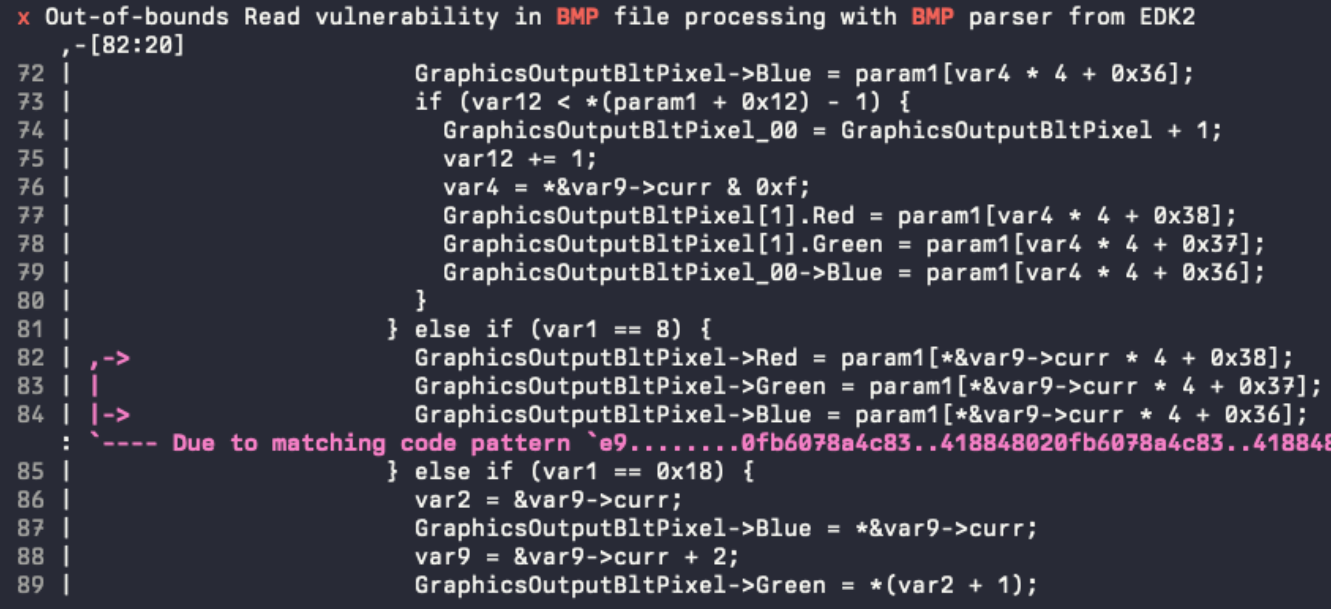 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
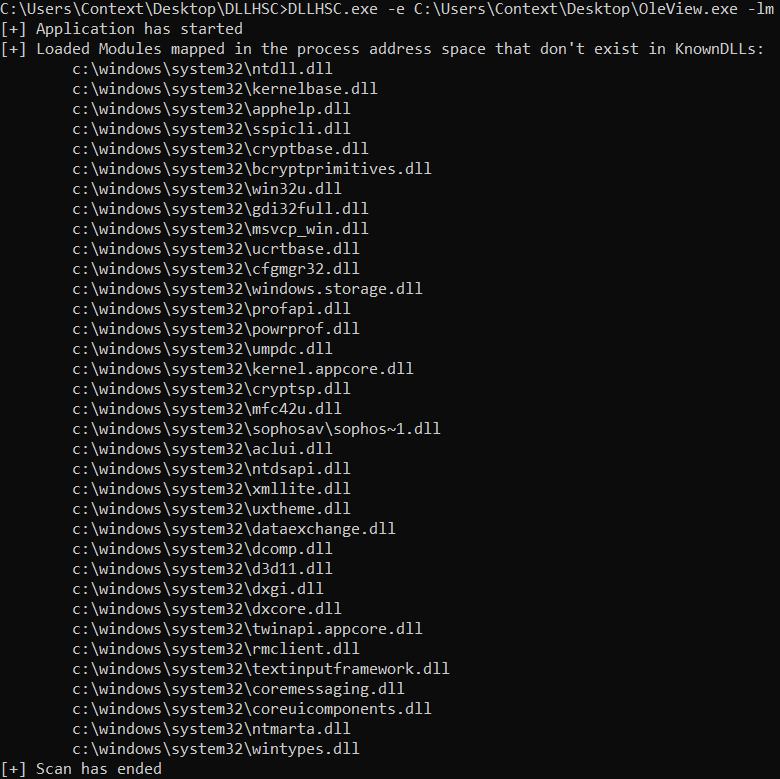 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
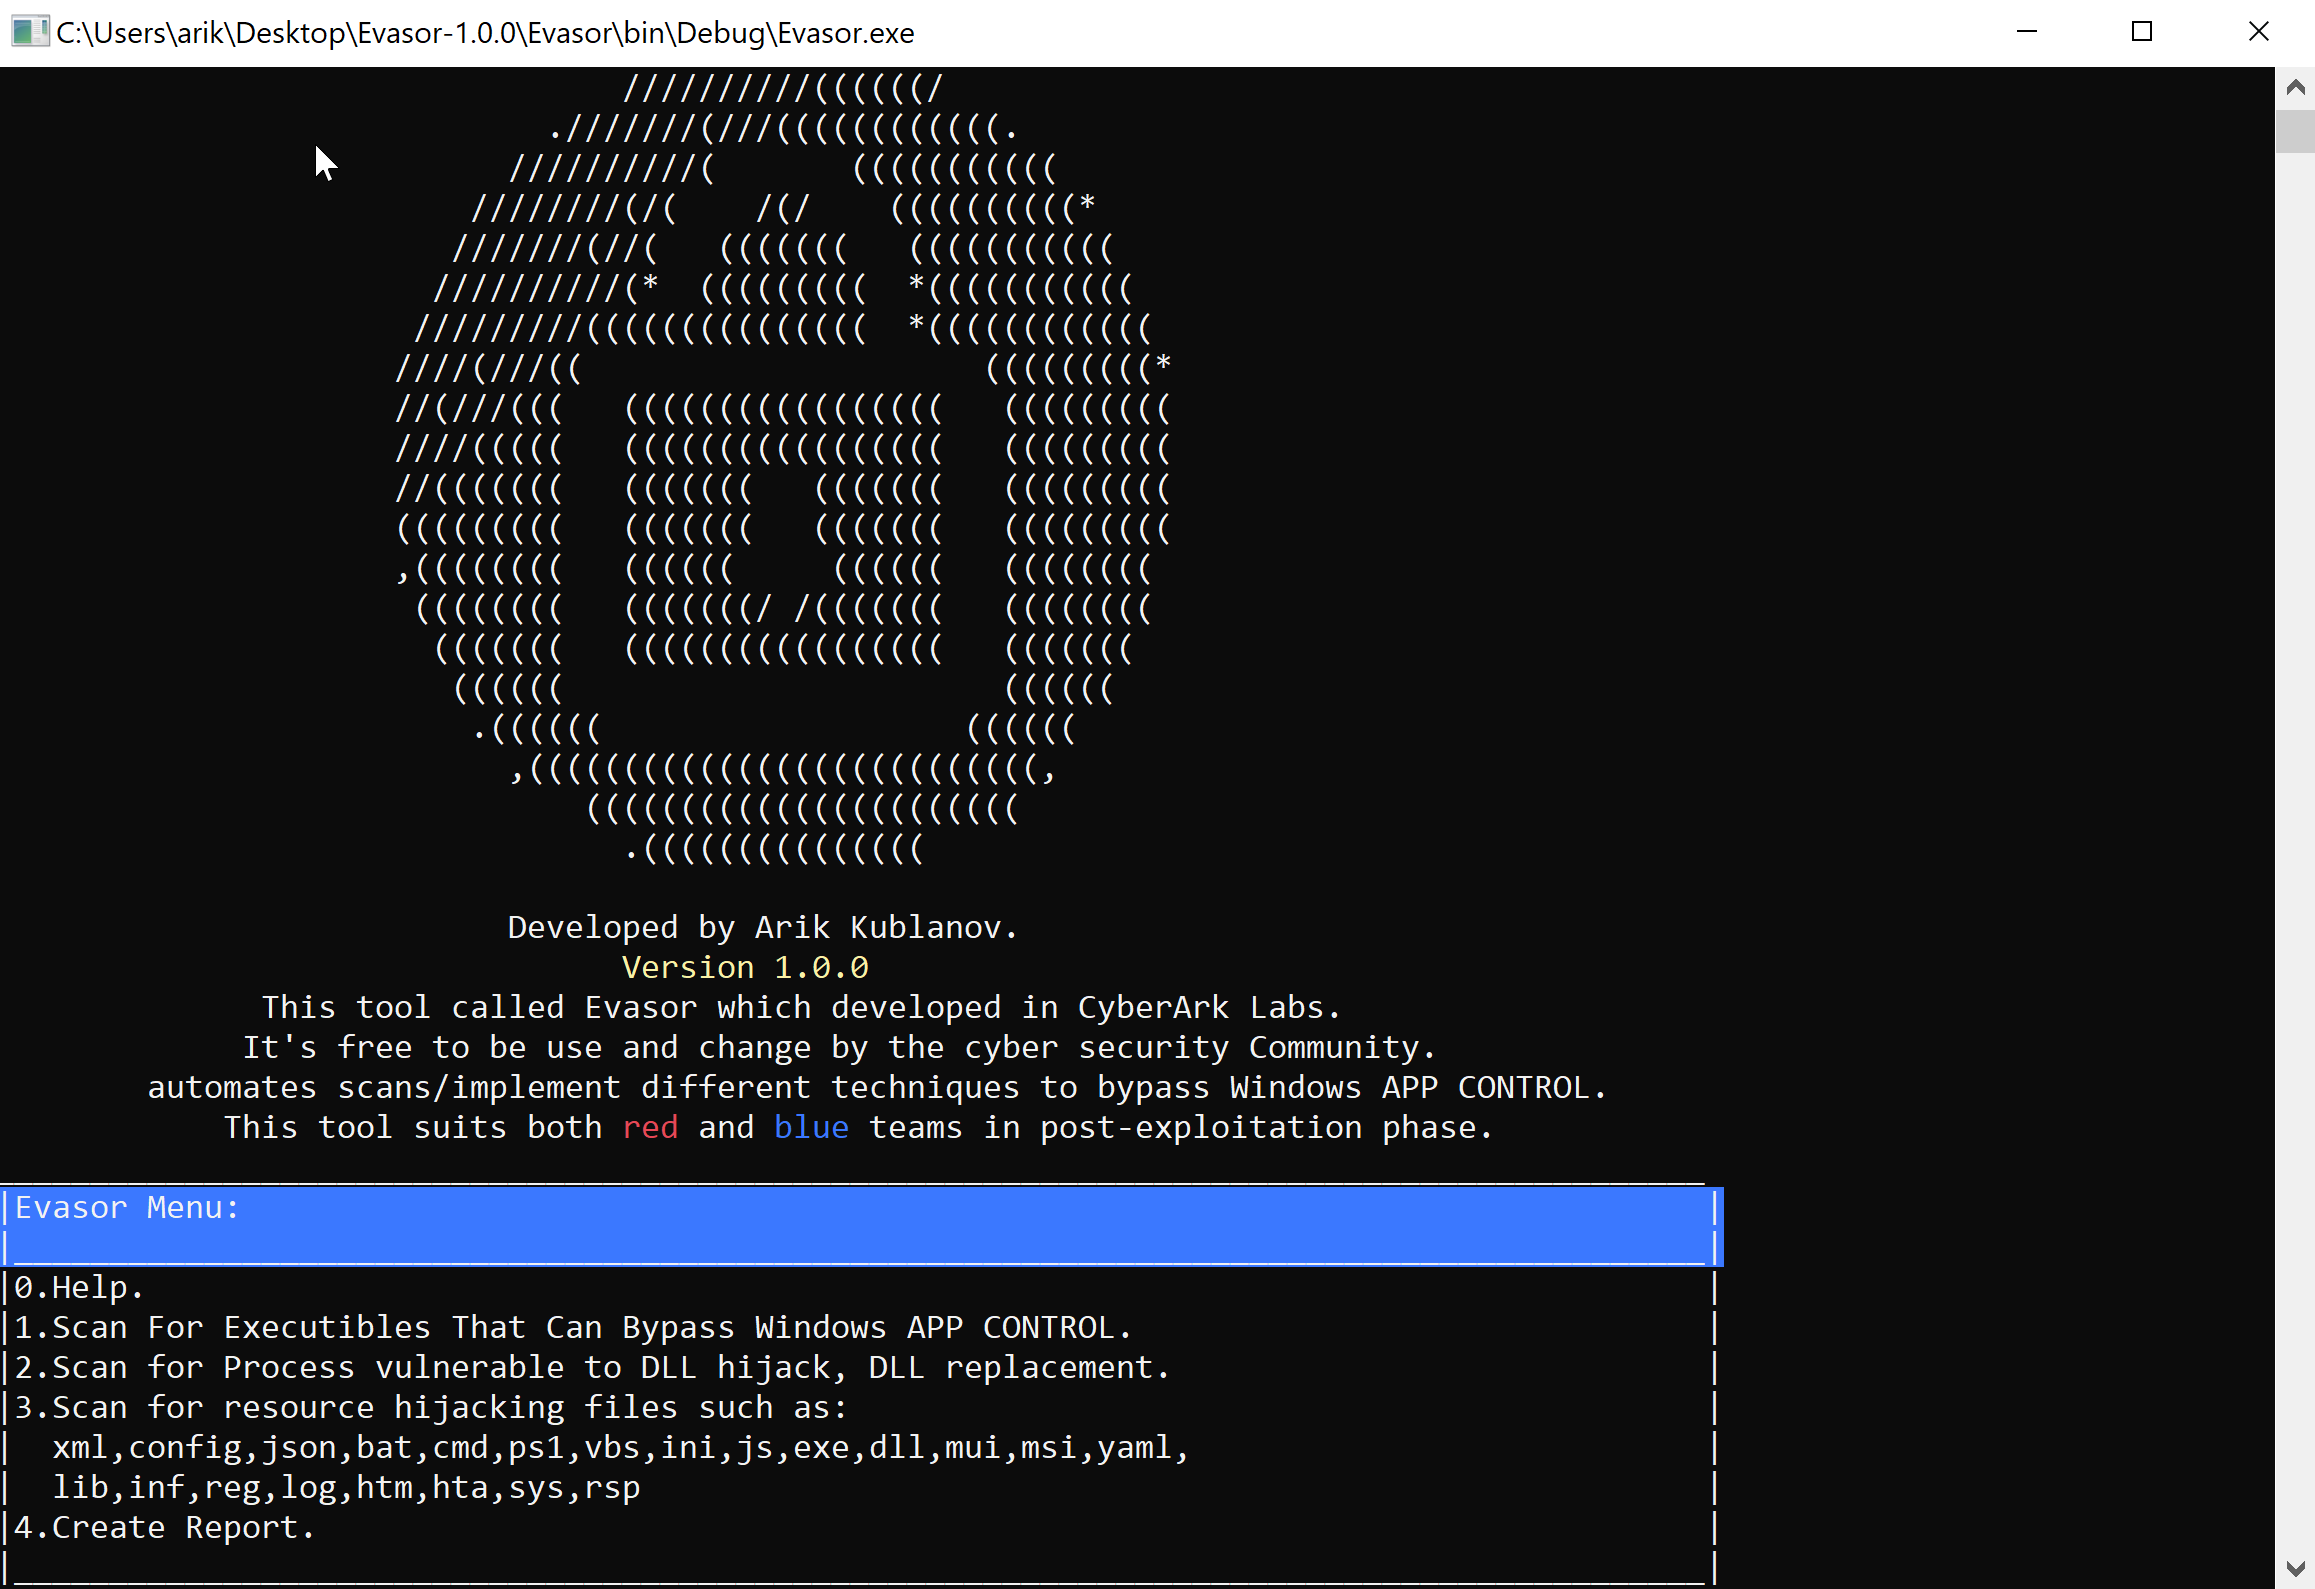 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 jonathansalwan/ropgadget
Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 baiduxlab/sgxray
Automated reasoning tool based on the SMACK verifier that detects SGX enclave bugs from trusted boundary violations, including invalid pointer…
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
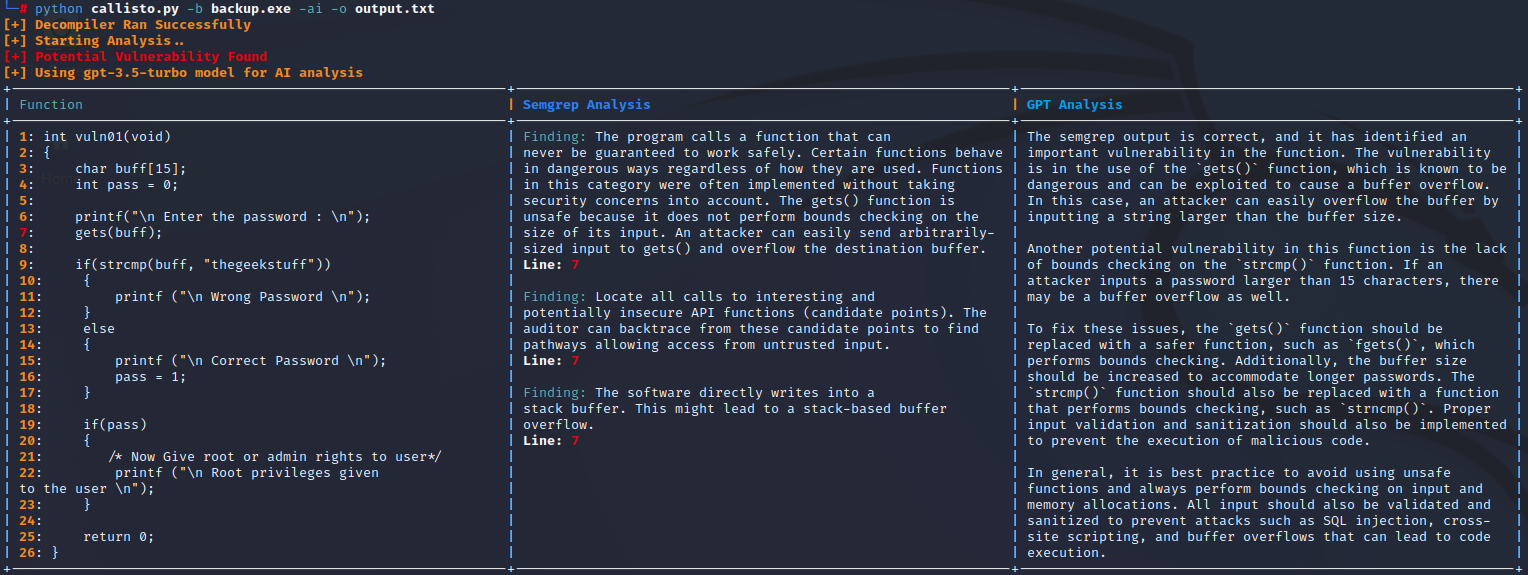 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 ideaslocas/adll
Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…