
Bypass-Sandbox-Evasion
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
anti-botbinary-analysisids-ips-evasion+1
140
zeromemoryex/bypass-sandbox-evasionC++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 kyxiaxiang/360wfp_exploit
BYOVD: Use 360 WFP driver to block EDR/XDR network connection.
 kudaes/dinvoke_rs
Dynamically invoke arbitrary unmanaged code
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
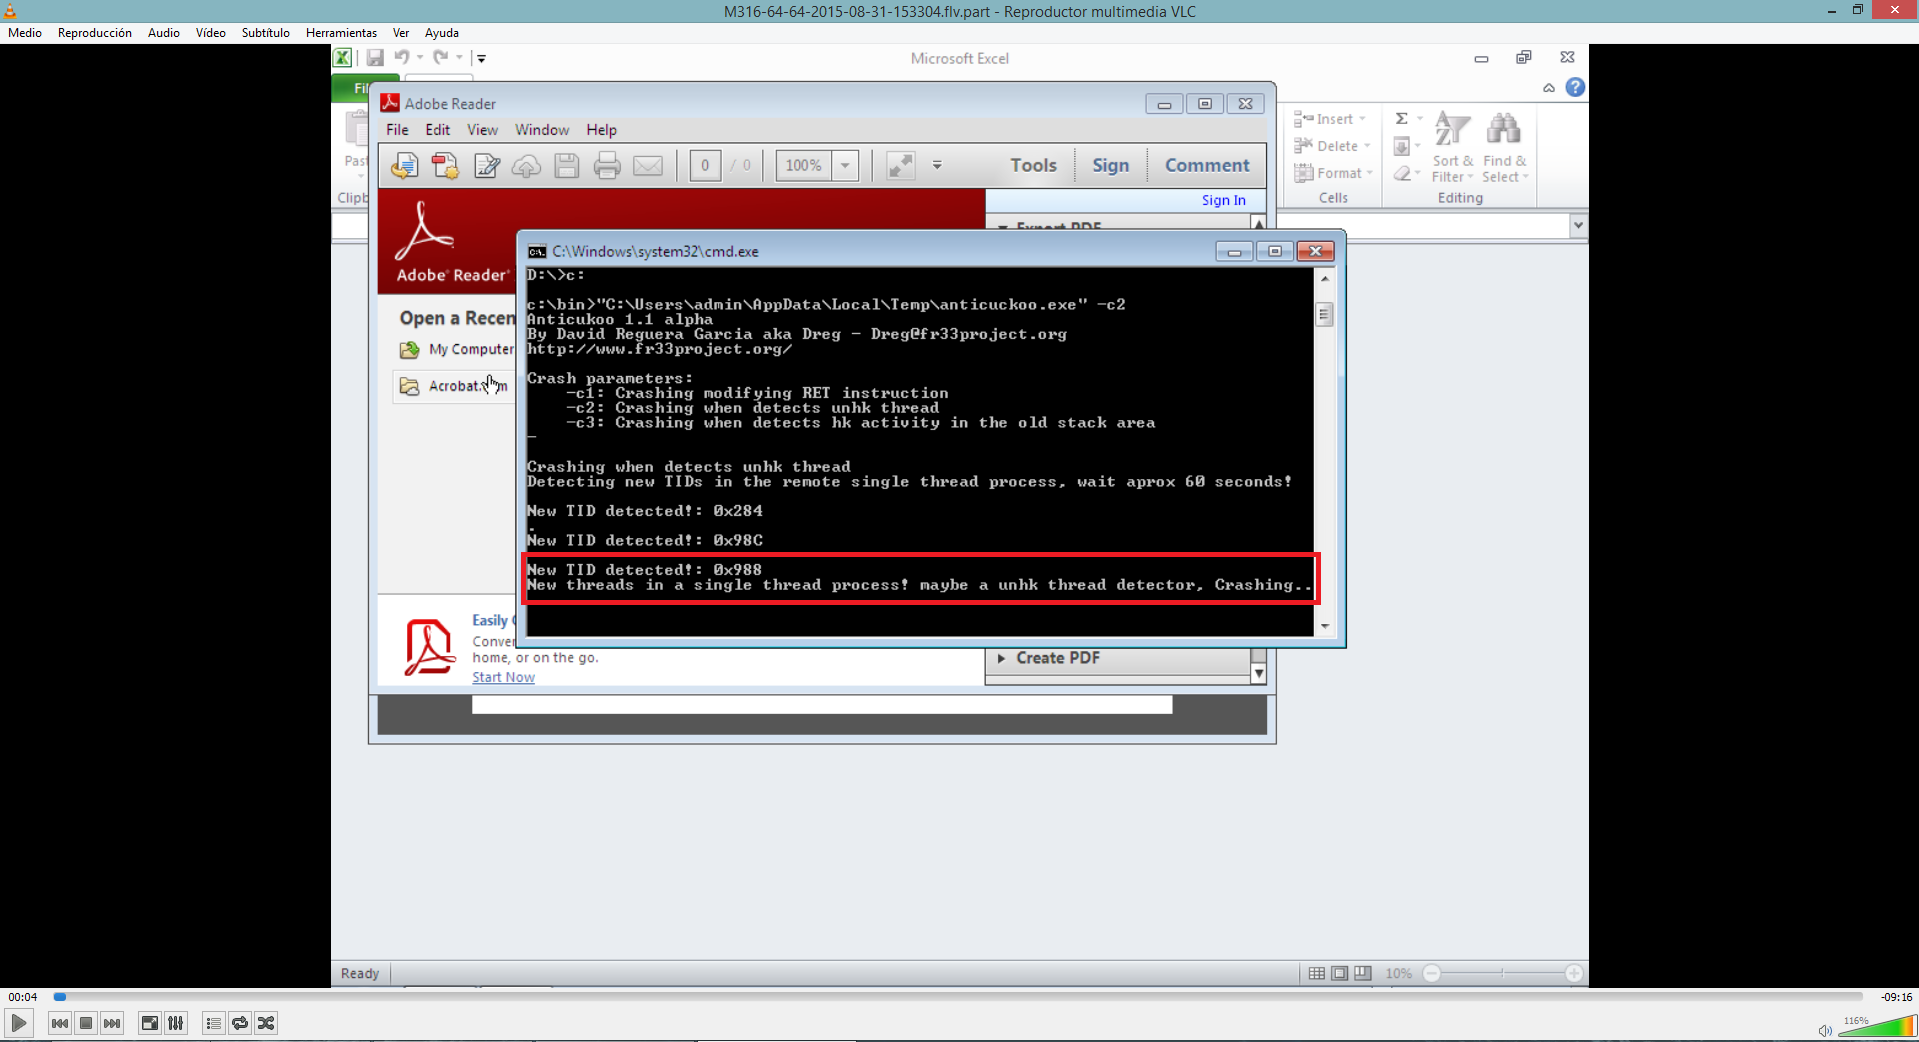 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 hardenedlinux/userland-exec
Userland exec PoC to be used as attack vector technique
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 cenobyte-vincit/dyen
In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…
 gmh5225/no-access-protection-x86
It encrypts the text section and set the protection to NO_ACCESS.
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
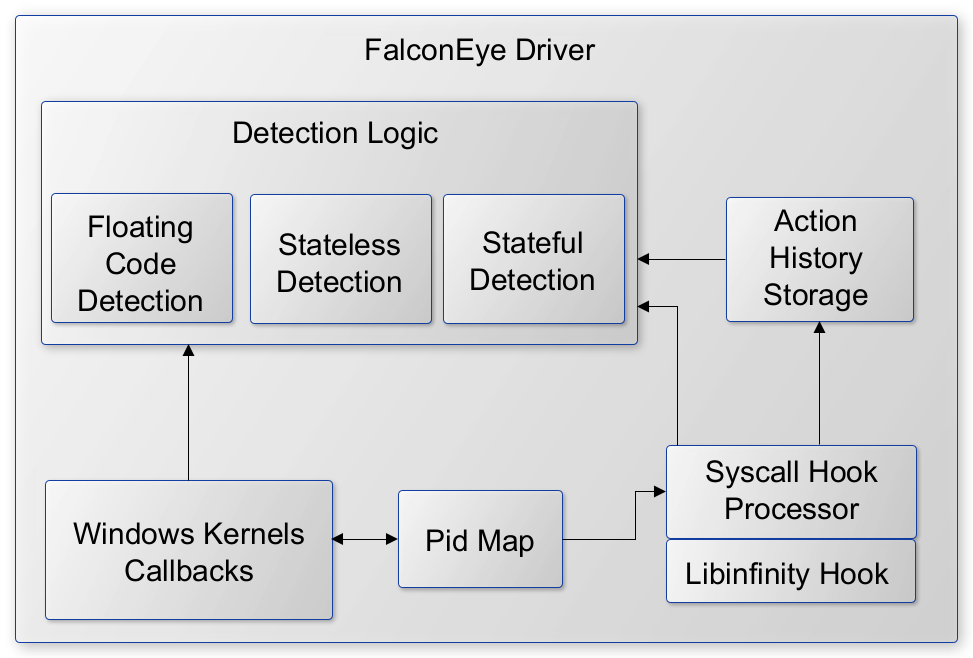 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
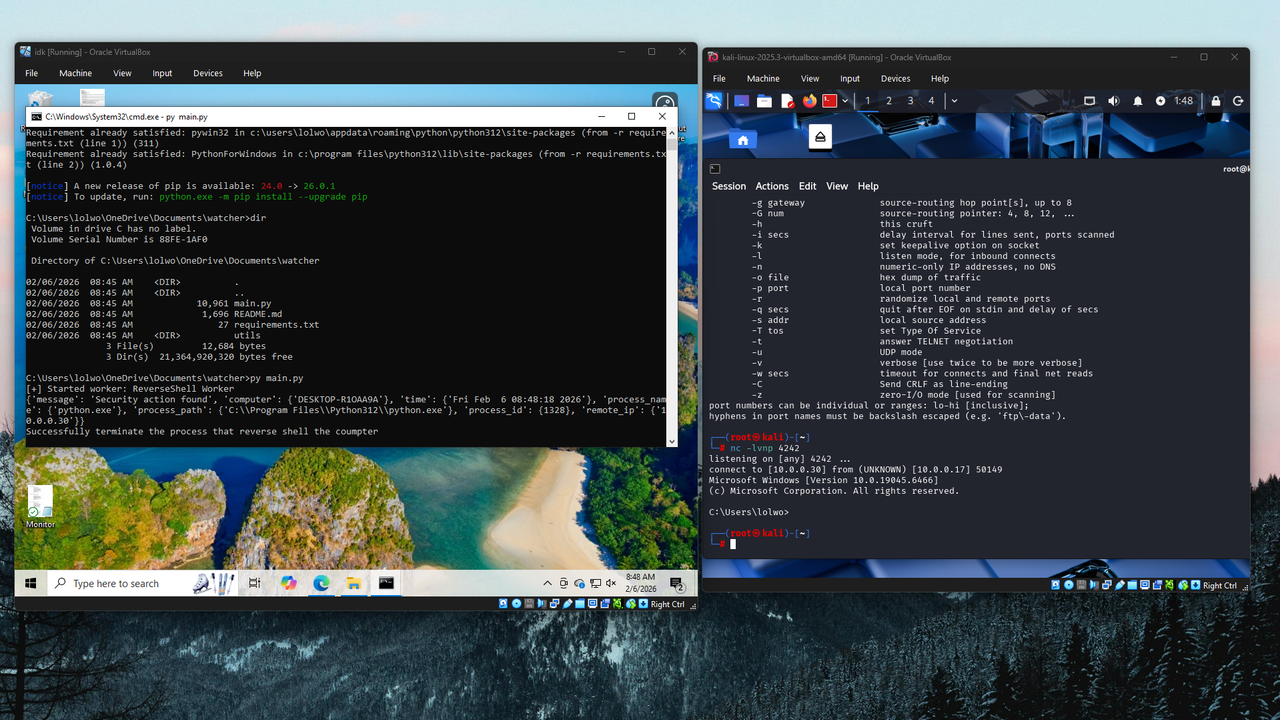 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 corelight/zeek-elf
A Zeek ELF File Analyzer