
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
39 results
GoRedOps preview
Archived

GoRedOps

GitHubkiexitdispatcher/goredops

🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…

anti-botbinary-analysiscommand-and-control+9
670
1 year ago
OmniSec-Hex preview

OmniSec-Hex

GitHubvighnesh91/omnisec-hex

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…

ai-securitybinary-analysisfuzzing+9
16 days ago
T3MP3ST preview

T3MP3ST

GitHubelder-plinius/t3mp3st

autonomous red teaming platform; multi-agent offensive-security meta-harness
ai-securitybinary-analysiscloud-security+9
6.3k19 days ago
RedTeamCCode preview

RedTeamCCode

GitHubmr-un1k0d3r/redteamccode

Red Team C code repo

binary-analysisdefensive-toolsmalware-analysis+1
5751 year ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
binary-analysiscurated-resourcesids-ips-evasion+3
2.2k5 months ago
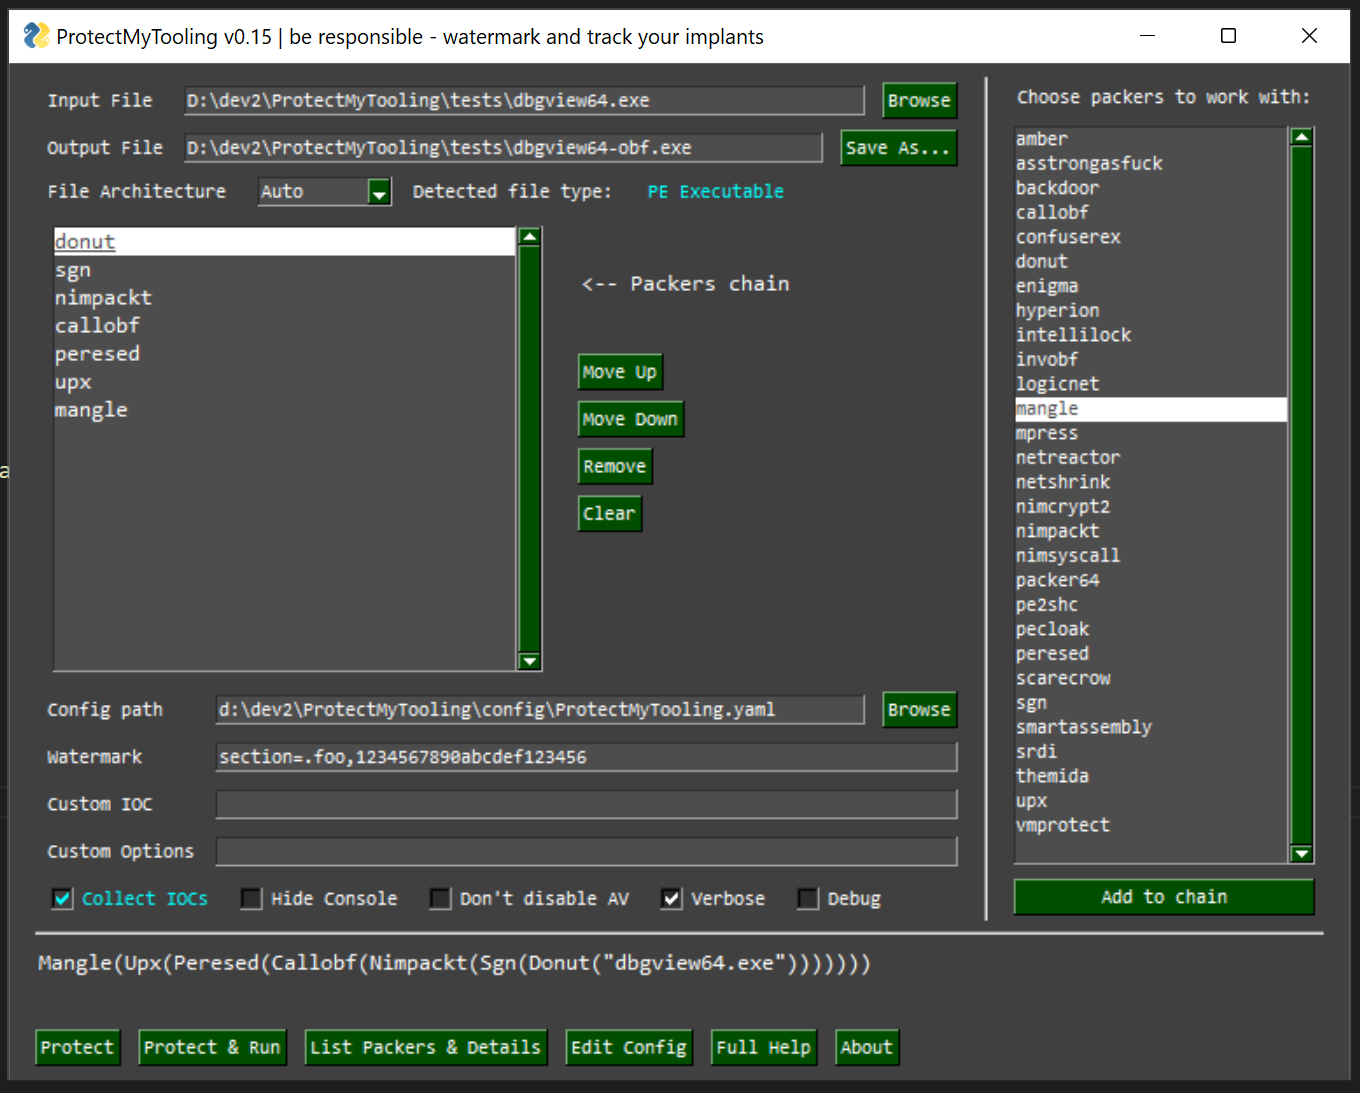
ProtectMyTooling preview

ProtectMyTooling

GitHubmgeeky/protectmytooling

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…
binary-analysisexploit-frameworksioc-management+5
1.1k11 months ago
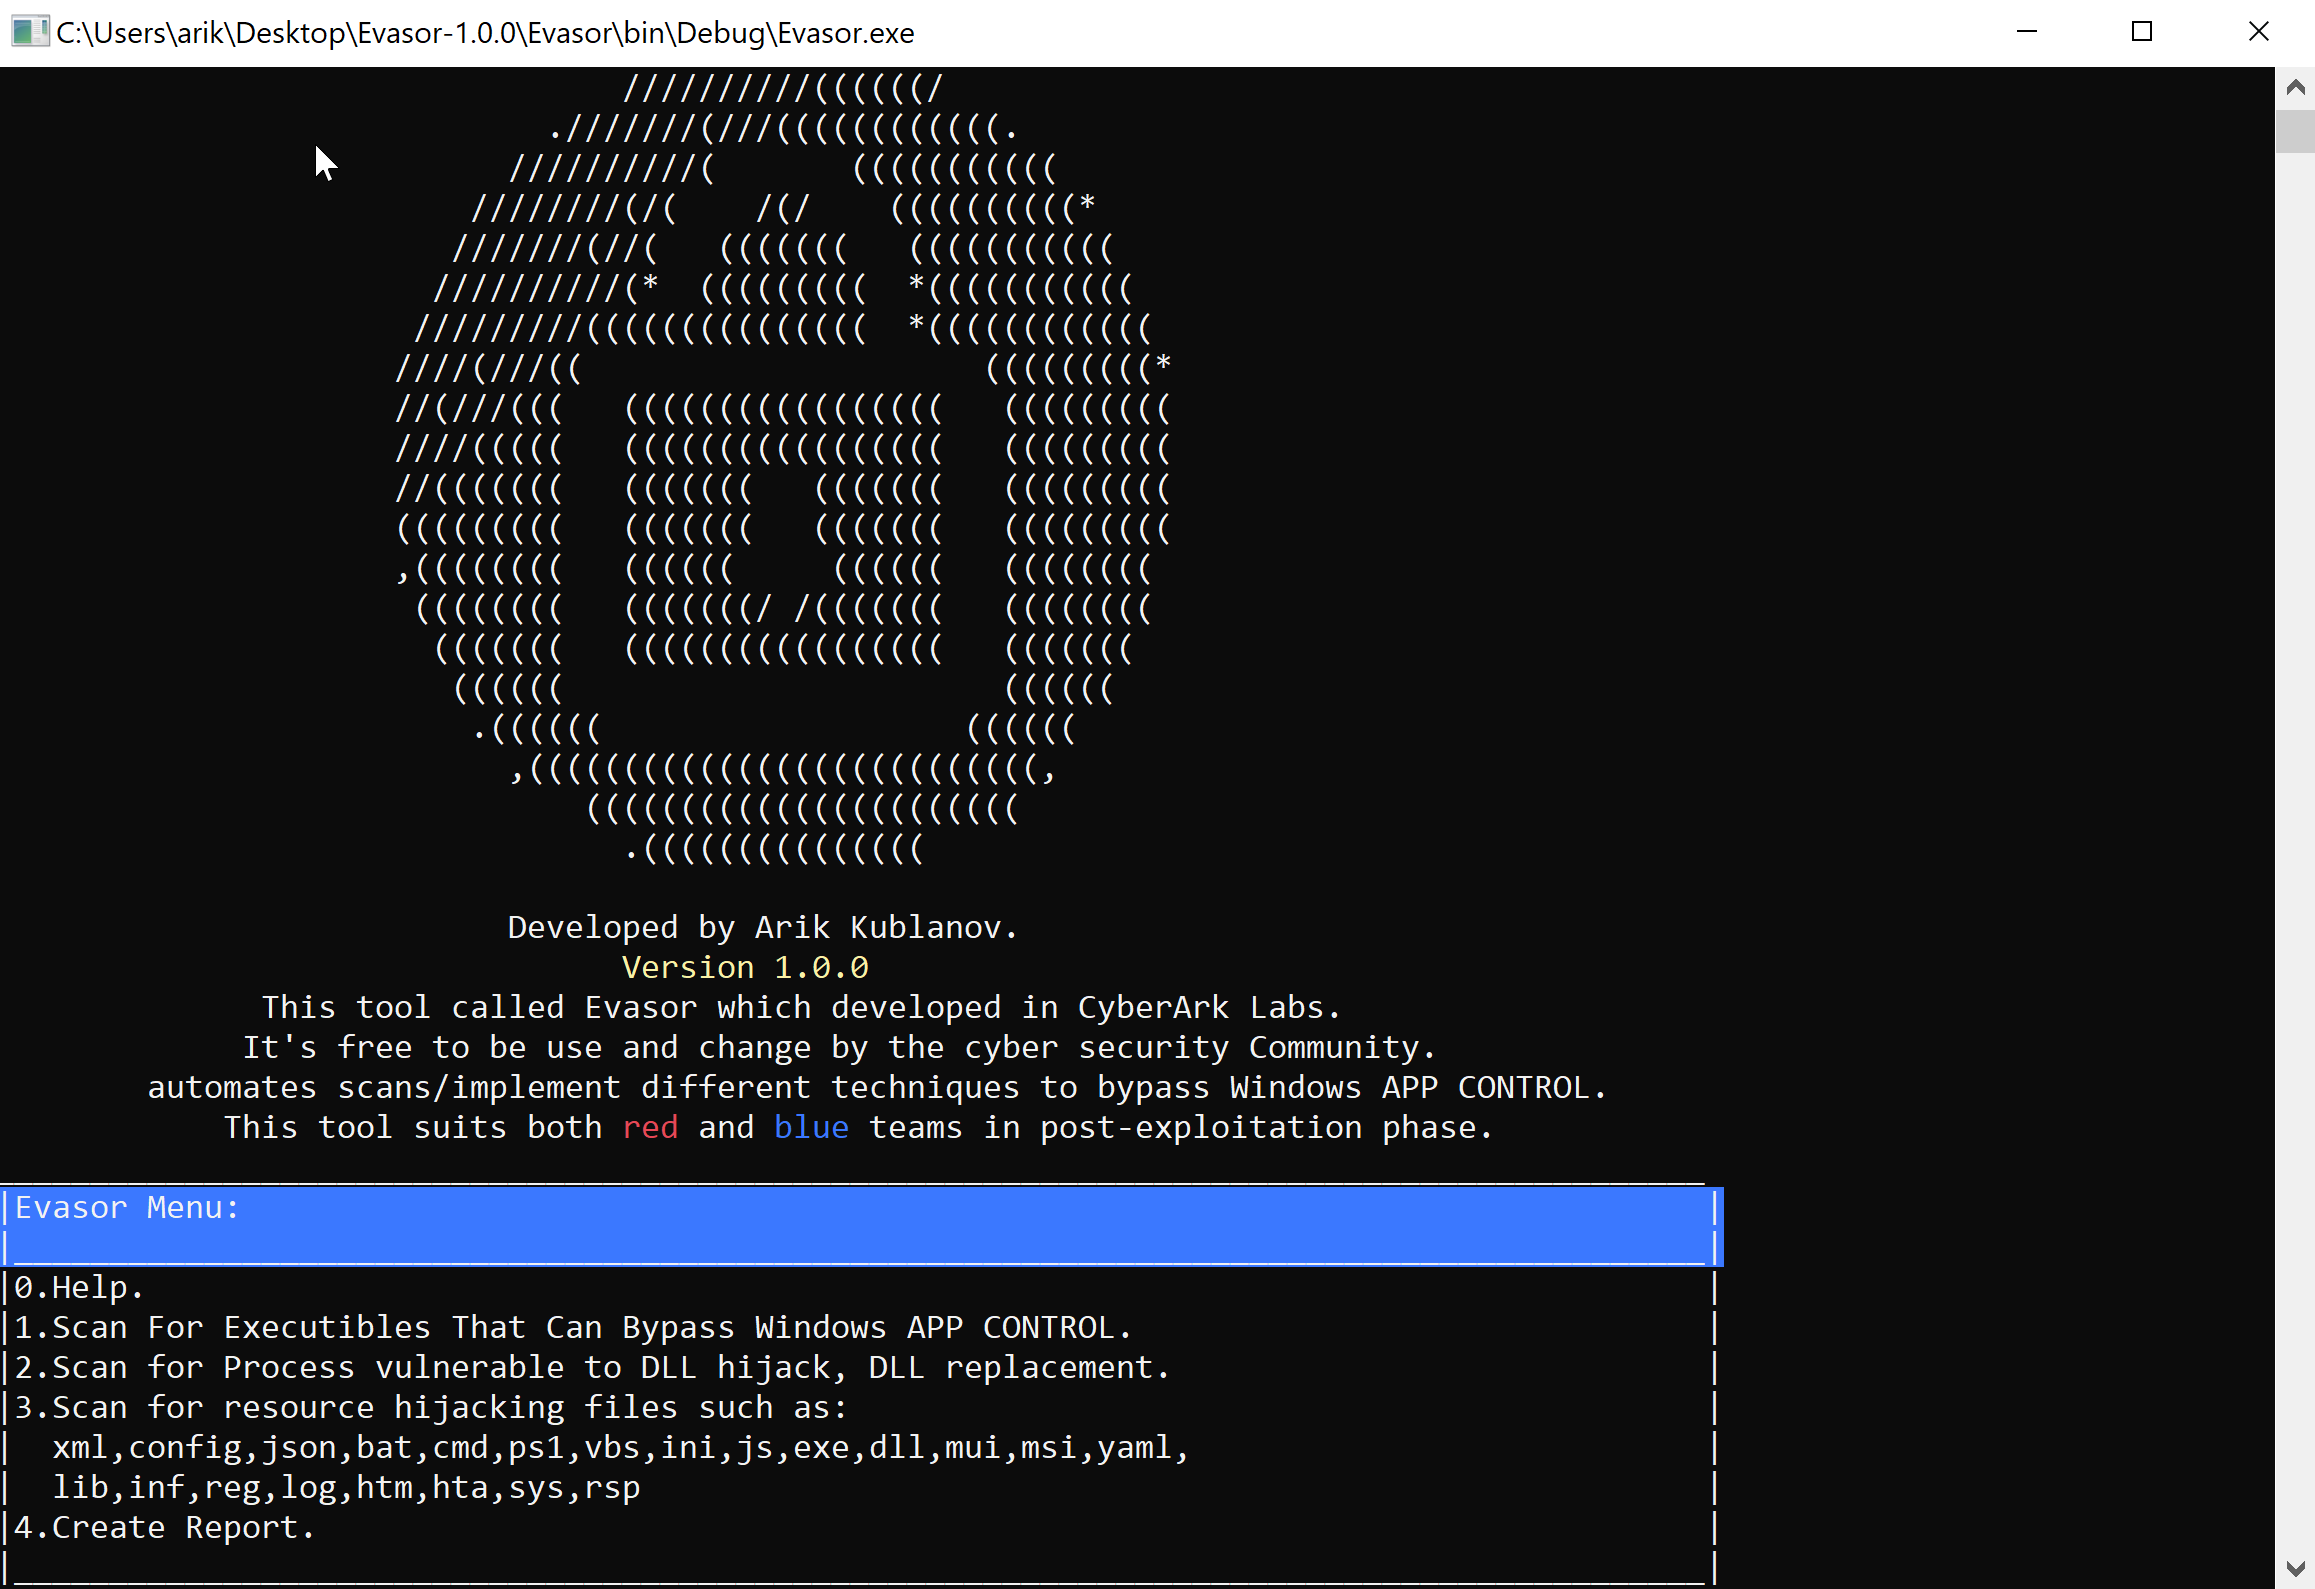
Evasor preview

Evasor

GitHubcyberark/evasor

A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
binary-analysisdefensive-toolspenetration-testing+3
3266 years ago
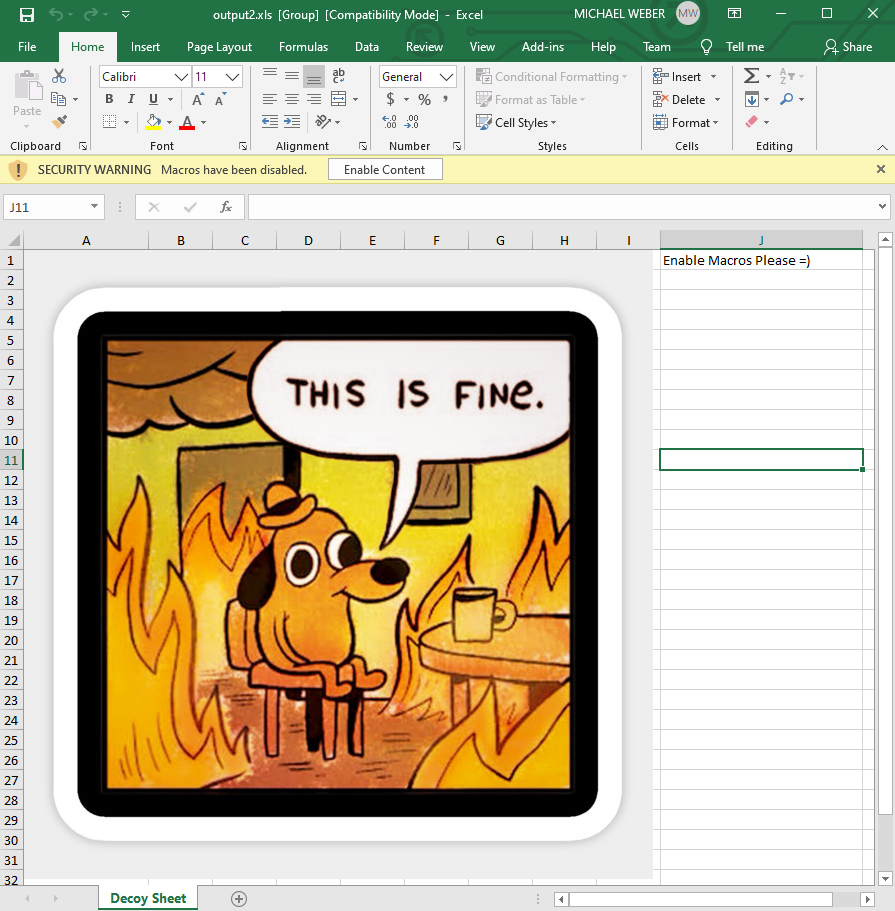
Macrome preview

Macrome

GitHubmichaelweber/macrome

Excel Macro Document Reader/Writer for Red Teamers & Analysts

binary-analysisexploitationmalware-analysis+5
5234 years ago
Scanners-Box preview

Scanners-Box

GitHubwe5ter/scanners-box

The Ultimate Open-Source Security Arsenal for Hackers, Enterprises, and AI Agents——面向极客、企业与 AI 智能体的全域开源网络安全工具矩阵
ai-securitybinary-analysiscurated-resources+6
9.1k3 days ago
rtx-cve-2023-45779 preview

rtx-cve-2023-45779

GitHubmetaredteam/rtx-cve-2023-45779

Proof-of-concept code for Android APEX key reuse vulnerability
android-securitybinary-analysisexploitation+3
1092 years ago
reverse-skill preview

reverse-skill

GitHubzhaoxuya520/reverse-skill

AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
ai-securitybinary-analysisctf+8
38.3k5 days ago
CyberStrikeAI preview

CyberStrikeAI

GitHubed1s0nz/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…

ai-securitybinary-analysiscloud-security+9
7.0k2 days ago
CyberStrikeAI preview

CyberStrikeAI

GitHubaipentest/cyberstrikeai

The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+8
7.0k9 days ago
fickling preview

fickling

GitHubtrailofbits/fickling

A Python pickling decompiler and static analyzer
ai-securitybinary-analysiscode-analysis+5
6708 days ago
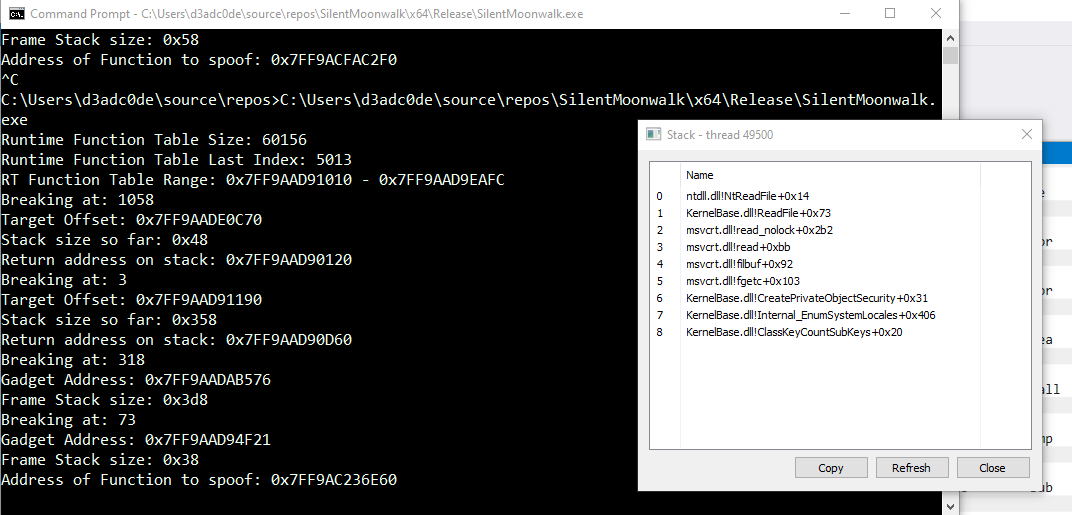
SilentMoonwalk preview

SilentMoonwalk

GitHubklezvirus/silentmoonwalk

PoC Implementation of a fully dynamic call stack spoofer
binary-analysisexploitationpayload-development+2
9972 years ago
nCPU preview

nCPU

GitHubrobertcprice/ncpu

Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
ai-securitybinary-analysiscryptography+8
6582 months ago
sharem preview

sharem

GitHubbw3ll/sharem

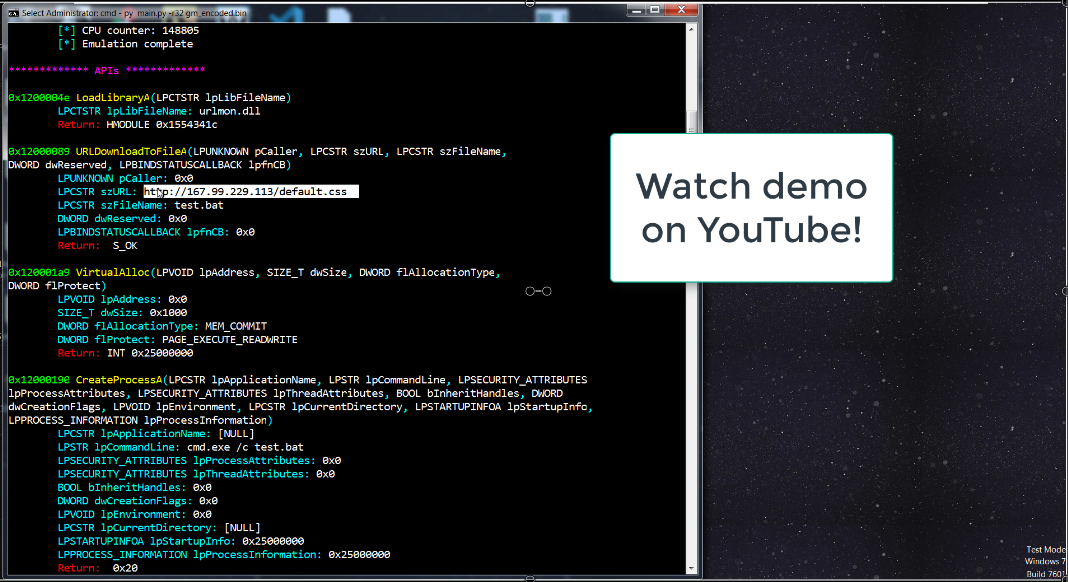
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4936 months ago
ane preview

ane

GitHubeiln/ane

Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…

ai-securitybinary-analysisembedded-systems-security+3
5372 years ago
Previous123Next