
CVE-2024-20696
 clearbluejar/cve-2024-20696
Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…
binary-analysiseducationexploitation+3
8
clearbluejar/cve-2024-20696Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…
 uthrasri/framework_base_cve-2023-21285_nopatch
Android framework vulnerability analysis and exploitation demonstration for CVE-2023-21285, providing a no-patch test case for security researchers.
 sdneon/cvetest
Test case for Node.JS V0.10.31 v8 backport CVE-2013-6668 crash
 jianrongxiao-linksys/dnsmasq-cve-2026
Automated defect verification tool for 6 dnsmasq CVEs (CVE-2026-2291, 4890, 4891, 4892, 4893, 5172)
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 uds-se/formatfuzzer
Template-driven binary format fuzzer that generates and parses valid test inputs at high speed, with AFL++ integration for coverage-guided fuzzing.
 star-sg/v8harvest
Curated dashboard for browsing recent V8 vulnerability patterns, parsing regression test files with linked Chromium bug reports, code reviews, and…
 denuvosoftwaresolutions/gamba
Simplification of General Mixed Boolean-Arithmetic Expressions: GAMBA
 google/afl
american fuzzy lop - a security-oriented fuzzer
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 dantsco/cve-2025-64720-poc
Proof-of-concept exploit for CVE-2025-64720, a libpng buffer overflow in palette premultiplication. Includes exploit generator, test harness with…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
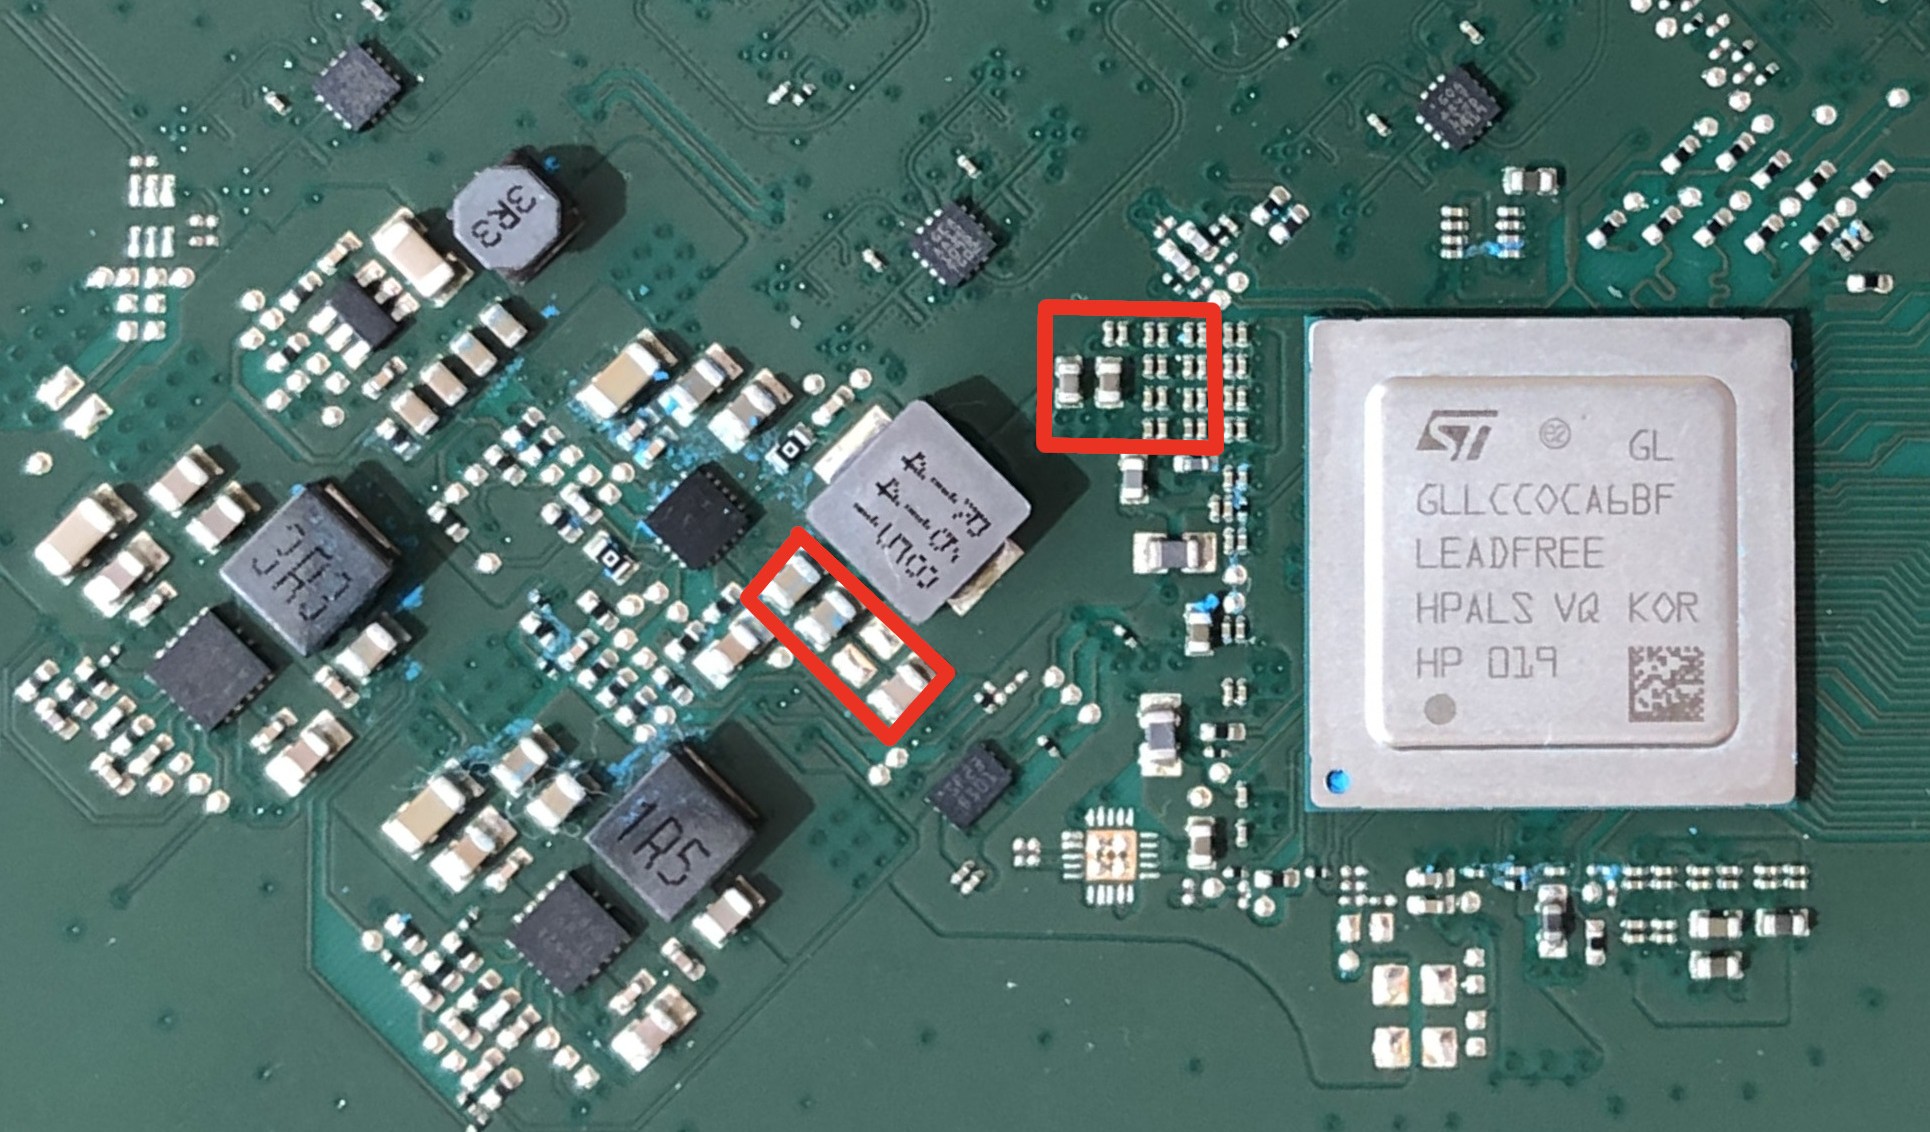 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 google/silifuzz
Fuzzes CPU implementations by generating test inputs from software proxies, then executes them on real hardware to detect microarchitecture defects…
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 chenzhuo0618/test
Proof-of-concept exploit for CVE-2017-1000117, demonstrating a remote code execution vulnerability in Git.
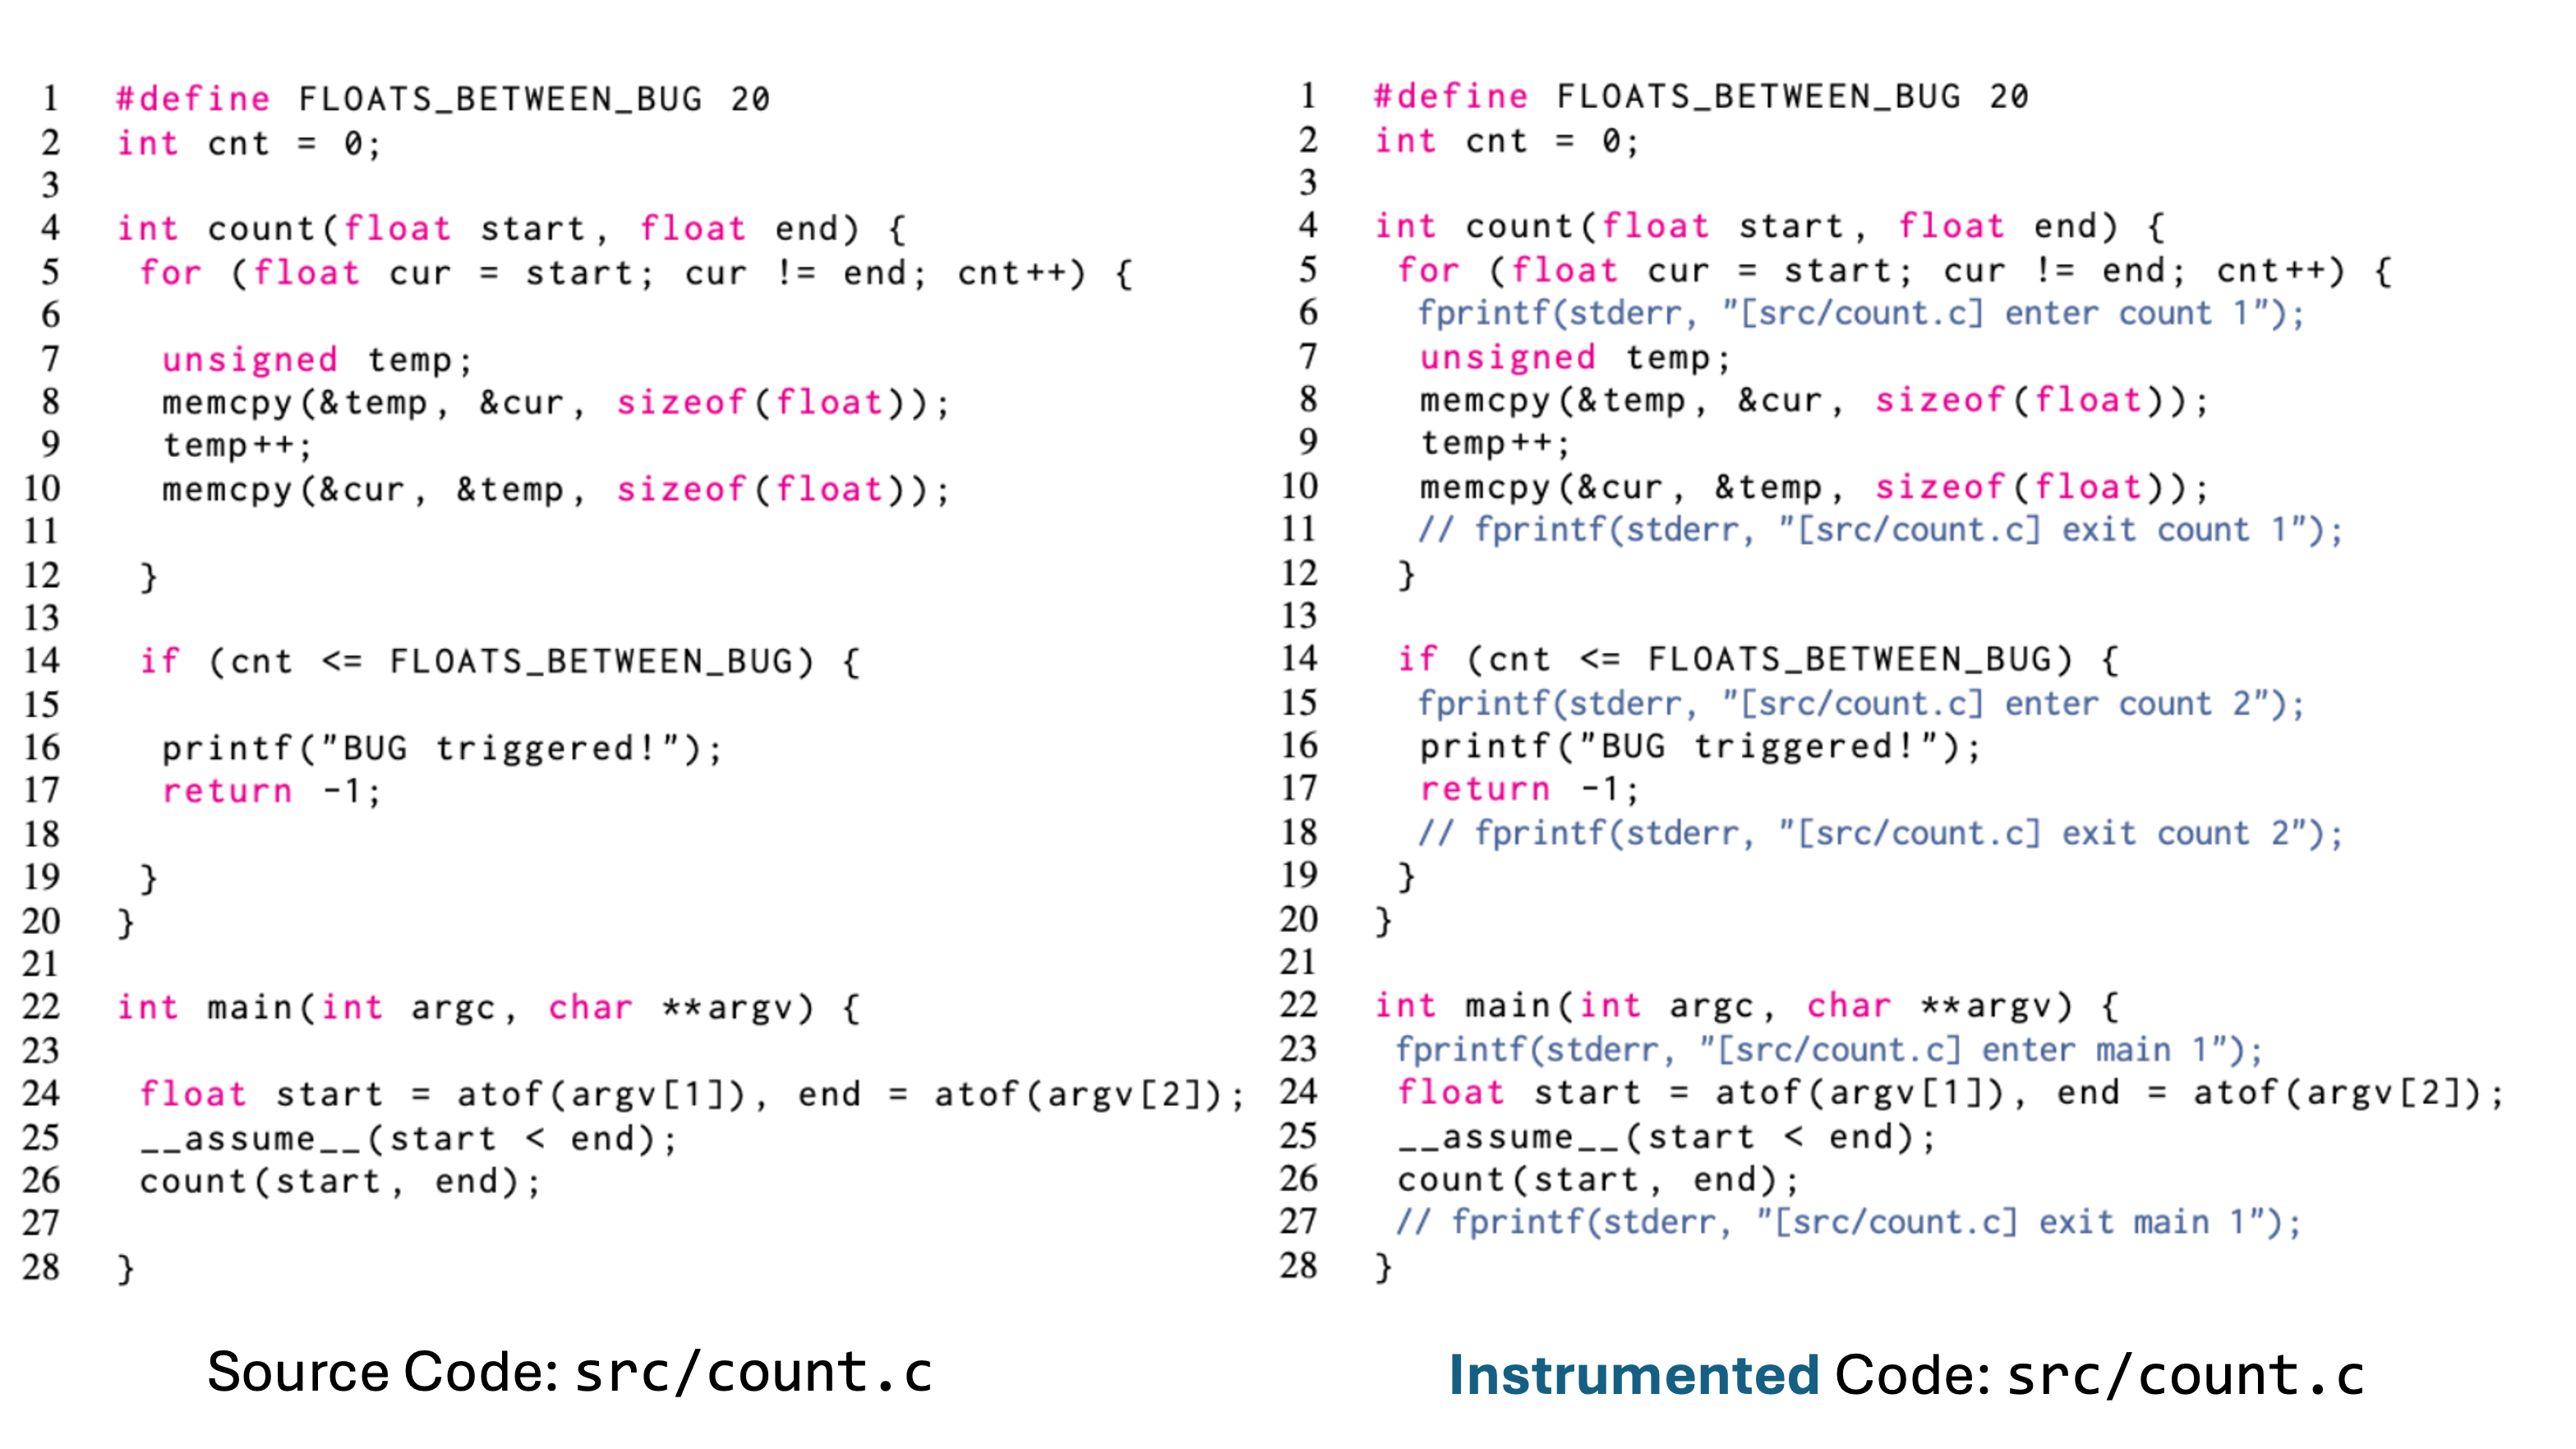 concollmic/concollmic
LLM-agent-powered concolic execution engine that instruments source code, summarizes path constraints in natural language, and generates test cases…