
draytek-arsenal
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
binary-analysisembedded-systems-securityfirmware-analysis+5
53
infobyte/draytek-arsenalReverse Engineering and Observability toolkit for Draytek firewalls
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
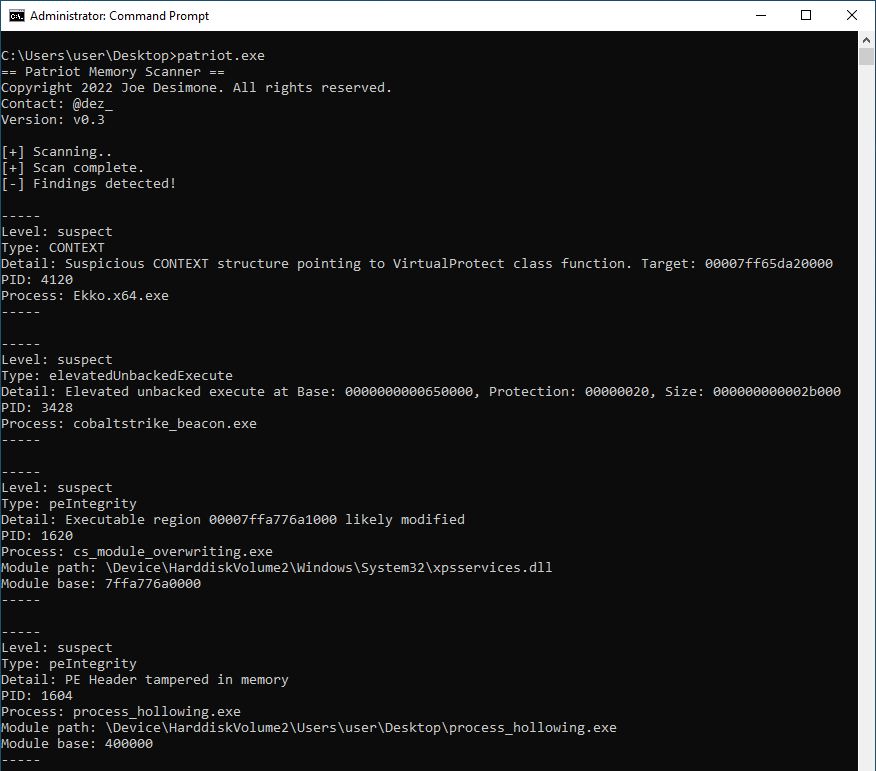 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
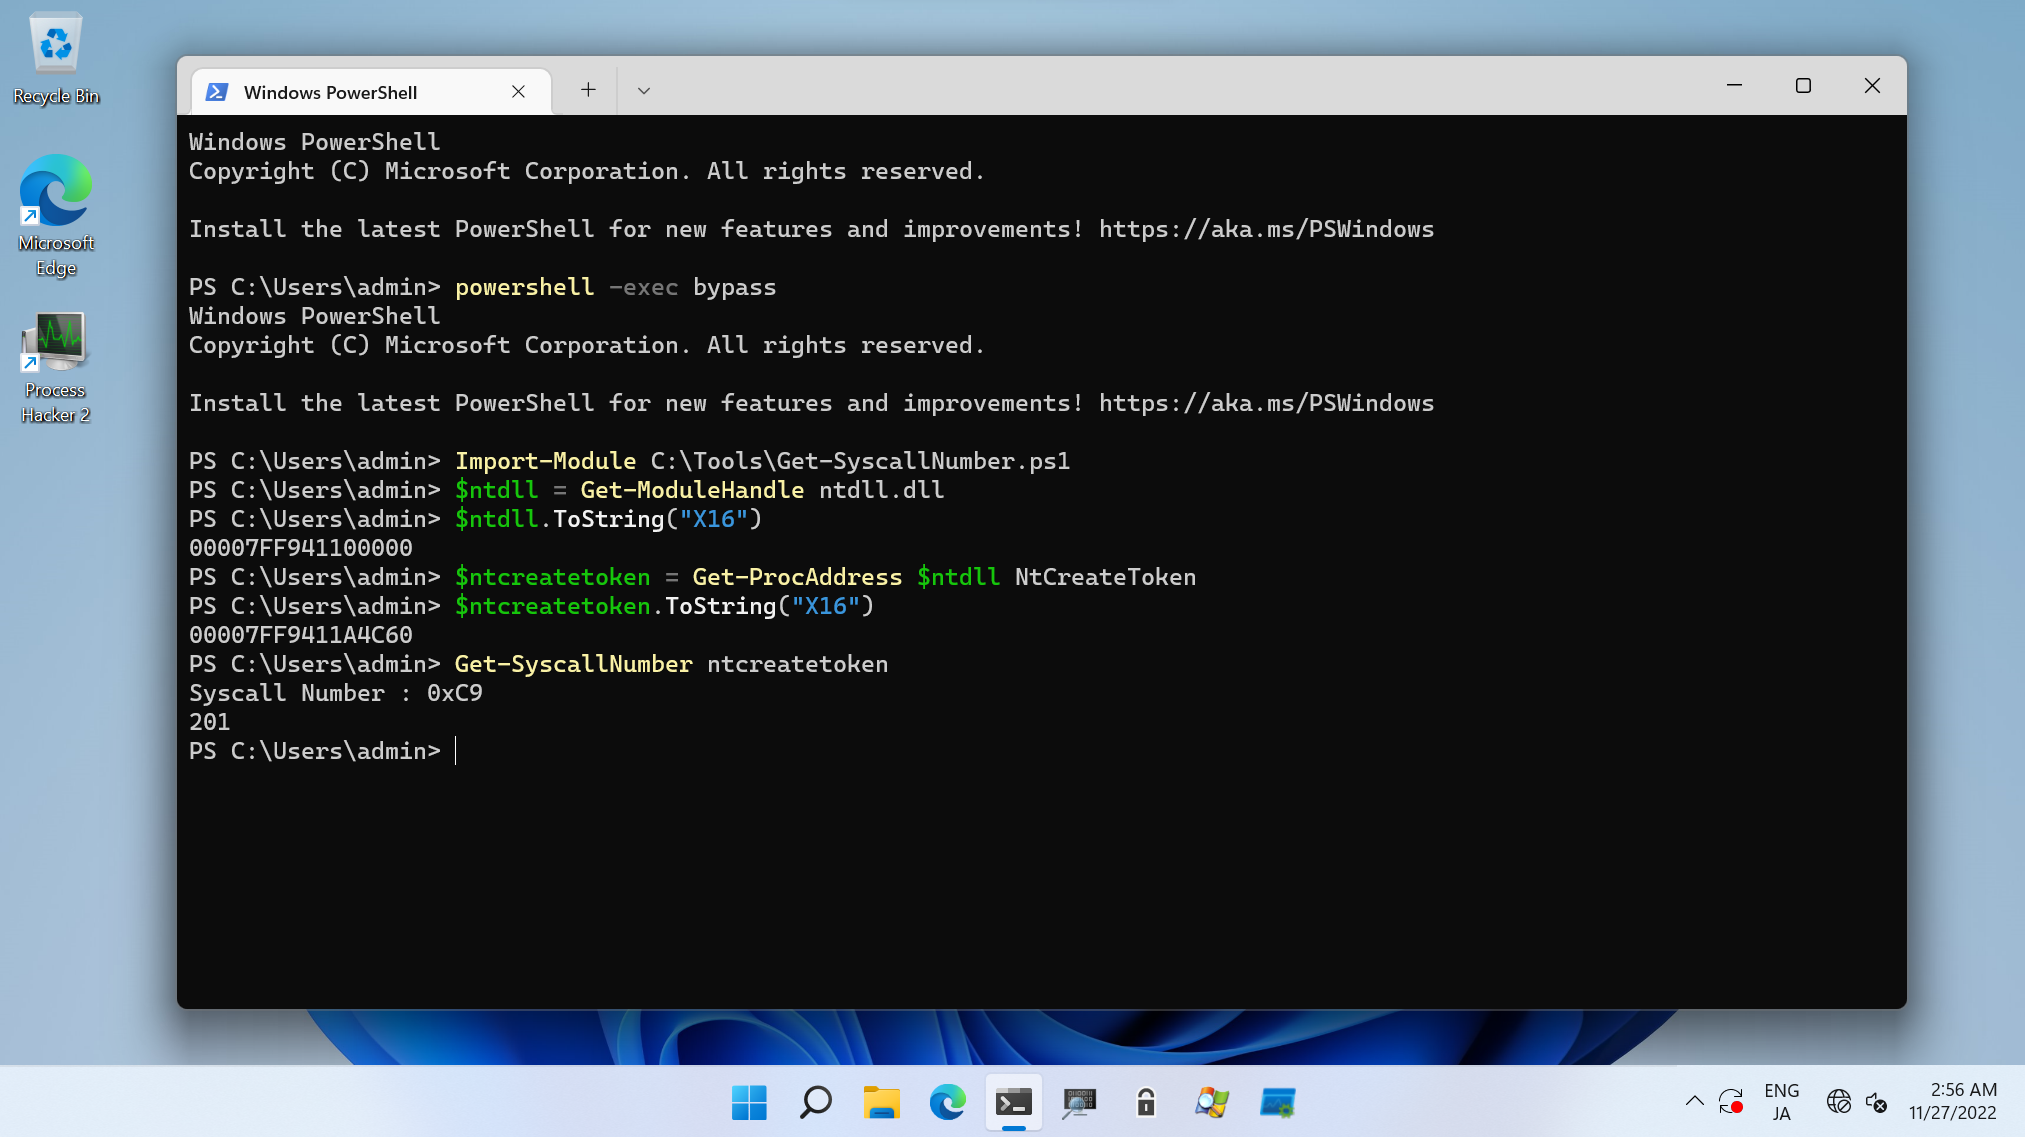 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
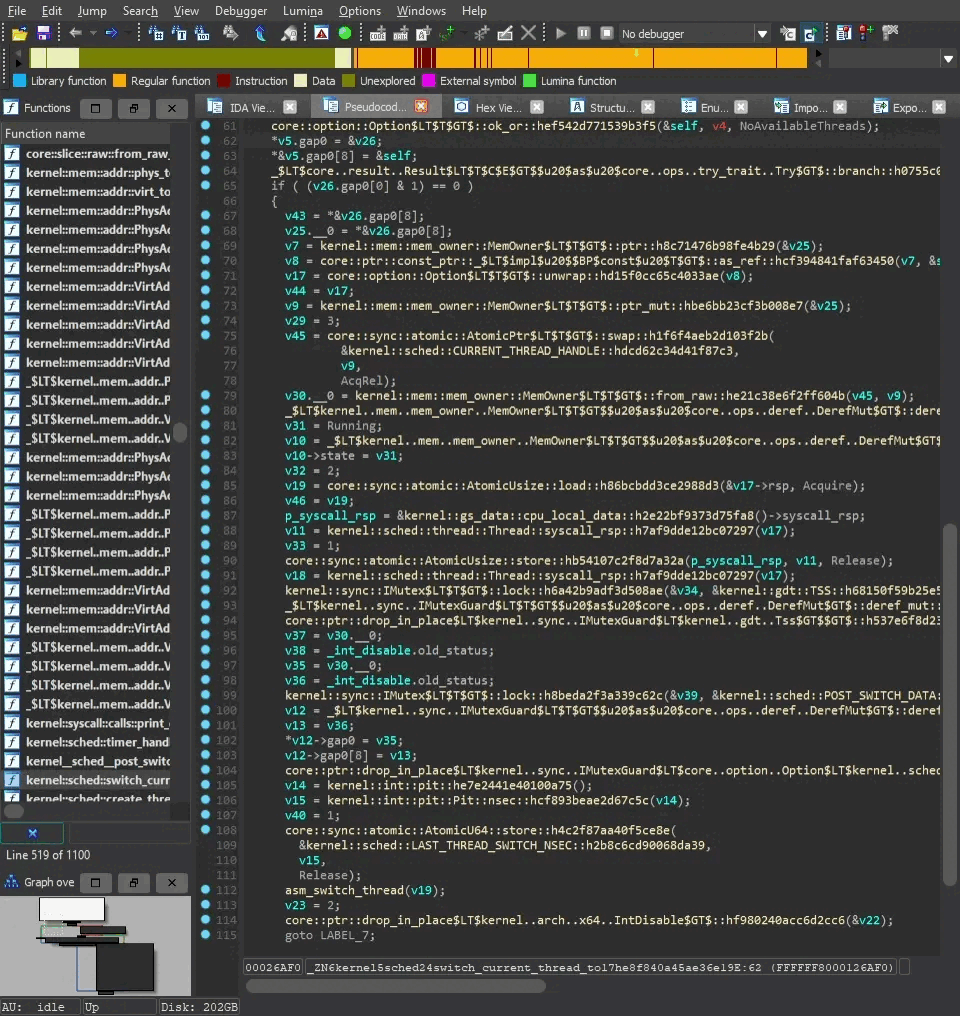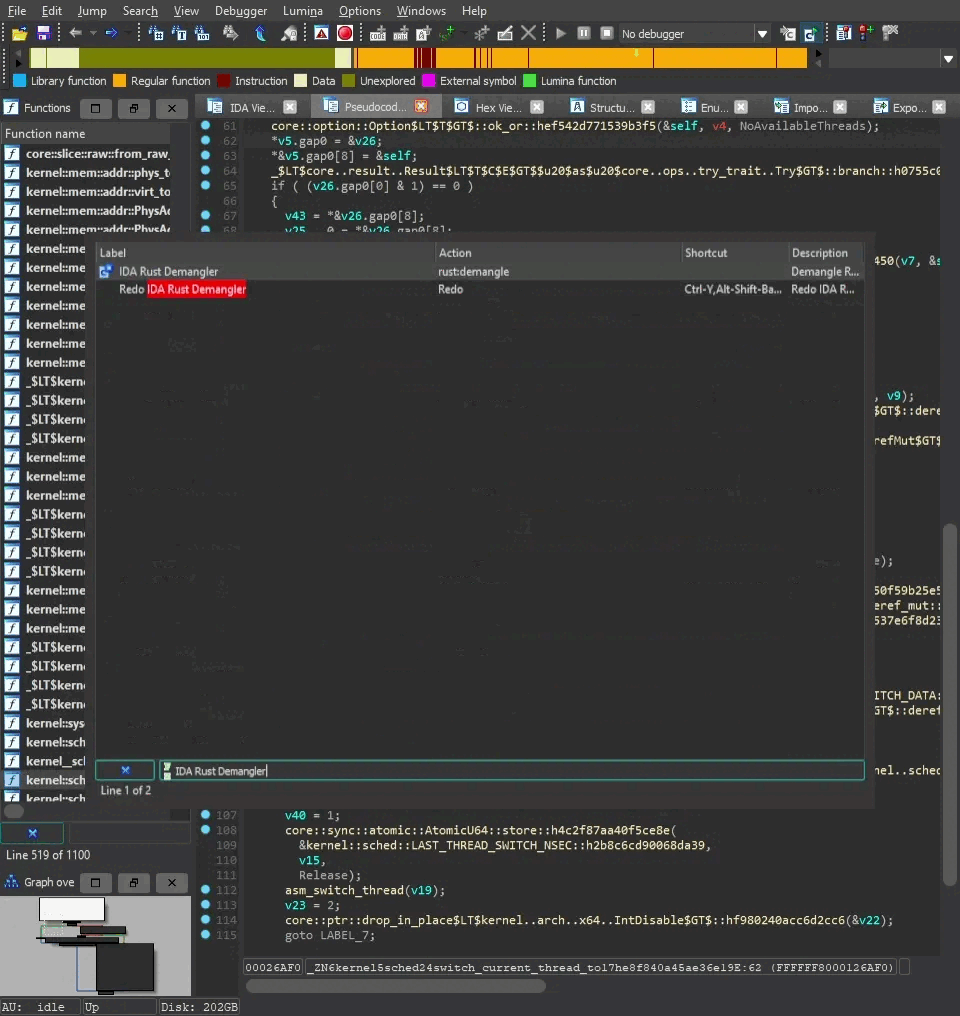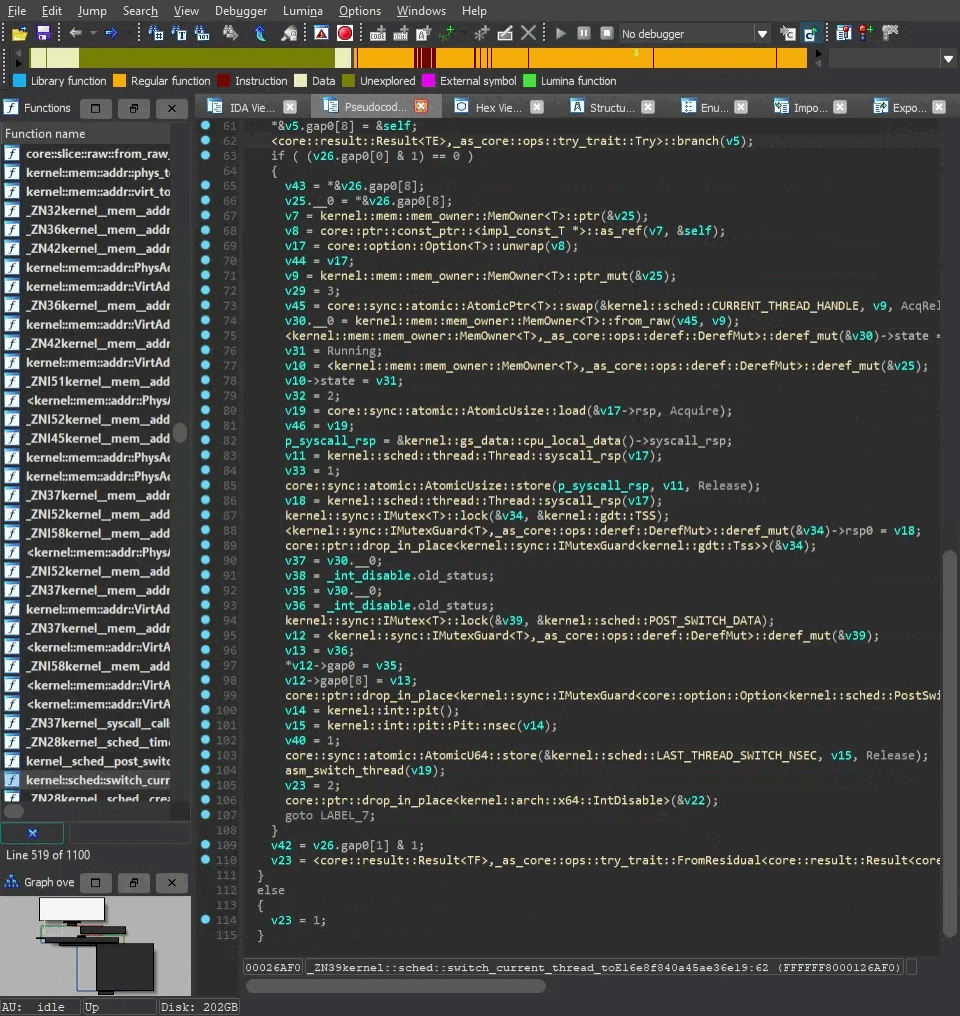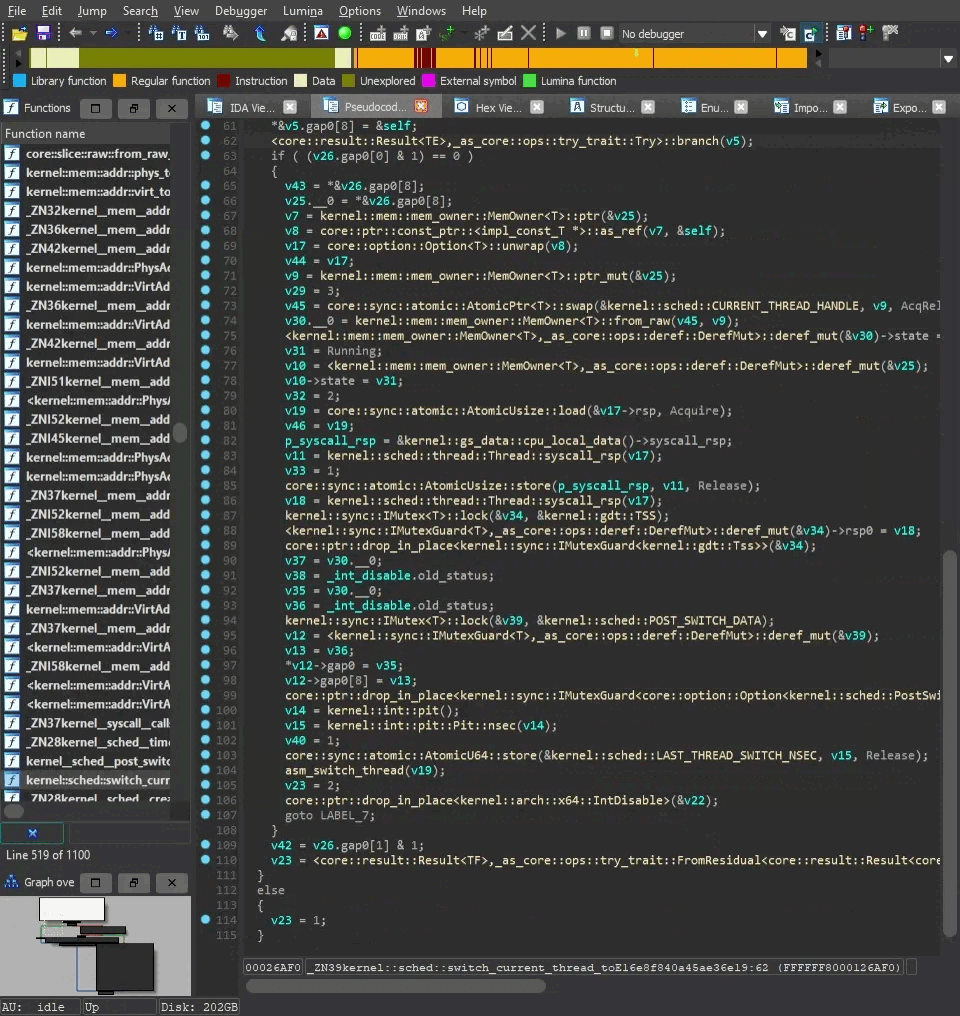 timetravelthree/idarustdemangler
Rust Demangler & Normalizer plugin for IDA
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
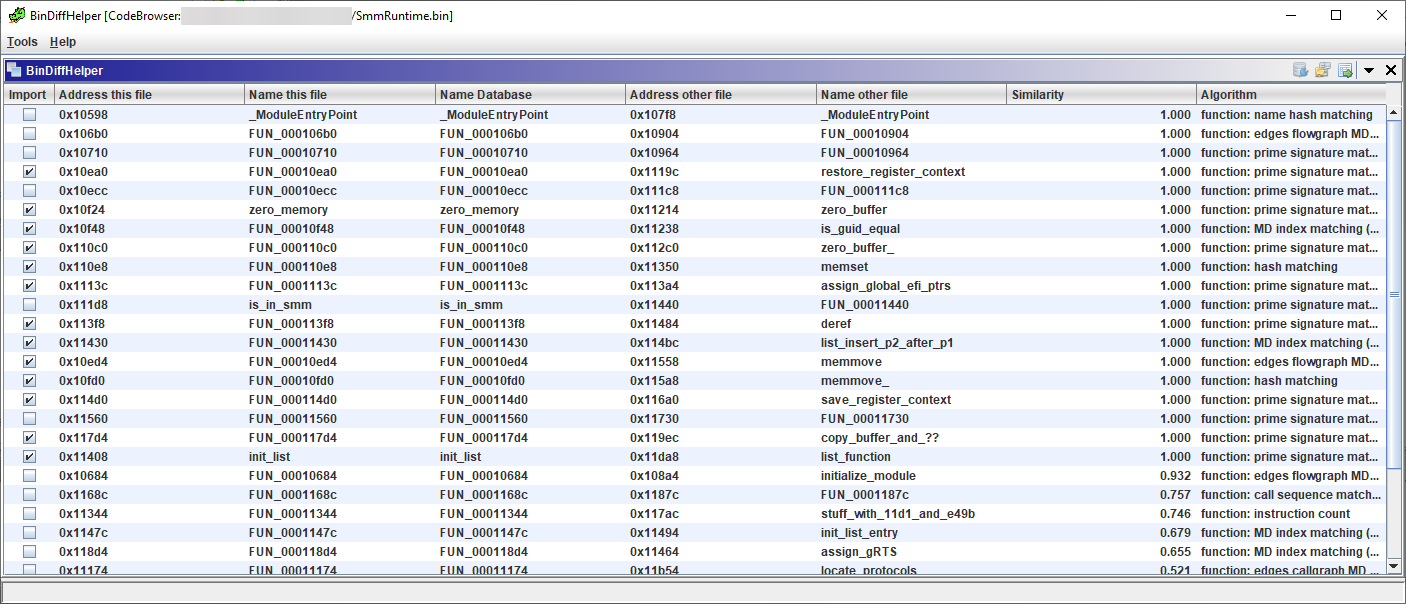 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
 secrary/infectpe
InfectPE - Inject custom code into PE file [This project is not maintained anymore]
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
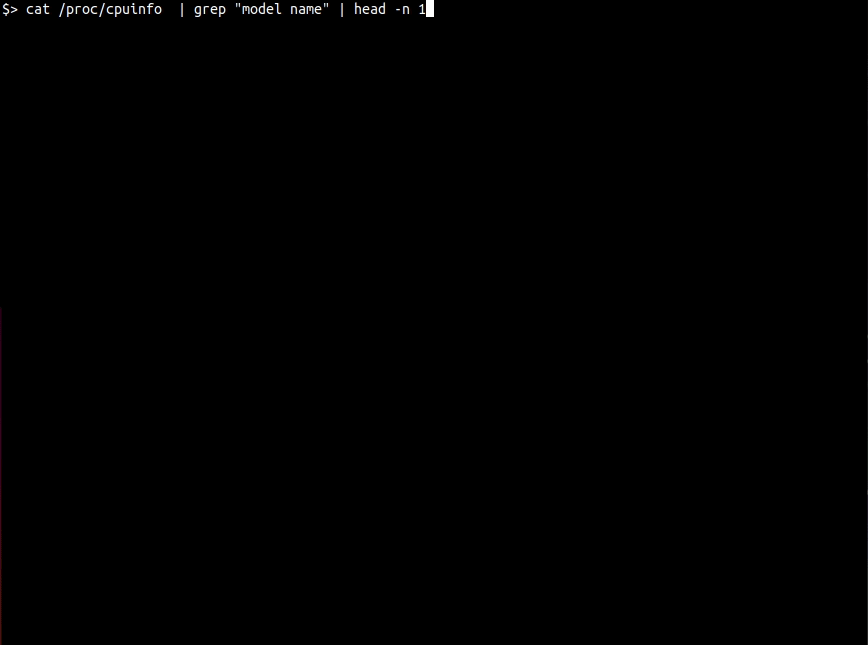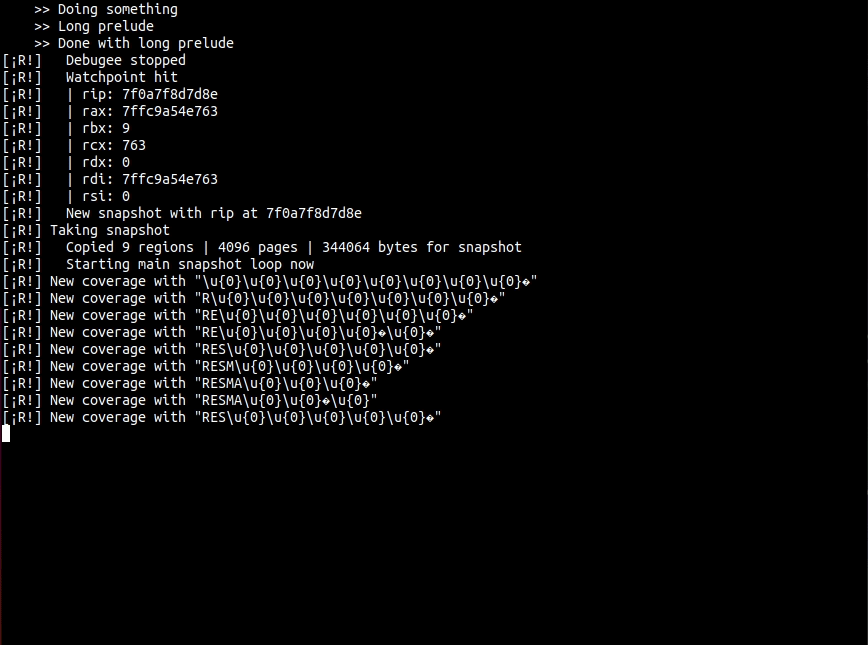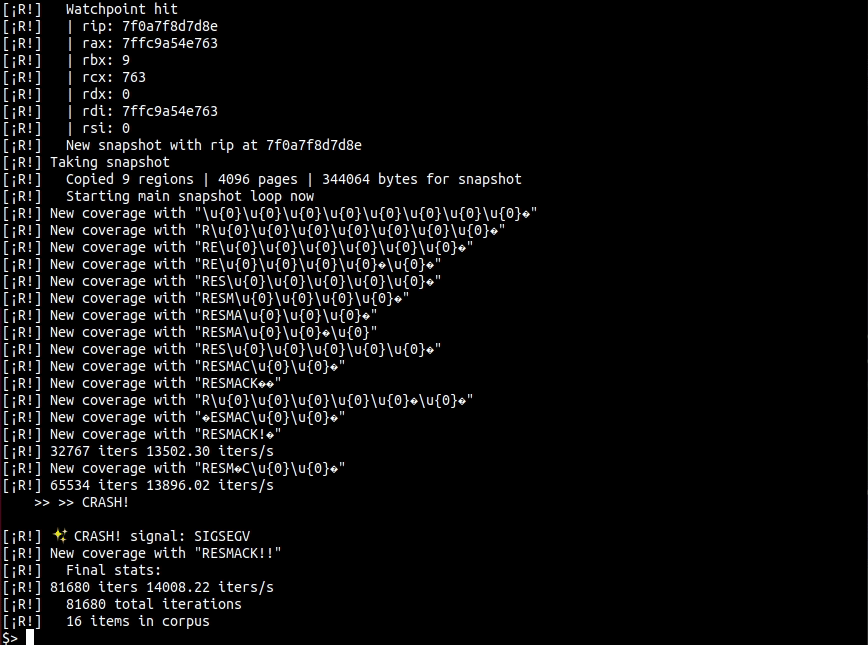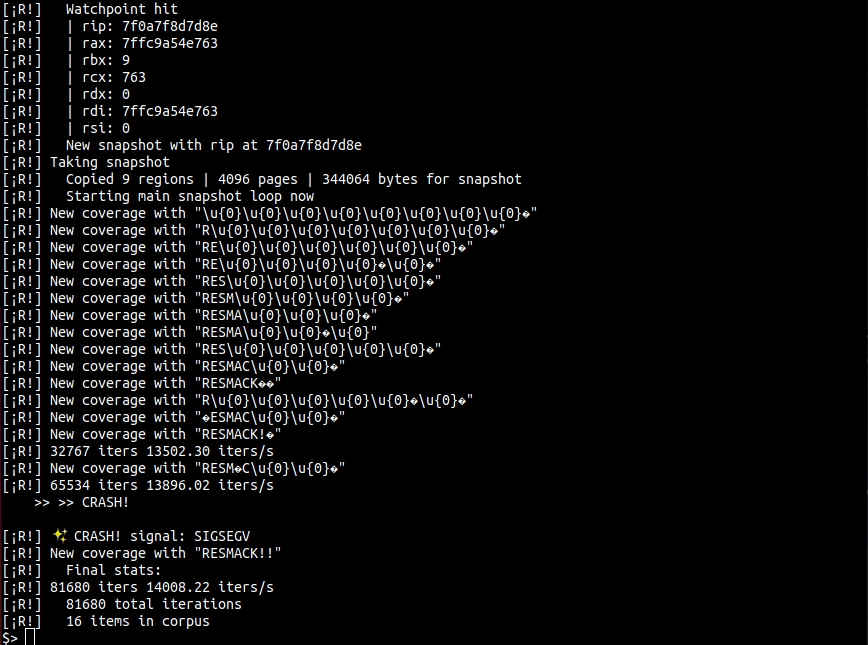
 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
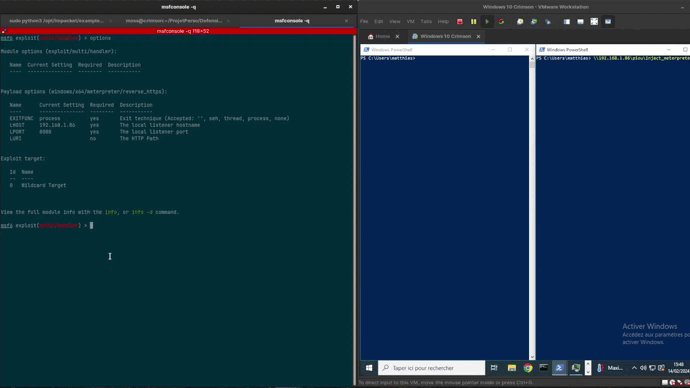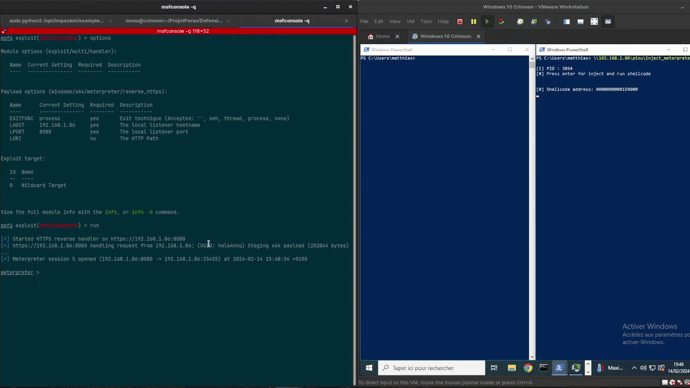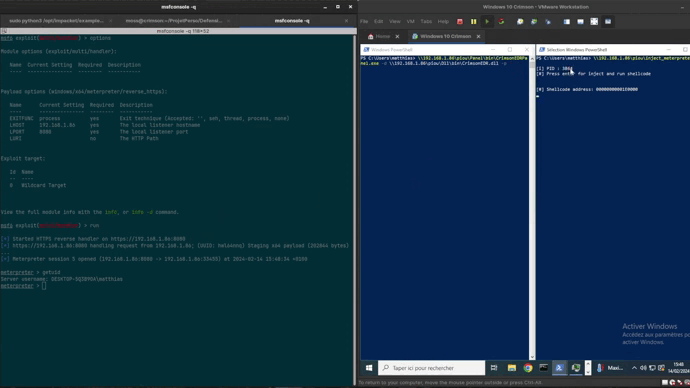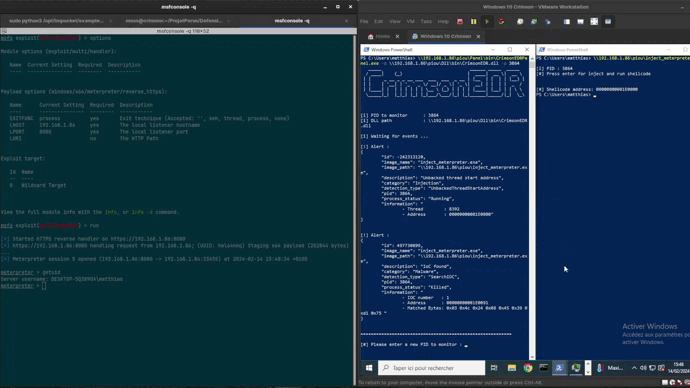 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 enessar/libpng_oss-fuzz
Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…