
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
152 results
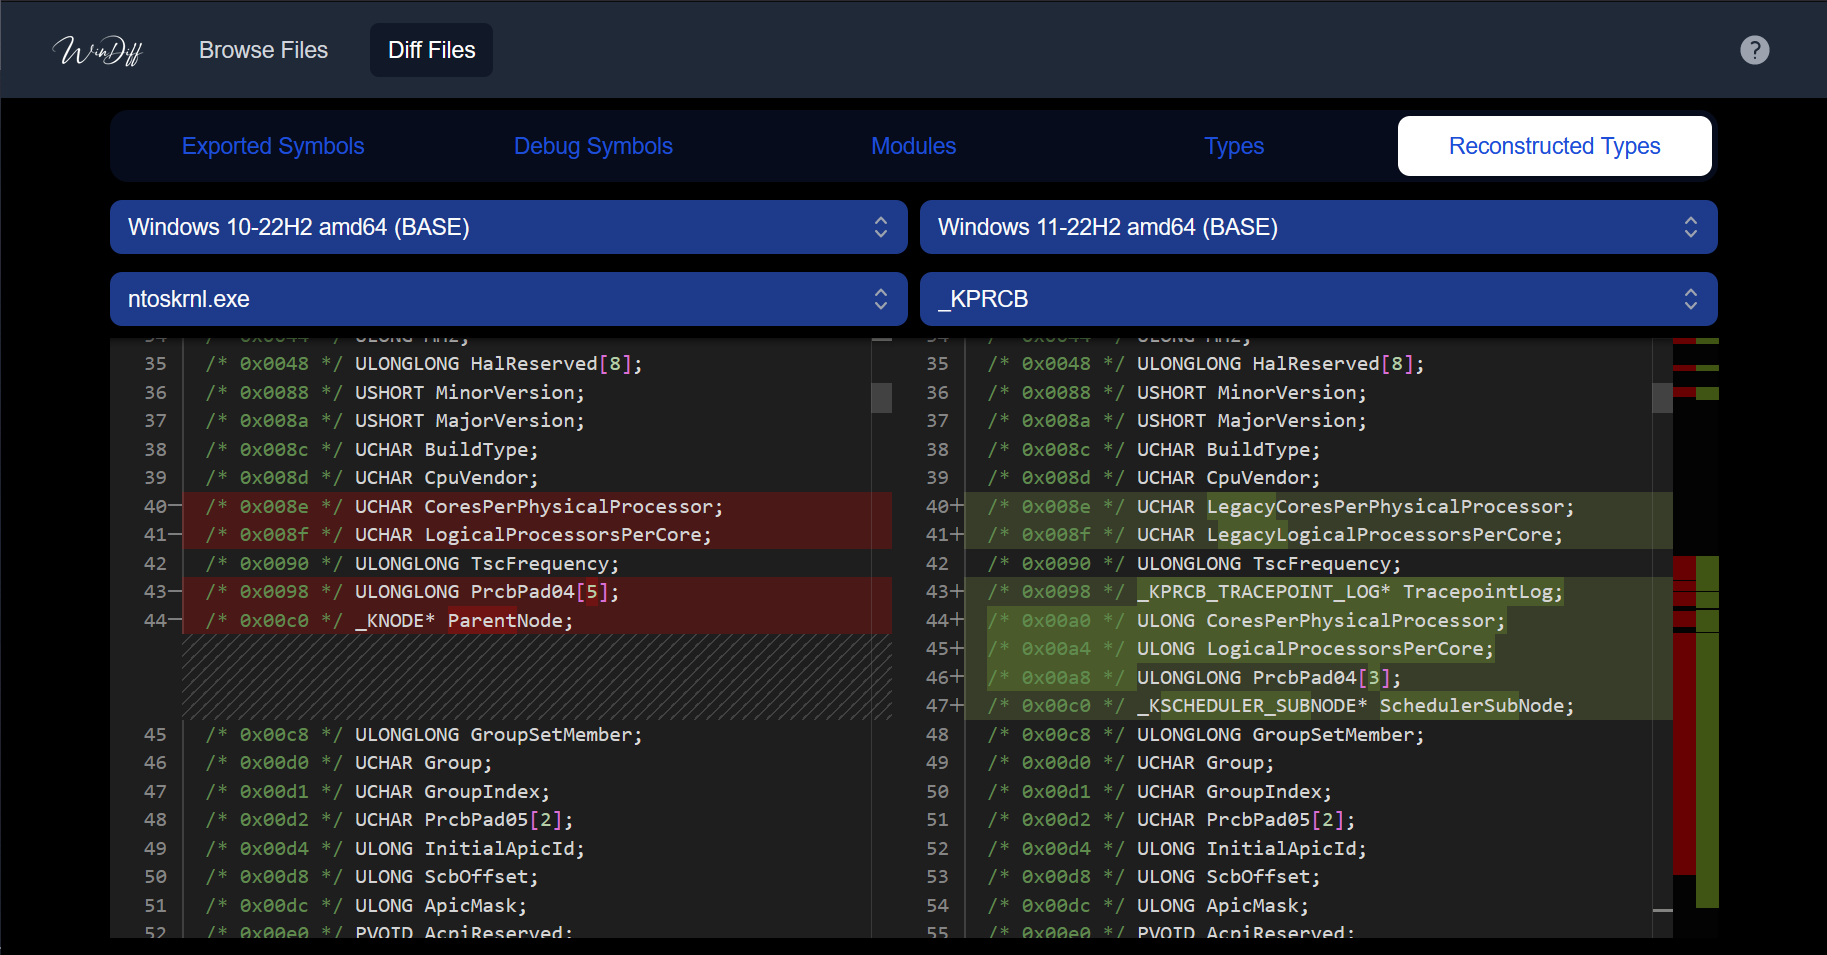
windiff preview

windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
392
11h 23m ago
XenoScan preview

XenoScan

GitHubnickcano/xenoscan

Open source memory scanner written in C++

binary-analysisdebuggersexploitation+2
3696 years ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.1k4 days ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
ollytlscatch preview

ollytlscatch

GitHubgmh5225/ollytlscatch

OllyDbg plugin that intercepts and dumps TLS/SSL plaintext traffic during debugging sessions, aiding reverse engineering and malware analysis of…
binary-analysisdebuggersdynamic-code-analysis+2
13 years ago
Analysis-for-stage1-shellcode-loader-from-hacking- preview

Analysis-for-stage1-shellcode-loader-from-hacking-

GitHubspiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-

Analysis for stage1 shellcode loader from hacking
binary-analysiseducationmalware-analysis+2
31 year ago
360WFP_Exploit preview

360WFP_Exploit

GitHubkyxiaxiang/360wfp_exploit

BYOVD: Use 360 ​​WFP driver to block EDR/XDR network connection.
binary-analysisexploitationids-ips-evasion+6
1298 months ago
CVE-2024-5633 preview

CVE-2024-5633

GitHubadikso/cve-2024-5633

PoC for CVE-2024-5633

binary-analysisembedded-systems-securityexploitation+3
12 years ago
hexvero preview

hexvero

GitHubmaximilianfeix/hexvero

Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
ai-securityandroid-securitybinary-analysis+9
91 day ago
OffensiveCSharp preview

OffensiveCSharp

GitHubmatterpreter/offensivecsharp

Collection of Offensive C# Tooling
binary-analysiscode-analysisexploitation+7
1.5k3 years ago
FreeRDP-Out-of-Bounds-Read-CVE-2024-32459- preview

FreeRDP-Out-of-Bounds-Read-CVE-2024-32459-

GitHubabsholi7ly/freerdp-out-of-bounds-read-cve-2024-32459-

The FreeRDP - Out-of-Bounds Read (CVE-2024-32459) vulnerability concerns FreeRDP, a free implementation of Remote Desktop Protocol. FreeRDP-based…
binary-analysisexploitationinformation-gathering+2
42 years ago
OmniSec-Hex preview

OmniSec-Hex

GitHubvighnesh91/omnisec-hex

Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
ai-securitybinary-analysisfuzzing+9
27 days ago
CVE-2026-20805-PoC preview

CVE-2026-20805-PoC

GitHubuzair-baig0900/cve-2026-20805-poc

The PoC of information disclosure in Microsoft Desktop Windows Management.
binary-analysisexploitationinformation-gathering+2
29 months ago
cve-2018-15968 preview

cve-2018-15968

GitHubsandi-go/cve-2018-15968

Technical disclosure of CVE-2018-15968: an out-of-bounds read vulnerability in Adobe Reader's PDF parsing, enabling information disclosure and…
binary-analysisexploitationinformation-gathering+2
7 years ago
CVE-2023-23583-Reptar- preview

CVE-2023-23583-Reptar-

GitHubmav3r1ck0x1/cve-2023-23583-reptar-

This script can help determine the CPU ID for the processor of your system, please note that I have not added every CPU ID to this script, edit as…
binary-analysisexploitationhardware-security+2
2 years ago
lifer preview

lifer

GitHubpaul-tew/lifer

Windows link file (shortcuts) examiner

binary-analysisdigital-forensicsforensics+1
682 years ago
CVE-2019-8540 preview

CVE-2019-8540

GitHubmaldiohead/cve-2019-8540

Kernel Stack info leak at exportObjectToClient function
binary-analysisexploitationinformation-gathering+2
407 years ago
CVE-2019-19012 preview

CVE-2019-19012

GitHubmanhndd/cve-2019-19012

Integer overflow in Oniguruma

binary-analysisexploitationfuzzing+3
46 years ago
Previous12…9Next