
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
66 results
pythia preview

pythia

GitHubnccgroup/pythia

A tool to extract RTTI information from Delphi executables, written in pure Python
binary-analysismalware-analysisreverse-engineering
247 years ago
hexcymatix preview

hexcymatix

GitHubxoreaxeaxeax/hexcymatix

Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
binary-analysisreverse-engineeringstatic-analysis
262 months ago
DIRT preview

DIRT

GitHubjthuraisamy/dirt

Driver Initial Reconnaissance Tool
binary-analysisreconnaissancevulnerability-analysis
1276 years ago
drltrace preview

drltrace

GitHubmxmssh/drltrace

Drltrace is a library calls tracer for Windows and Linux applications.
binary-analysisdebuggersdynamic-analysis-sandboxing+2
4196 years ago
PS-2017-13---CVE-2018-9950 preview

PS-2017-13---CVE-2018-9950

GitHubsandi-go/ps-2017-13---cve-2018-9950

Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…
binary-analysisexploitationinformation-gathering+2
7 years ago
dwarf2json preview

dwarf2json

GitHubvolatilityfoundation/dwarf2json

convert ELF/DWARF symbol and type information into vol3's intermediate JSON

binary-analysisdigital-forensicsmemory-forensics+2
1602 years ago
Ropper preview

Ropper

GitHubsashs/ropper

Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
binary-analysisbinary-exploitationctf+3
2.1k2 months ago
Mastik preview

Mastik

GitHub0xade1a1de/mastik

C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
binary-analysiscryptographyeducation+3
1243 years ago
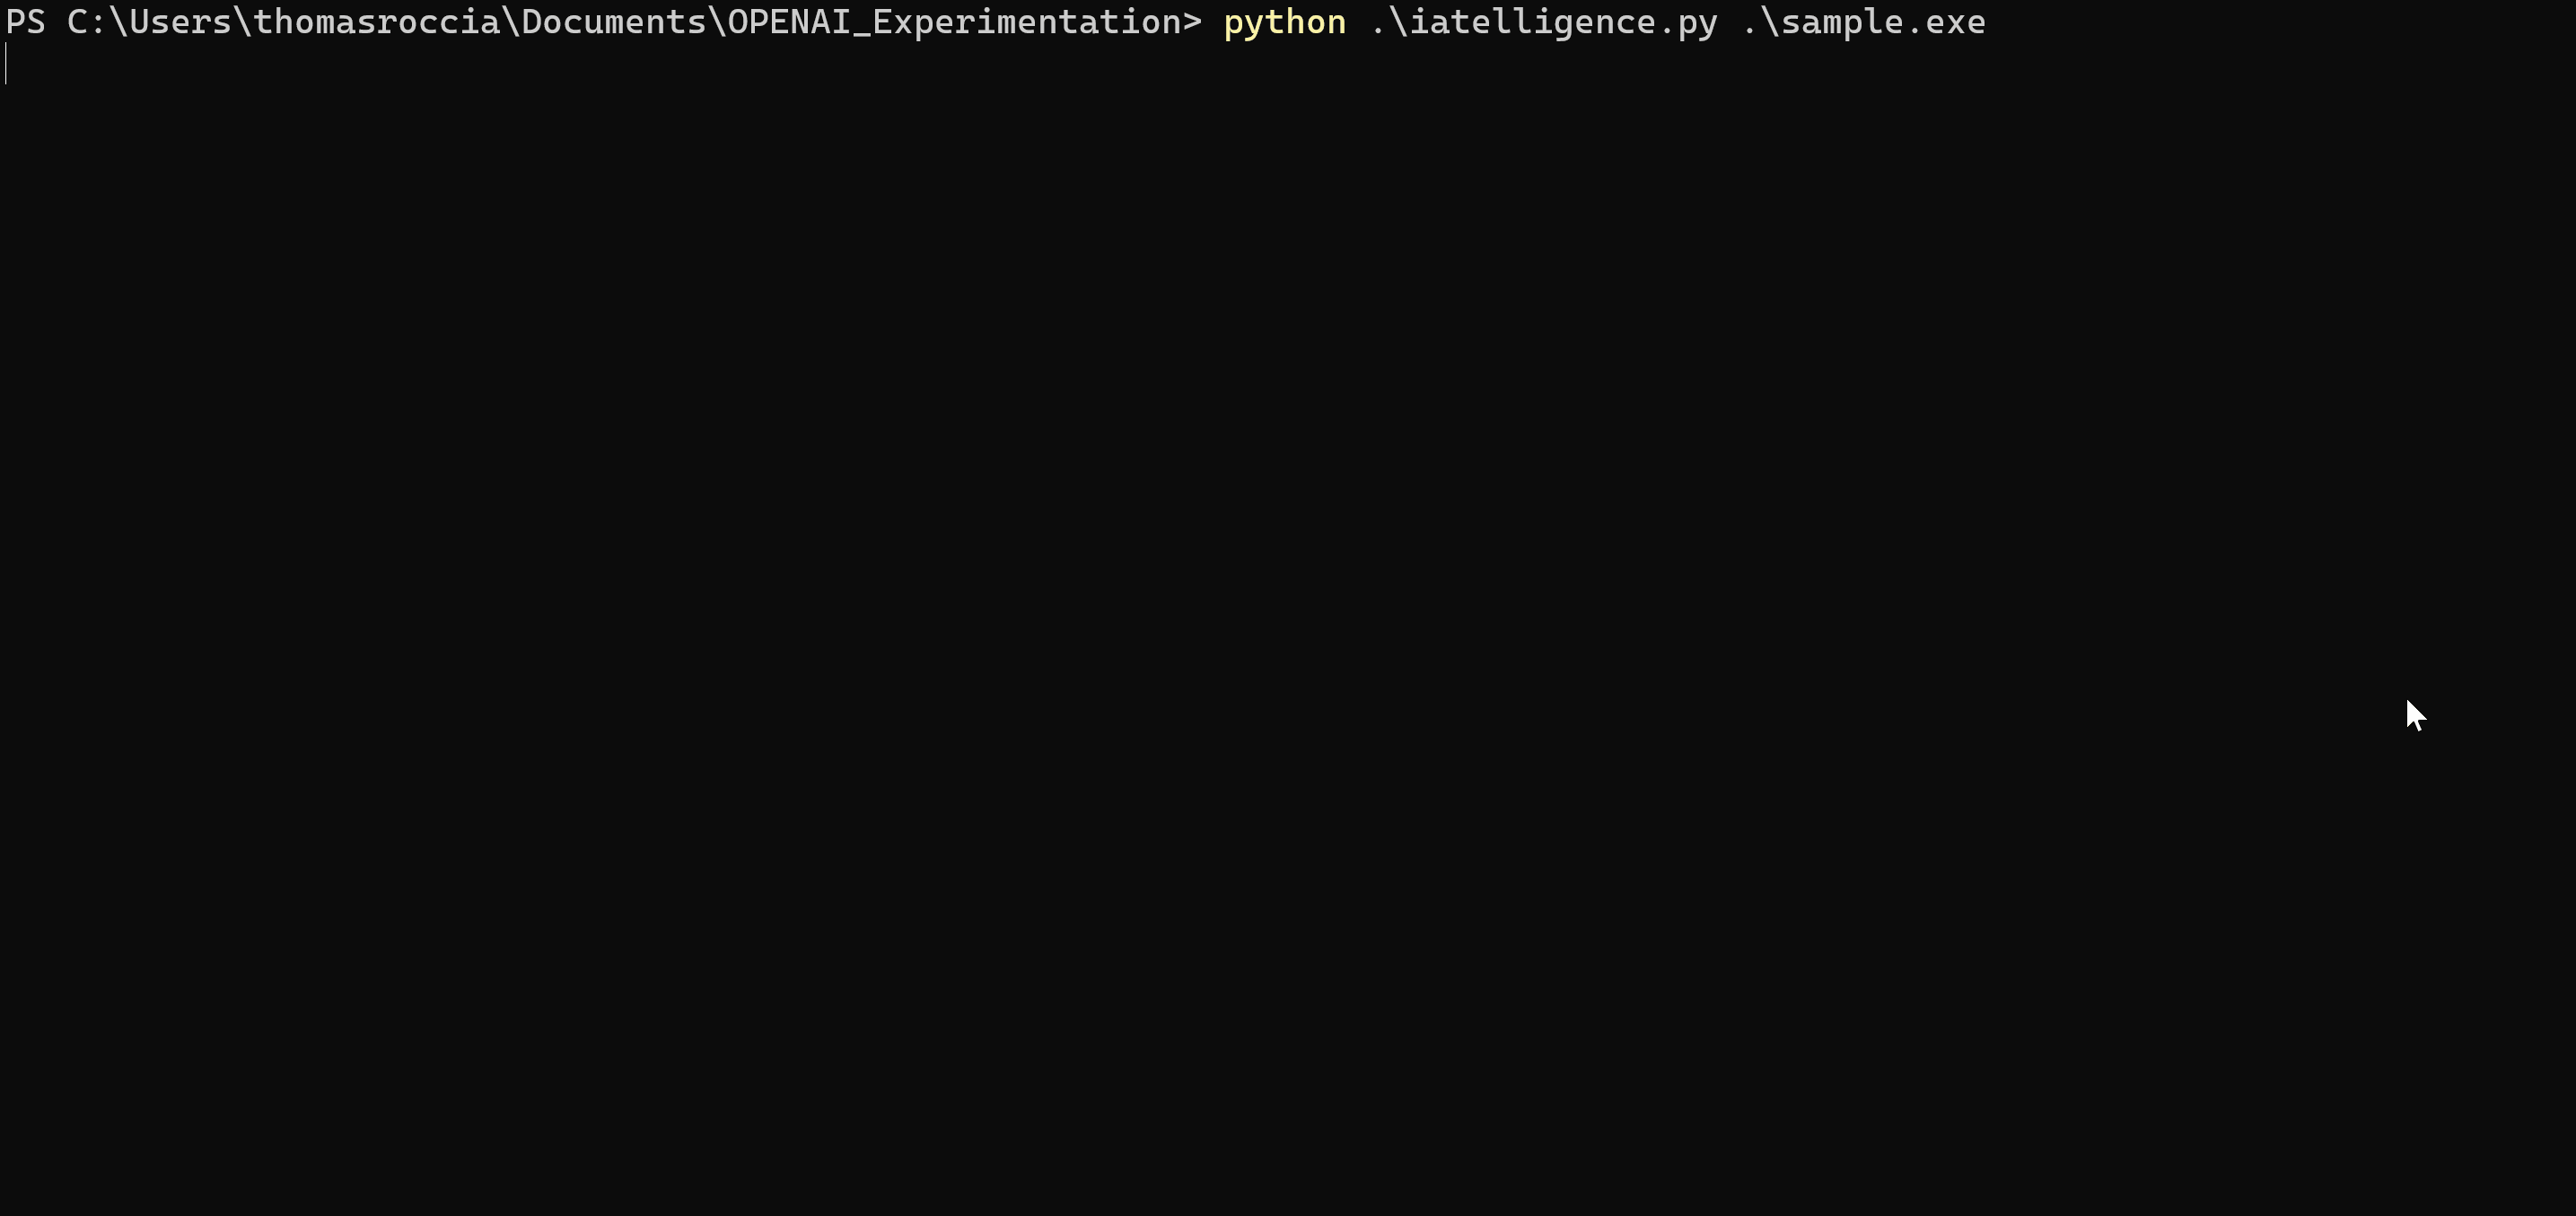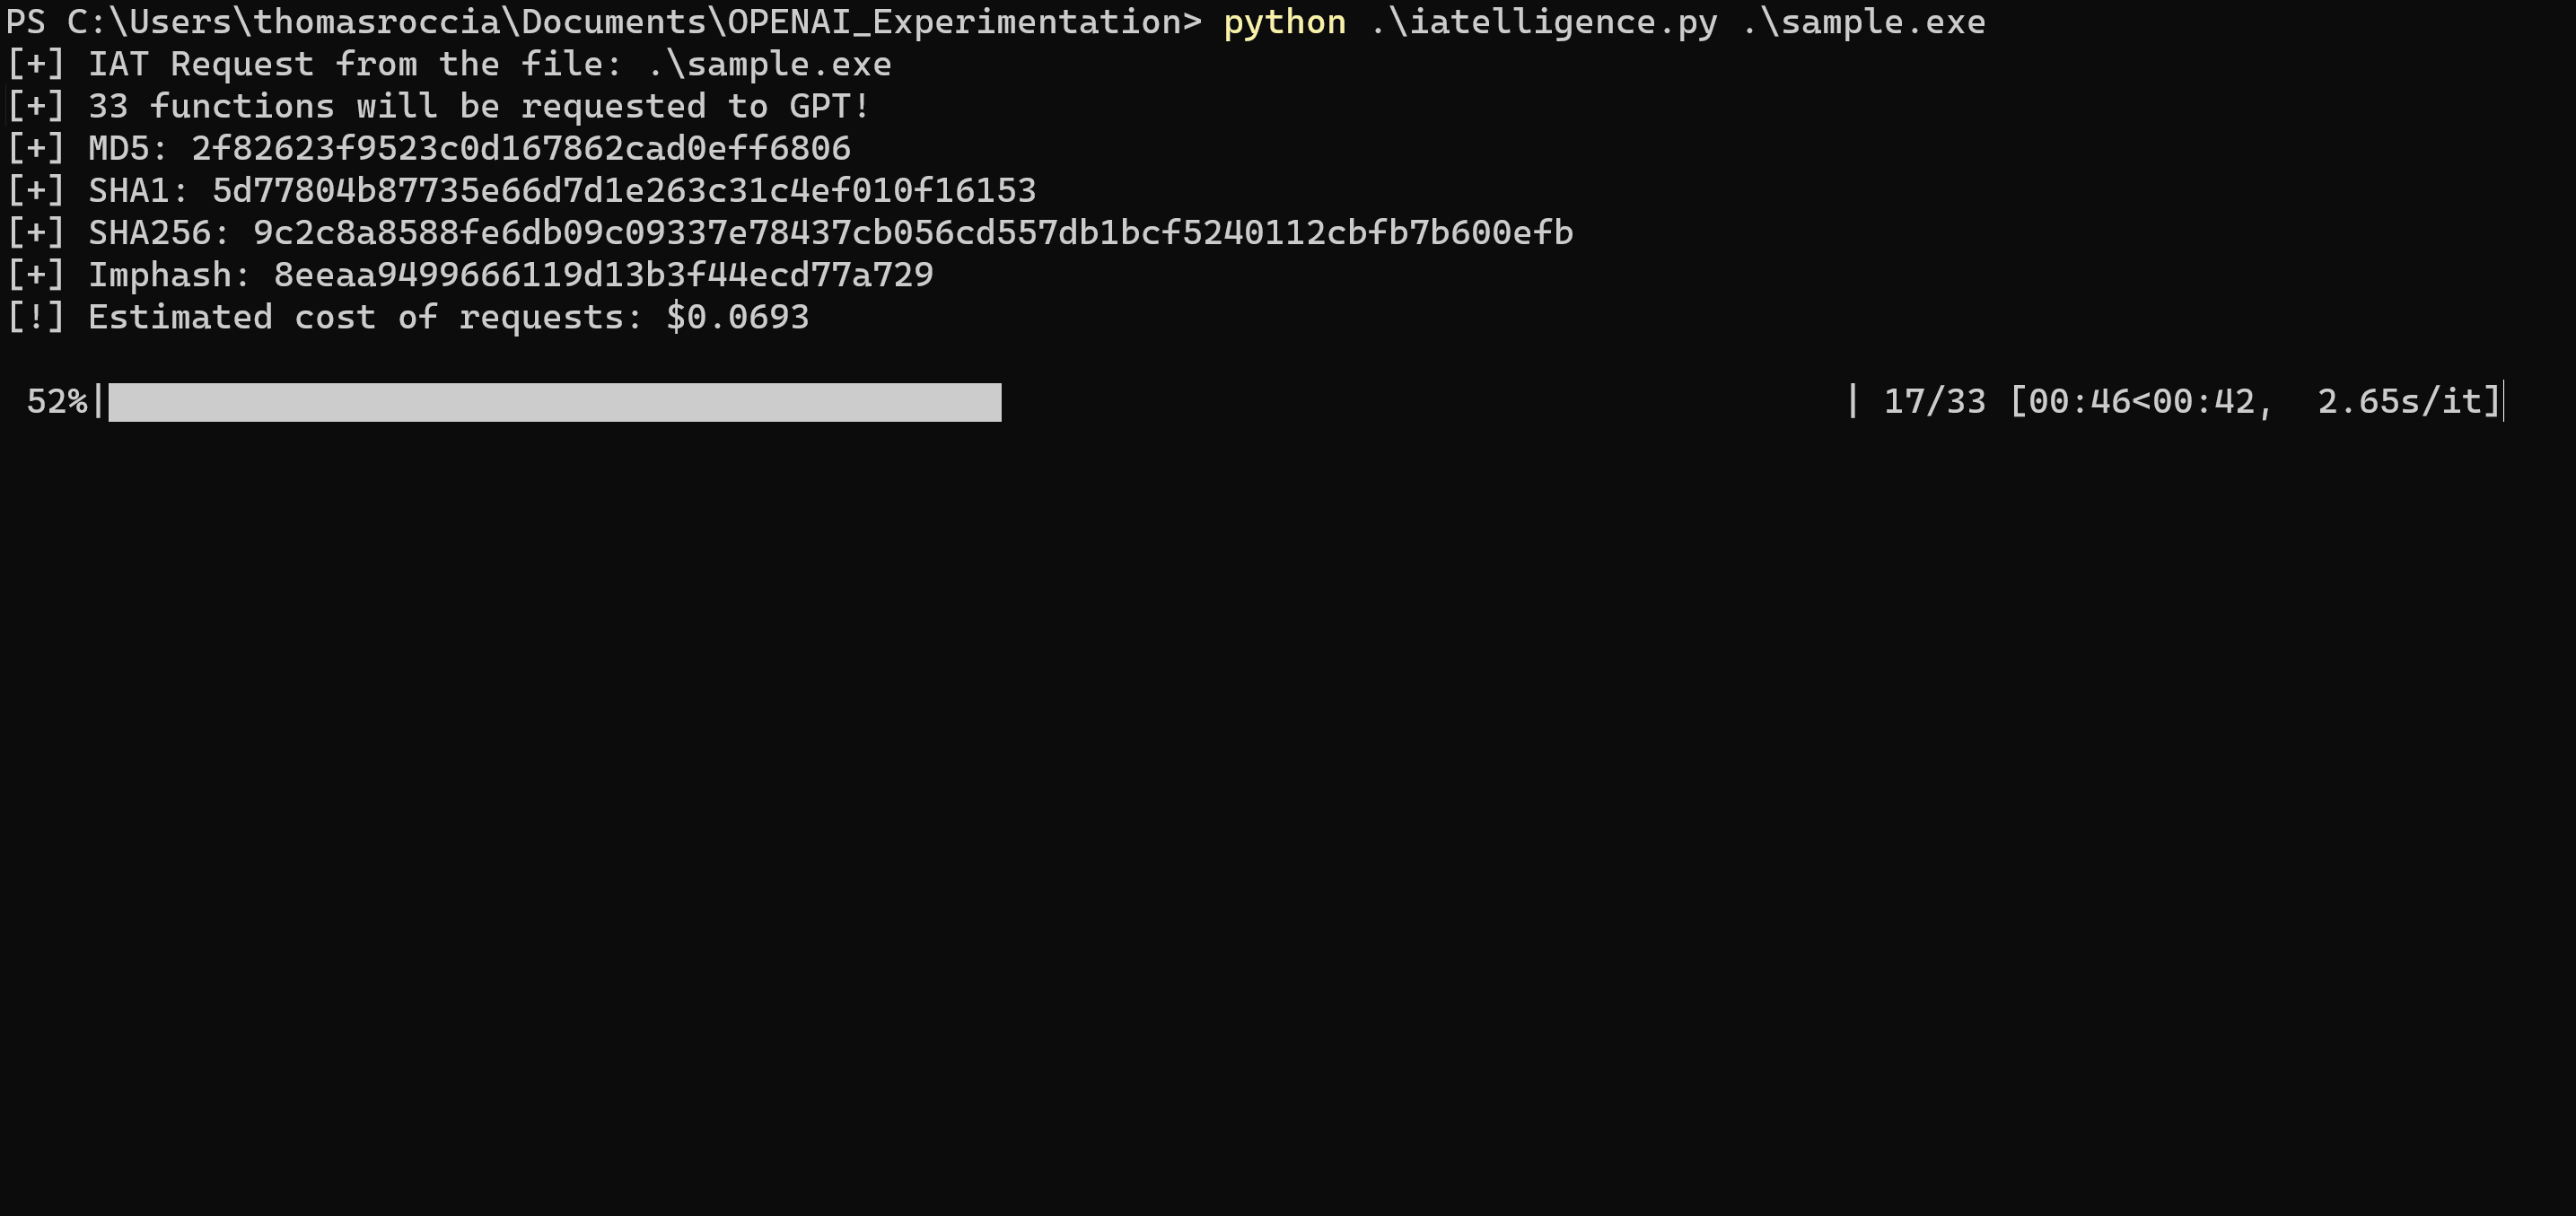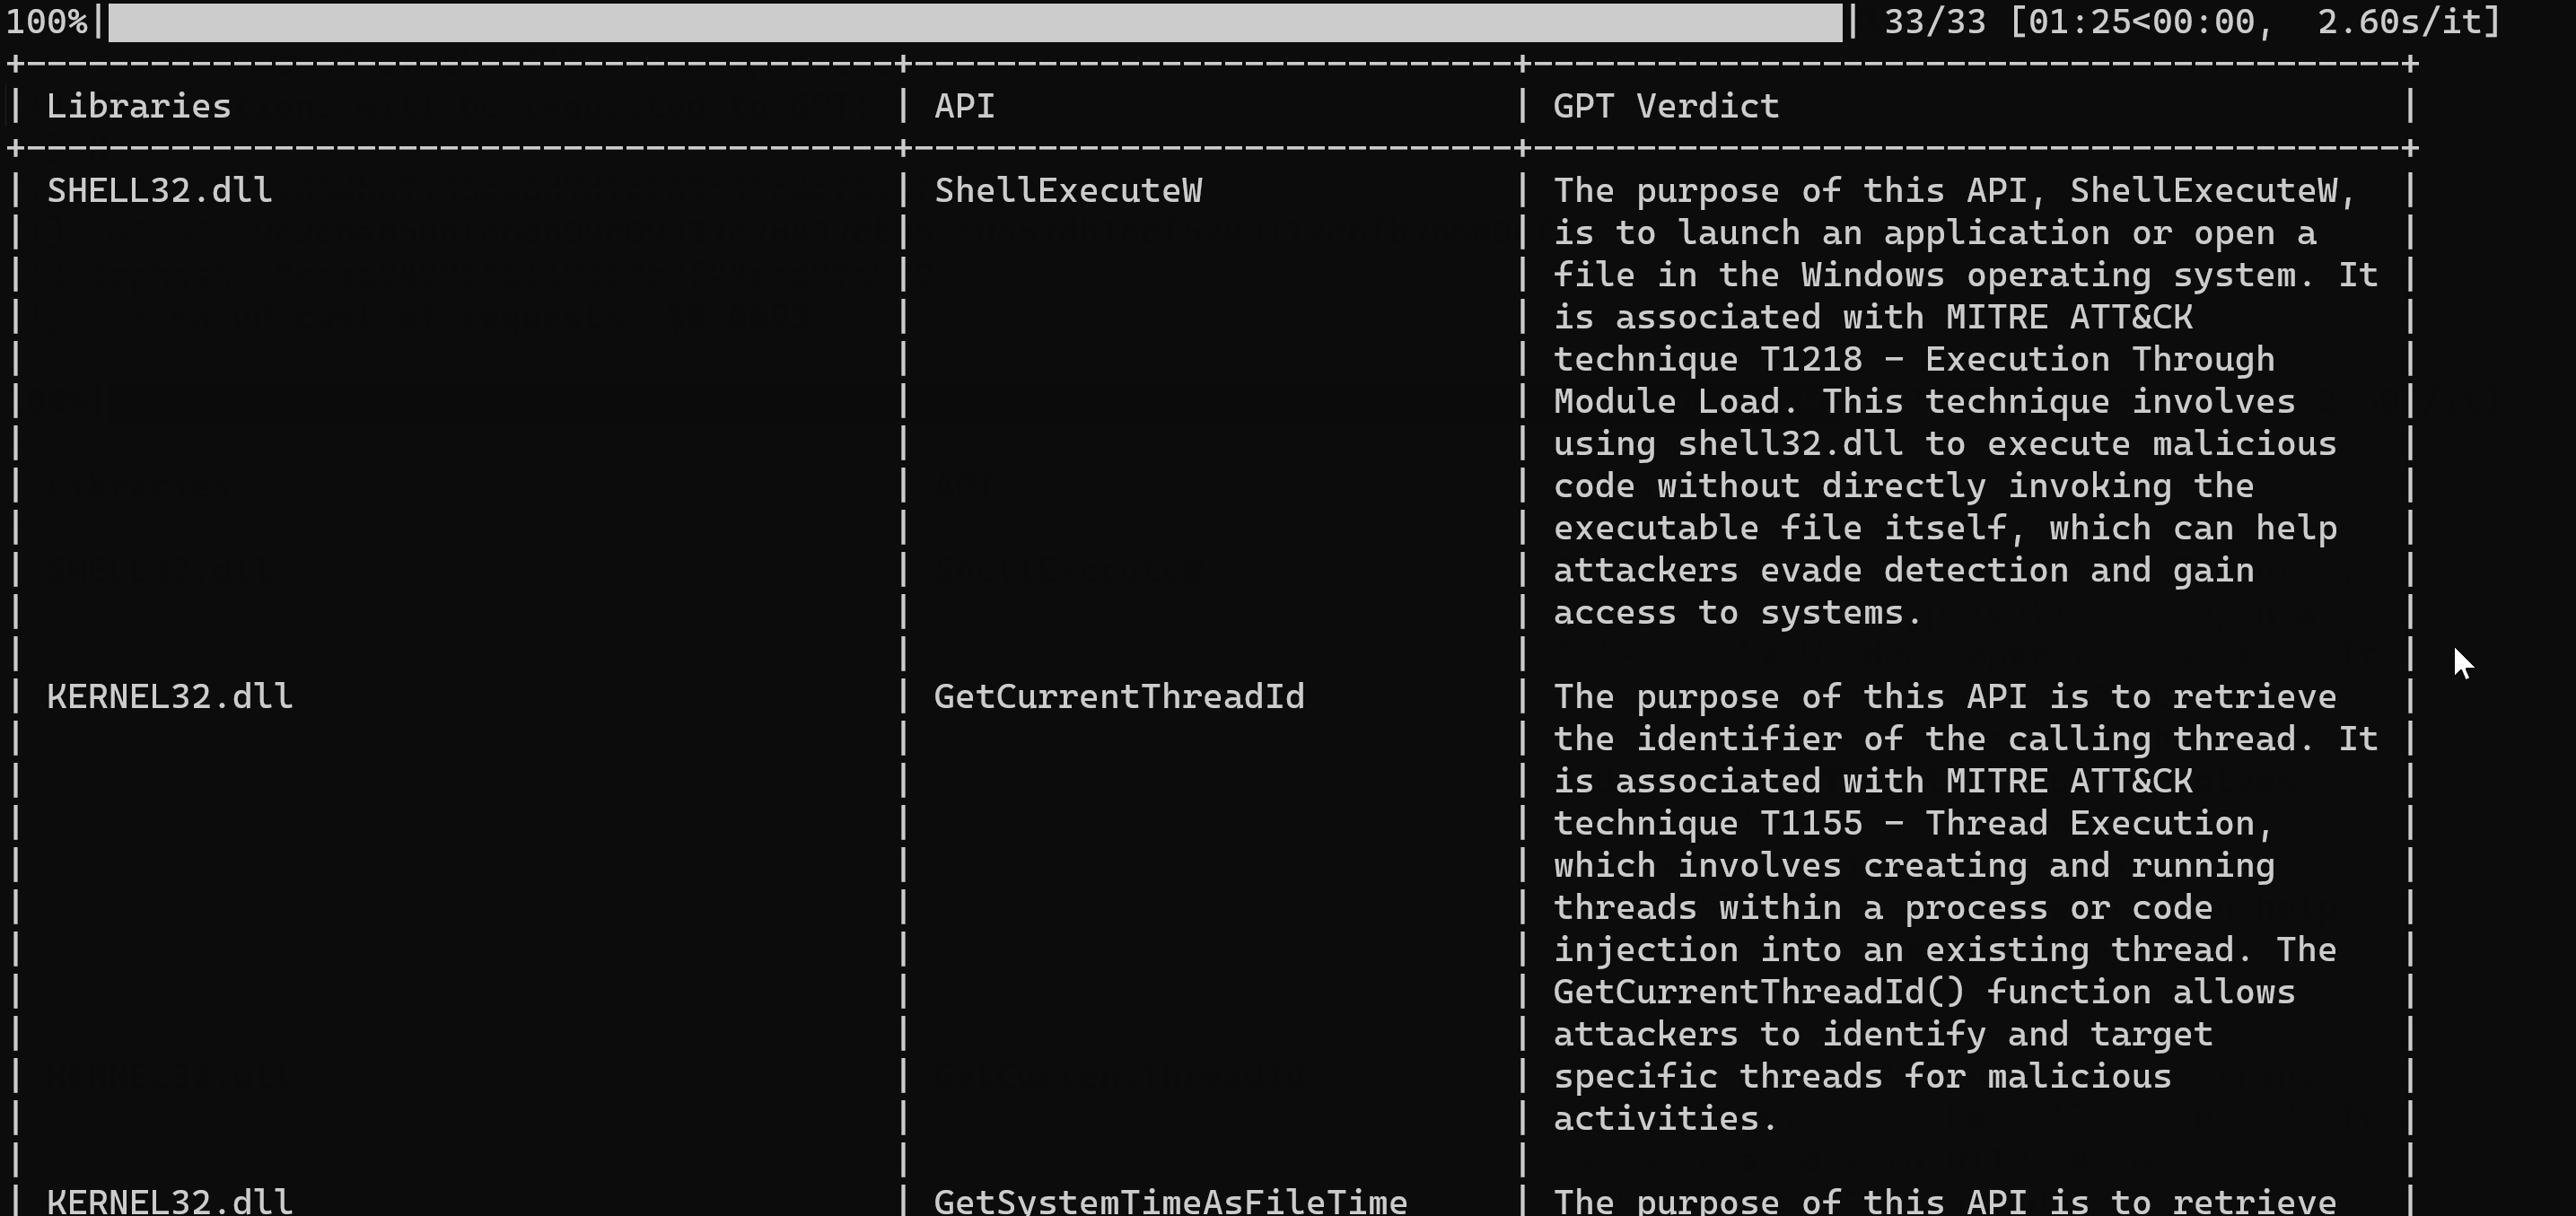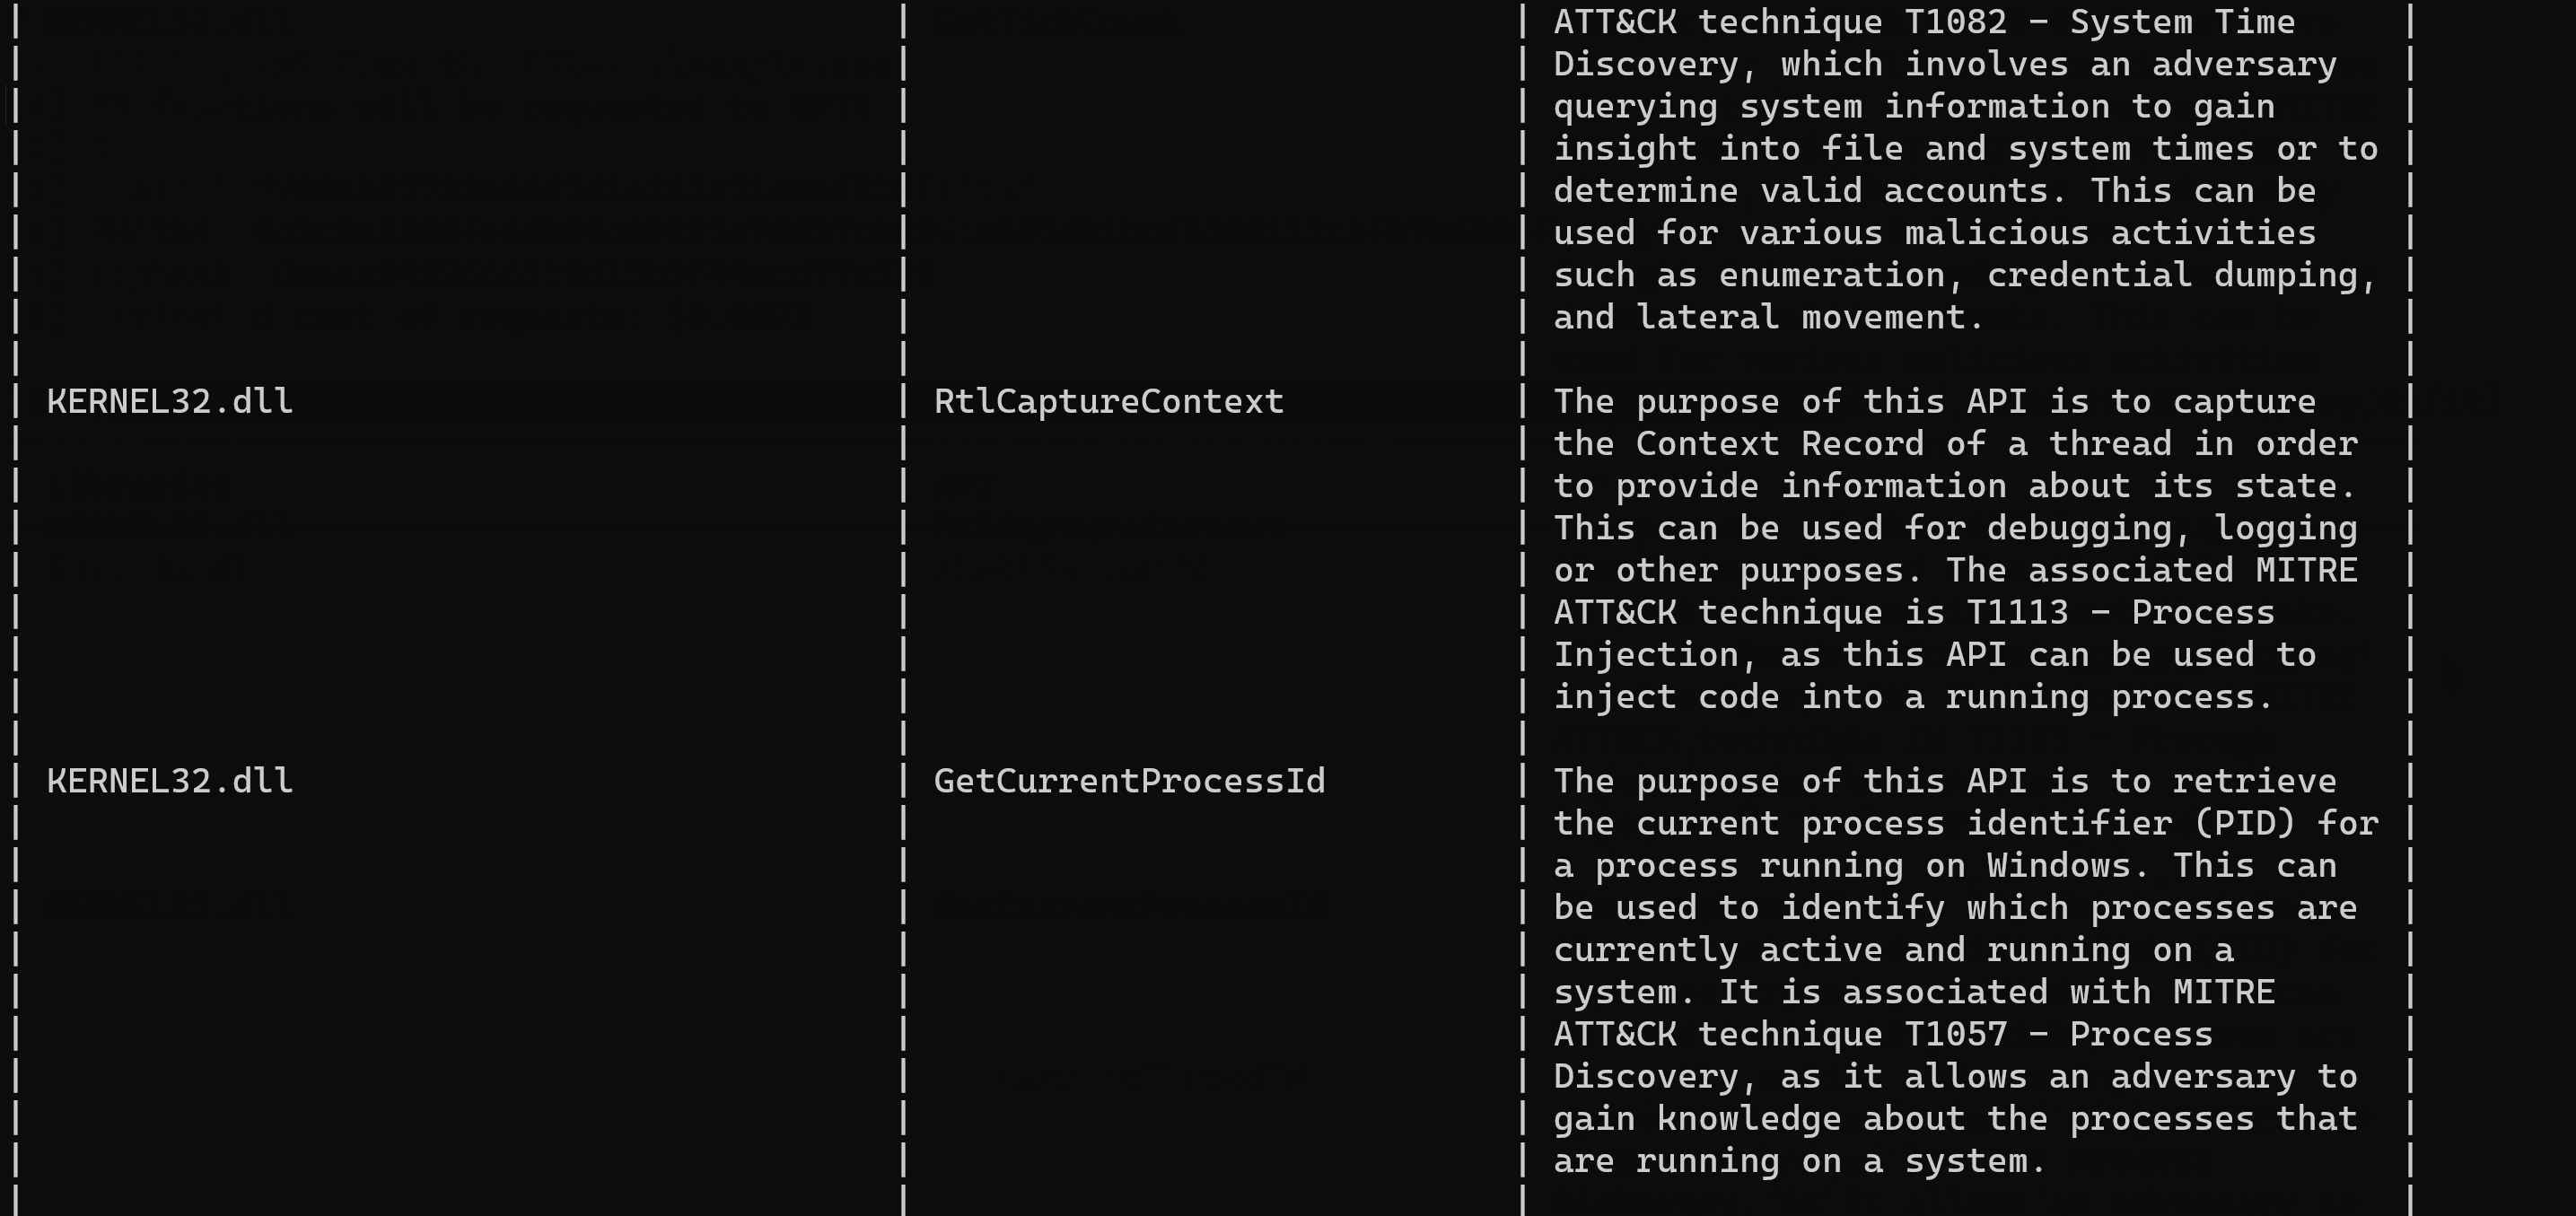
IATelligence preview

IATelligence

GitHubfr0gger/iatelligence

IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
ai-assisted-reversingbinary-analysismalware-analysis+3
3843 years ago
binprotect preview

binprotect

GitHubnoahware/binprotect

x64 PE bin2bin obfuscator which doesn't add a section to the binary

binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
3042 months ago
binwally preview

binwally

GitHubbmaia/binwally

Binary and Directory tree comparison tool using Fuzzy Hashing
binary-analysisdata-recoverydigital-forensics+3
8411 years ago
DiaSymbolView preview

DiaSymbolView

GitHubdiversenok/diasymbolview

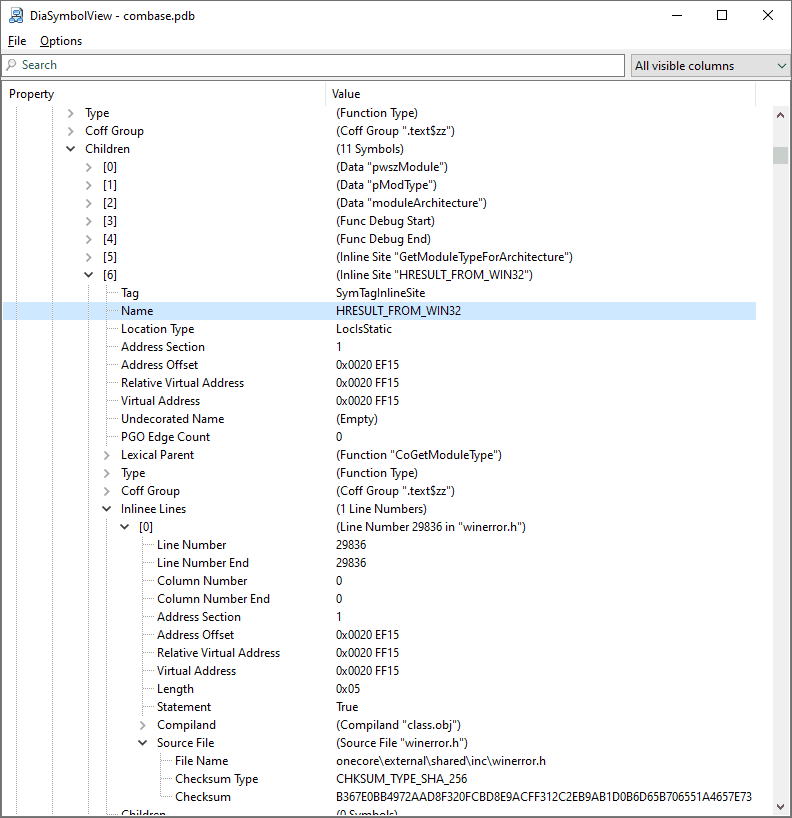
PDB file inspection tool
binary-analysisdebuggersreverse-engineering+1
13811 months ago
binja_arch_ref preview

binja_arch_ref

GitHubnccgroup/binja_arch_ref

A simple Binary Ninja plugin to display a cheat sheet with information about the current architecture
binary-analysisembedded-systems-securityreverse-engineering
79 years ago
CVE-2026-20805-PoC preview

CVE-2026-20805-PoC

GitHubuzair-baig0900/cve-2026-20805-poc

The PoC of information disclosure in Microsoft Desktop Windows Management.
binary-analysisexploitationinformation-gathering+2
29 months ago
windiff preview

windiff

GitHubergrelet/windiff

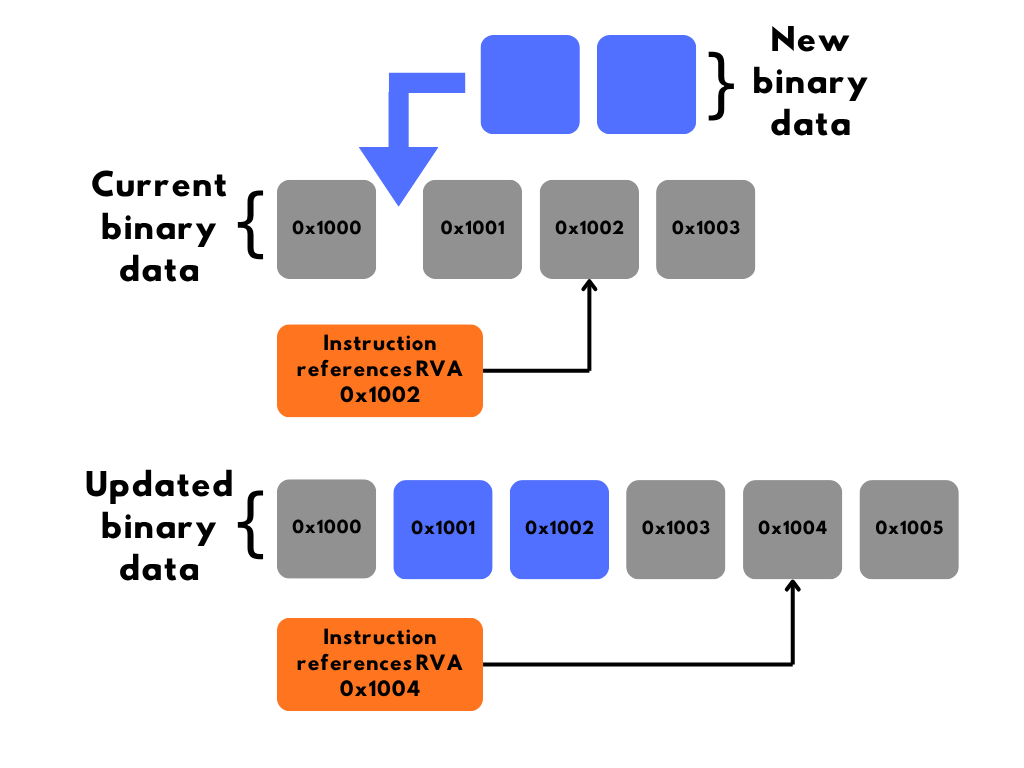
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

binary-analysisinformation-gatheringreverse-engineering+1
39221h 36m ago
EDRs preview

EDRs

GitHubmr-un1k0d3r/edrs

Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
binary-analysiscurated-resourcesids-ips-evasion+3
2.2k7 months ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
binary-analysisdefensive-toolsdigital-forensics+6
8842 years ago
PSI_BOF preview

PSI_BOF

GitHubwhokilleddb/psi_bof

A BOF designed to inspect processes memory and addresses

binary-analysisdebuggersmemory-forensics+4
406 months ago
Previous1234Next