

B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
551
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 m4b/goblin
An impish, cross-platform binary parsing crate, written in Rust
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 openrce/paimei
A reverse engineering framework written in Python.
 nickcano/xenoscan
Open source memory scanner written in C++
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
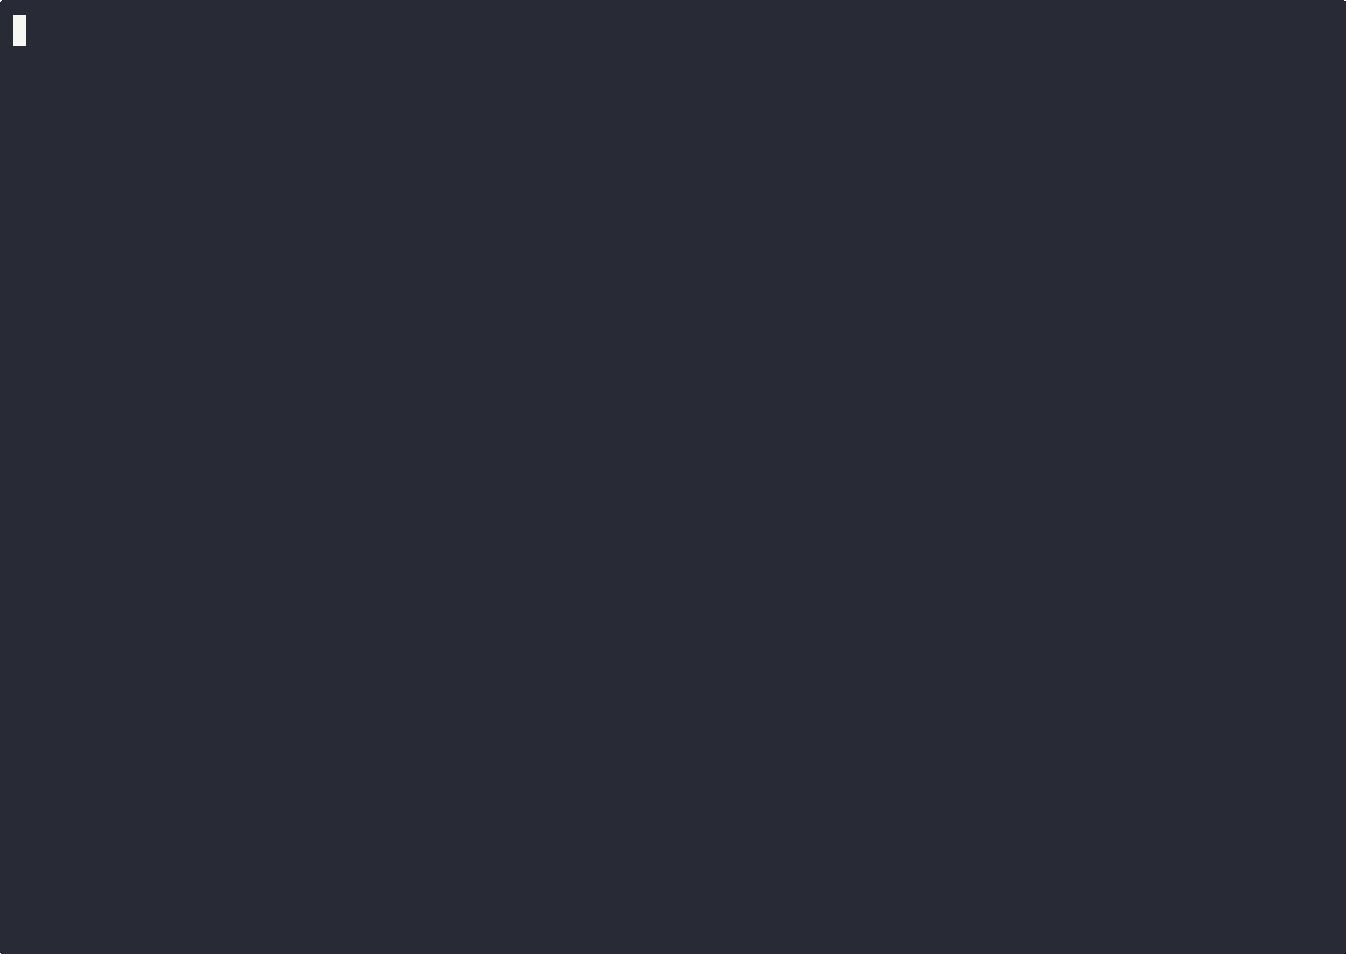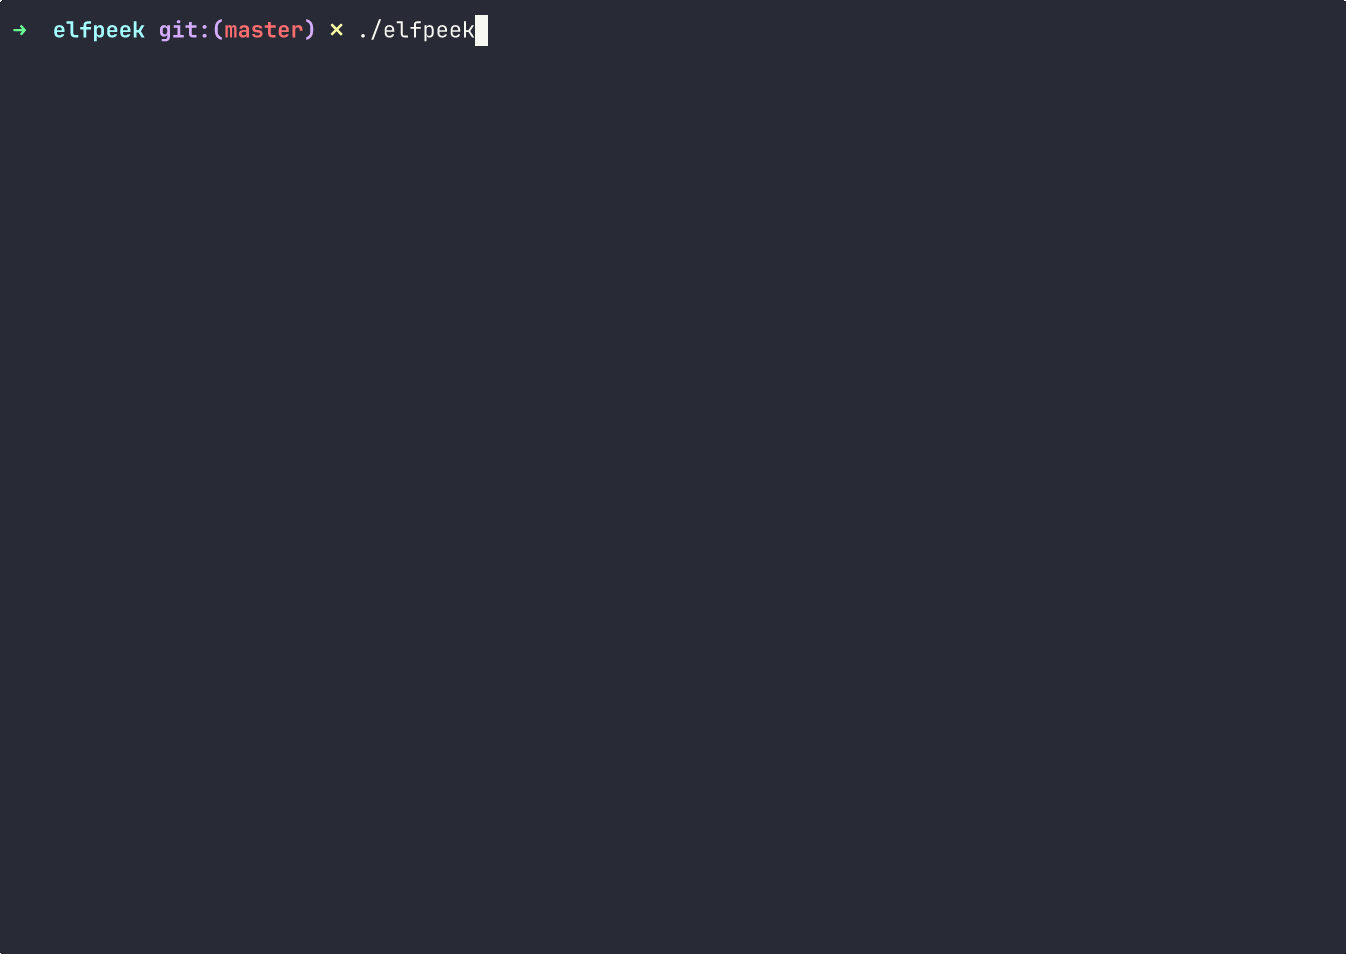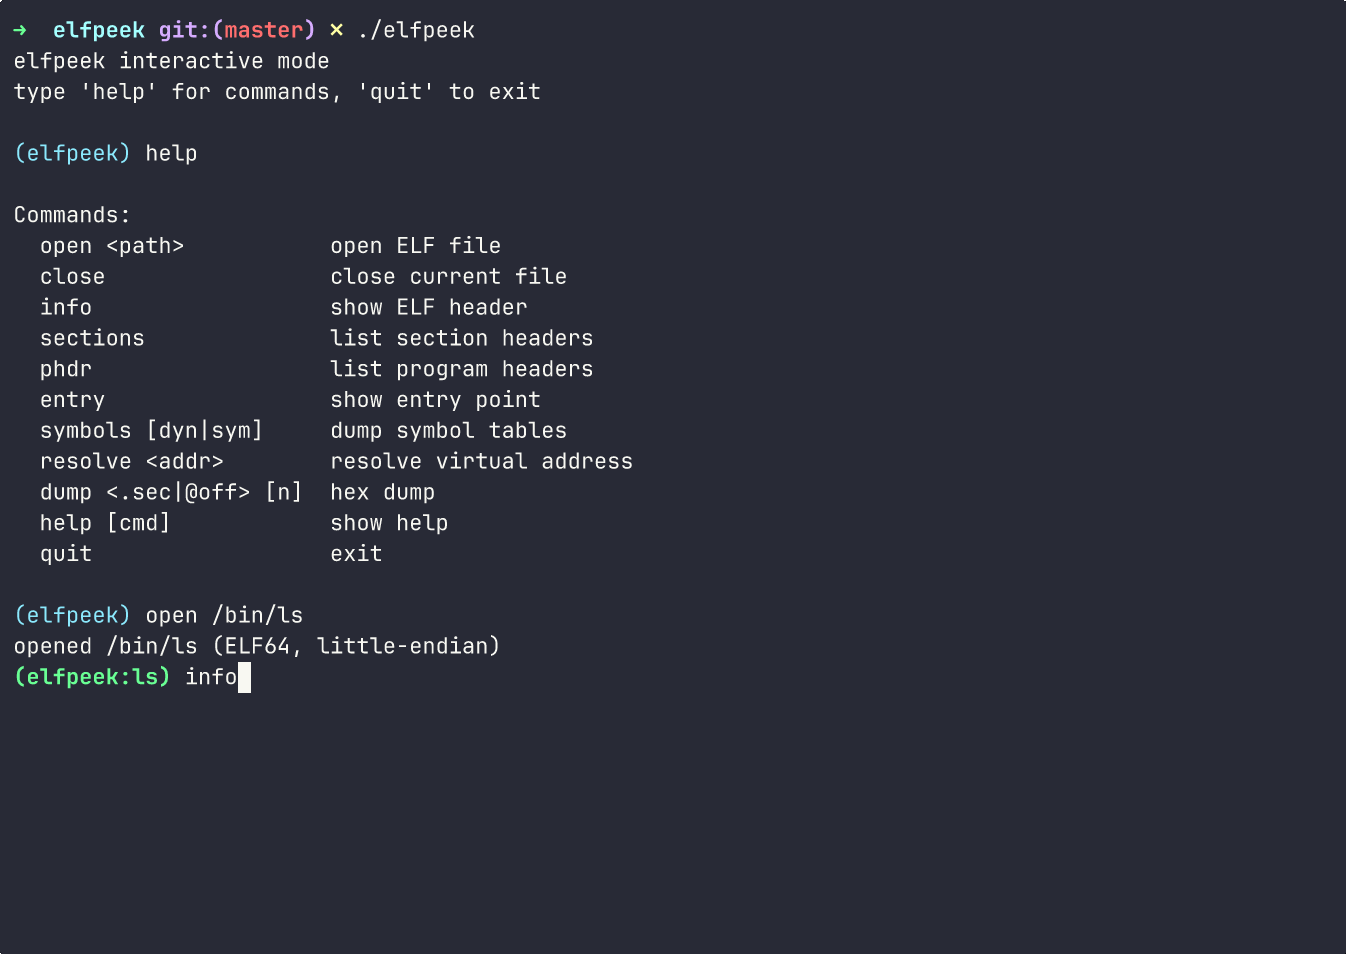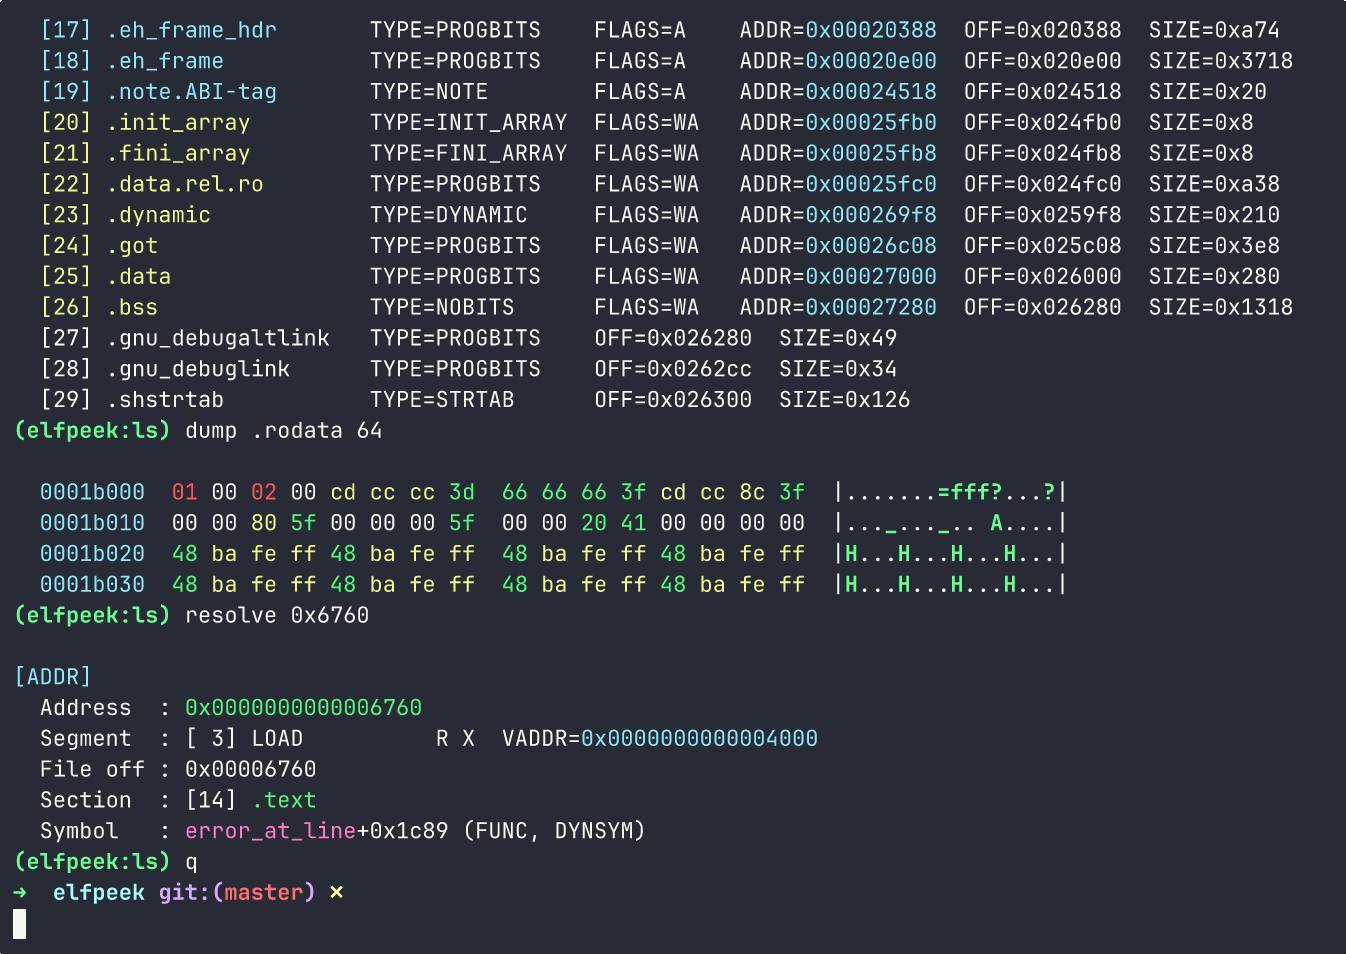 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…

 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…