
Archived
pe_tree
 blackberry/pe_tree
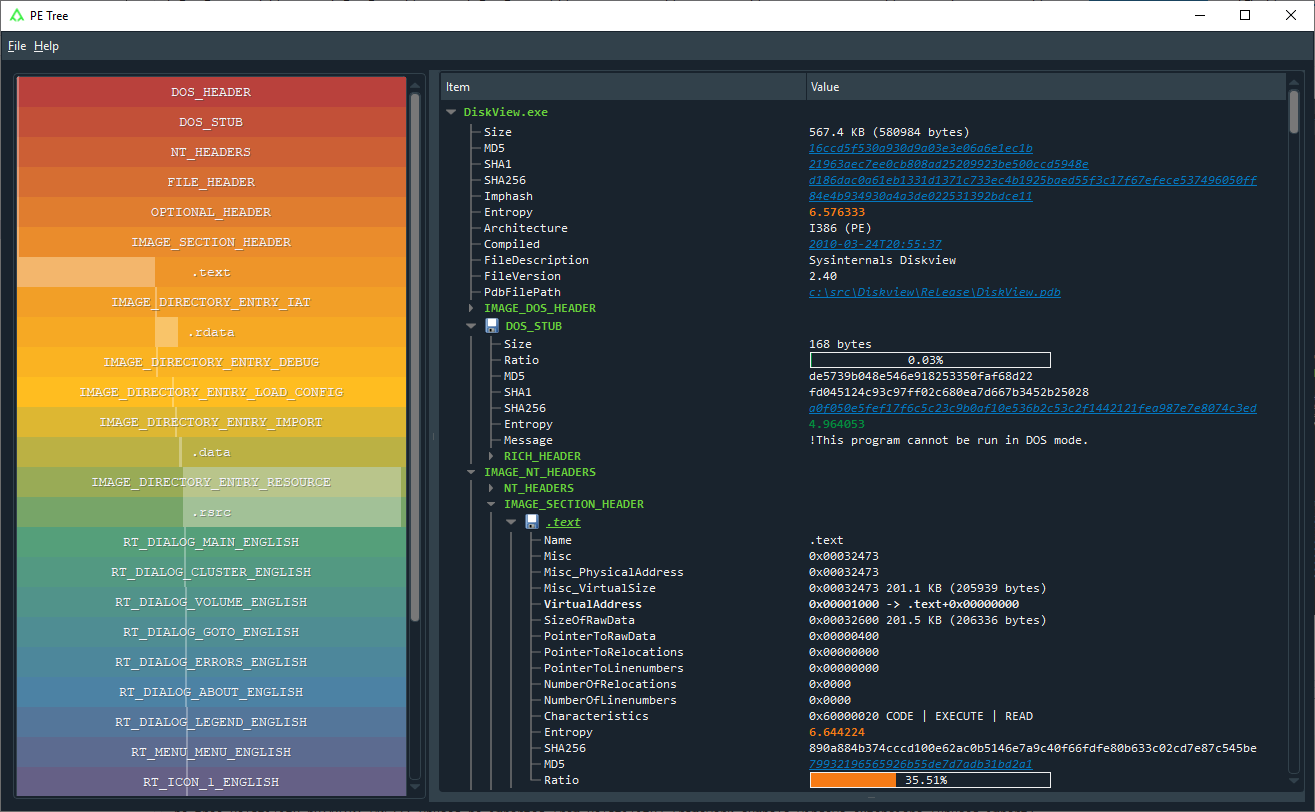
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…