
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
24 results
windiff preview

windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
390
10h 36m ago
CVE-2026-20805-PoC preview

CVE-2026-20805-PoC

GitHubuzair-baig0900/cve-2026-20805-poc

The PoC of information disclosure in Microsoft Desktop Windows Management.
binary-analysisexploitationinformation-gathering+2
28 months ago
CVE-2021-24086 preview
Archived

CVE-2021-24086

GitHub0vercl0k/cve-2021-24086

Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
binary-analysisexploitationfuzzing+2
2365 years ago
RedTeamCCode preview

RedTeamCCode

GitHubmr-un1k0d3r/redteamccode

Red Team C code repo
binary-analysisdefensive-toolsmalware-analysis+1
5731 year ago
Vidar-Stealer-Reverse-Engineering preview

Vidar-Stealer-Reverse-Engineering

GitHubkaandemir993/vidar-stealer-reverse-engineering

"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
binary-analysiseducationforensics+7
32 months ago
DLLHSC preview

DLLHSC

GitHubctxis/dllhsc

Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
binary-analysisexploitationpayload-development+1
1586 years ago
dns_client_fuzzing preview

dns_client_fuzzing

GitHubpersonnumber3377/dns_client_fuzzing

Fuzzing the Microsoft Windows DNS client library. Inspired by CVE-2026-41096.
binary-analysisdns-analysisexploitation+2
3 months ago
CVE-2025-62821 preview

CVE-2025-62821

GitHubhyunjungg/cve-2025-62821

Microsoft HEIF Extension (msheif_store.dll) OOB-read
binary-analysisexploitationfuzzing+3
1 year ago
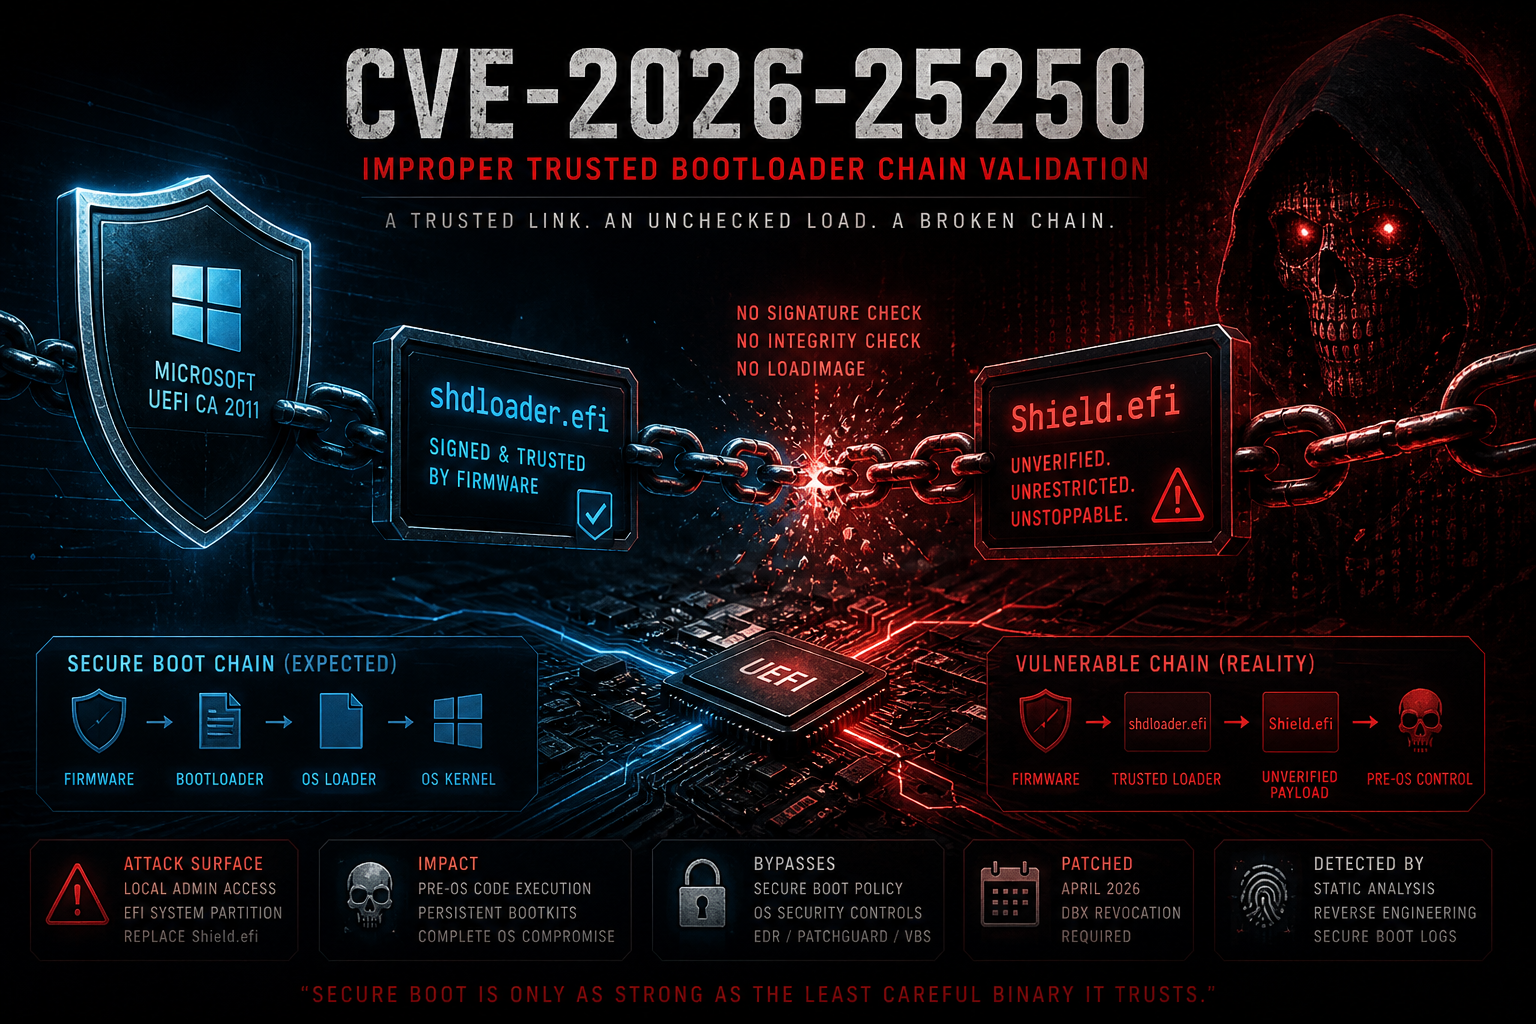
CVE-2026-25250 preview

CVE-2026-25250

GitHubthemalwareguardian/cve-2026-25250

Analysis and exploit for CVE-2026-25250, a Secure Boot bypass in Horizon DataSys Reboot Restore where shdloader.efi loads Shield.efi without…
binary-analysiseducationexploitation+3
11 month ago
warbird-docs preview

warbird-docs

GitHubwitherornot/warbird-docs

Documentation of Microsoft's Warbird obfuscation
binary-analysiseducationembedded-systems-security+2
912 years ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex
binary-analysisforensicsmalware-analysis+3
1910 months ago
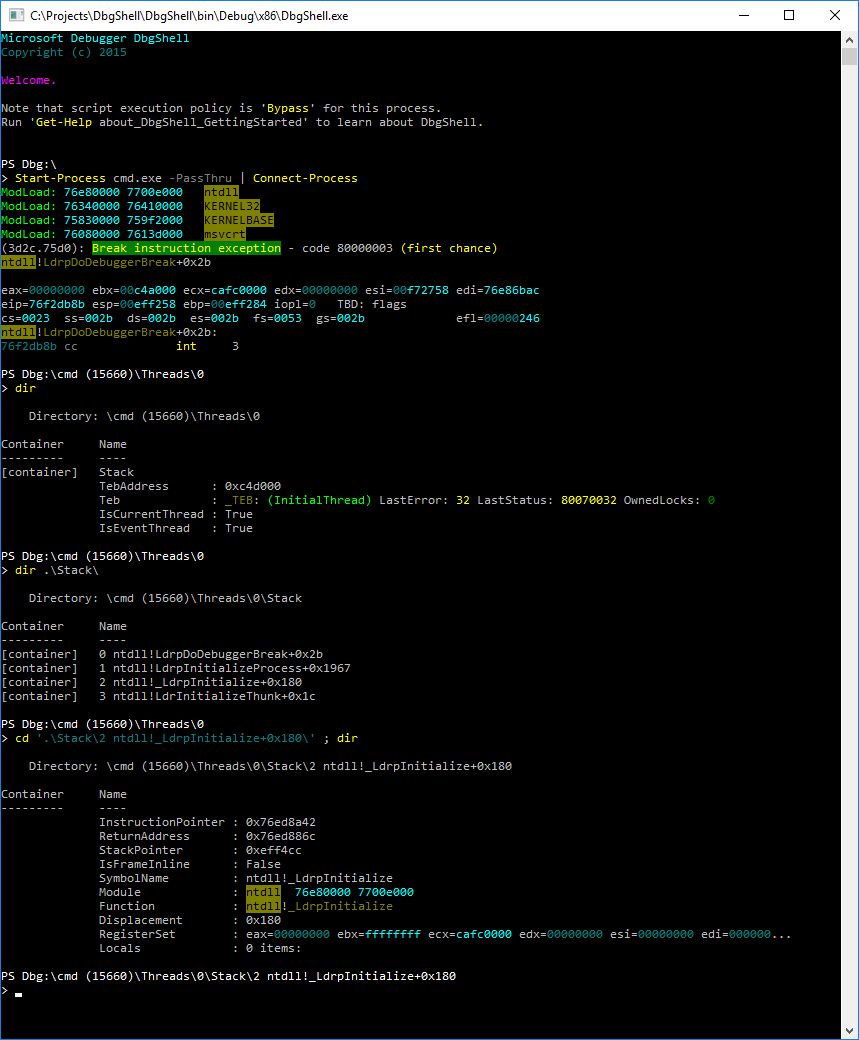
DbgShell preview

DbgShell

GitHubmicrosoft/dbgshell

A PowerShell front-end for the Windows debugger engine.

binary-analysisdebuggersreverse-engineering+2
7022 years ago
DefenderCheck preview

DefenderCheck

GitHubmatterpreter/defendercheck

Identifies the bytes that Microsoft Defender flags on.
binary-analysisdefensive-toolsmalware-analysis
2.6k3 years ago
ThreatCheck preview

ThreatCheck

GitHubrasta-mouse/threatcheck

Identifies the bytes that Microsoft Defender / AMSI Consumer flags on.

binary-analysisdefensive-toolsmalware-analysis+1
1.6k6 months ago
COM-Code-Helper preview

COM-Code-Helper

GitHubfboldewin/com-code-helper

Two IDAPython Scripts help you to reconstruct Microsoft COM (Component Object Model) Code

binary-analysisdebuggersmalware-analysis+1
1866 years ago
PsyloDbg preview

PsyloDbg

GitHubdarkcodersc/psylodbg

User-friendly Microsoft Windows Debugger for Malware Analysts.

binary-analysisdebuggersmalware-analysis+1
2093 years ago
MSDIA-x64 preview

MSDIA-x64

GitHubmalwaretech/msdia-x64

Enable Microsoft PDB support in Ghidra without installing Visual Studio
binary-analysisdebuggersfirmware-analysis+3
387 years ago
CVE-2026-20841_notepad_analysis preview

CVE-2026-20841_notepad_analysis

GitHubuky007/cve-2026-20841_notepad_analysis

Investigates Microsoft Notepad RCE vulnerability CVE-2026-20841 through binary analysis and PoC exploit development for educational purposes.

binary-analysiseducationexploitation+2
37 months ago
Previous12Next