

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
280 results
dynamorio preview

dynamorio

GitHubdynamorio/dynamorio

Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
binary-analysiscode-analysisdebuggers+3
3.2k
1 day ago
krie preview

krie

GitHubgui774ume/krie

Linux Kernel Runtime Integrity with eBPF

binary-analysisdefensive-toolsintrusion-detection
1872 years ago
keystone preview

keystone

GitHubkeystone-engine/keystone

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.6k3 months ago
javajive preview

javajive

GitHubyaklang/javajive

Pure-Go Java Decompiler and Serialization Operator
binary-analysiscode-analysismalware-analysis+4
223 days ago
ansvif preview

ansvif

GitHuboxagast/ansvif

A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.

binary-analysisexploitationfuzzing+2
1055 years ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
ai-assisted-reversingbinary-analysisbinary-exploitation+7
24 days ago
Furtex preview

Furtex

GitHubmatheuzsecurity/furtex

Post-exploitation and evasion research toolkit for Linux.
binary-analysiscommand-and-controlexploitation+6
2912 months ago
dd preview

dd

GitHubricccrd/dd

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…

binary-analysiscontainer-securitydevsecops+3
2591 month ago
autoPwn preview

autoPwn

GitHubbannsec/autopwn

Automate repetitive tasks for fuzzing

binary-analysisexploitationfuzzing
1255 years ago
MAccConc preview

MAccConc

GitHubgoogleprojectzero/maccconc

Toolkit for exploring Linux kernel race conditions using KCOV traces: GUI and terminal viewers for concurrent execution and memory access, plus…
binary-analysisdebuggersdynamic-analysis-sandboxing+6
521 month ago
manul preview

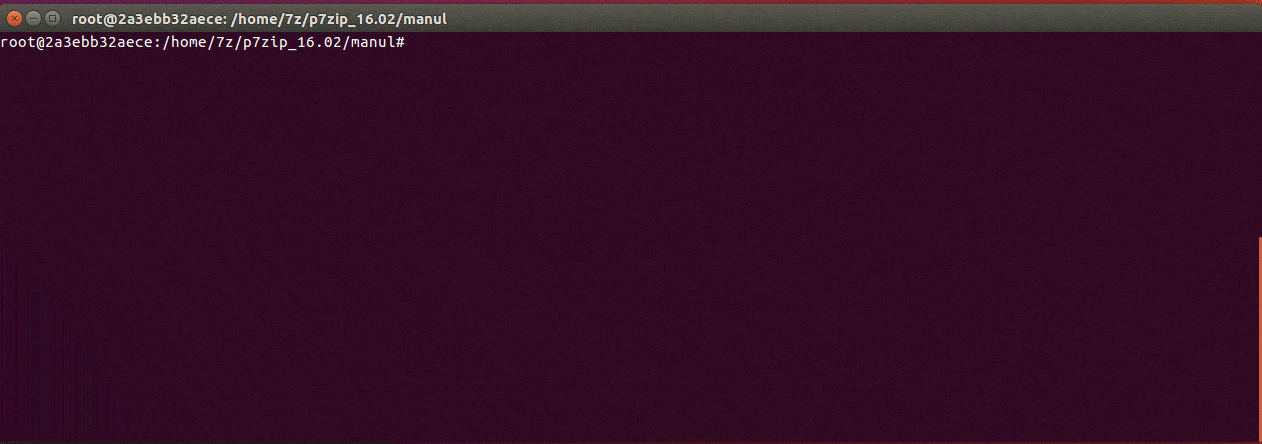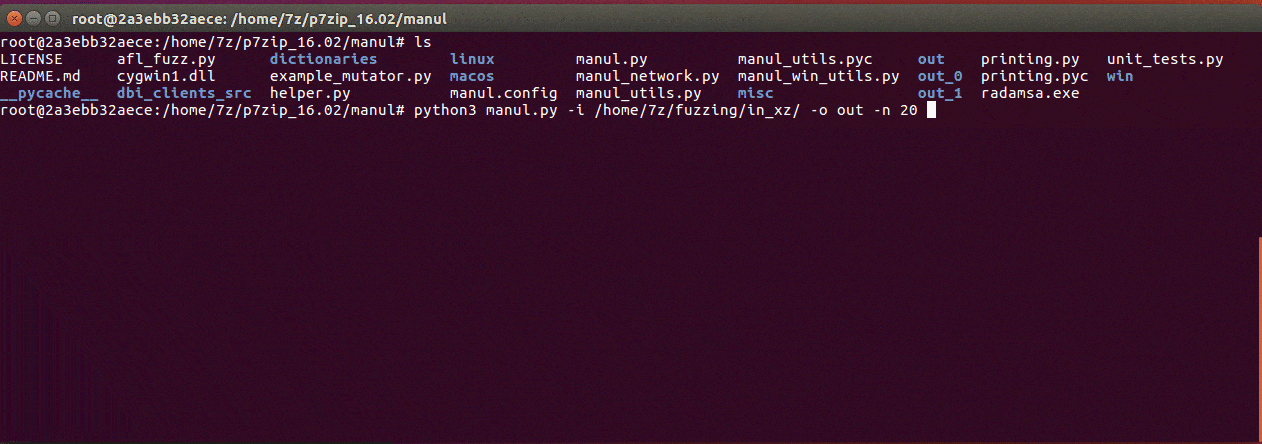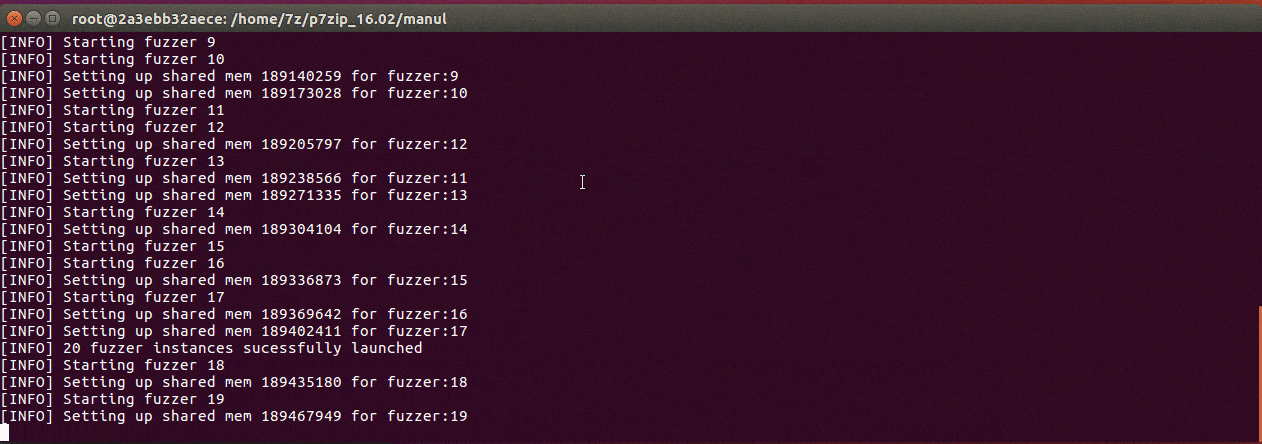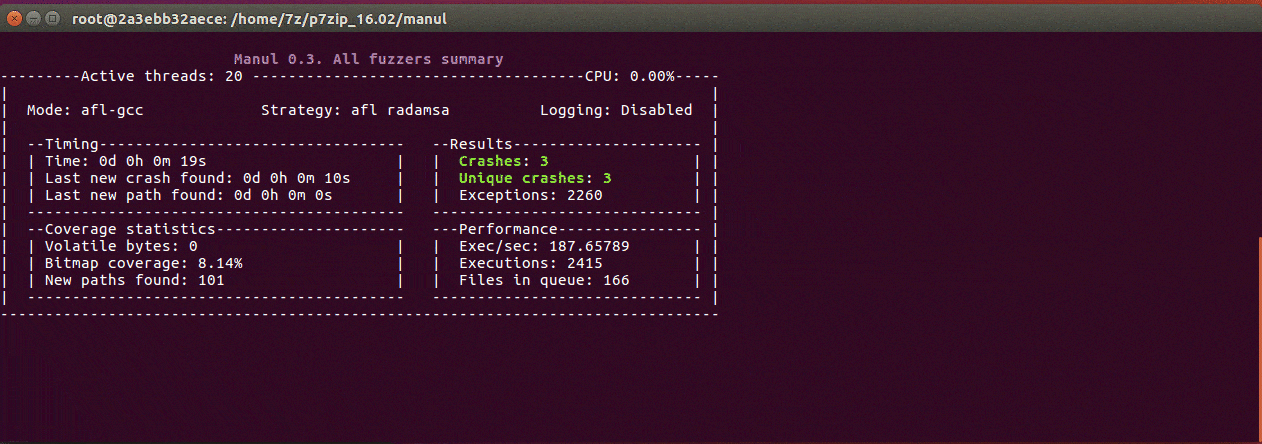
manul

GitHubmxmssh/manul

Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS

binary-analysisdynamic-analysis-sandboxingfuzzing+1
3356 years ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
binary-analysisfingerprint-spoofingids-ips-evasion+6
144 months ago
ida-cli preview

ida-cli

GitHubcpkt9762/ida-cli

Headless IDA Pro MCP server for AI-assisted binary analysis, powered by idalib
ai-assisted-reversingbinary-analysisreverse-engineering
304 days ago
LID preview

LID

GitHubazqzazq1/lid

LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…

binary-analysiseducationexploitation+6
204 months ago
qiling preview

qiling

GitHubqilingframework/qiling

A True Instrumentable Binary Emulation Framework
binary-analysisdebuggersdynamic-analysis-sandboxing+7
6.1k1 month ago
ghidra2frida preview

ghidra2frida

GitHubfedericodotta/ghidra2frida

Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…

android-securitybinary-analysisdynamic-analysis-sandboxing+3
1345 years ago
woody-woodpacker preview

woody-woodpacker

GitLabaurh1l-42-projects/woody-woodpacker

ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…

binary-analysisbinary-exploitationeducation+2
10 months ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .

binary-analysisdebuggerseducation+3
2266 days ago
Previous12…16Next