

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
11 results
DInvoke_rs preview

DInvoke_rs

GitHubkudaes/dinvoke_rs

Dynamically invoke arbitrary unmanaged code
binary-analysisids-ips-evasionpayload-development+3
3672 months ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
anticuckoo preview

anticuckoo

GitHubtherealdreg/anticuckoo

A tool to detect and crash Cuckoo Sandbox
binary-analysisids-ips-evasionmalware-analysis
2982 years ago
Bitmancer preview

Bitmancer

GitHubzimawhit3/bitmancer

Nim Library for Offensive Security Development
binary-analysisids-ips-evasionpayload-development+4
2003 years ago
recomposer preview

recomposer

GitHubsecretsquirrel/recomposer

Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
anti-botbinary-analysisids-ips-evasion+2
13212 years ago
userland-exec preview

userland-exec

GitHubhardenedlinux/userland-exec

Userland exec PoC to be used as attack vector technique
binary-analysisexploitationids-ips-evasion+2
1465 months ago
Bypass-Sandbox-Evasion preview

Bypass-Sandbox-Evasion

GitHubzeromemoryex/bypass-sandbox-evasion

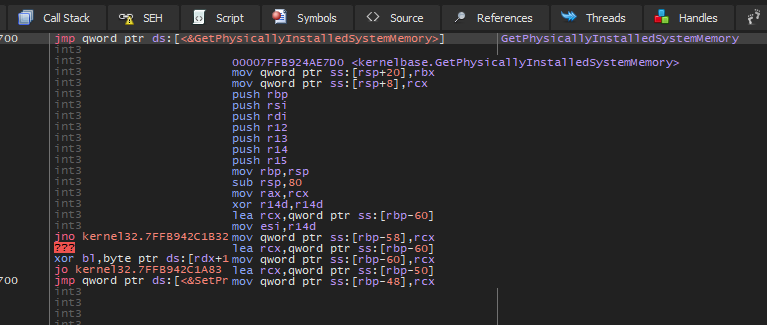
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
anti-botbinary-analysisids-ips-evasion+1
1413 years ago
peCloakCapstone preview

peCloakCapstone

GitHubv-p-b/pecloakcapstone

Platform independent peCloak fork based on Capstone
binary-analysisids-ips-evasionmalware-analysis+2
10911 years ago
360WFP_Exploit preview

360WFP_Exploit

GitHubkyxiaxiang/360wfp_exploit

BYOVD: Use 360 ​​WFP driver to block EDR/XDR network connection.

binary-analysisexploitationids-ips-evasion+6
1317 months ago
dyen preview

dyen

GitHubcenobyte-vincit/dyen

In-memory Mach-O dylib loader for stock macOS Python; decrypts, maps, and runs payloads without dlopen or writing to disk, with optional encrypted…

binary-analysiscryptographyids-ips-evasion+4
1 month ago
Darkcloak preview

Darkcloak

GitHub0x574r/darkcloak

Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…

binary-analysisfingerprint-spoofingids-ips-evasion+6
113 months ago