apiscope
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
api-security-testingbinary-analysisdebuggers+4
kaisonox/apiscopeAn API hooking framework for intercepting and monitoring Windows applications
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
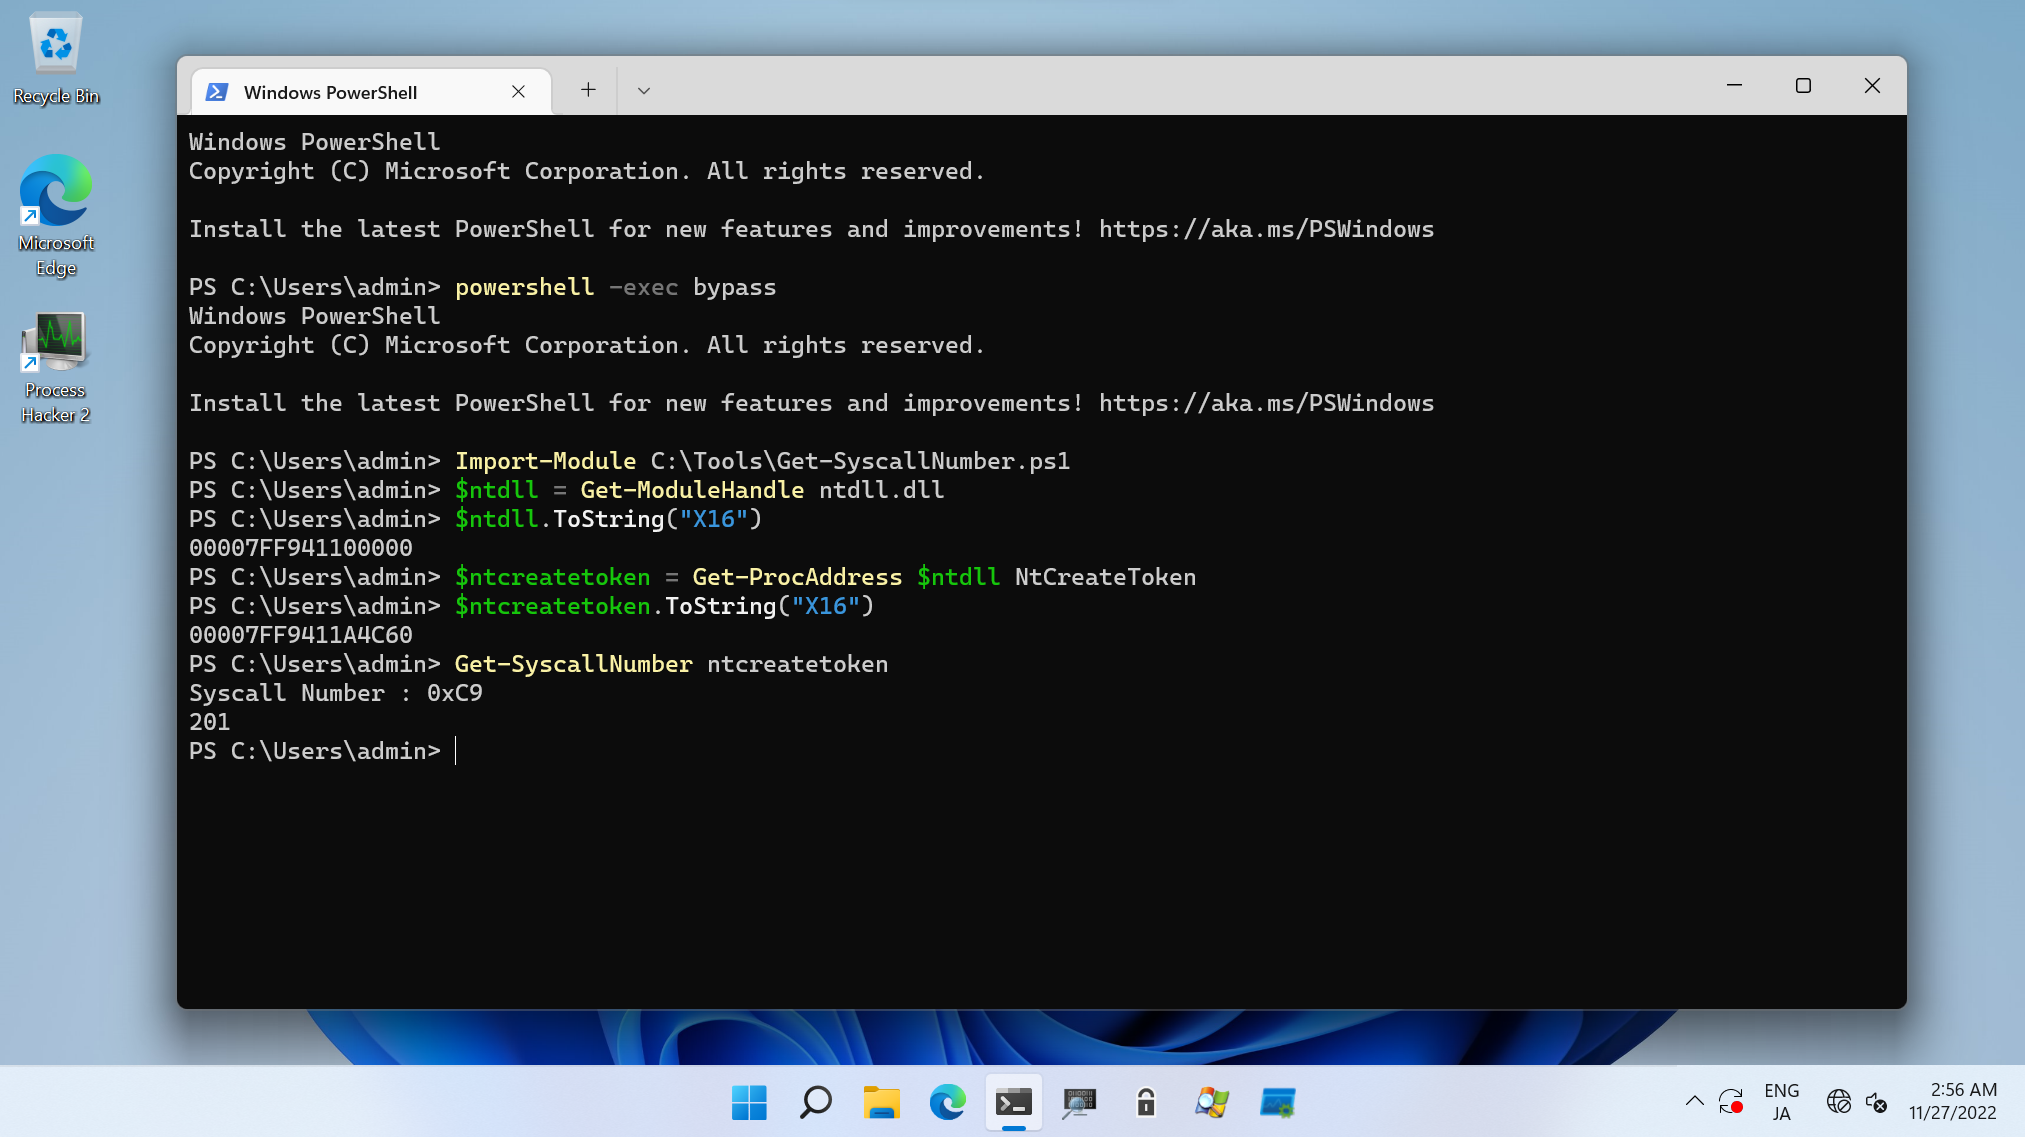 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 simoneavogadro/android-reverse-engineering-skill
Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
 futureslab/binvariants
Register-level invariant-guided fuzzing framework for closed-source binaries, leveraging likely invariant violations to discover crashes and bugs in…
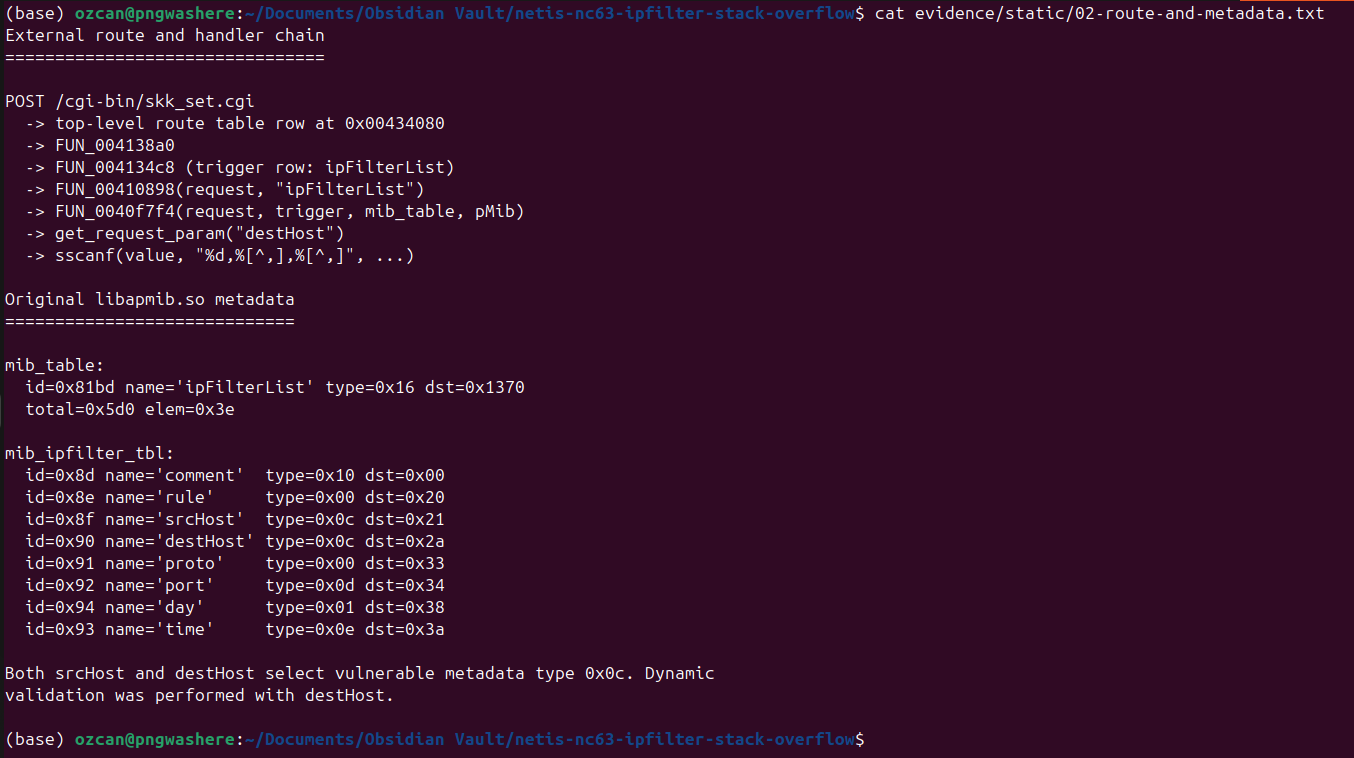 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
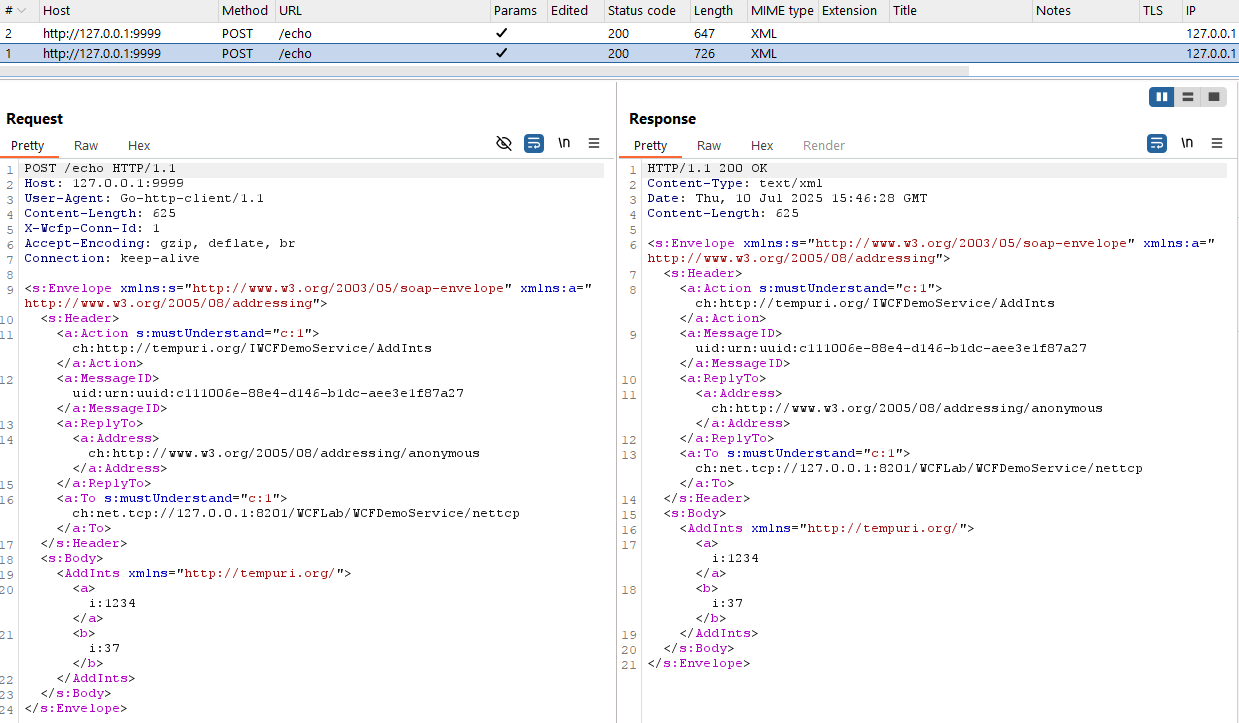 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 colton1skees/dna
LLVM based static binary analysis framework
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 tarpeg007/cve-2026-19490
NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC