
netzob
 netzob/netzob
Open-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
binary-analysisfuzzingnetwork-security+1
839
netzob/netzobOpen-source toolkit for reverse engineering, modeling, and fuzzing communication protocols. Infers message formats and state machines from network…
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
 freddierice/cve-2020-35498-flag
C-based exploit tool to detect and trigger CVE-2020-35498 via raw socket injection with BPF filter, targeting wireless interfaces for vulnerability…
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
 corelight/zeek-elf
A Zeek ELF File Analyzer
 jm00nj/hpe-aruba-aos8-vulnerabilities
ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…
 rohithronanki/cve-2026-34159-vulnerability-research-analysis-detection
Critical buffer validation bypass in deserialize_tensor() (llama.cpp < b8492). Null tensor buffer skips bounds check, enabling unauthenticated…
 personnumber3377/windows_tcpip_fuzz
This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…
 wildfootw/cve-2014-0160_openssl_1.0.1f_heartbleed
Exploit for the Heartbleed vulnerability (CVE-2014-0160) in OpenSSL 1.0.1f, allowing memory disclosure from vulnerable servers.
 0vercl0k/cve-2021-24086
Proof of concept for CVE-2021-24086, a NULL dereference in tcpip.sys triggered remotely.
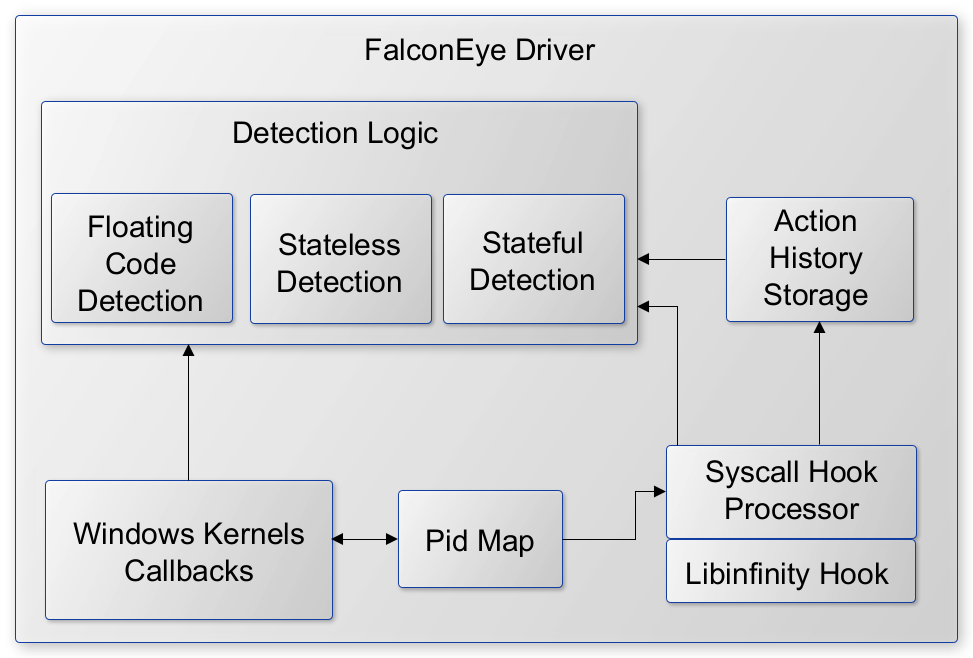 rajiv2790/falconeye
Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
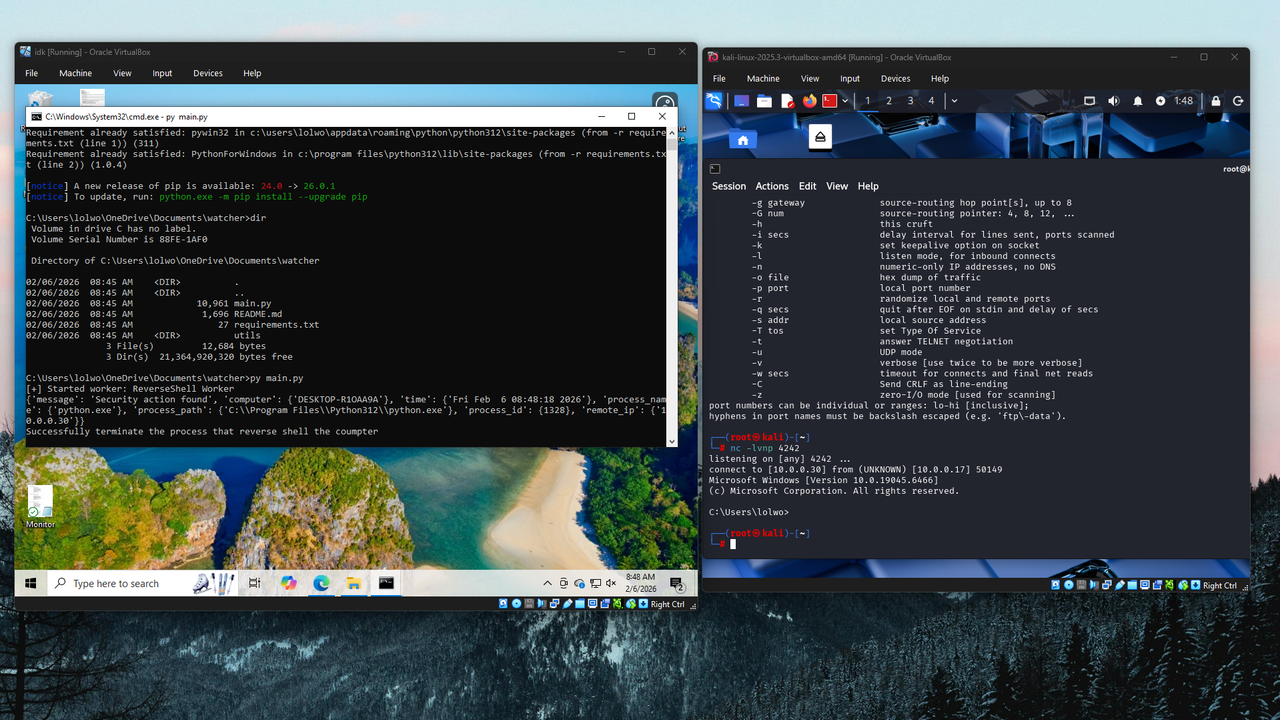 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 h4ckm310n/cve-2022-0847-ebpf
An eBPF program to detect attacks on CVE-2022-0847
 gui774ume/krie
Linux Kernel Runtime Integrity with eBPF
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
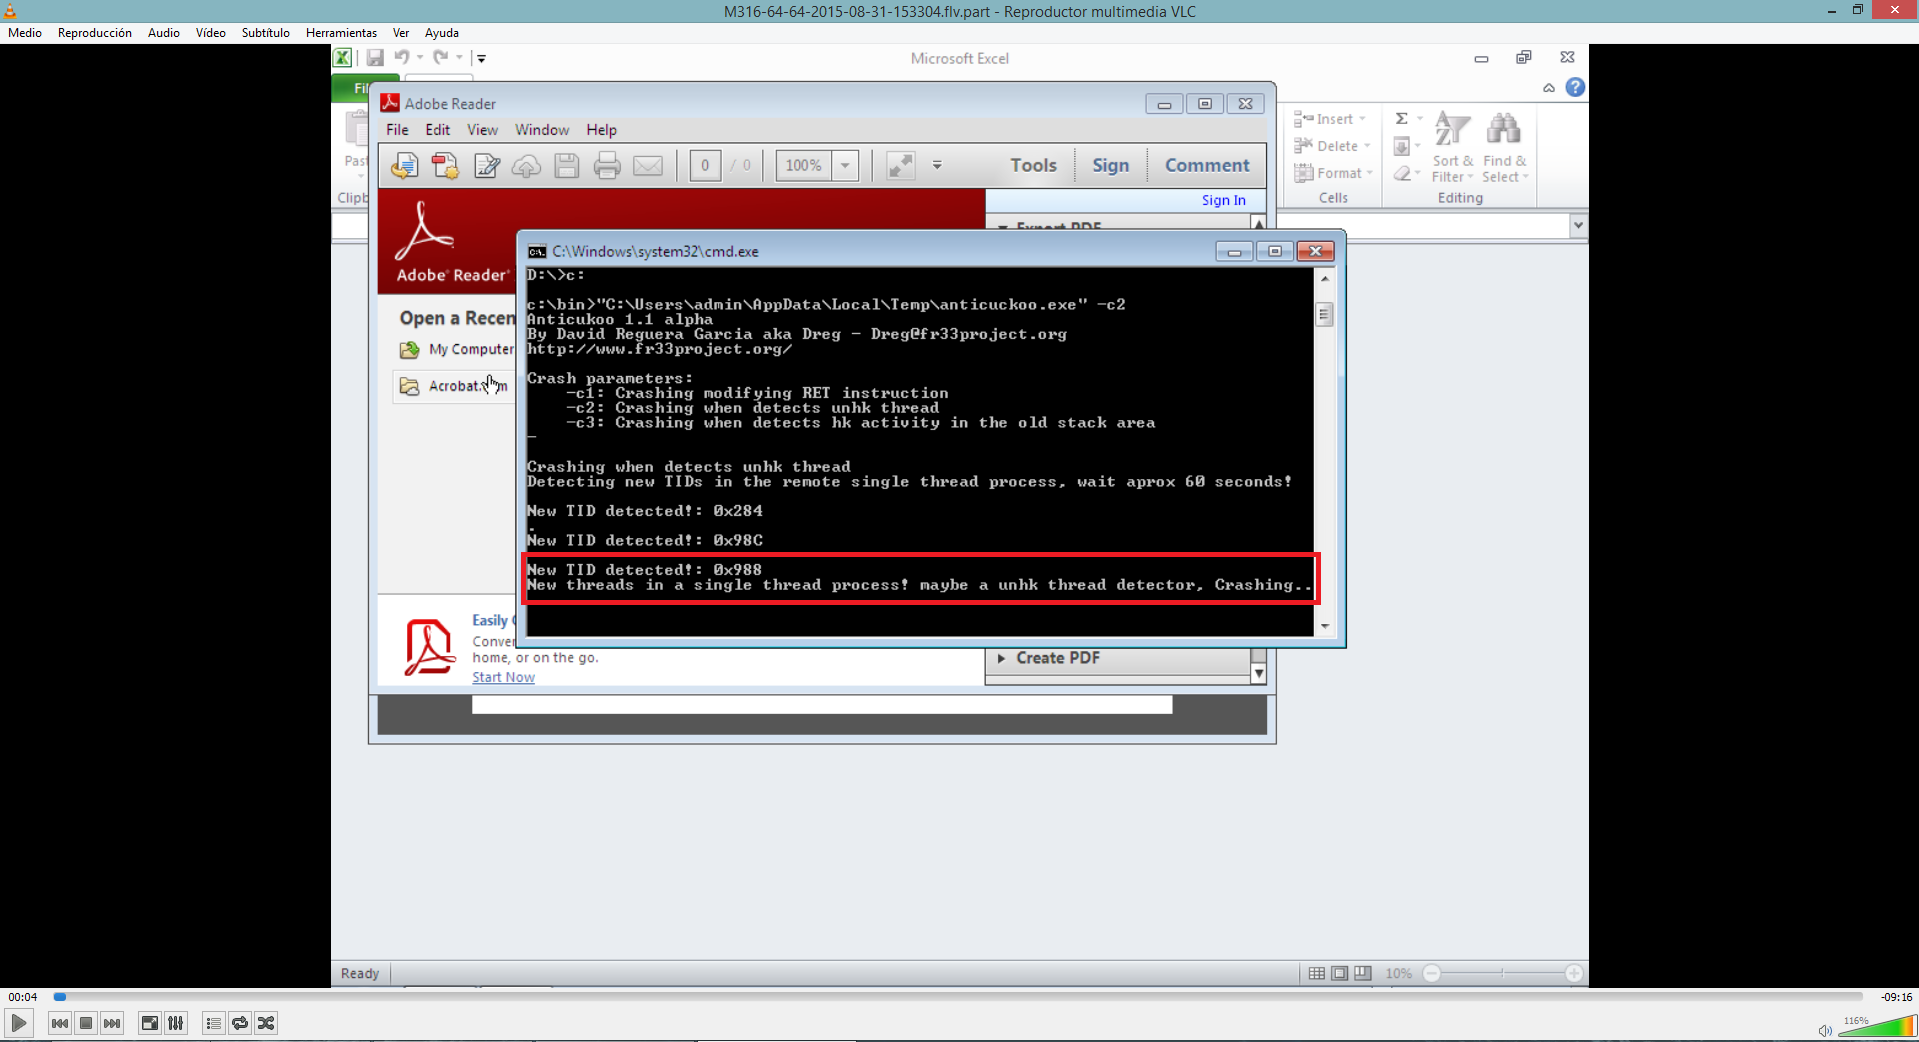 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.