
XenoScan
 nickcano/xenoscan
Open source memory scanner written in C++
binary-analysisdebuggersexploitation+2
3695 years ago
nickcano/xenoscanOpen source memory scanner written in C++
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
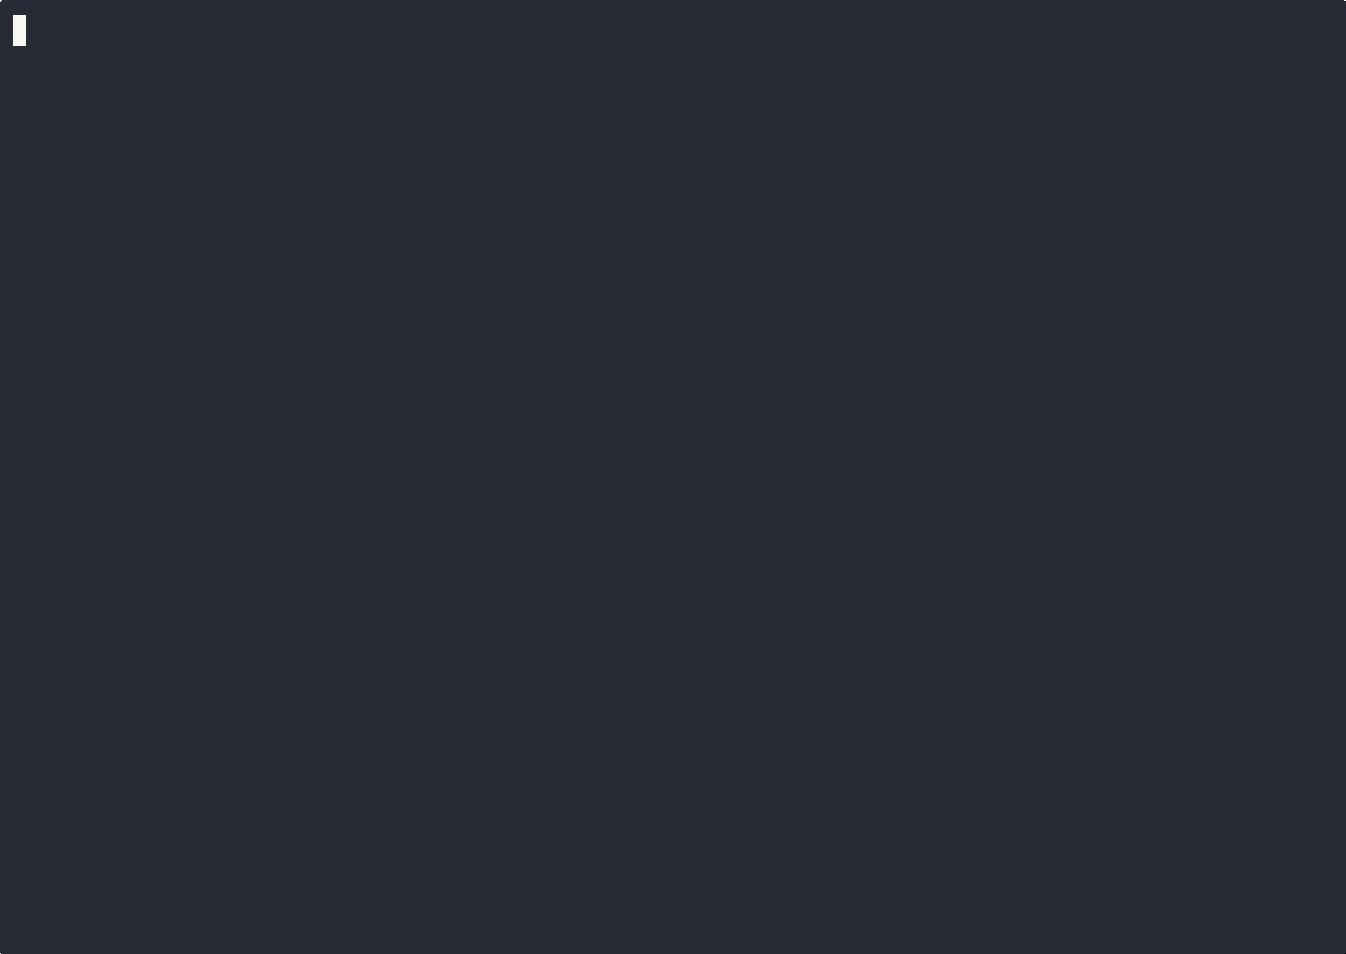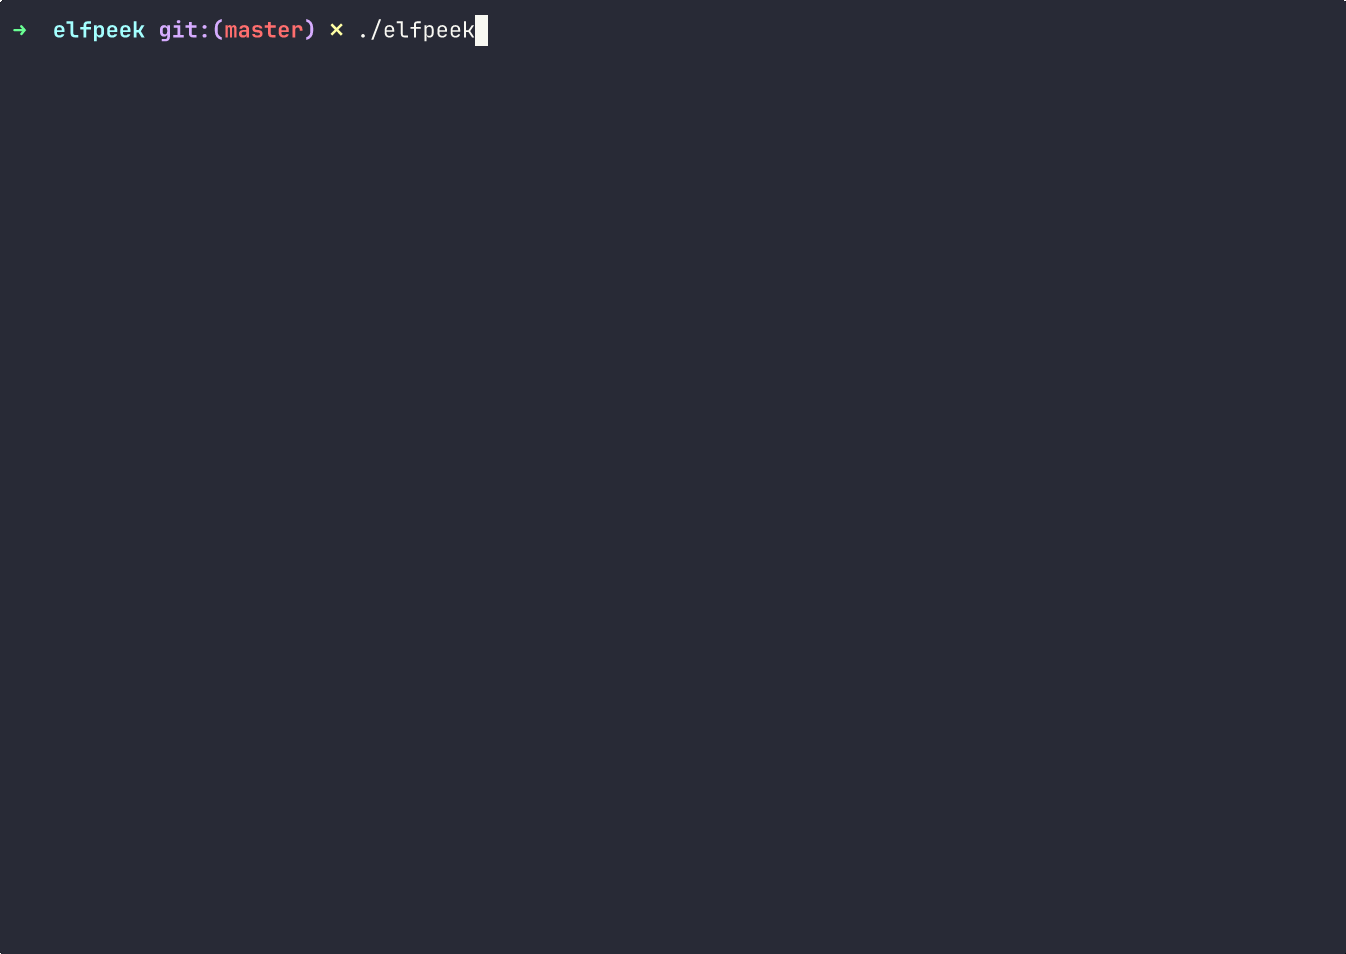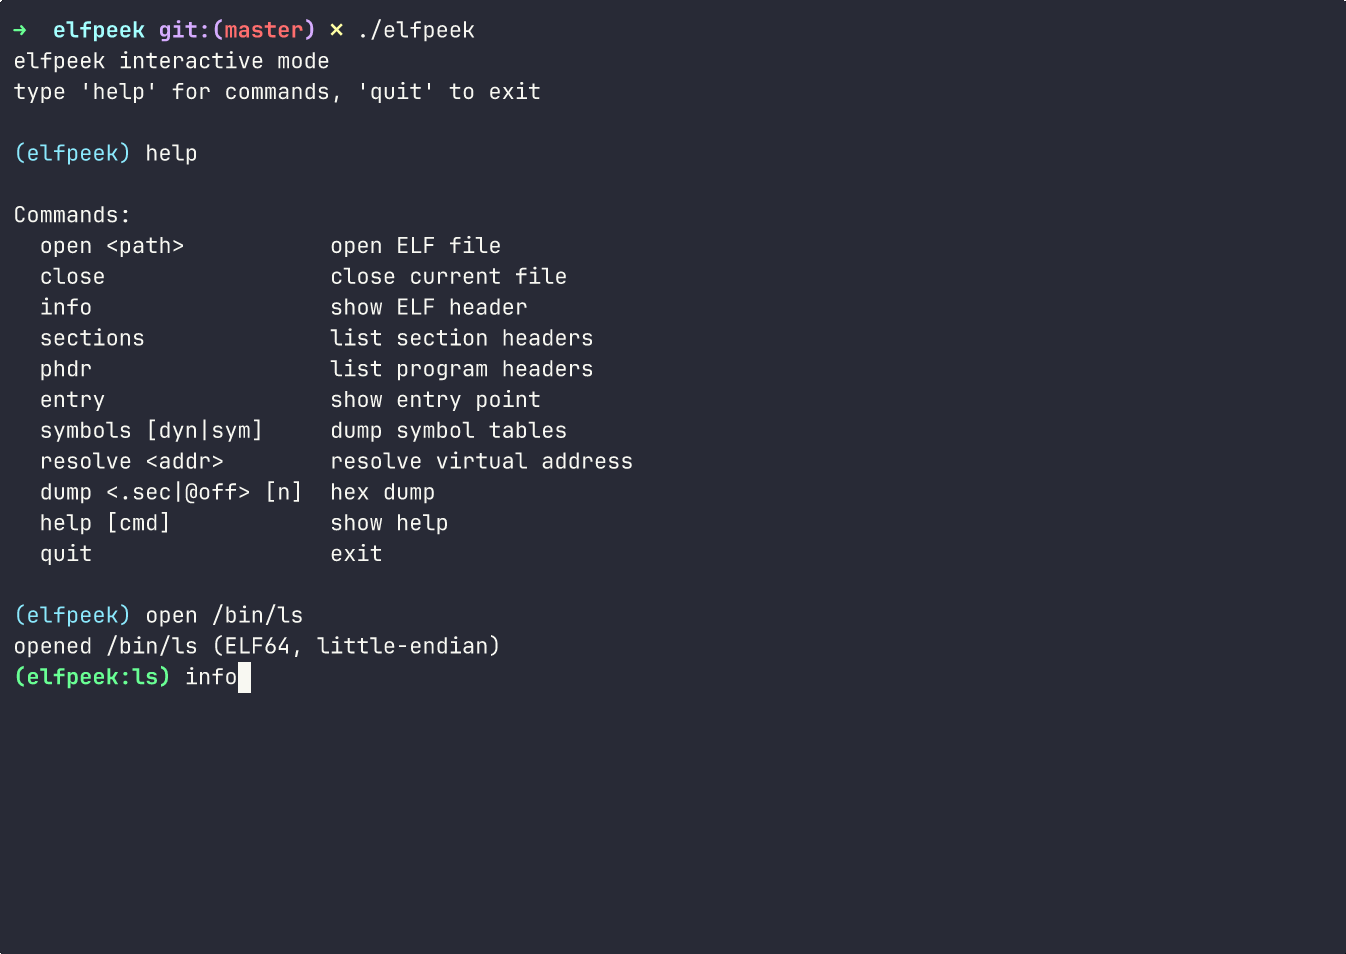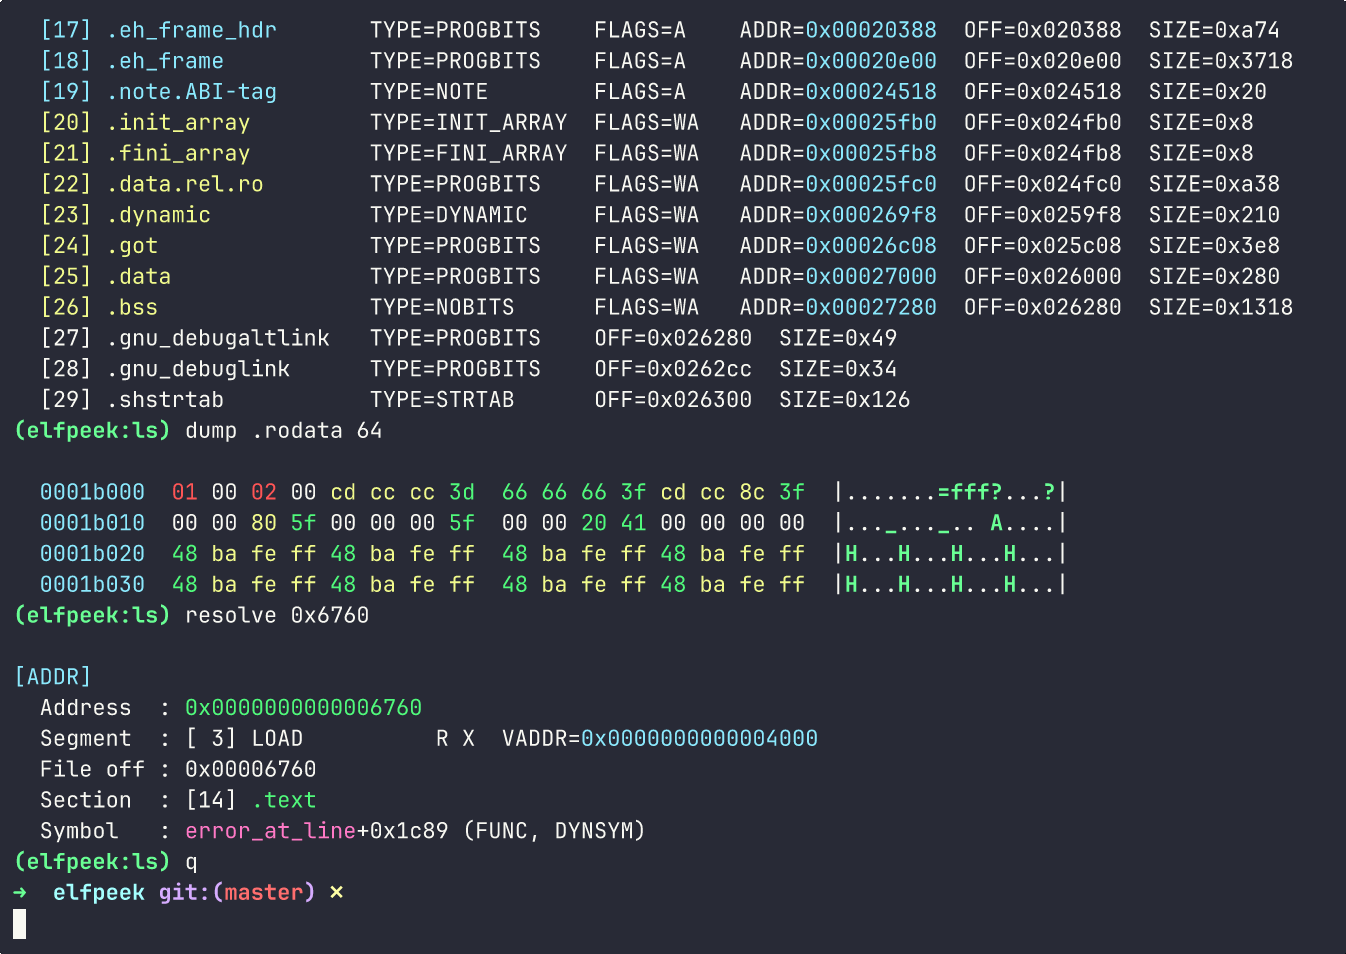 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection
 galoisinc/mate
Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…
 timon-l/3007project
Secure coding project, research on CVE-2019-17498 and implement a player score function written in C.
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
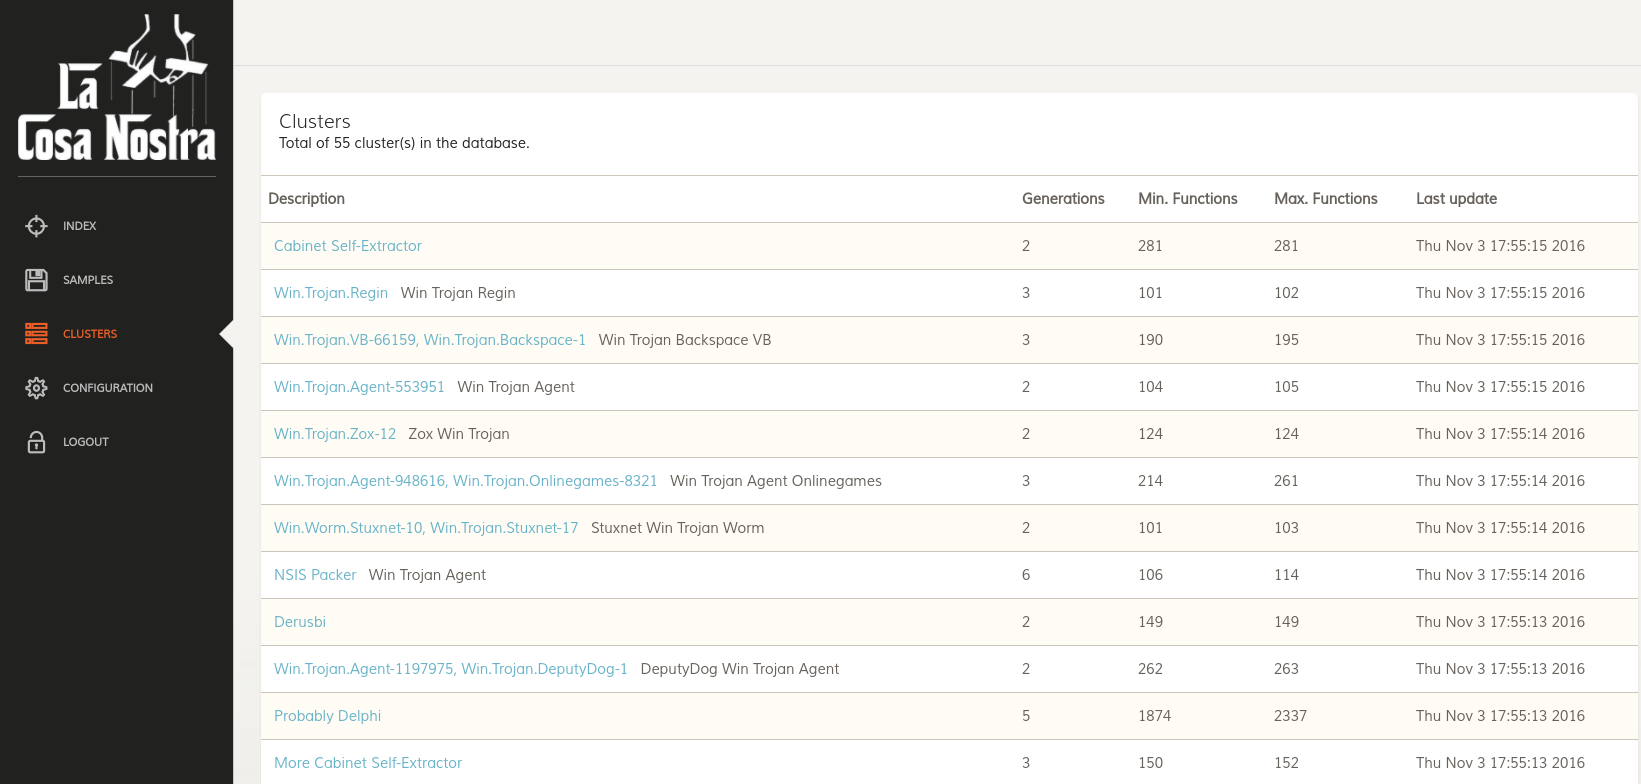 joxeankoret/cosa-nostra
Cosa Nostra, a FOSS graph based malware clusterization toolkit.
 pazhanivel07/openjpeg-2.3.0_cve-2020-27824
CVE-2020-27824 exploit reproduction environment for OpenJPEG JPEG 2000 codec, enabling vulnerability analysis, fuzzing, and binary exploitation…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 vardhan0257/upb-any-recursion-audit
Audit harness testing whether the CVE-2026-0994 Any-unwrapping recursion bug class affects upb's C core in Ruby and PHP protobuf bindings, with…
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
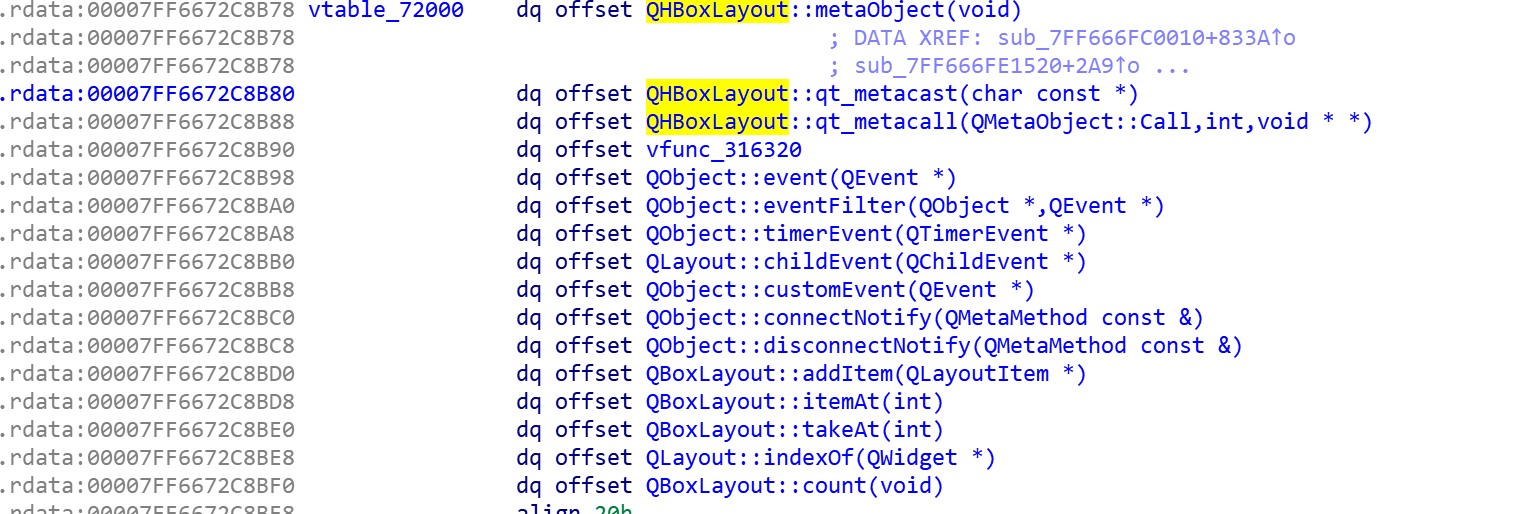 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 logsec/cve-2010-2387
Proof-of-concept exploit for CVE-2010-2387, a privilege escalation vulnerability in GNOME Display Manager (GDM). Includes C source code targeting the…
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 runtimeverification/kernel-c-to-rust-spike
Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).
 malwaretech/msdia-x64
Enable Microsoft PDB support in Ghidra without installing Visual Studio
 saurabh2088/expat_2_1_0_cve-2024-28757
C library for stream-oriented XML parsing, with a focus on analyzing and reproducing CVE-2024-28757 vulnerability in Expat 2.1.0.