

replica
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
binary-analysiscryptographymalware-analysis+2
315
reb311ion/replicaGhidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
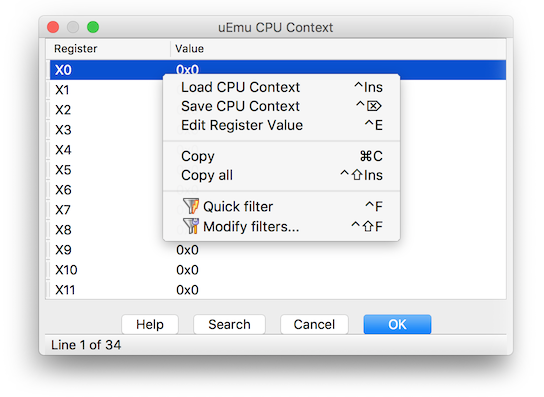 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
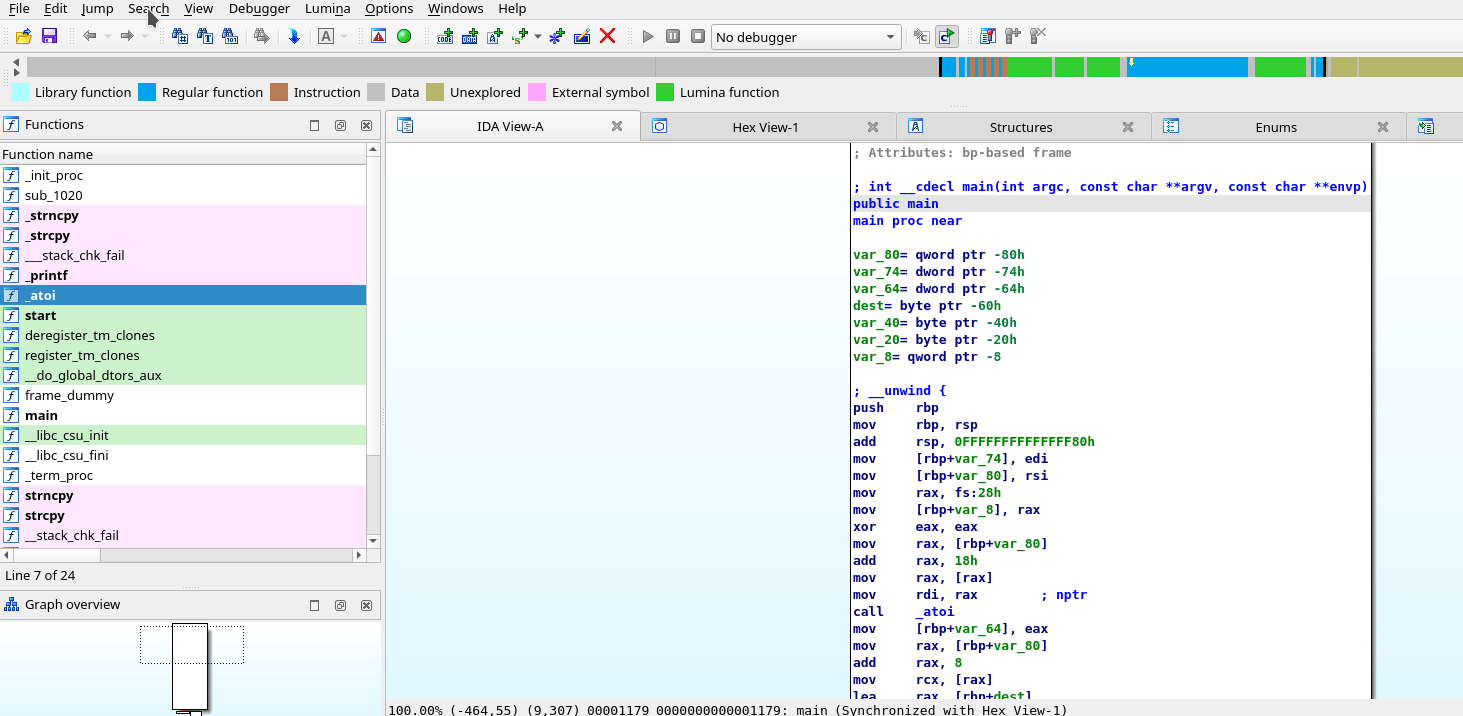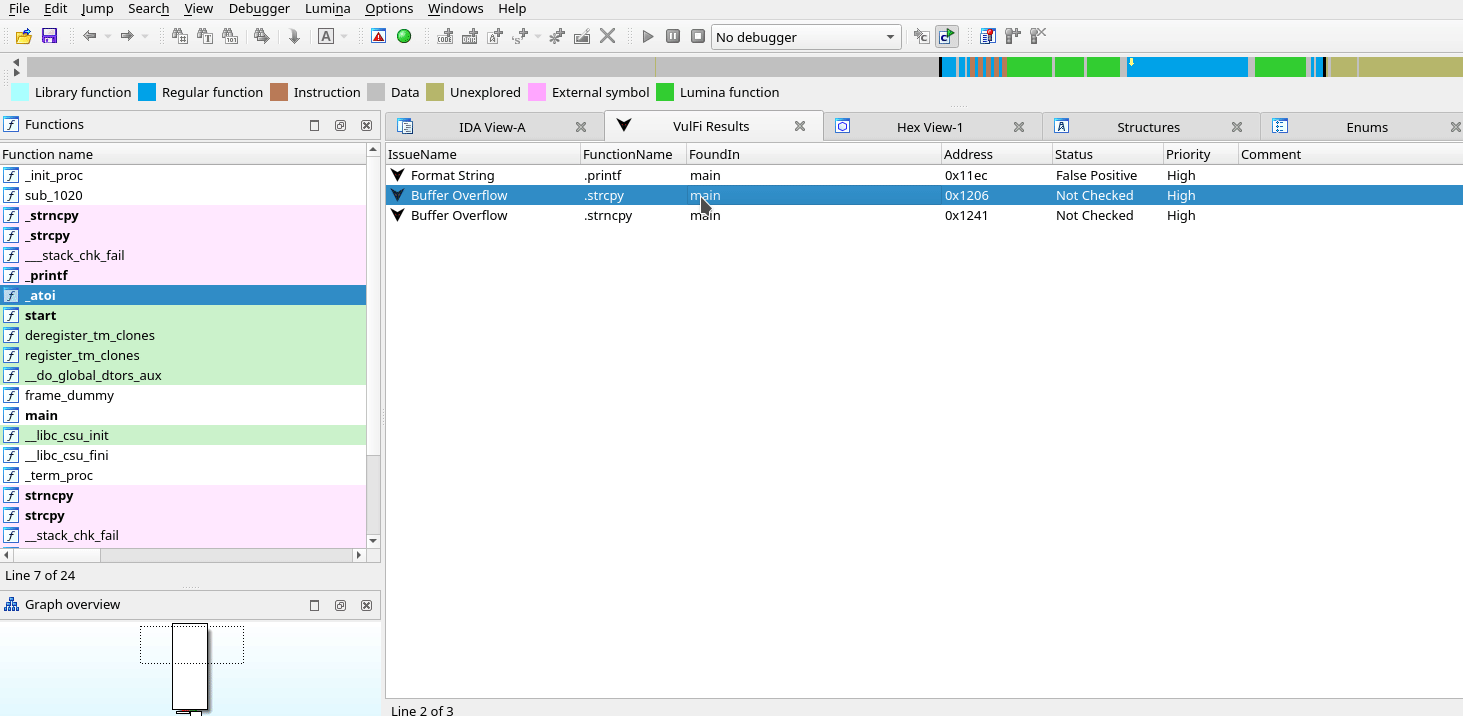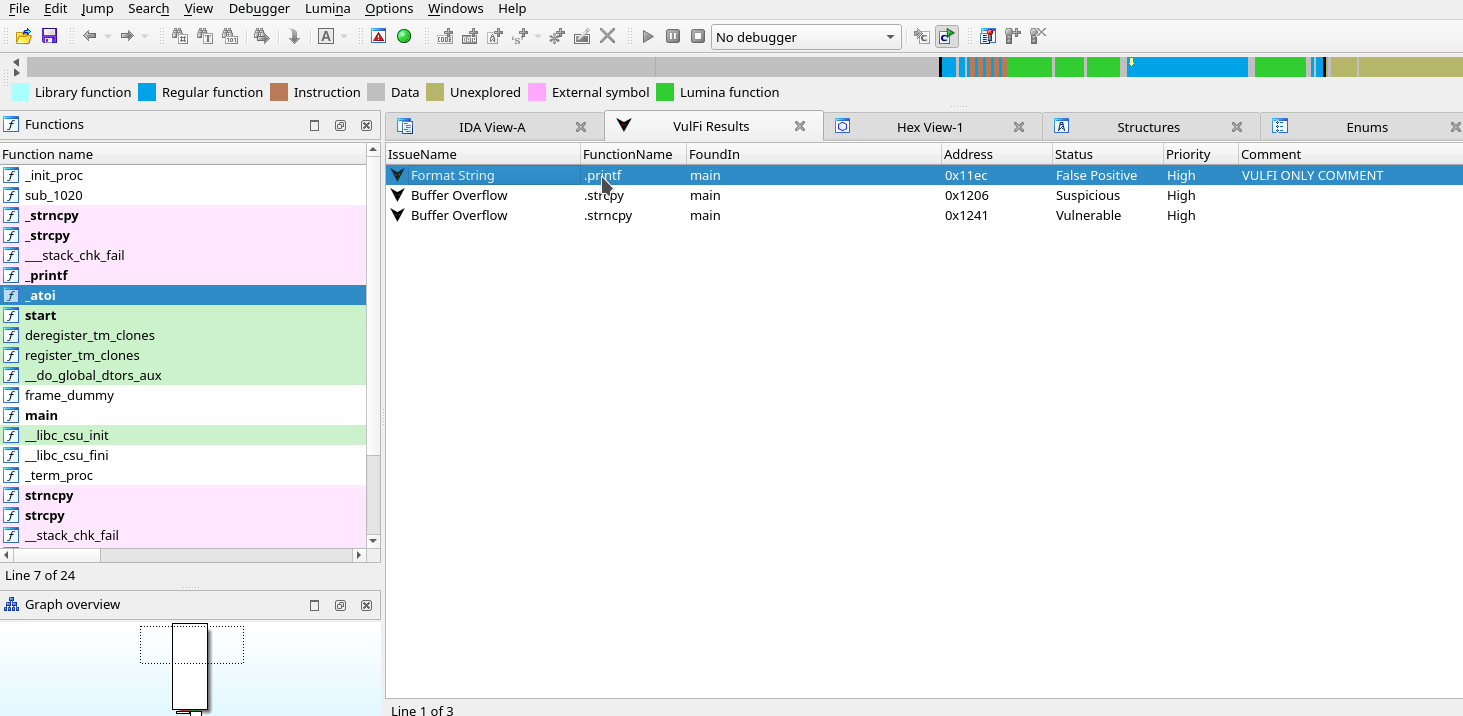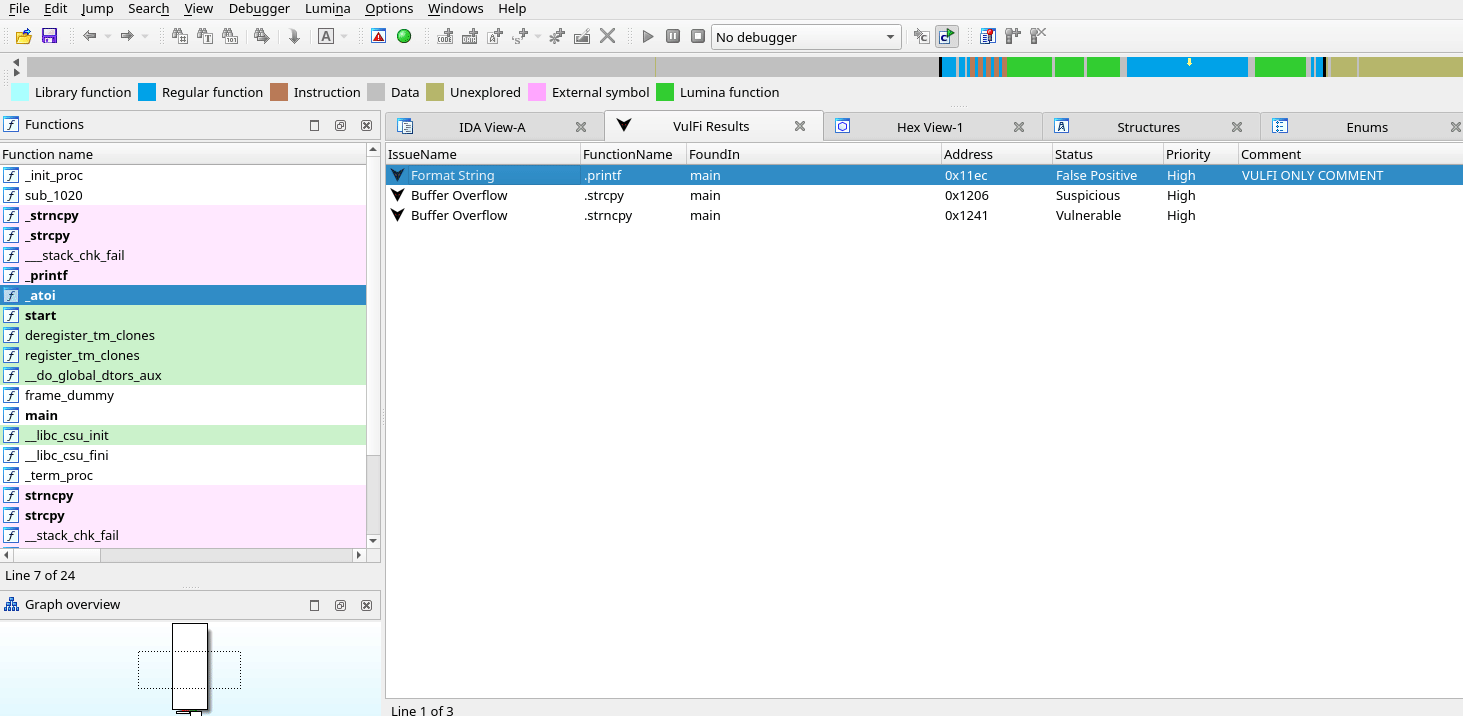 accenture/vulfi
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
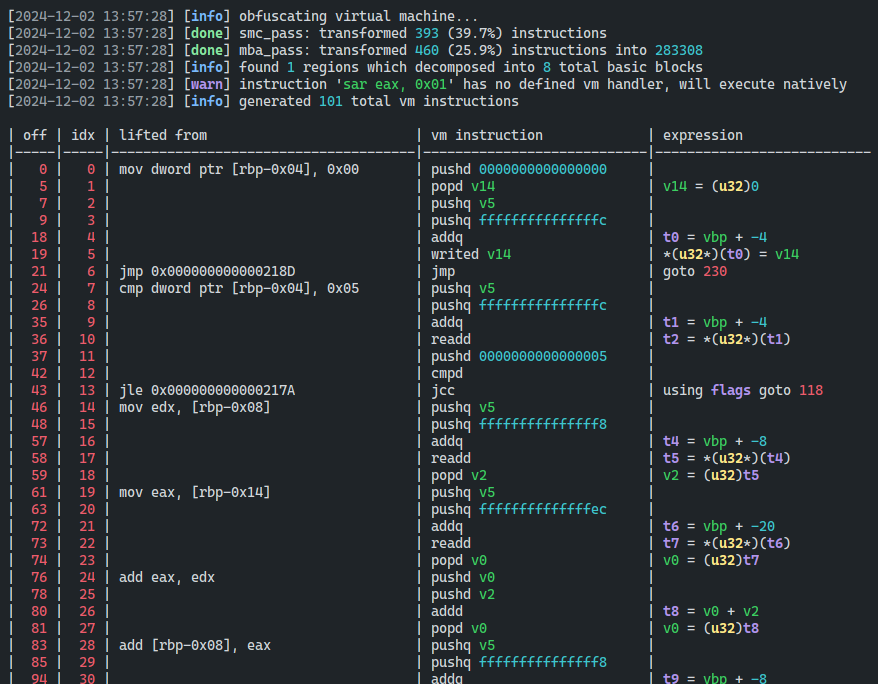 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
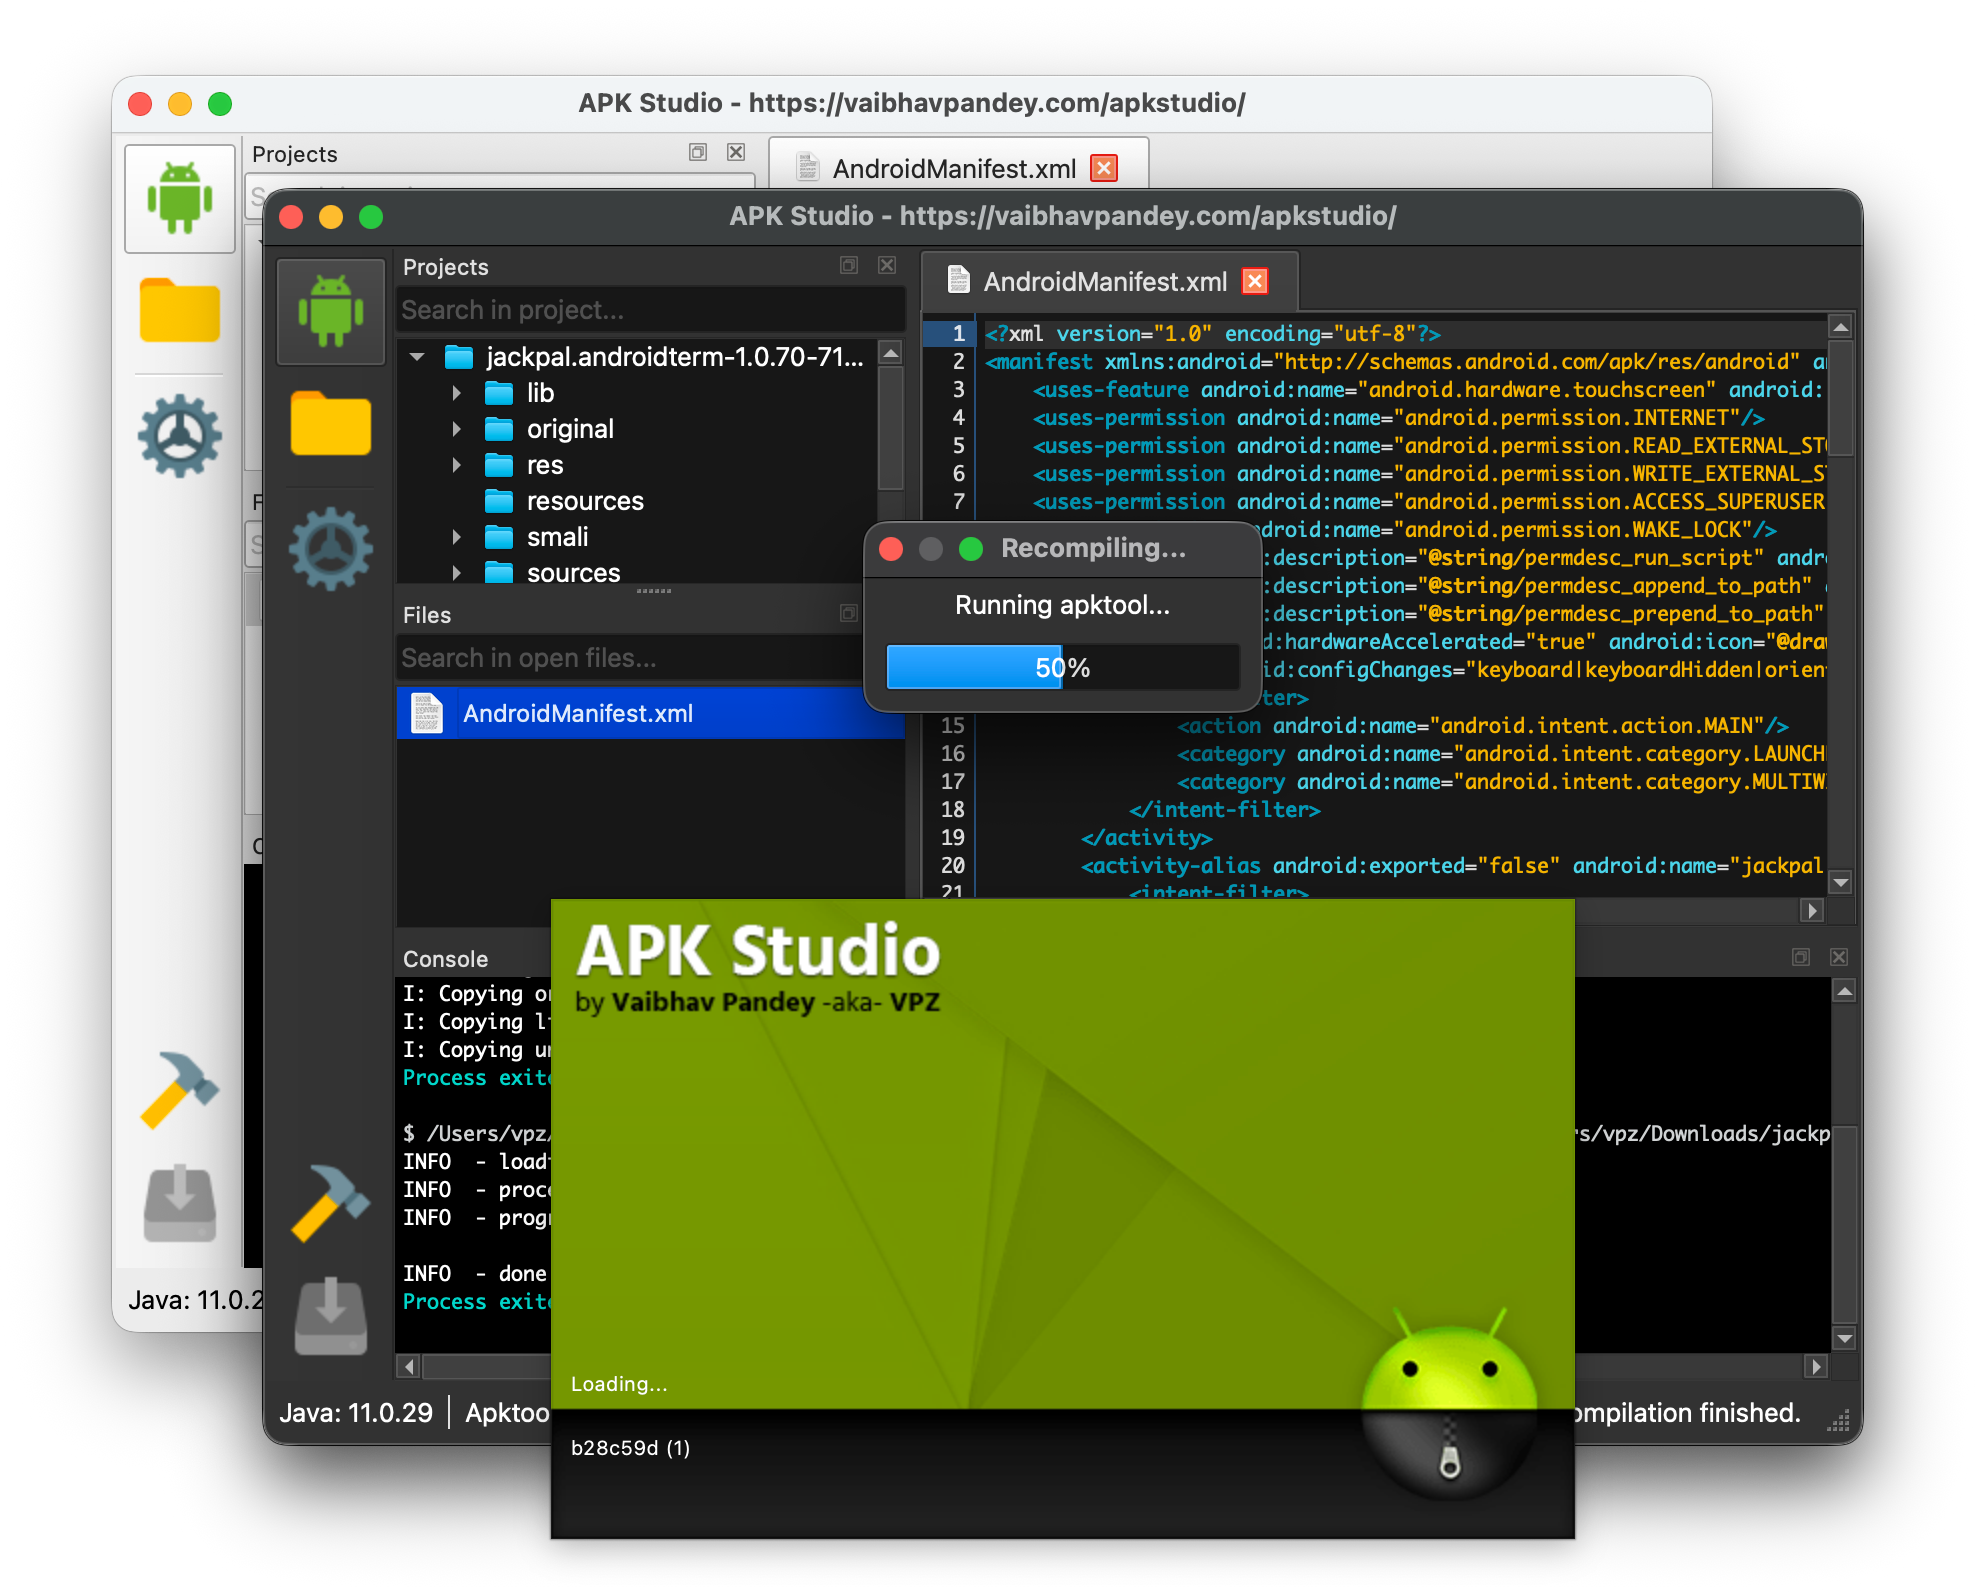 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
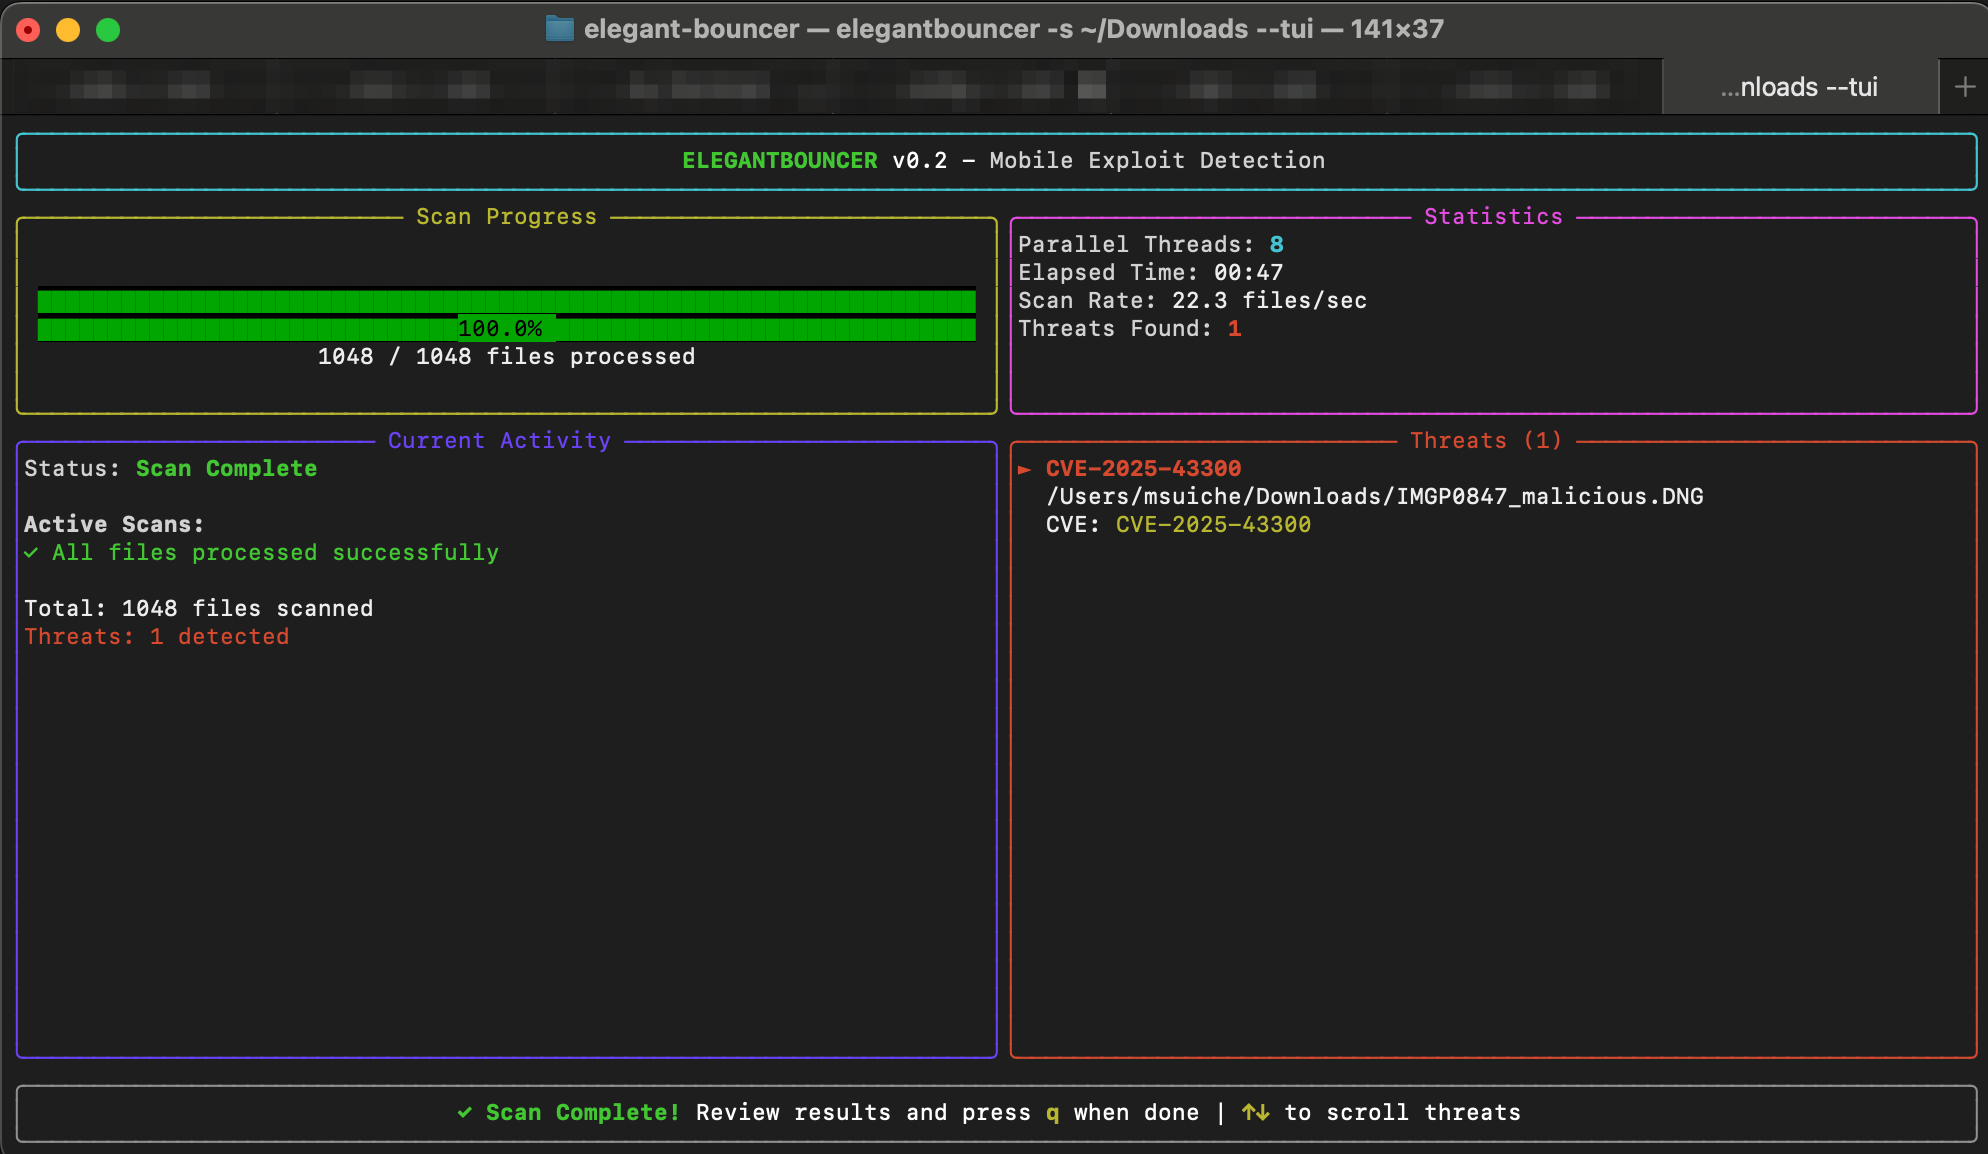 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 l33tdawg/aether
AI Smart Contract Security Analysis and PoC Generation Framework
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 websecnl/cve-2024-5535
PoC - OpenSSL NPN Buffer Overread
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 komimoe/arkari
Yet another llvm based obfuscator based on goron.
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework