
Archived
pe_tree
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
binary-analysisdebuggersdigital-forensics+5
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 zrax/pycdc
C++ python bytecode disassembler and decompiler
 cea-sec/miasm
Reverse engineering framework in Python
 rocky/python-uncompyle6
A cross-version Python bytecode decompiler
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
 trailofbits/fickling
A Python pickling decompiler and static analyzer
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
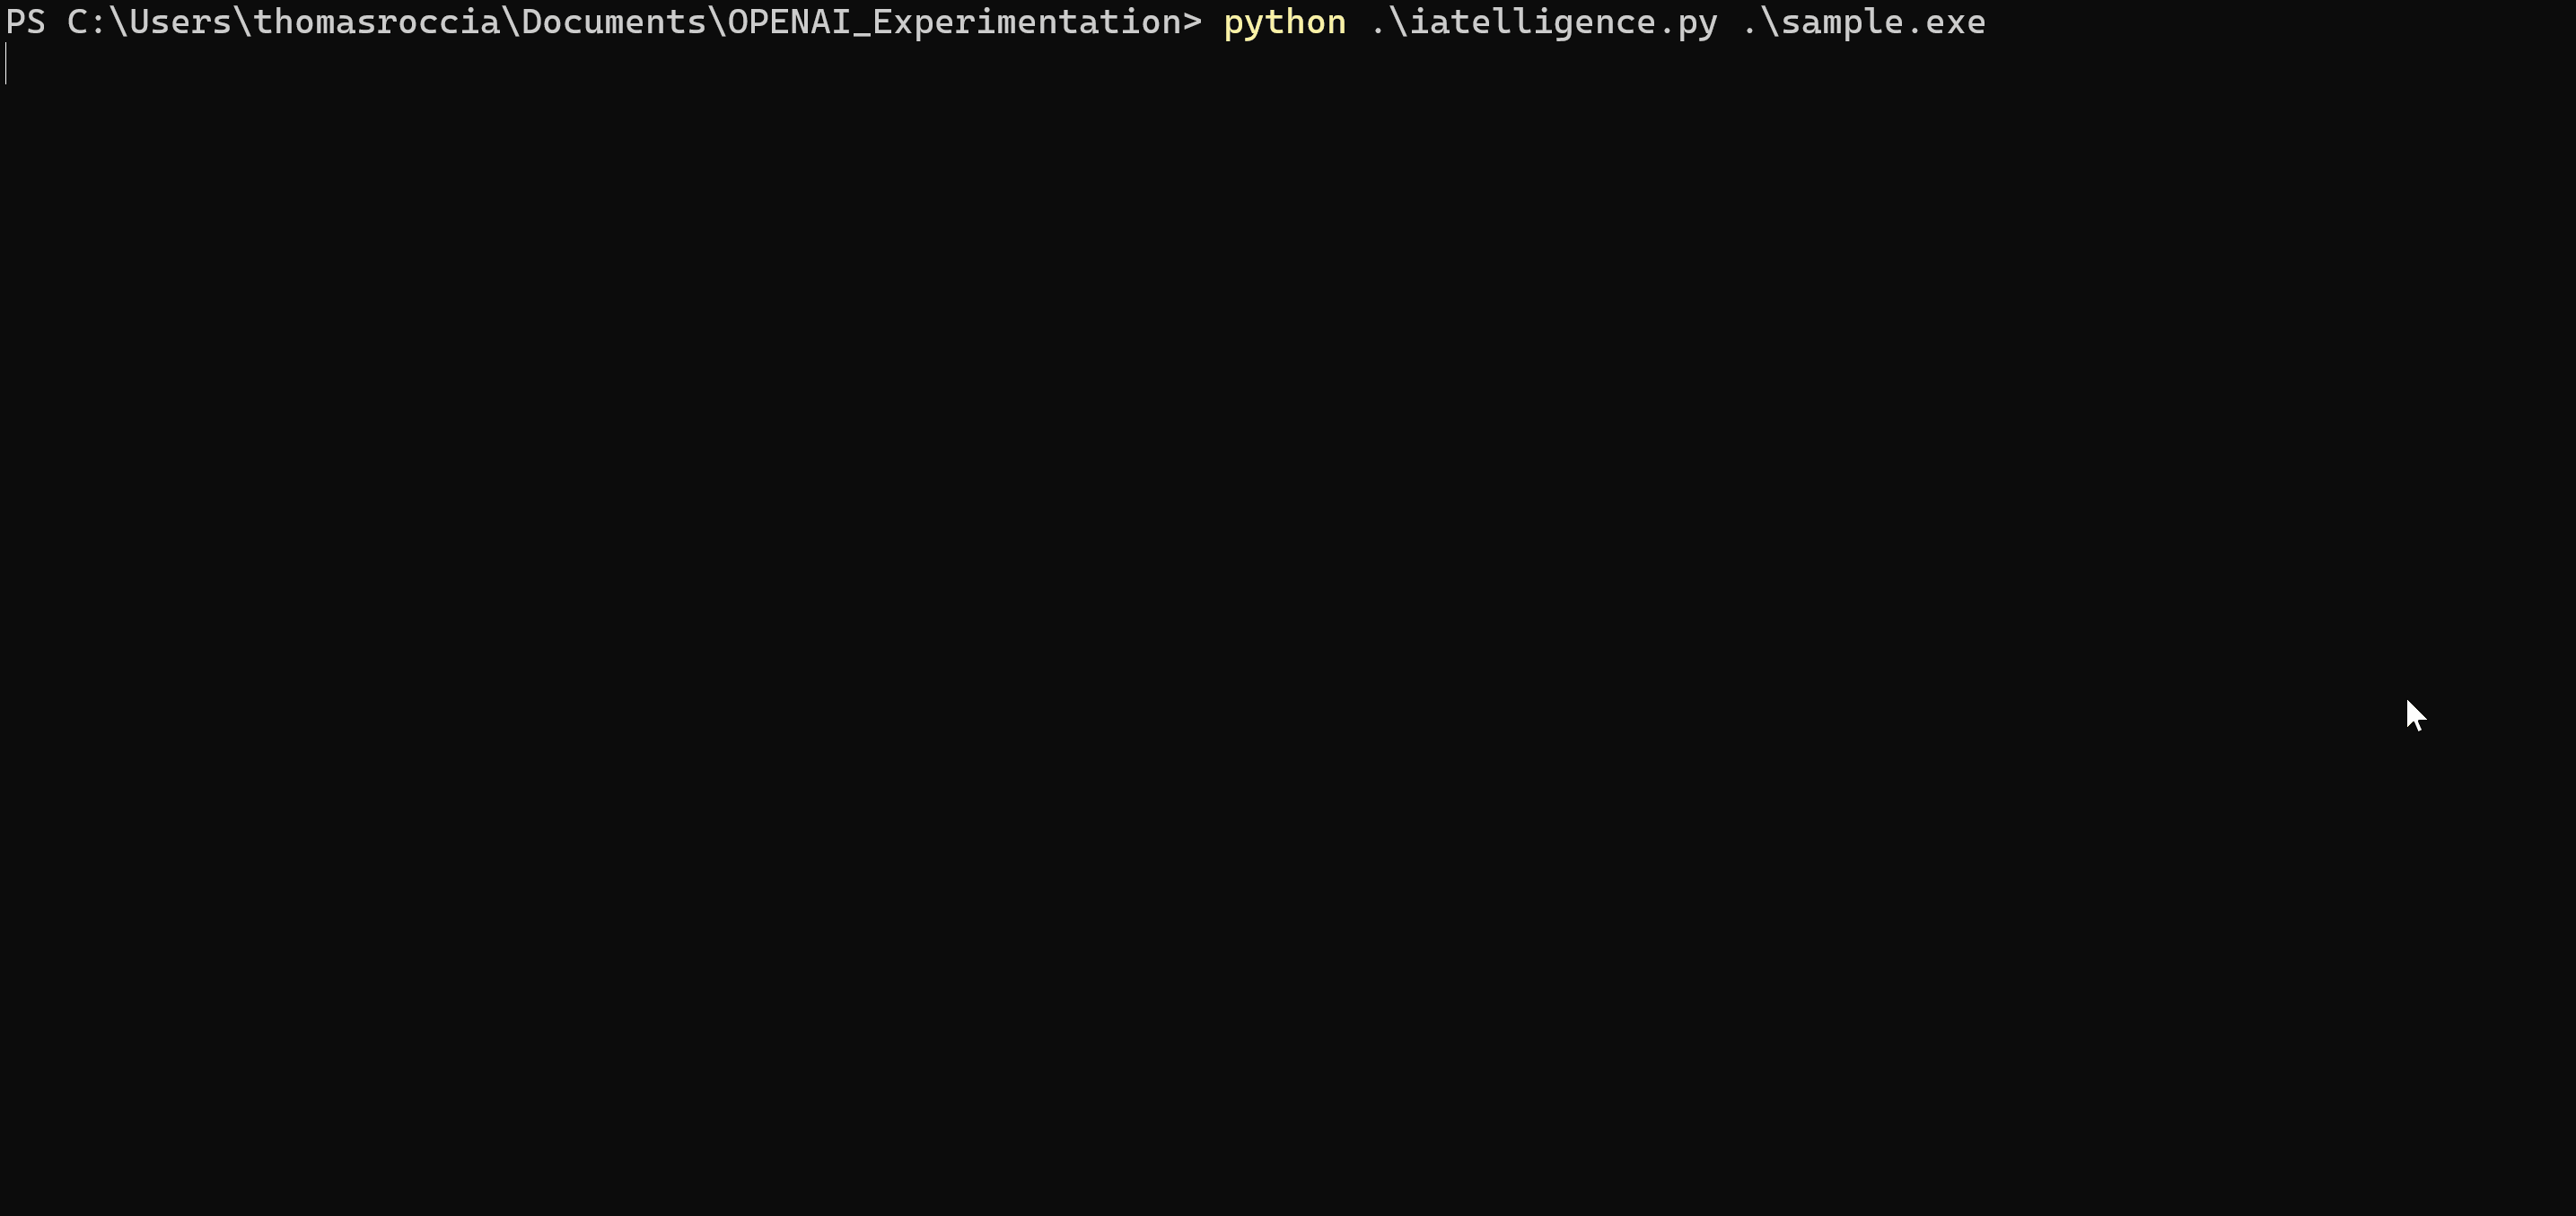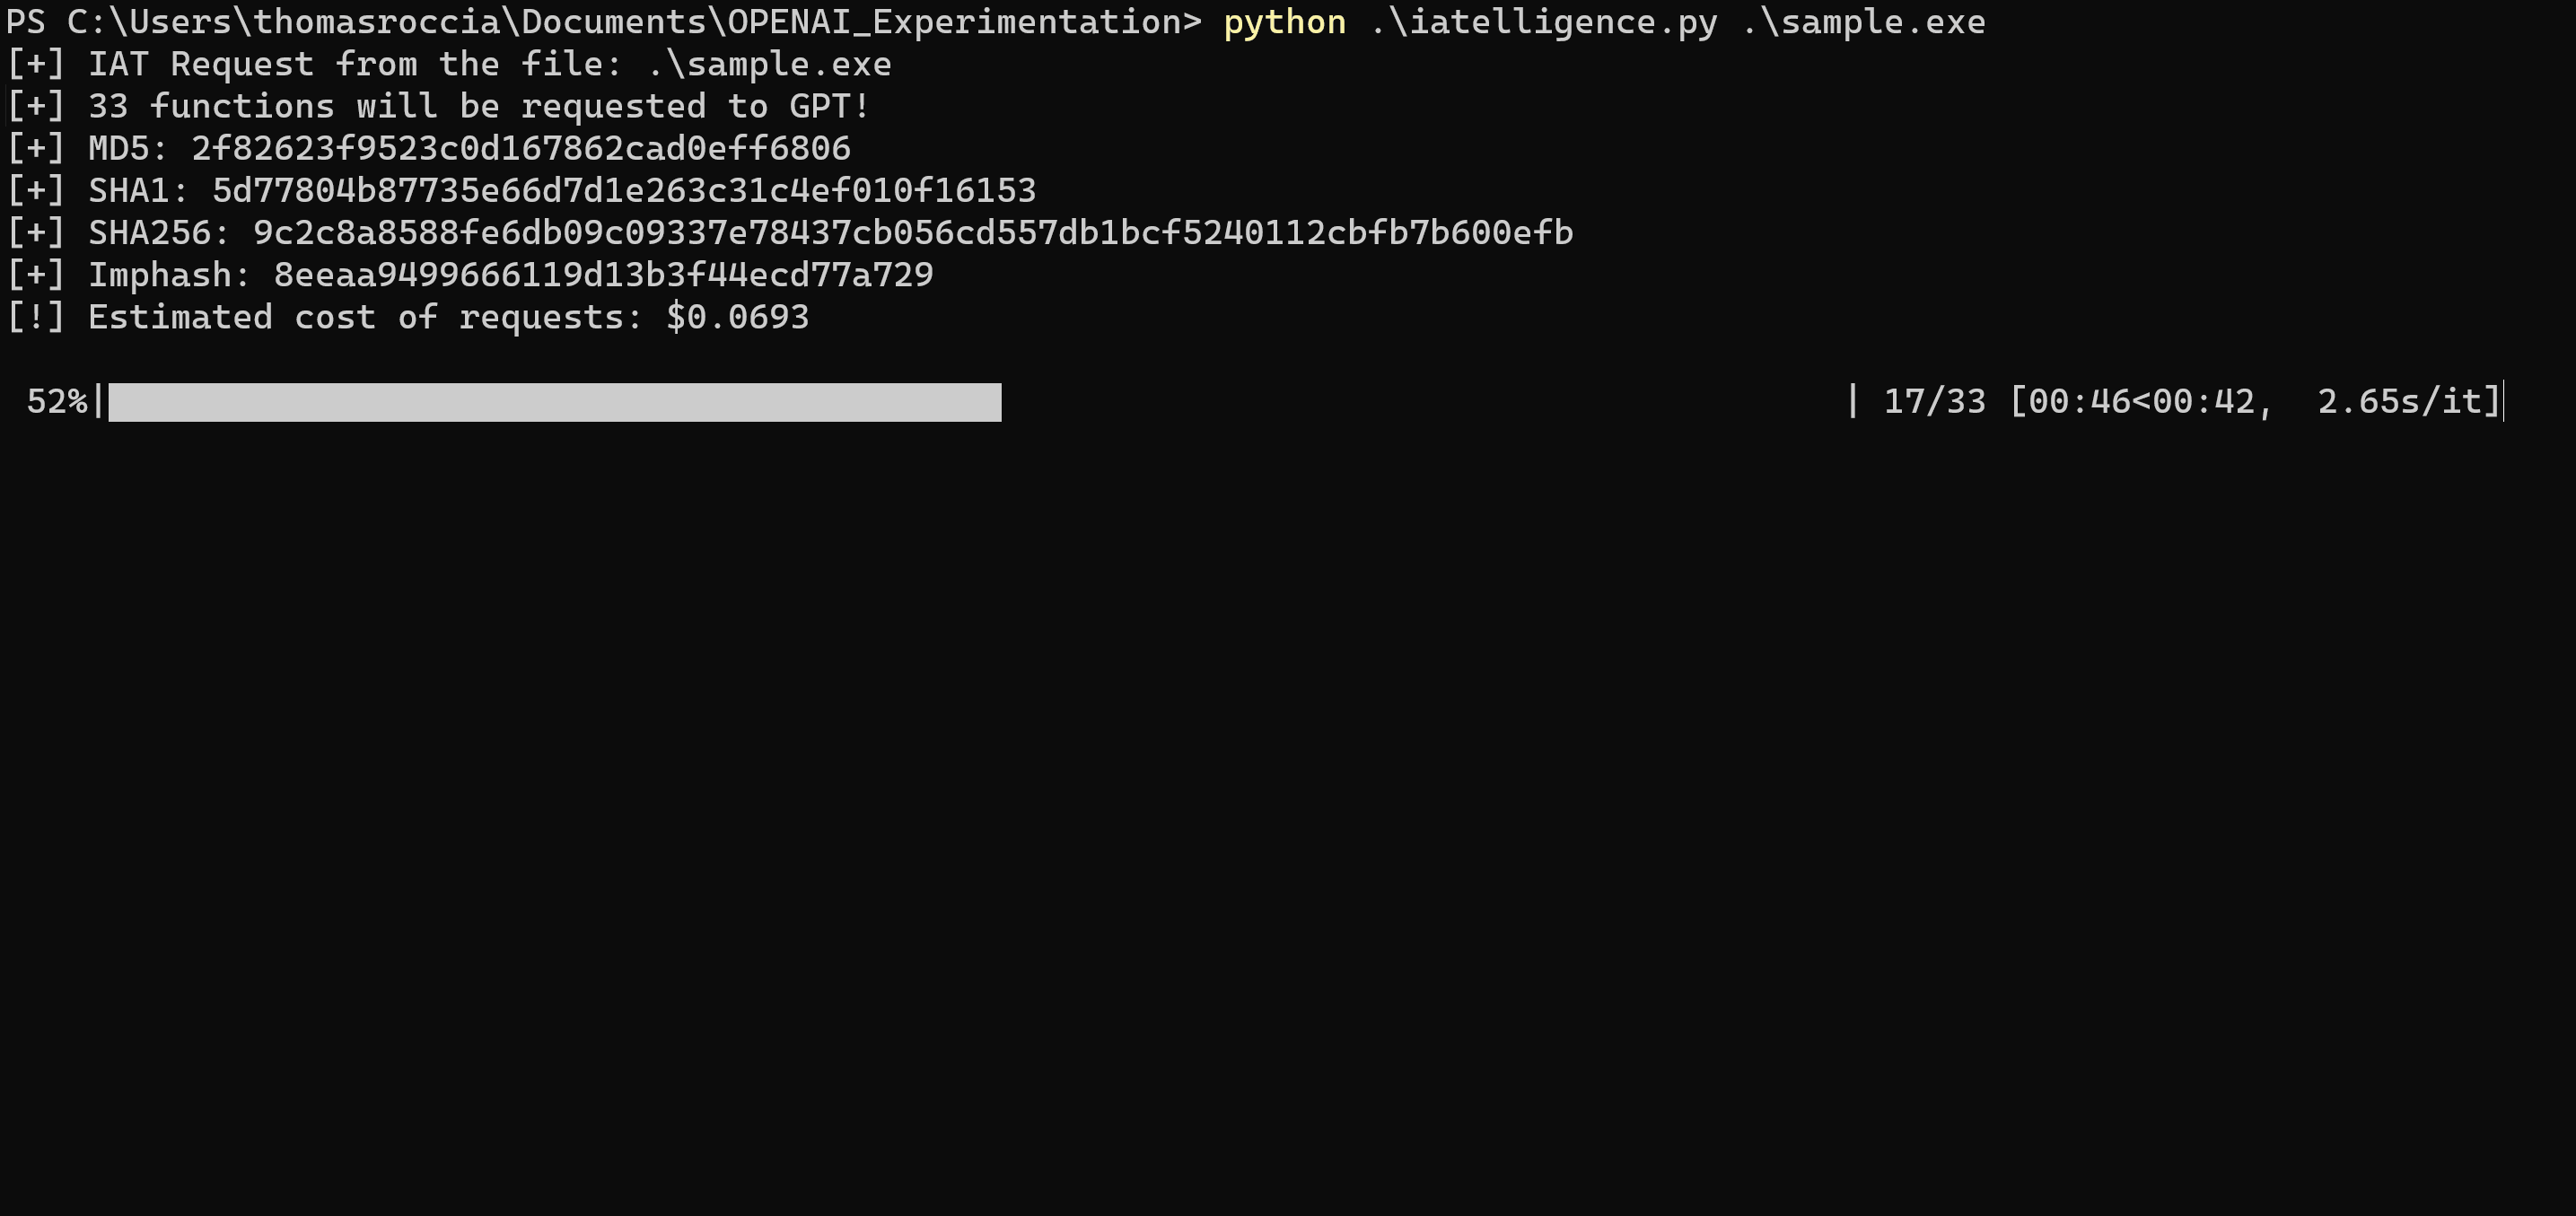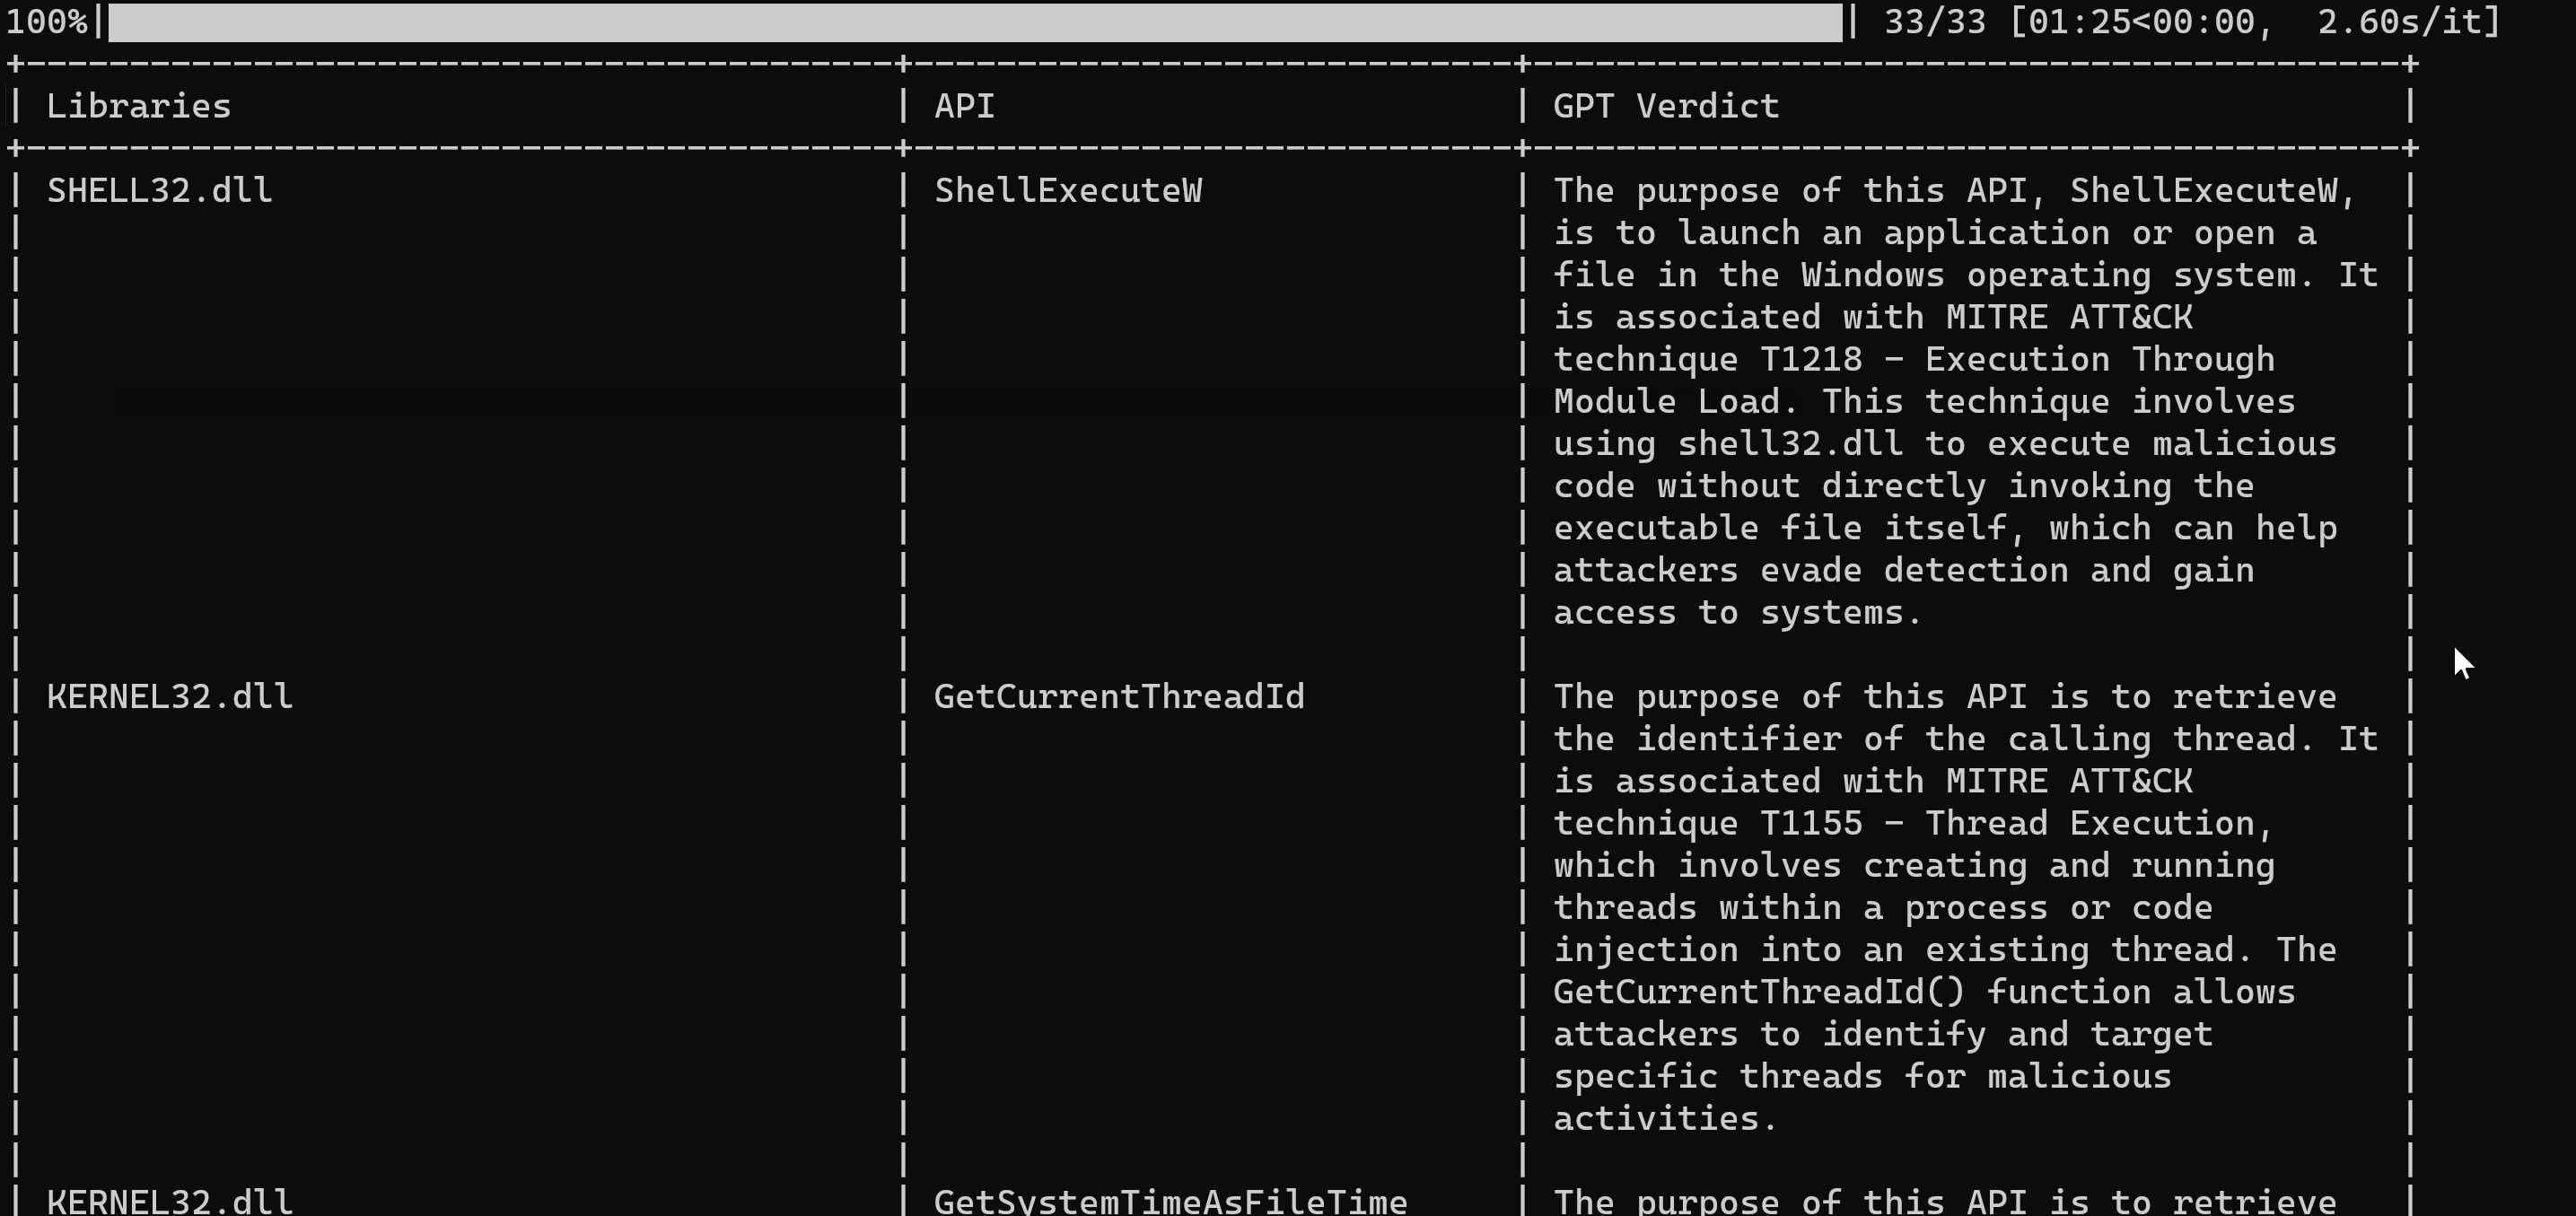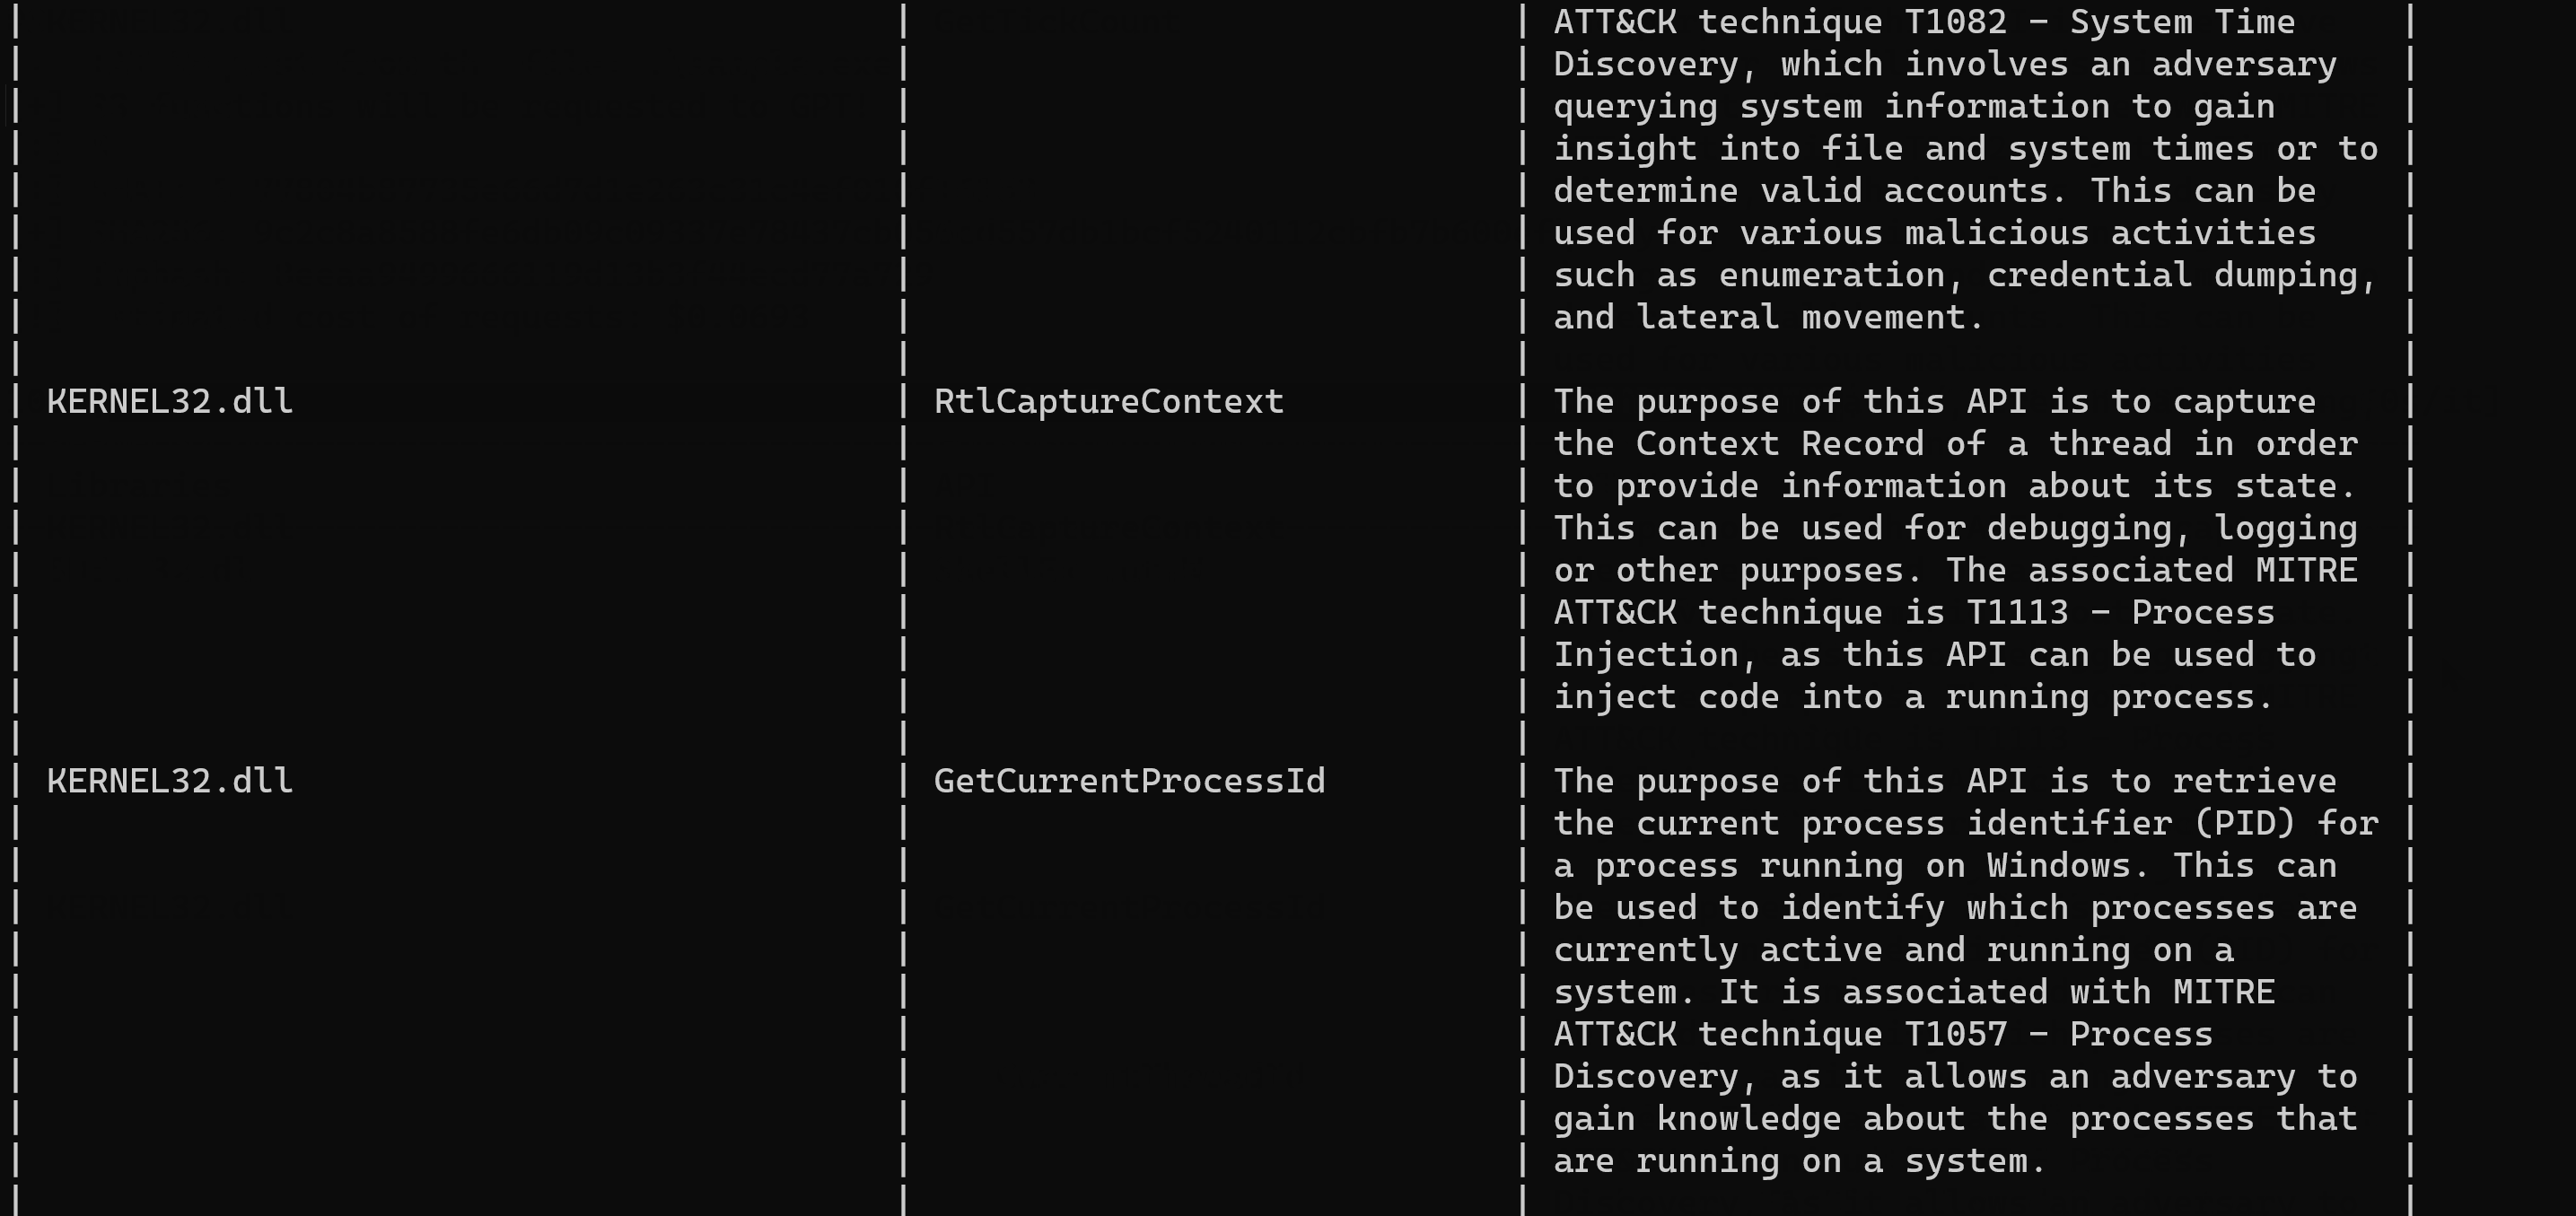 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
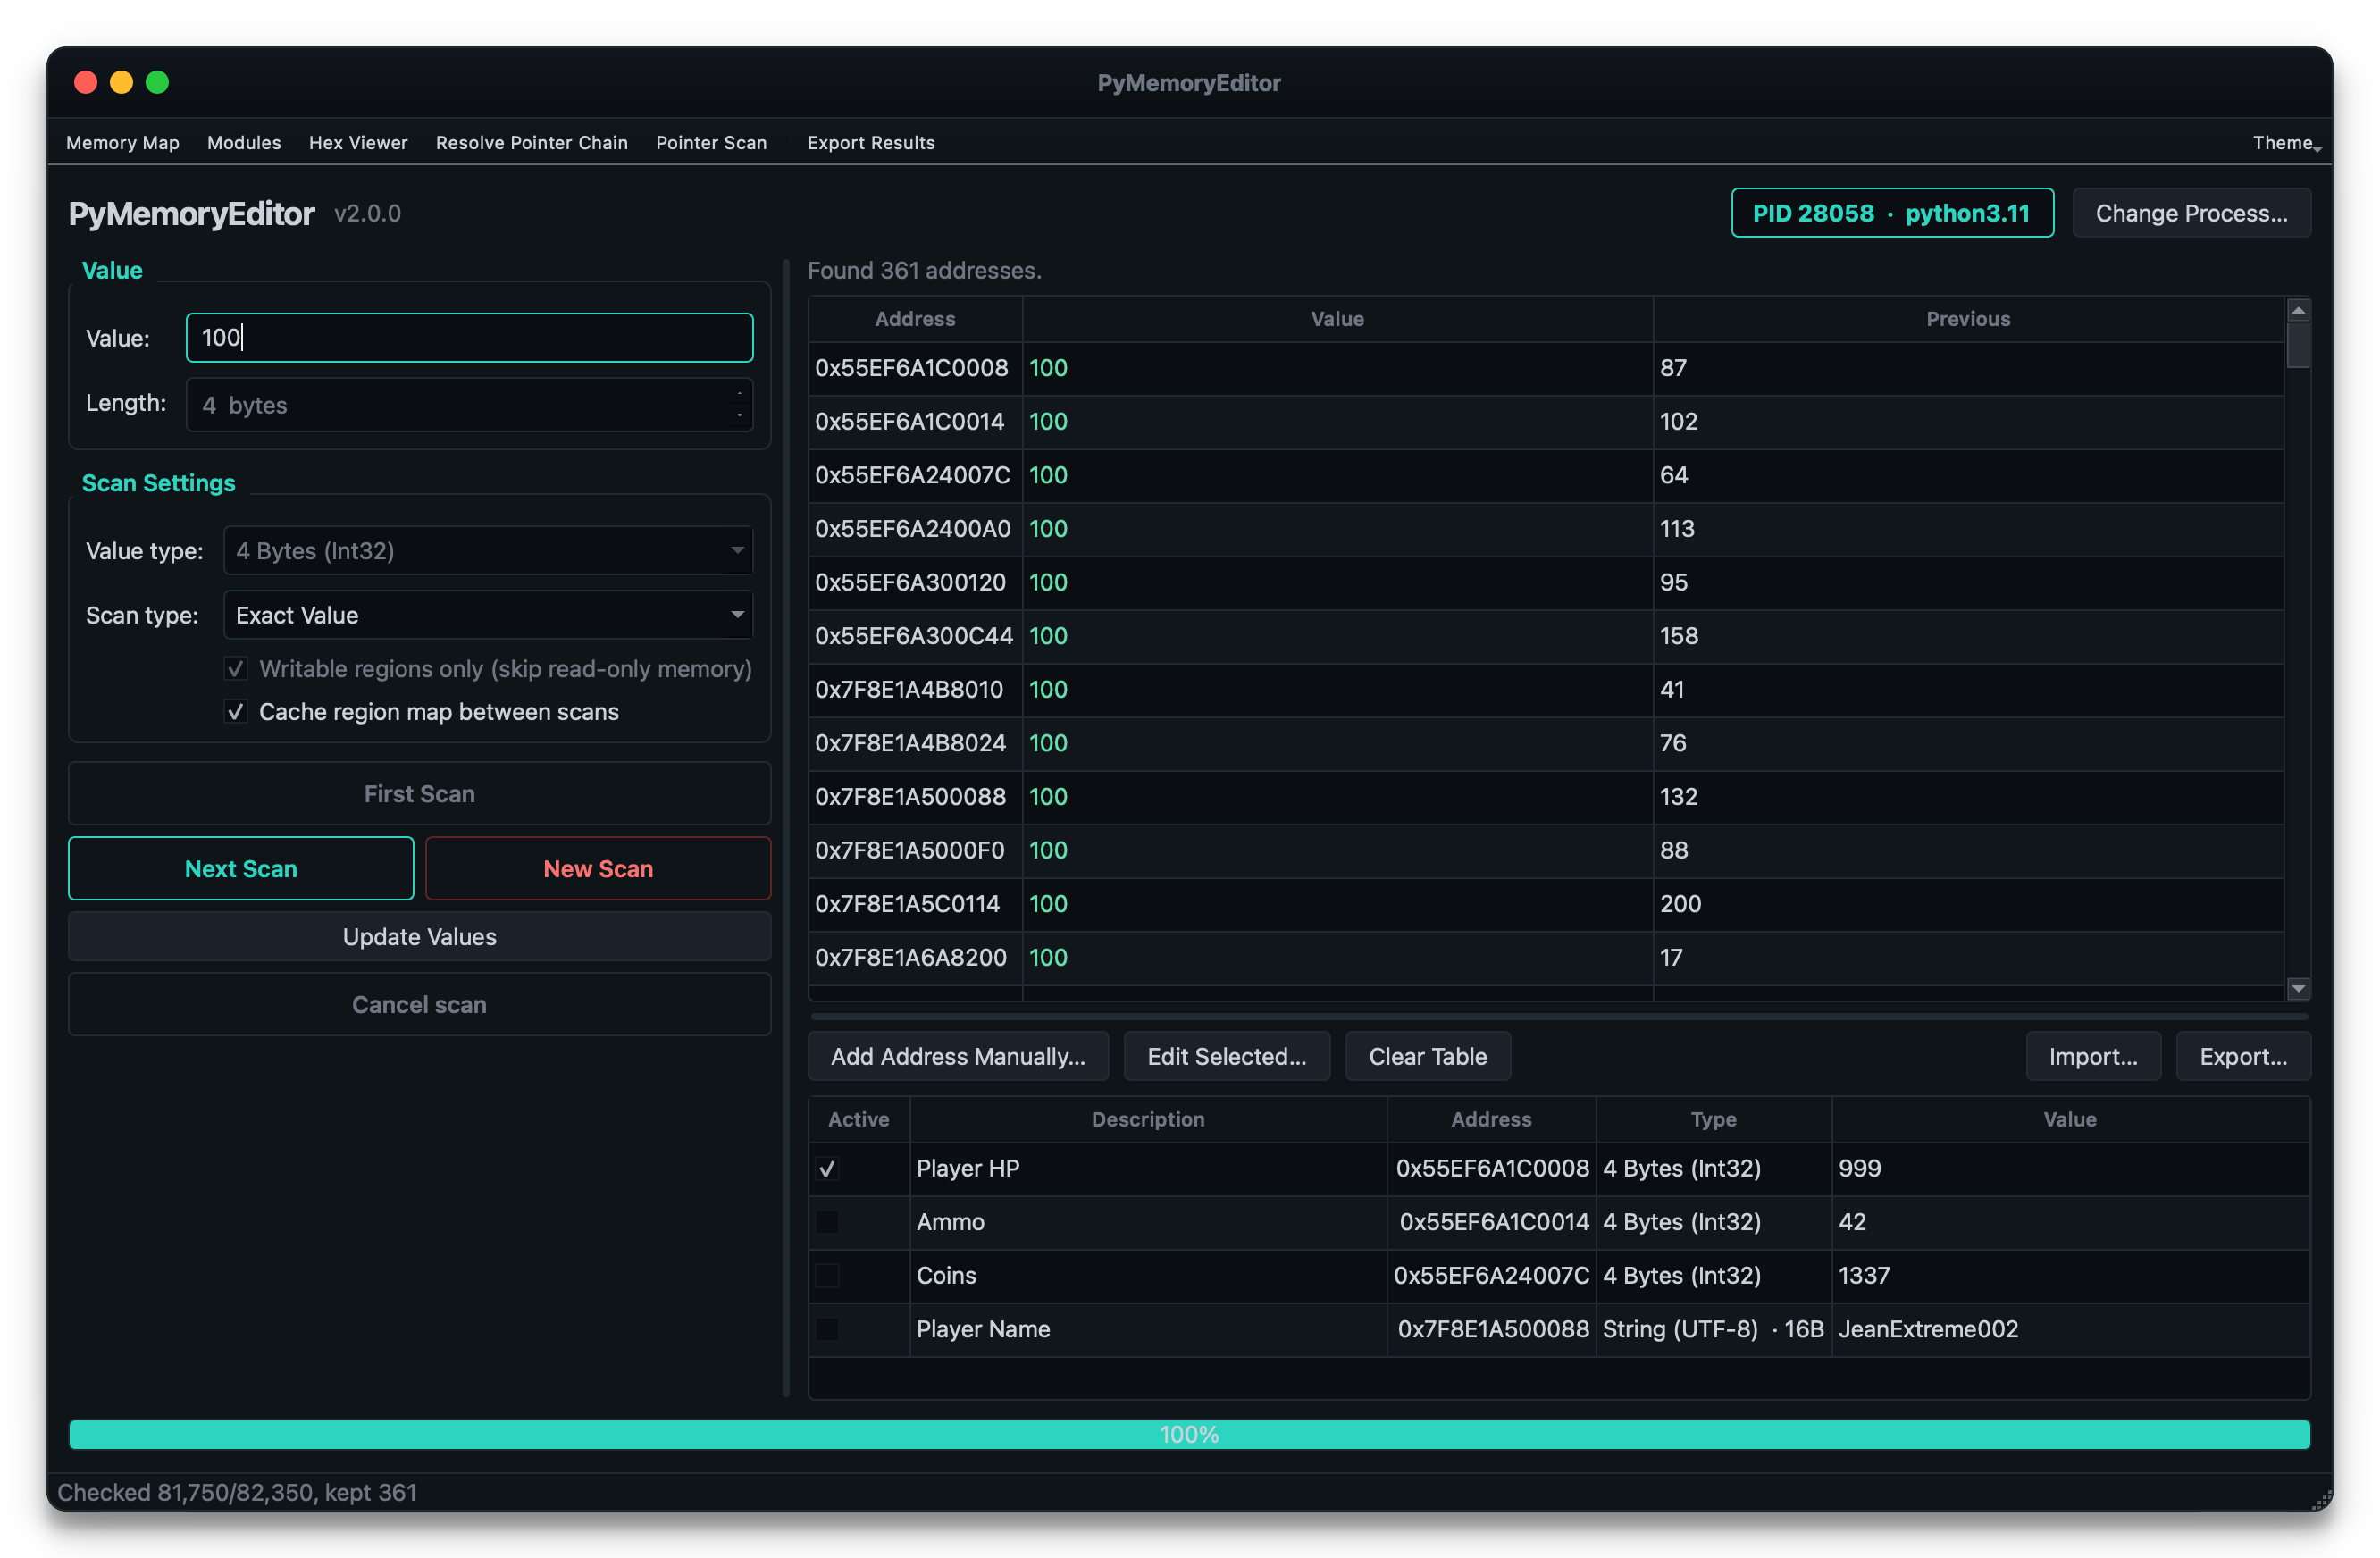 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 nteseyes/pylane
An python vm injector with debug tools, based on gdb.
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
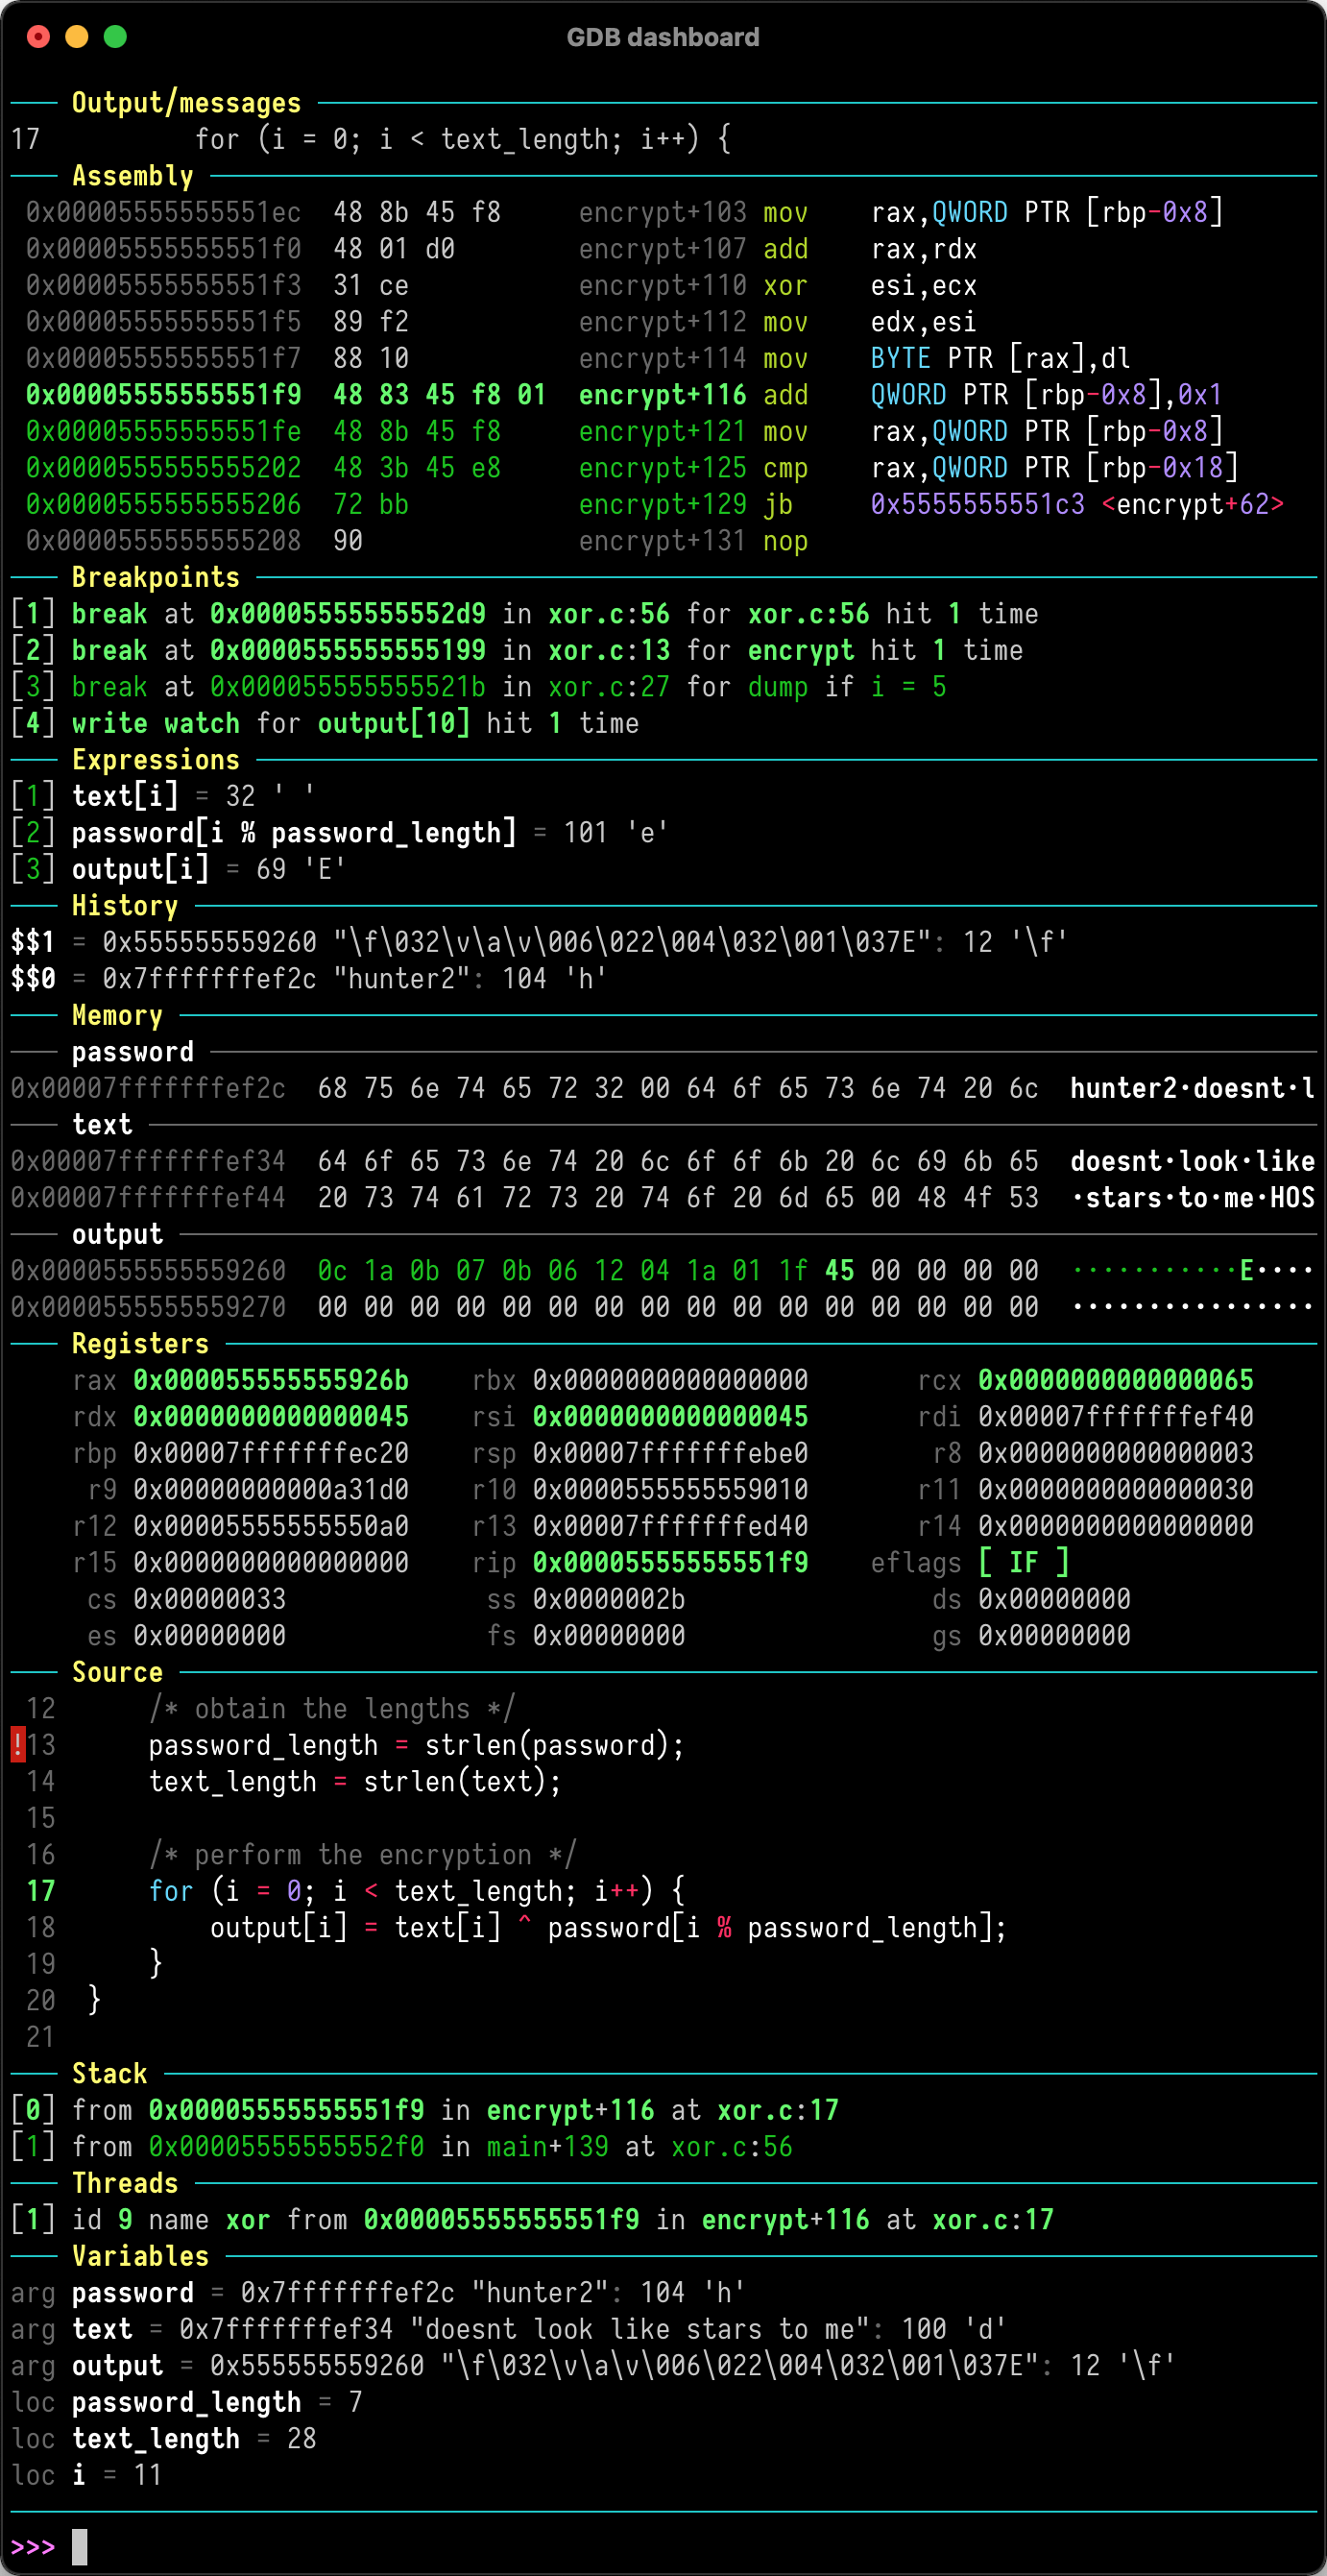 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…