
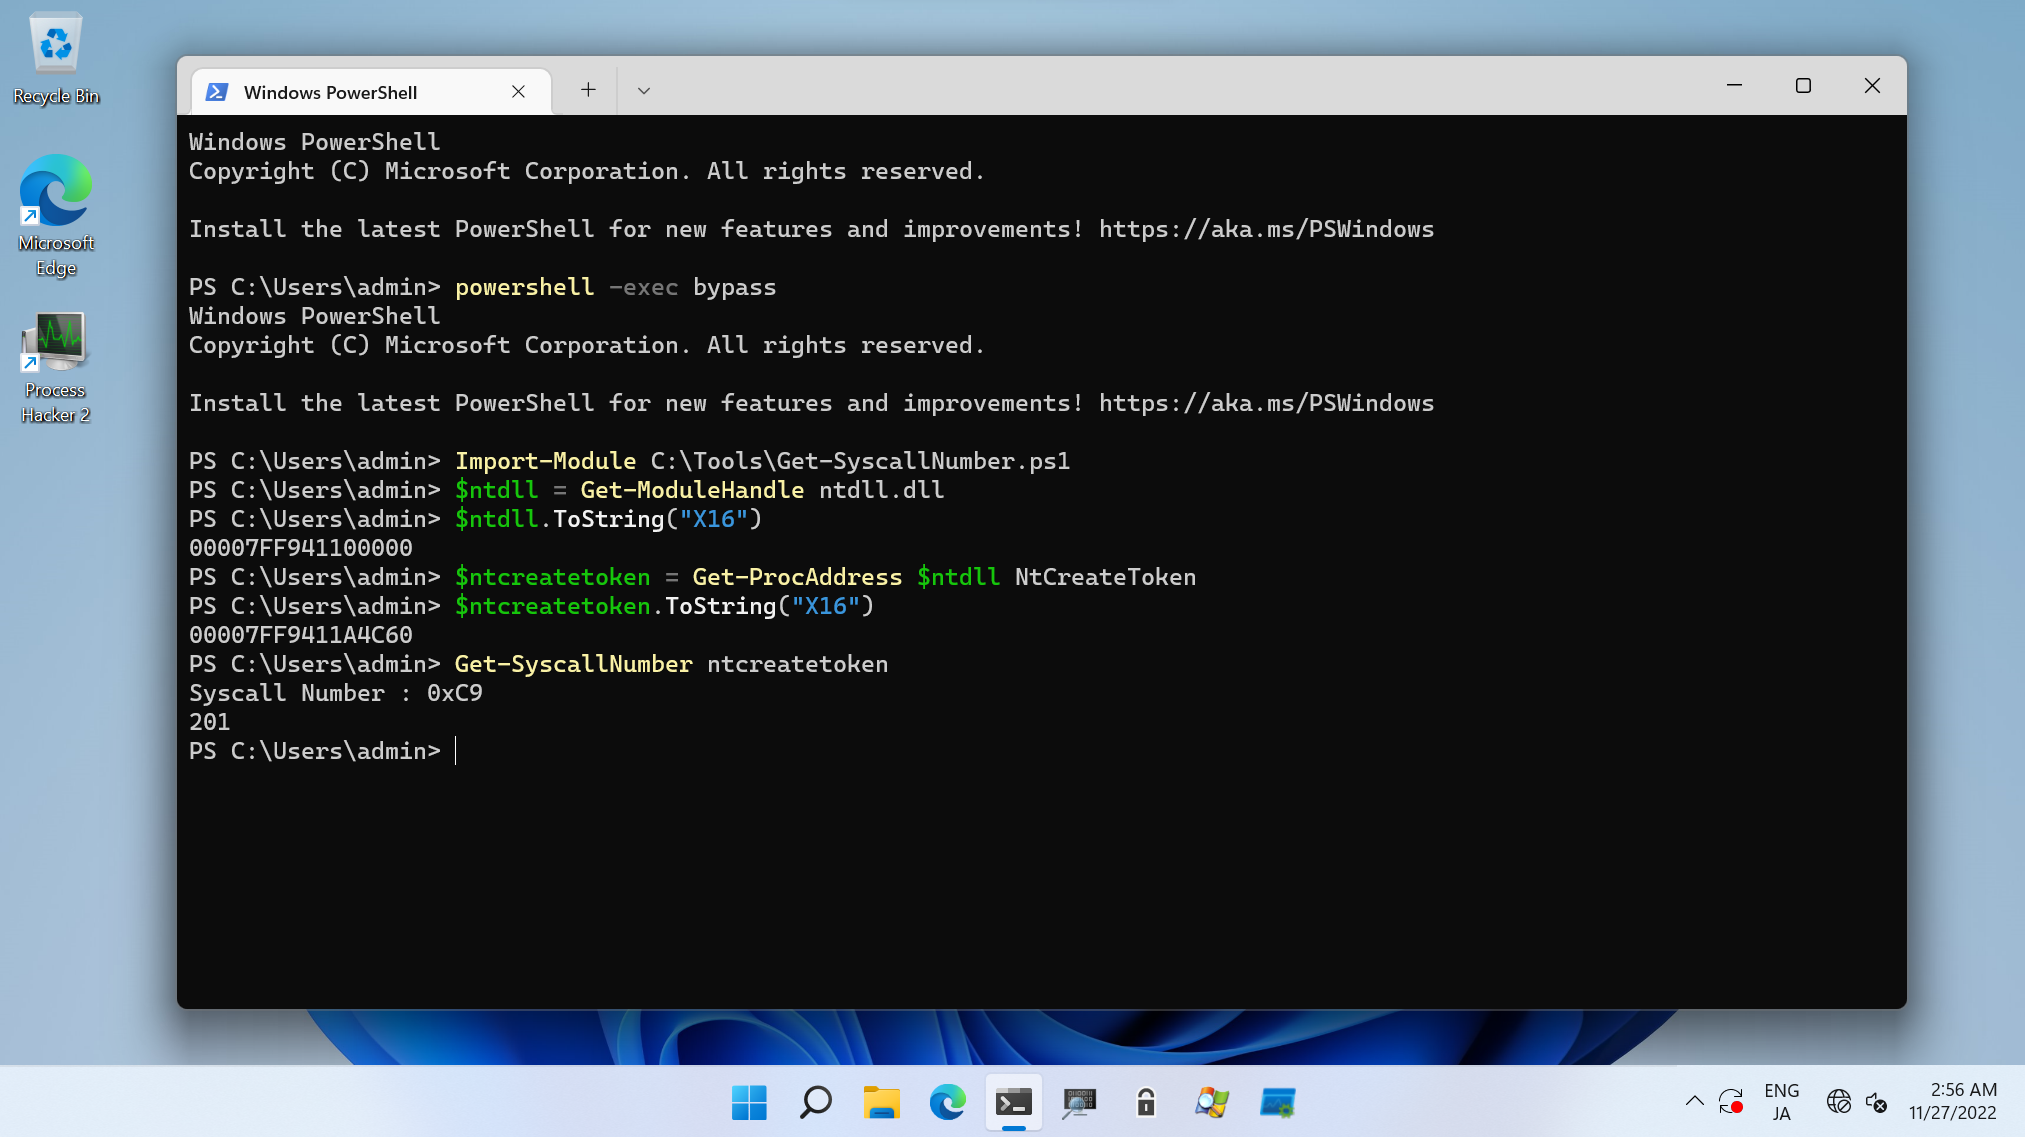
AtomicSyscall
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
adversarial-attackbinary-analysiseducation+3
daem0nc0re/atomicsyscallTools and PoCs for Windows syscall investigation.
 cyberclues/rtf_exploit_extractor
Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
 ylca0/idalib-cli
Agent-native CLI wrapping IDA Pro IDALib for stateless, JSON-output binary analysis: disassembly, Hex-Rays decompilation, CFG, xrefs, strings, and…
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 aliask/dinkleberry
Patch your D-Link device affected by CVE-2024-3272