
CVE-2026-64705
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
binary-analysiseducationexploitation+2
eddinos2/cve-2026-64705Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
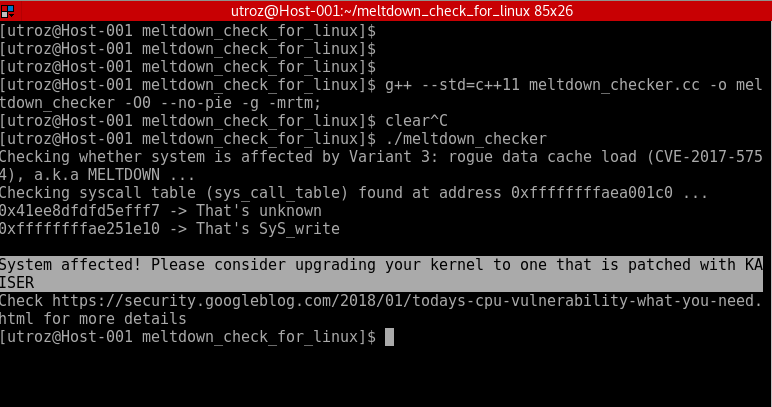 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
 hdm/juniper-cve-2015-7755
Notes, binaries, and related information from analysis of the CVE-2015-7755 & CVE-2015-7756 issues within Juniper ScreenOS
 qax-a-team/cve-2018-20250
010 Editor template for ACE archive format & CVE-2018-2025[0-3]
 0xjohnnydev/webkit-navigationapi-sop-bypass
WebKit NavigateEvent.canIntercept SOP bypass via cross-port interception — iOS 26.3.1 BSI (CVE-2026-20643)
 cyberclues/rtf_exploit_extractor
Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
 xingchenrs/cybermeowfians
The next stage of CyberMeowfil (CVE-2026-43499 and 43074),Possibly biased toward vivo devices?
 0x0oz/cve-2026-7482-poc
Proof-of-concept exploit for CVE-2026-7482, an unauthenticated heap out-of-bounds read in Ollama's GGUF loader, demonstrating memory exfiltration via…
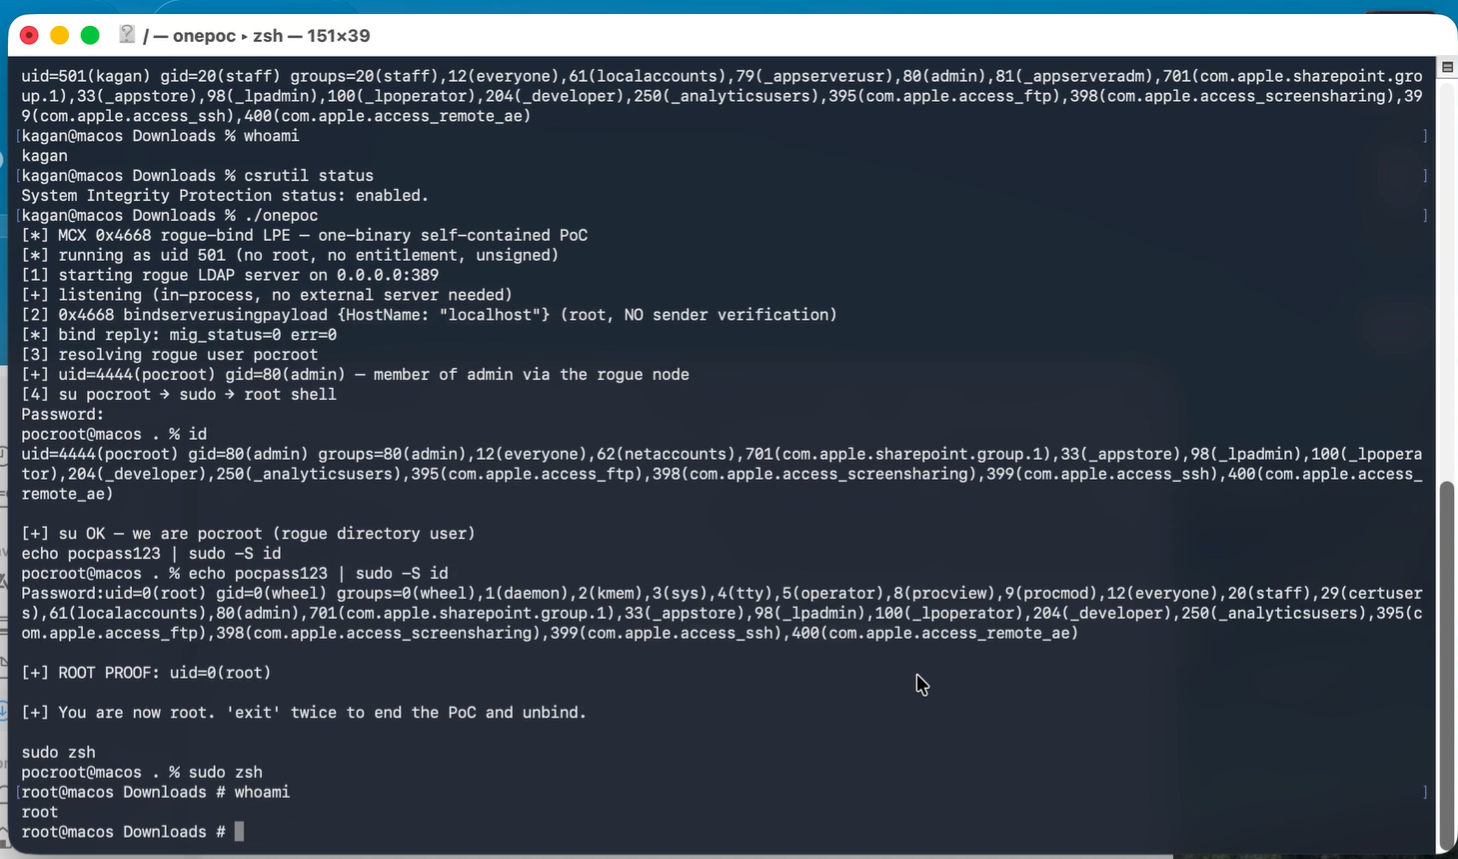 0xblackash/cve-2026-43786
Documentation and research notes for CVE-2026-43786, a macOS local privilege-escalation flaw caused by improper entitlement validation, covering root…
 virus-or-not/cve-2026-32202
Generates LNK files with crafted _IDCONTROLW structures to research Windows Shell spoofing vulnerabilities CVE-2026-21510 and CVE-2026-32202,…
 jvidhan/cve-2026-28912
Reverse engineering notes and a working PoC for the macOS PackageKit symlink-following bug (CVE-2026-28912), with disassembly diff of the 26.6 fix.
 007bsd/ml-kem-key-recovery
Full ML-KEM-1024 key recovery from a partial Fujisaki-Okamoto comparison in wolfSSL (CVE-2026-6330 NEON, CVE-2026-10097 AVX2)
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
 danish1162/cve-2026-2035703-x300
Tozed ZLT X300 5G CPE — Remote Root Code Execution via SDR Rogue Base Station (CVE-2026-2035703, CWE-78, CVSS 9.8) — Coordinated Disclosure
 hexrom/imagemagick-cve-2017-15277
Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.