
windiff
 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
392
ergrelet/windiffTool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 waleedassar/cve-2021-1656
Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…
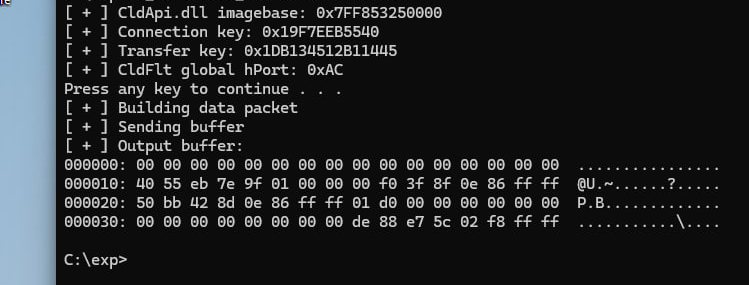 crackercat/cve-2024-26160
cldflt.sys information disclosure vulnerability (KB5034765 - KB5035853, Win 11).
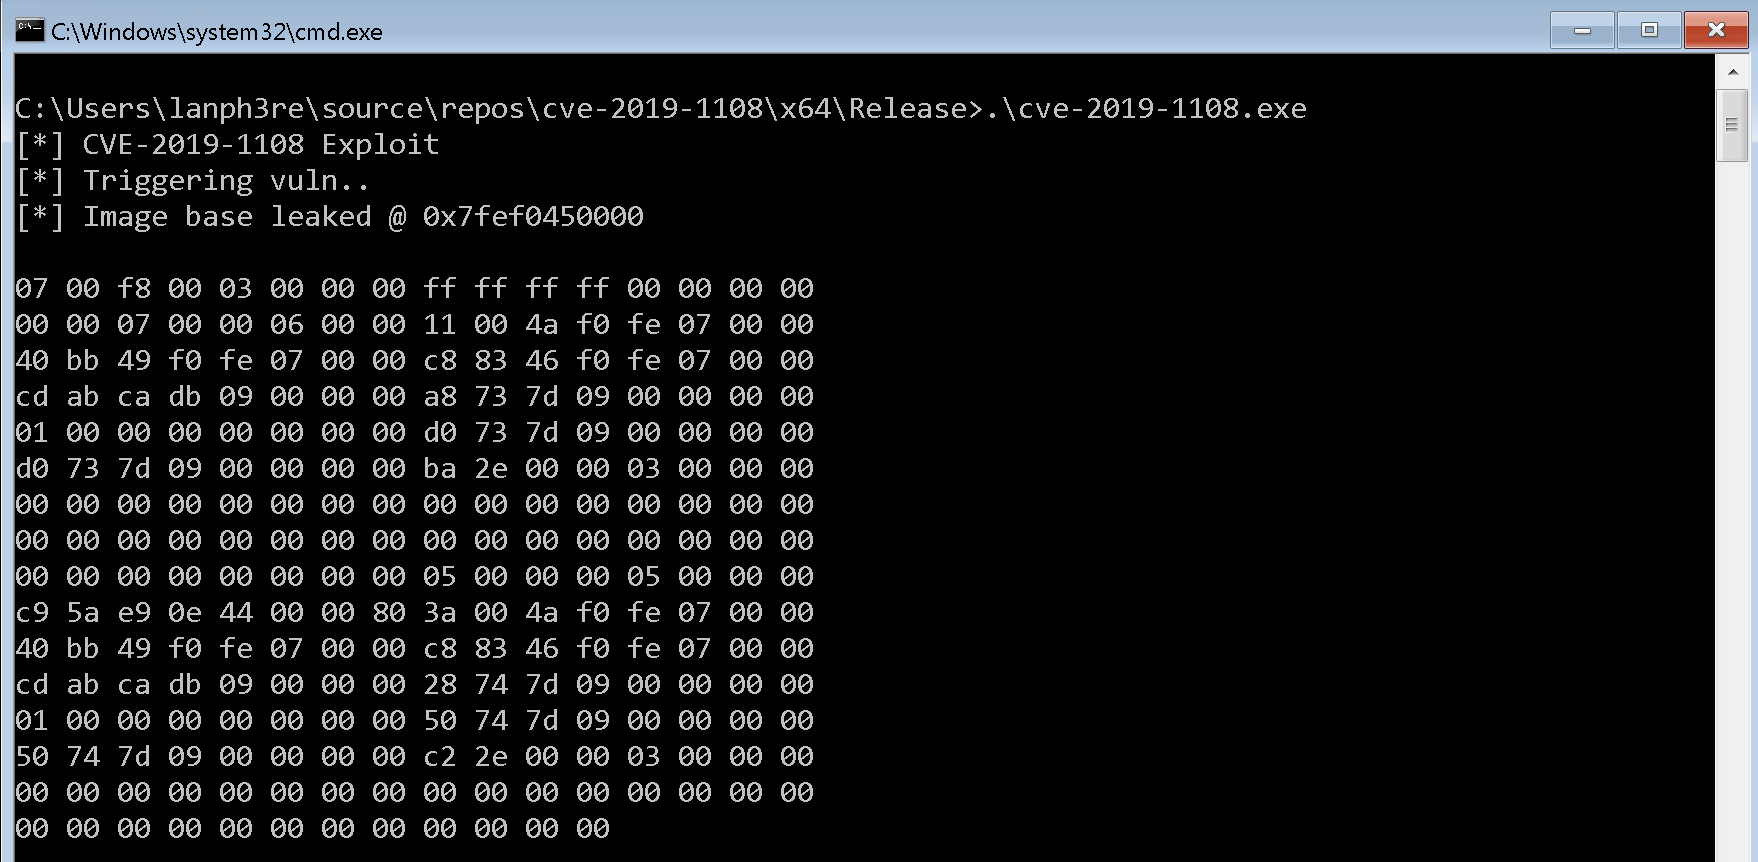 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 sandi-go/ps-2017-13---cve-2018-9950
Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…
 sandi-go/cve-2018-15968
Technical disclosure of CVE-2018-15968: an out-of-bounds read vulnerability in Adobe Reader's PDF parsing, enabling information disclosure and…
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
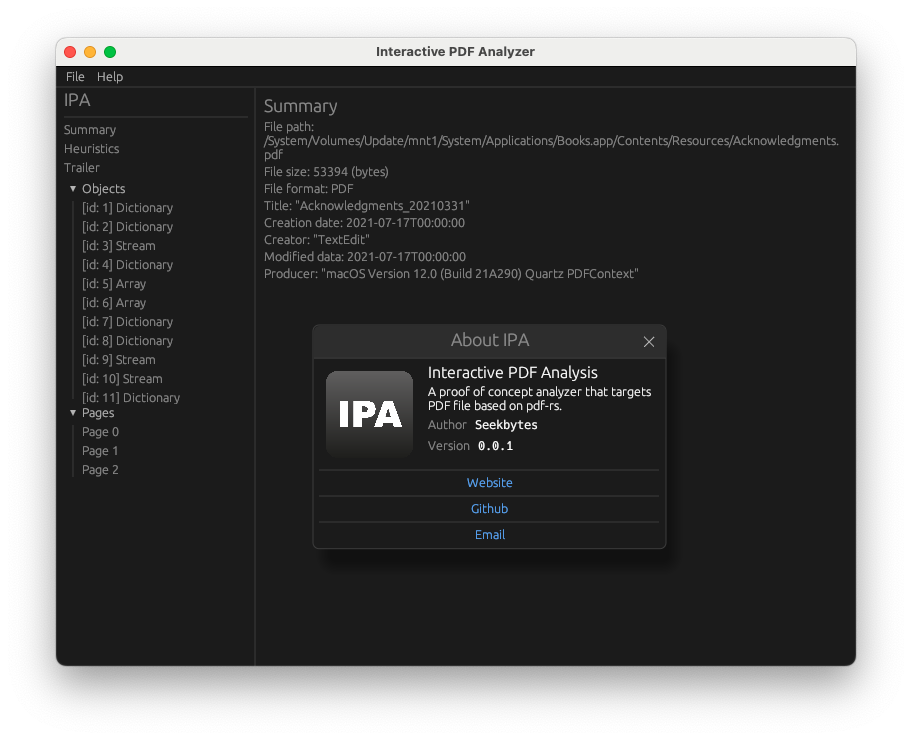 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
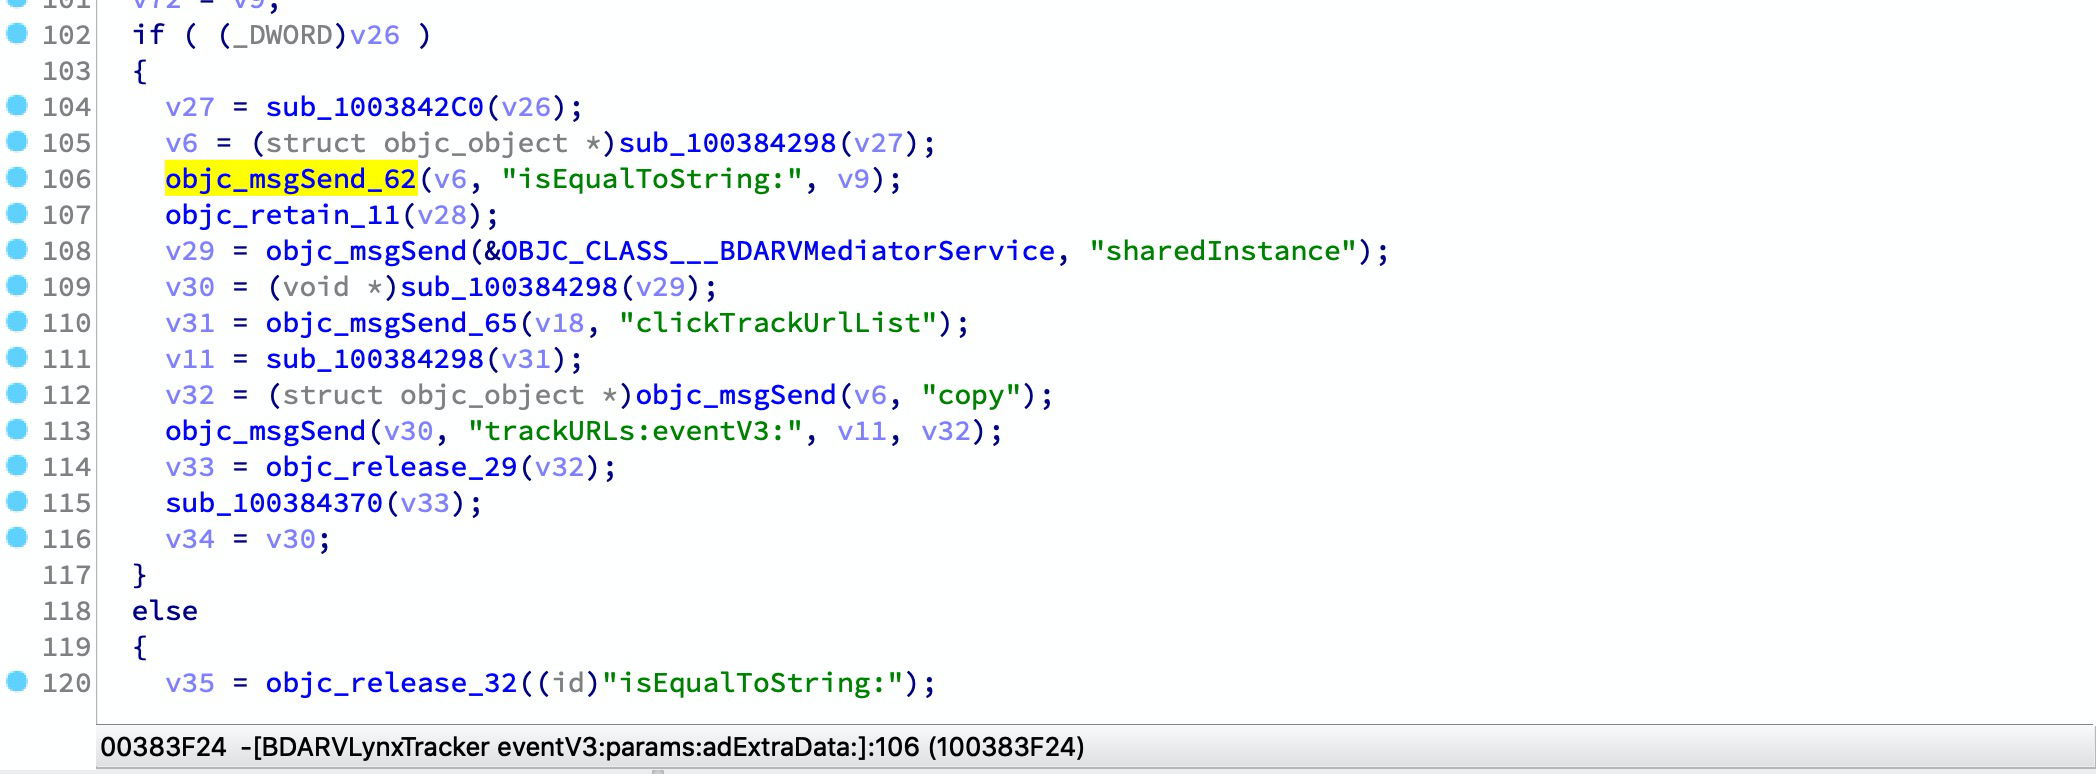 soulghost/iblessing
iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
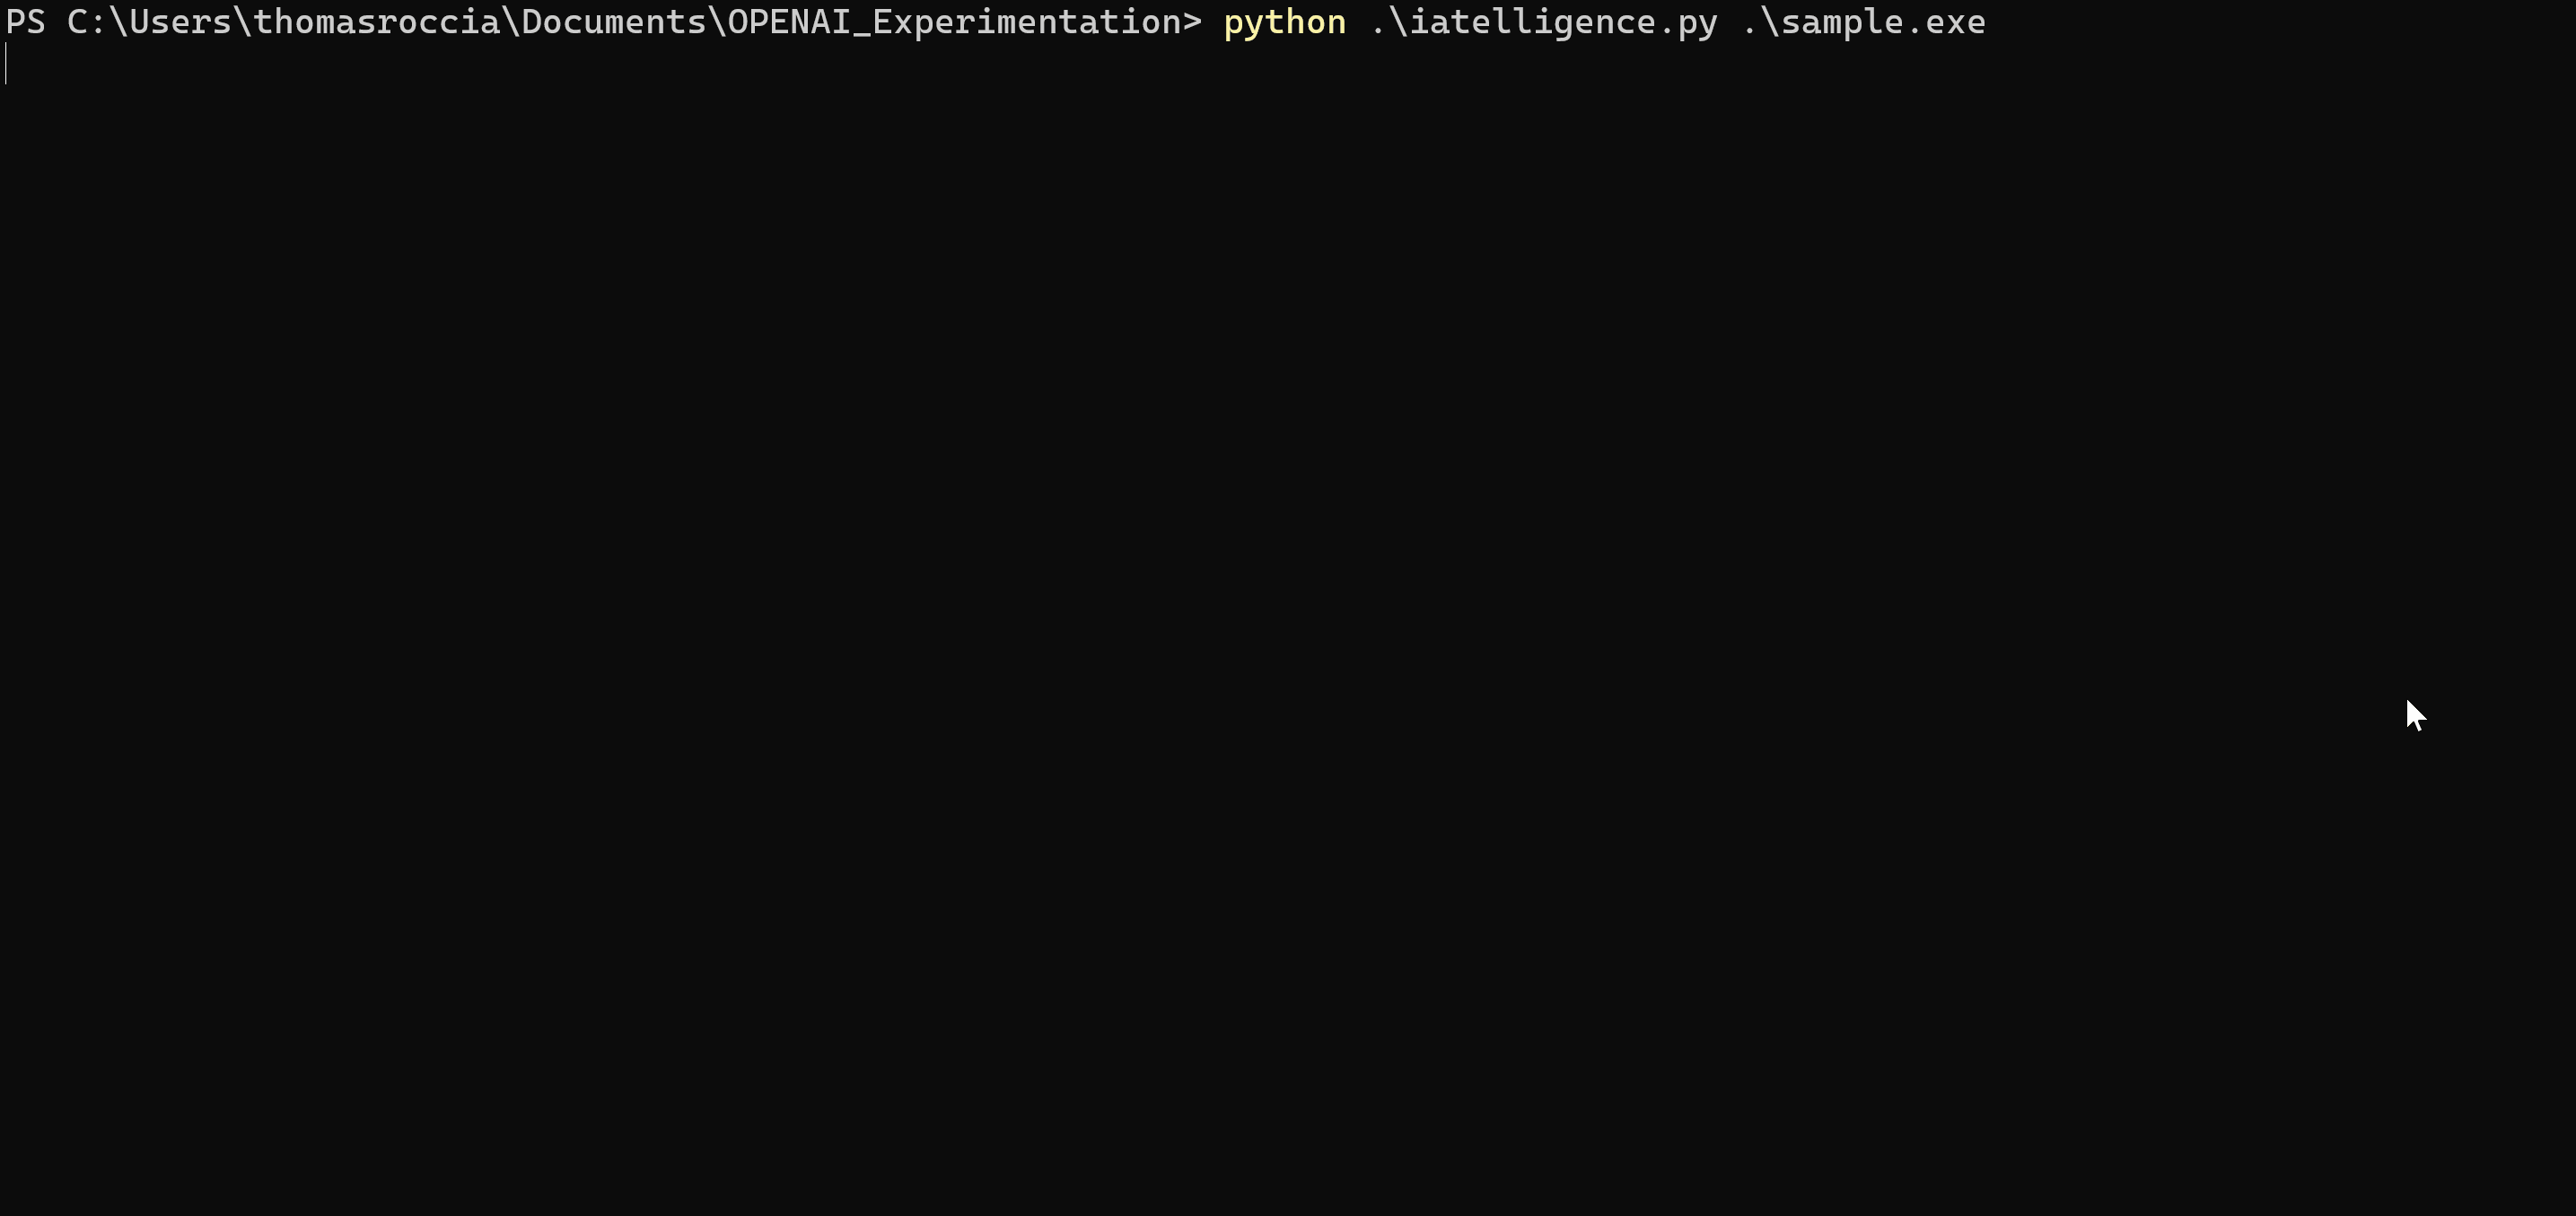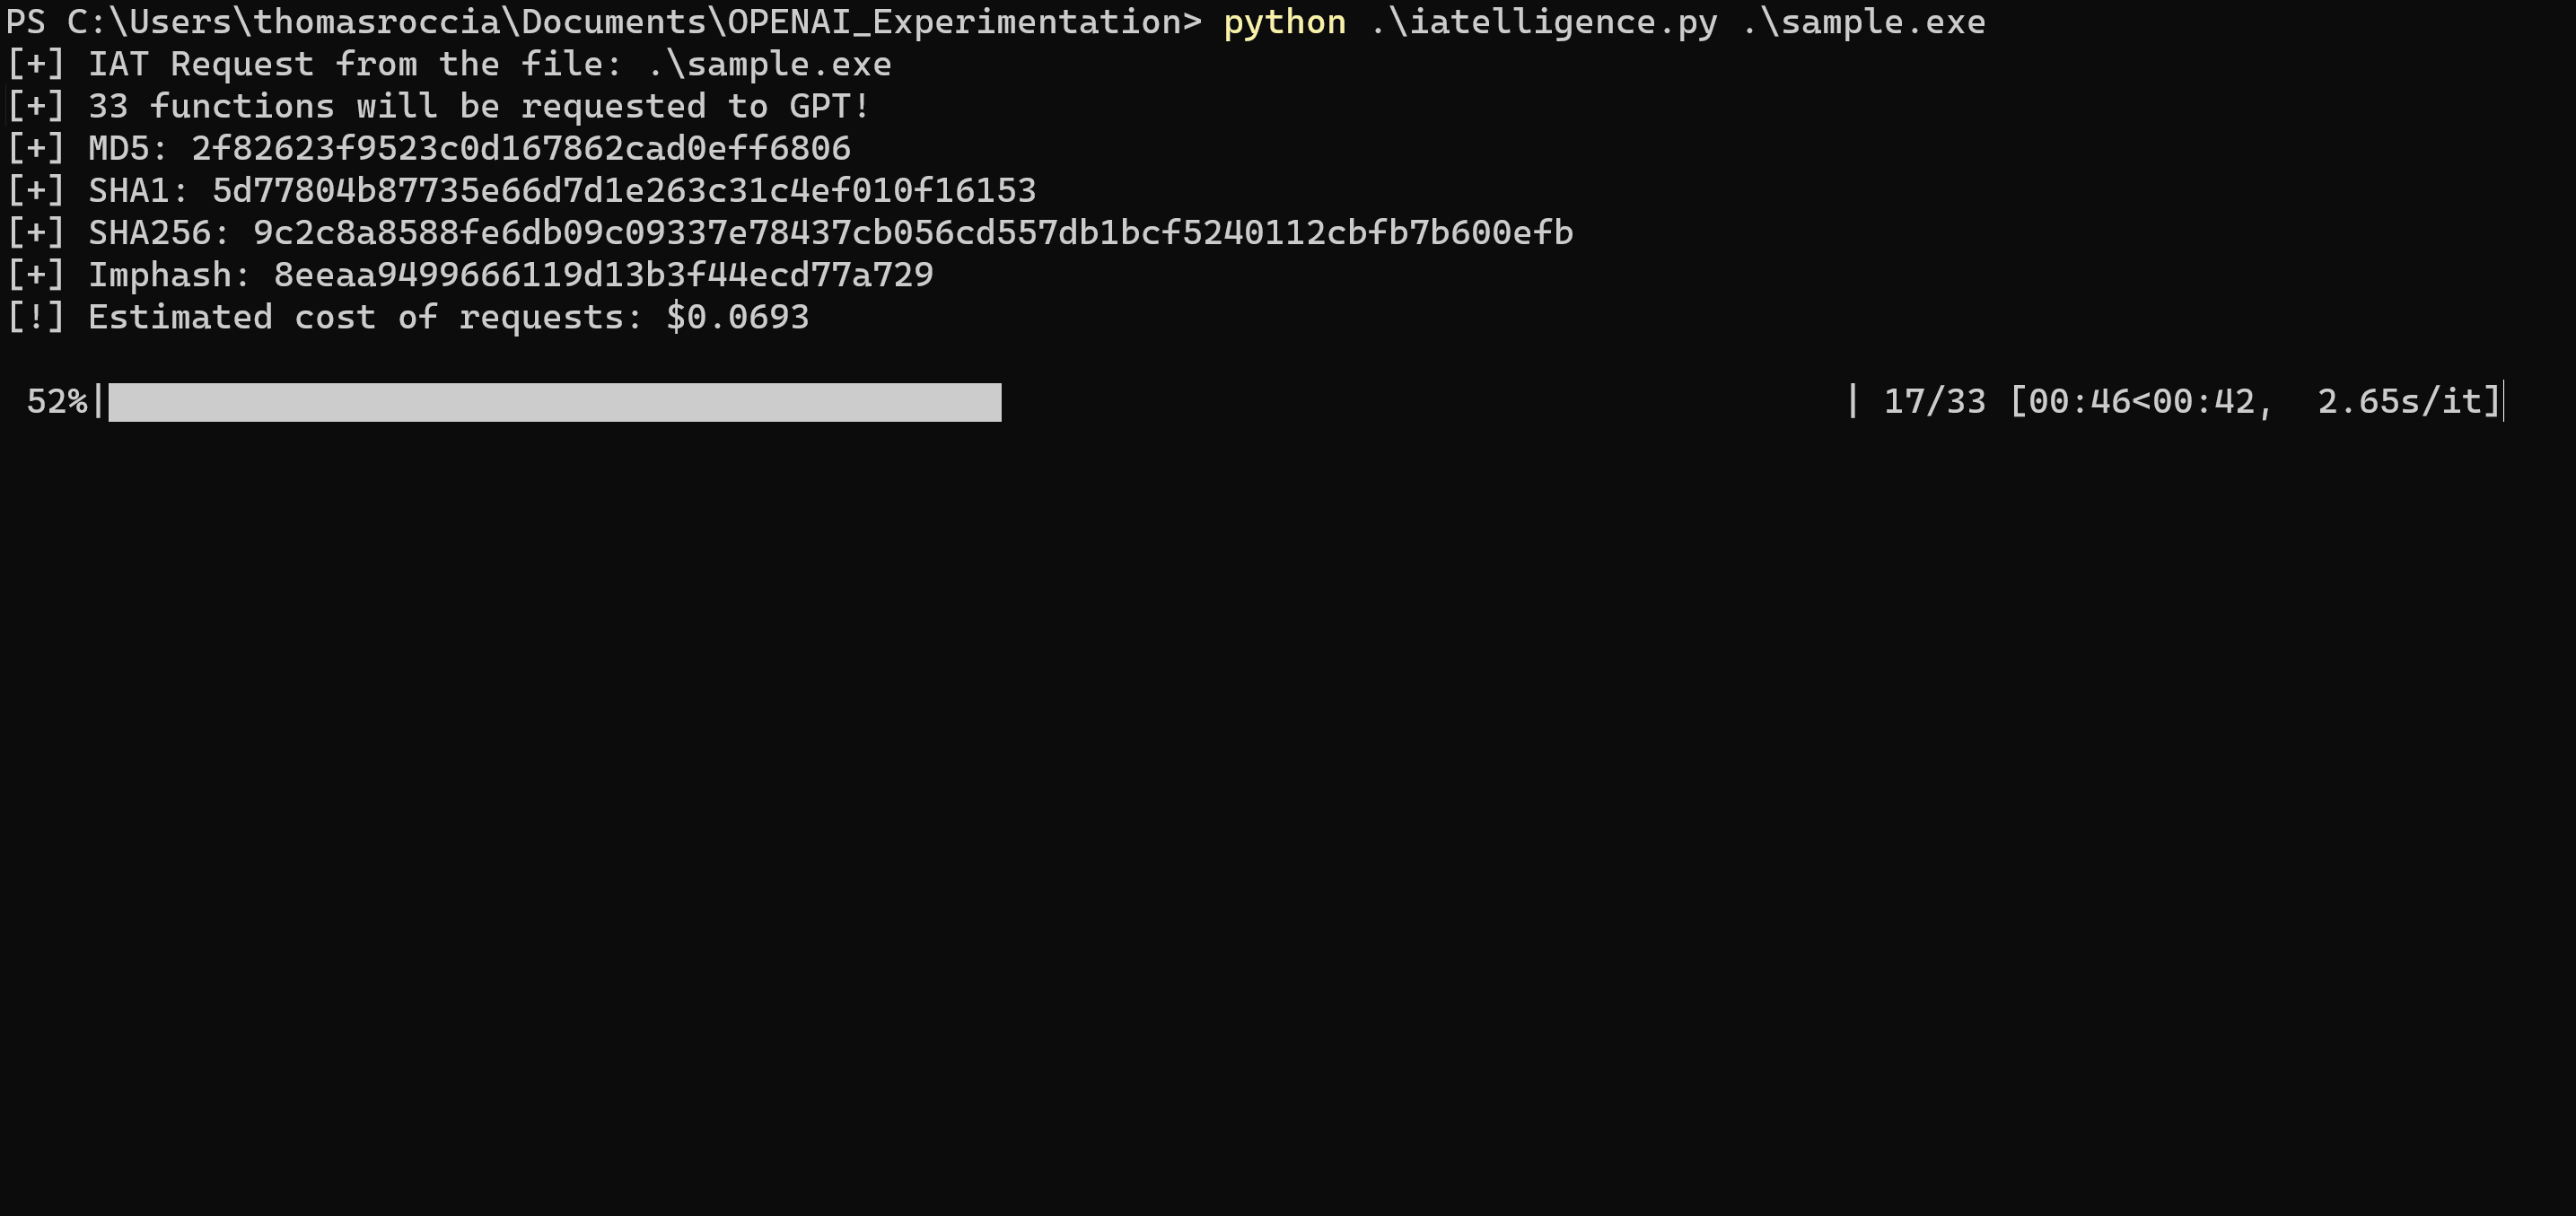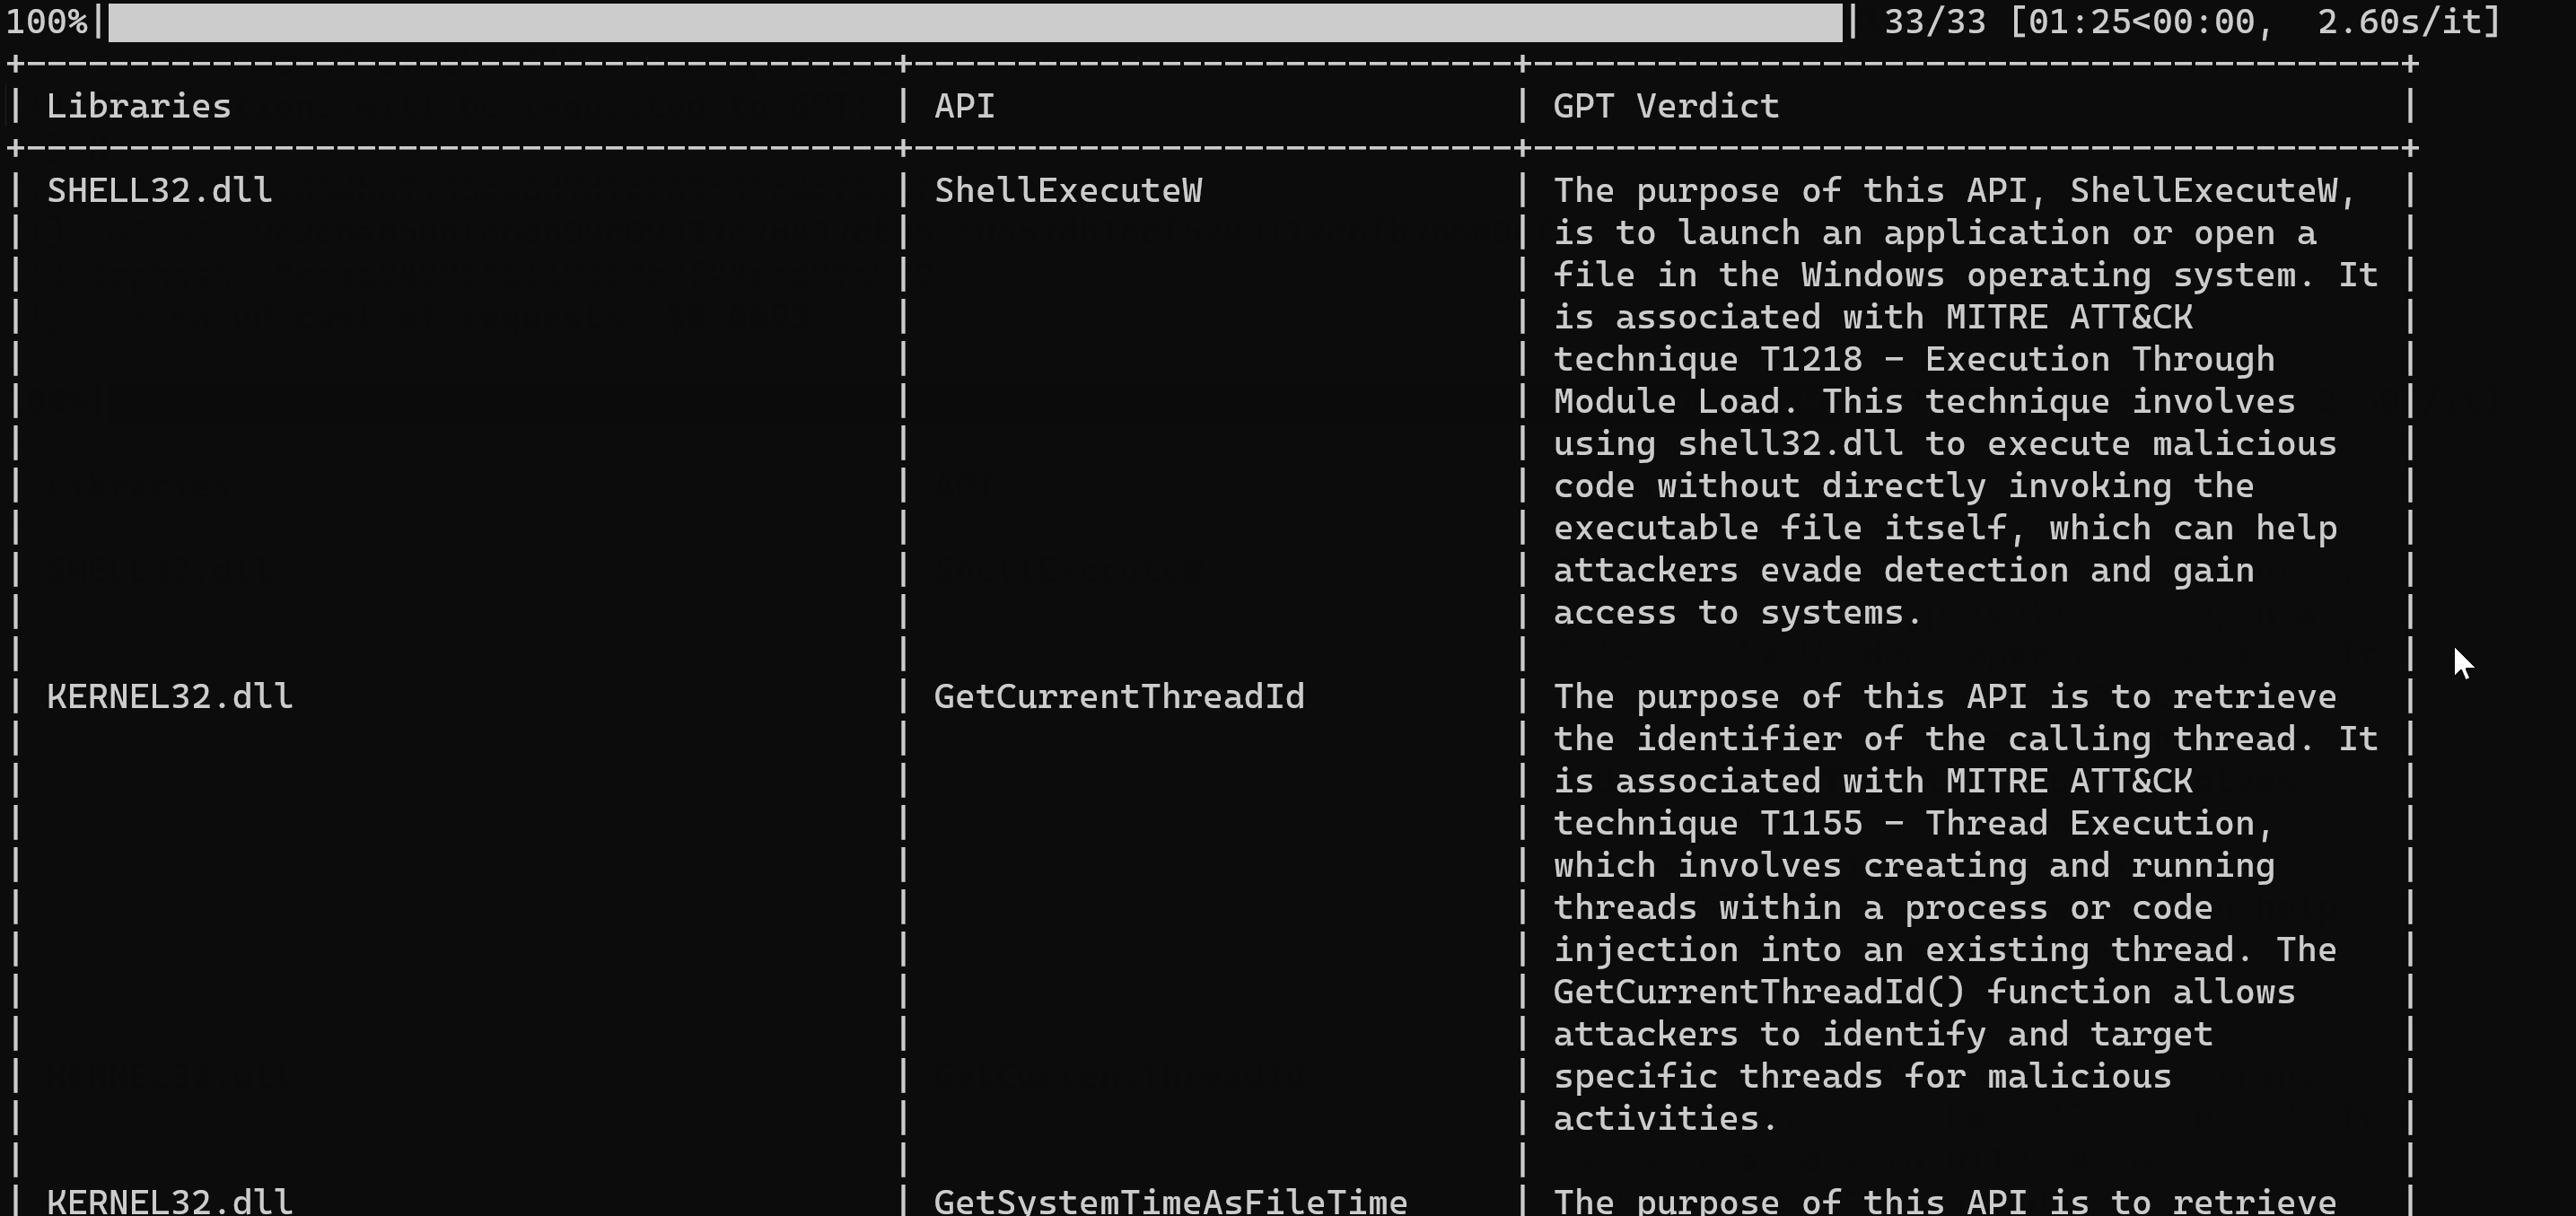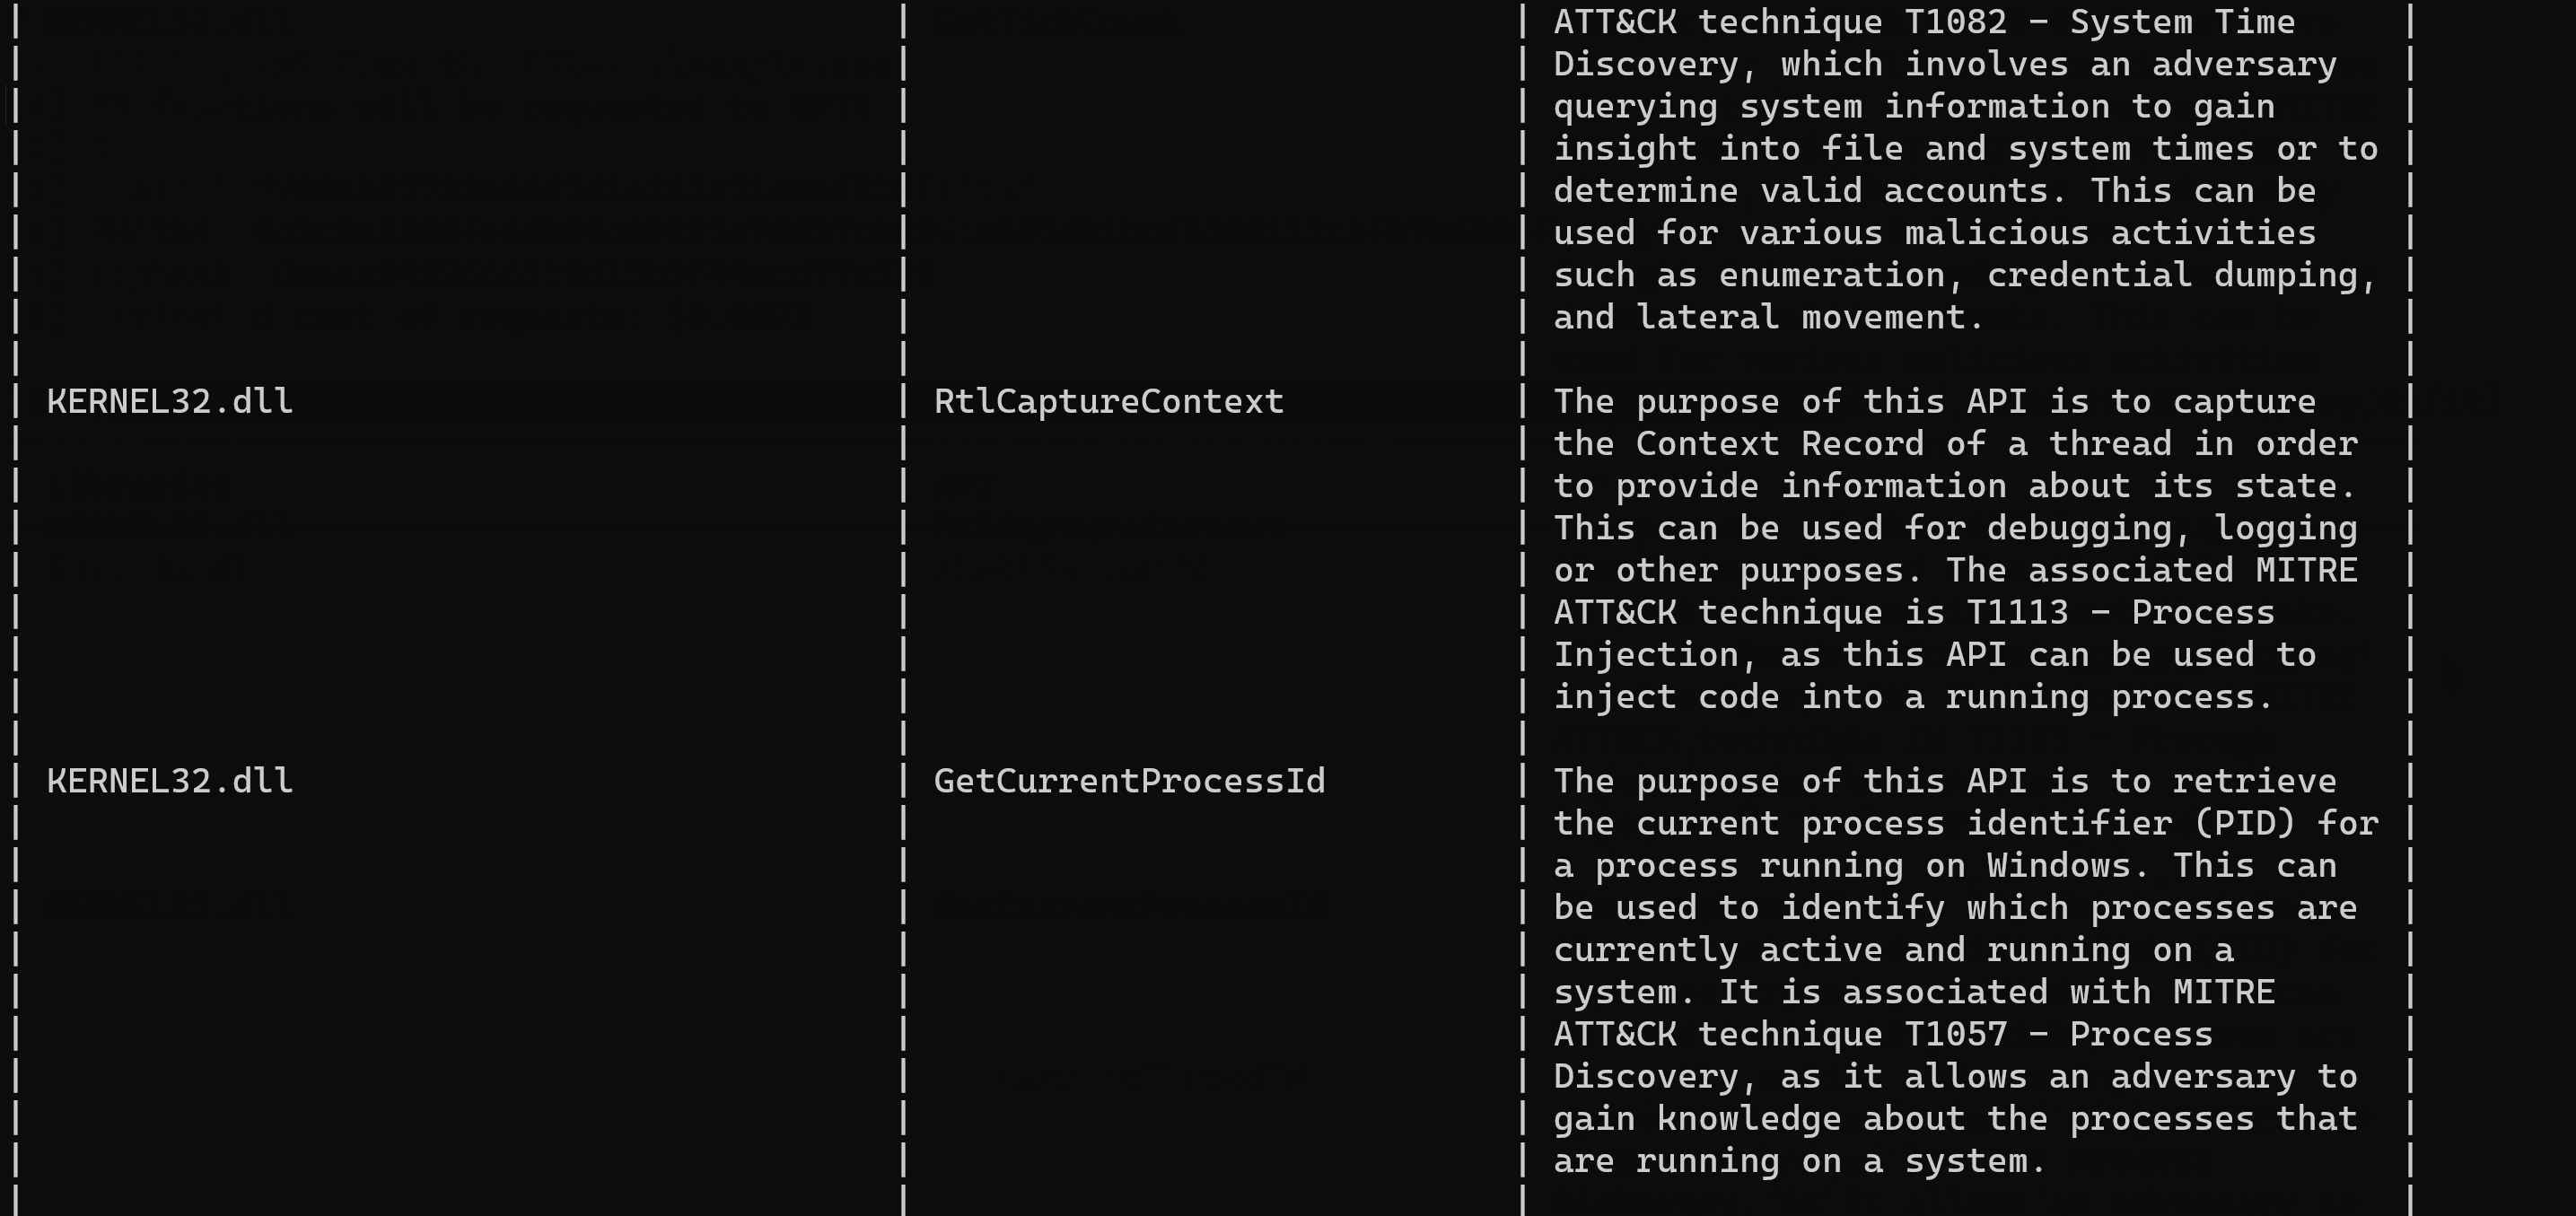 fr0gger/iatelligence
IATelligence is a Python script that will extract the IAT of a PE file and request GPT to get more information about the API and the ATT&CK matrix…
 hdm/juniper-cve-2015-7755
Notes, binaries, and related information from analysis of the CVE-2015-7755 & CVE-2015-7756 issues within Juniper ScreenOS
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 liamg/extrude
:detective: Analyse binaries for missing security features, information disclosure and more...
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
 gmh5225/driver-soulextraction
SoulExtraction is a windows driver library for extracting cert information in windows drivers