ecdsa-private-key-recovery

Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…

Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…

Ghidra-based tool for detecting and analyzing the Log4j vulnerability (CVE-2021-44228) in binary files, enabling reverse engineering of affected…

Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

Basic injectable for analyzing the behavior of evasive malware

Windows tool for dumping malware PE files from memory back to disk for analysis.

IDAPython tool for creating automatic C++ virtual tables in IDA Pro

Tool for reverse engineering macOS/OS X

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.

A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer


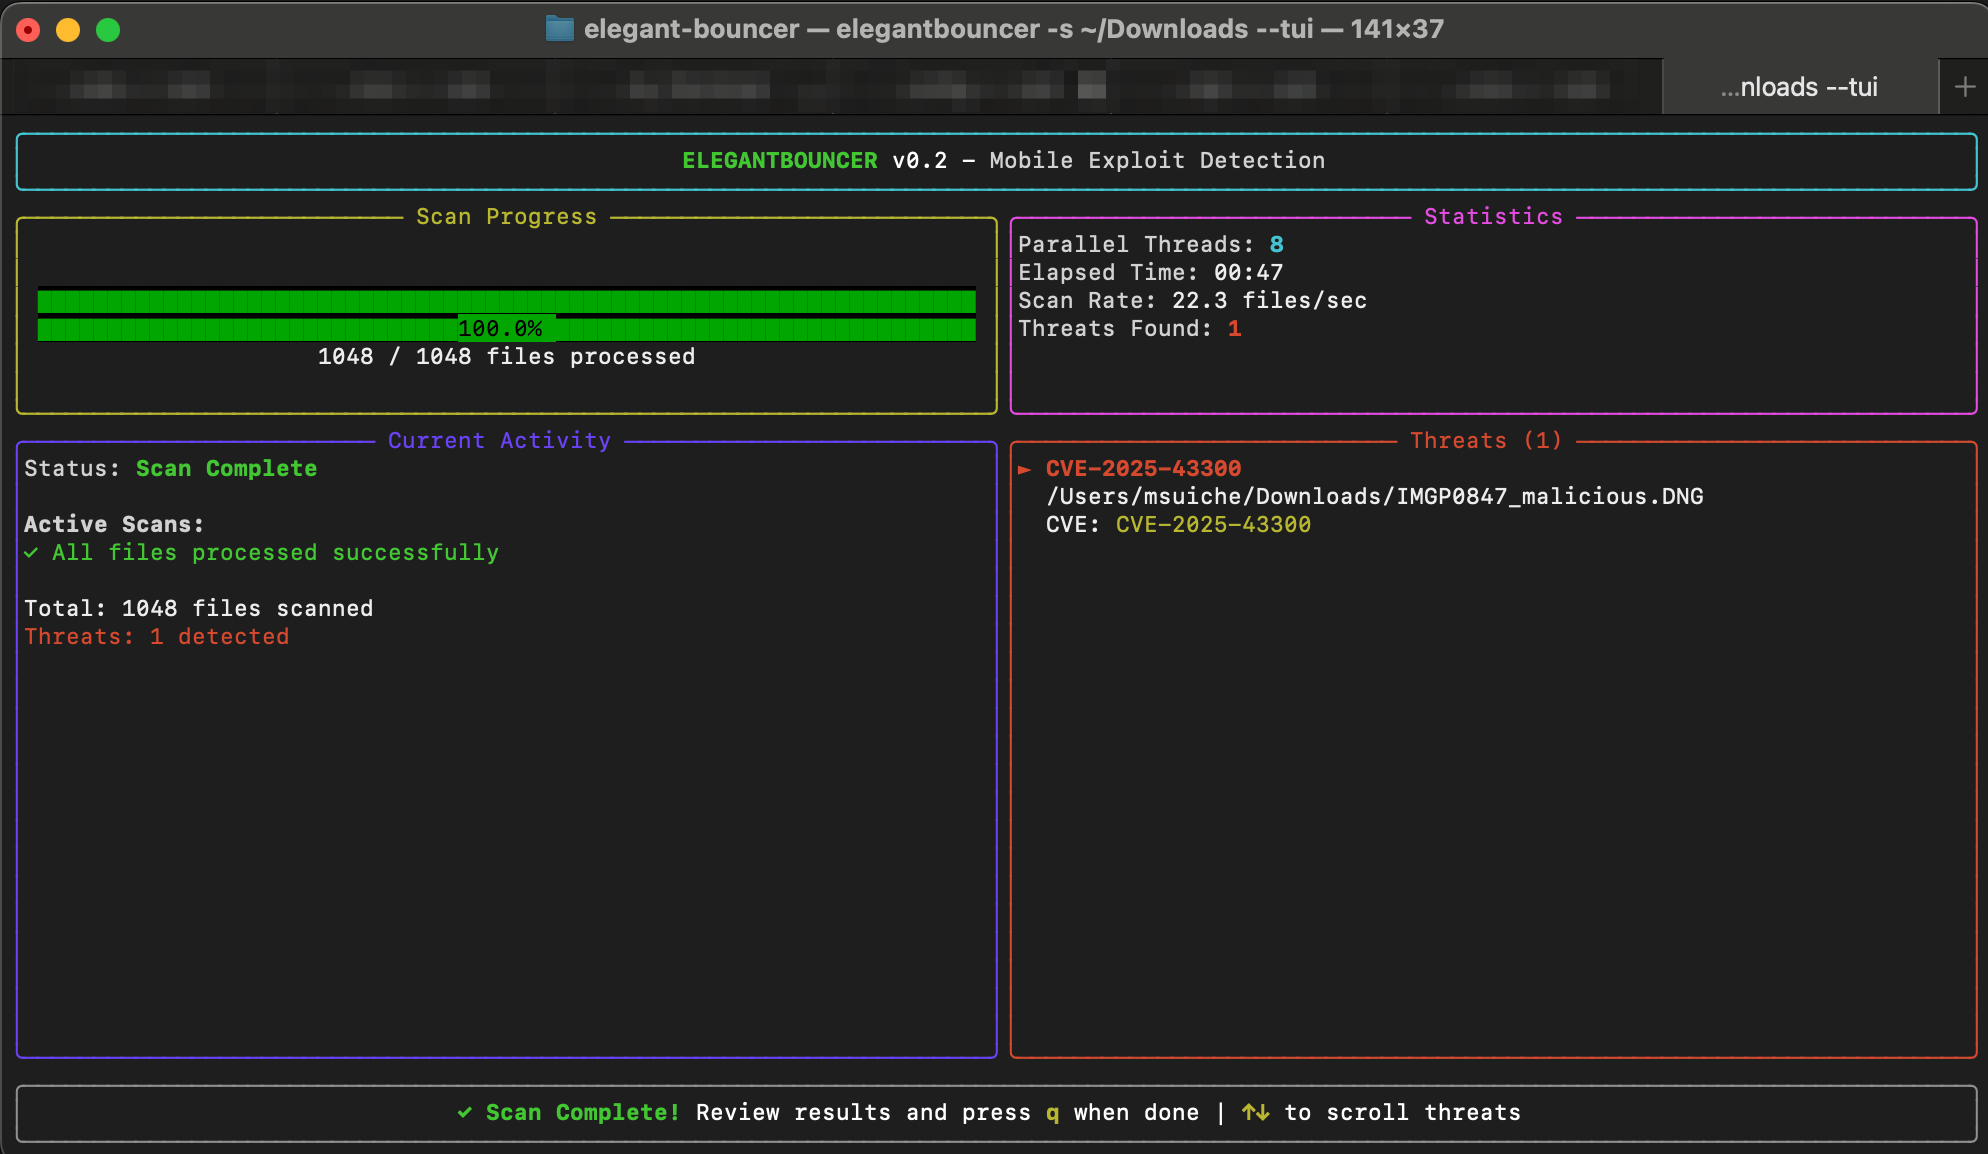
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.

ATrace is a tool for tracing execution of binaries on Windows.

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

A command line Windows API tracing tool for Golang binaries.


A tool for effective testing the binding layer of scripting languages

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…