

gef
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
ai-assisted-reversingbinary-analysisbinary-exploitation+10
8.4k
hugsy/gefGEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 trailofbits/mquire
Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
 inokinoki/attesor
AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…
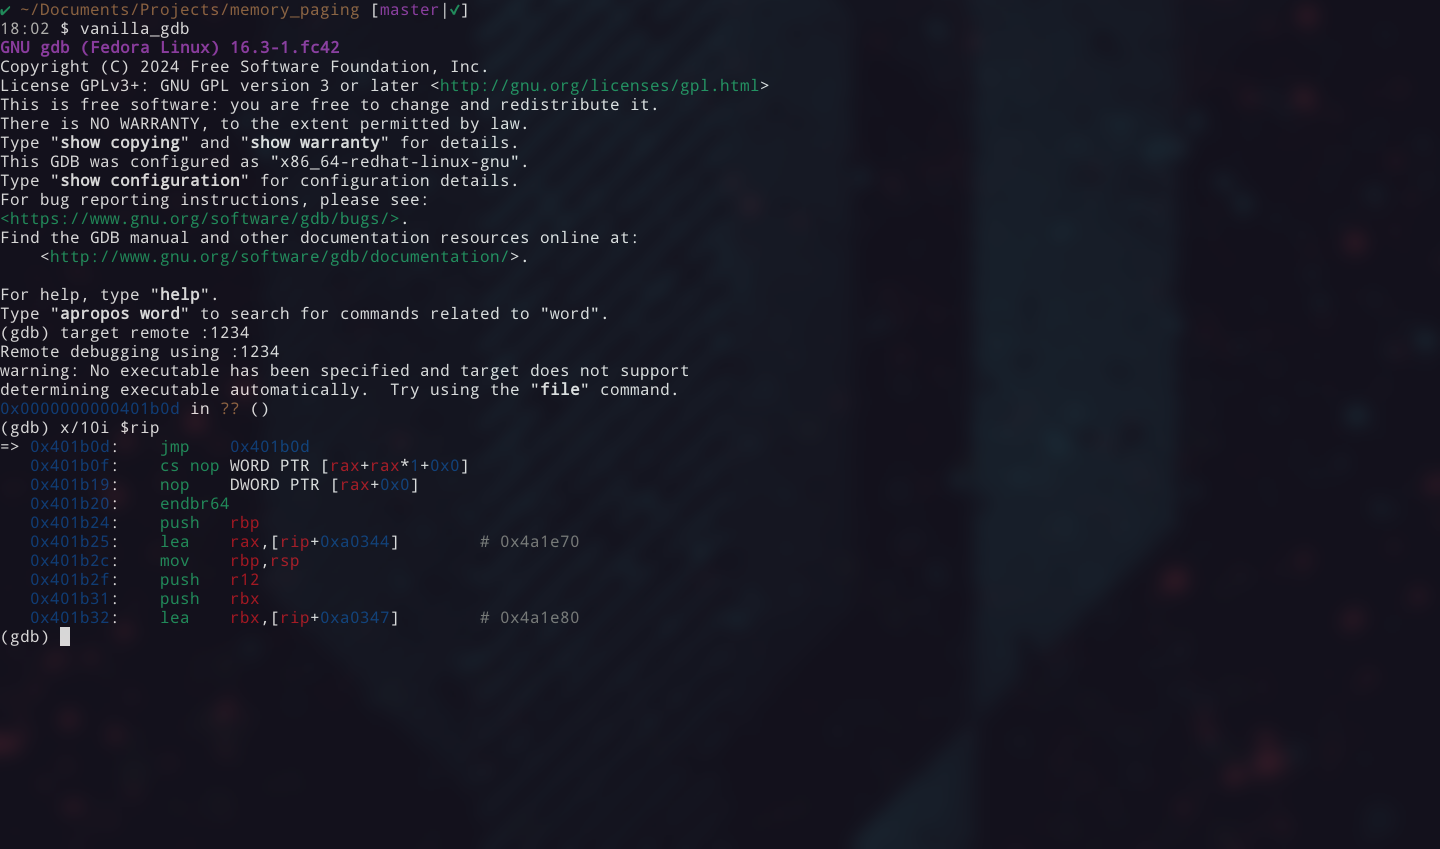 jazho76/page_table_walk
Walk x86-64 page tables by hand in qemu and gdb. Decompose a virtual address, follow cr3 through all levels of physical memory, and extract a flag…
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 chenaotian/cve-2021-3560
In-depth analysis of CVE-2021-3560, a local privilege escalation vulnerability in Linux PolKit. Includes root cause analysis, exploit mechanics, and…
 jihwan77/linux-kernel-copy-fail-cve-2026-31431-
Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…
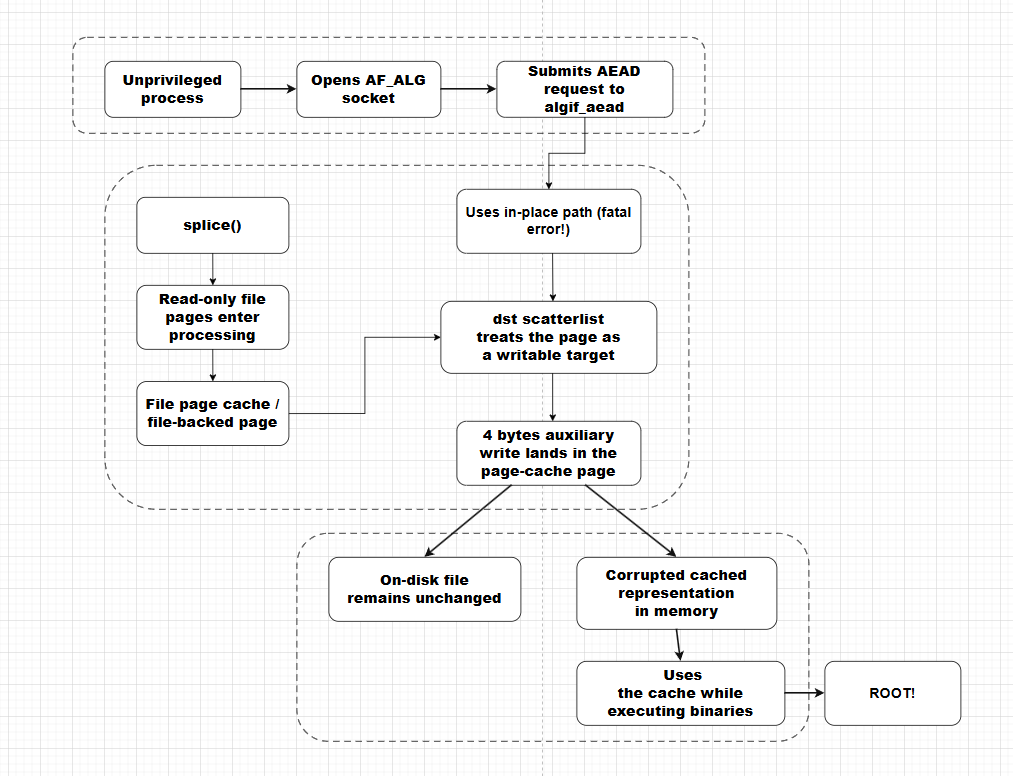 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 satheesh575555/linux-4.1.15_cve-2023-28772
Analyzes and demonstrates the Linux kernel vulnerability CVE-2023-28772, providing a patched or vulnerable kernel source for security research and…
 trinadh465/linux-4.1.15_cve-2022-45934
Linux kernel 4.1.15 source tree with a patch for CVE-2022-45934, a use-after-free vulnerability in the netfilter subsystem, for analysis and testing.
 trinadh465/linux-4.1.15_cve-2022-3564
Linux kernel 4.1.15 source code snapshot for analyzing and studying CVE-2022-3564, a vulnerability in the kernel's network subsystem.
 nanopathi/linux-4.19.72_cve-2020-25705
Linux kernel 4.19.72 source code with a focus on CVE-2020-25705, intended for vulnerability analysis, exploitation research, and educational study of…
 nanopathi/linux-4.19.72_cve-2020-29370
Linux kernel version 4.19.72 with a specific patch for CVE-2020-29370, intended for vulnerability analysis and exploitation research.
 trinadh465/linux-4.1.15_cve-2023-4128
Linux kernel 4.1.15 source code with a focus on CVE-2023-4128, intended for vulnerability analysis and educational study of kernel security.
 trinadh465/linux-4.1.15_cve-2023-28772
Linux kernel 4.1.15 source tree with patches for CVE-2023-28772, providing a reference for vulnerability analysis and exploitation research.
 trinadh465/linux-4.19.72_cve-2023-35828
Linux kernel source tree modified to demonstrate CVE-2023-35828, providing a reference for vulnerability analysis and exploitation research.
 trinadh465/linux-3.0.35_cve-2019-10220
Linux kernel 3.0.35 source tree with a focus on CVE-2019-10220, providing a reference for vulnerability analysis and exploitation research.
 aurh1l-42-projects/woody-woodpacker
ELF binary packer that encrypts code sections and injects a runtime decryption stub for 64-bit Linux executables, demonstrating code injection and…