

Process-Dump
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k1 month ago
glmcdona/process-dumpWindows tool for dumping malware PE files from memory back to disk for analysis.
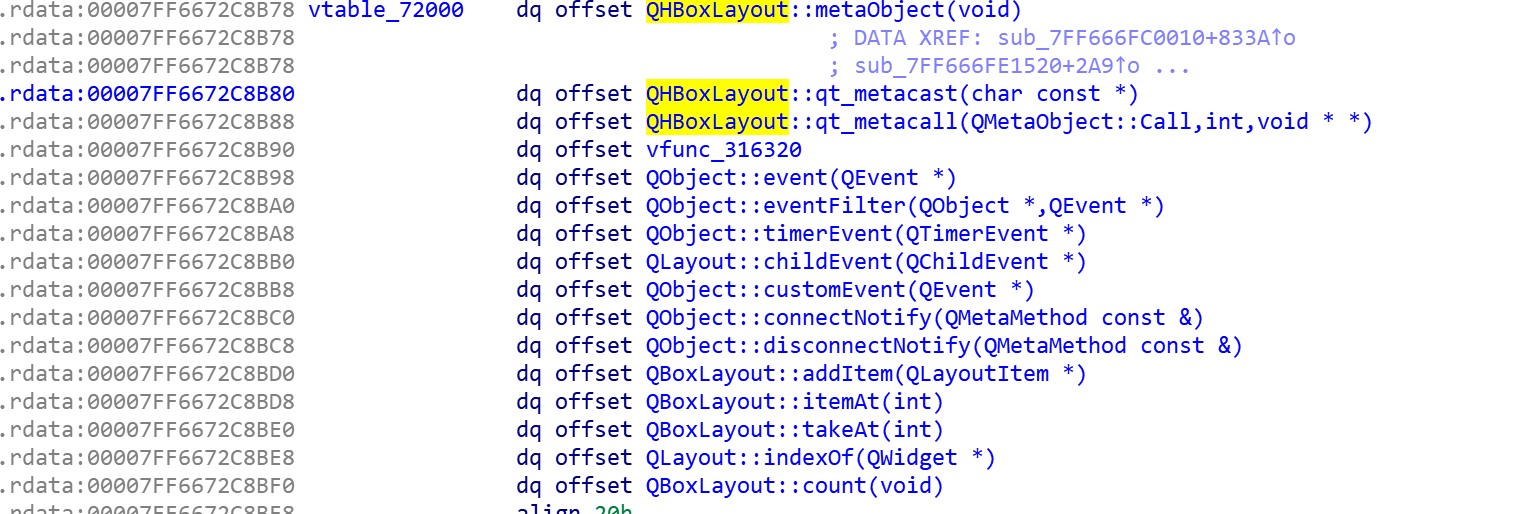 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
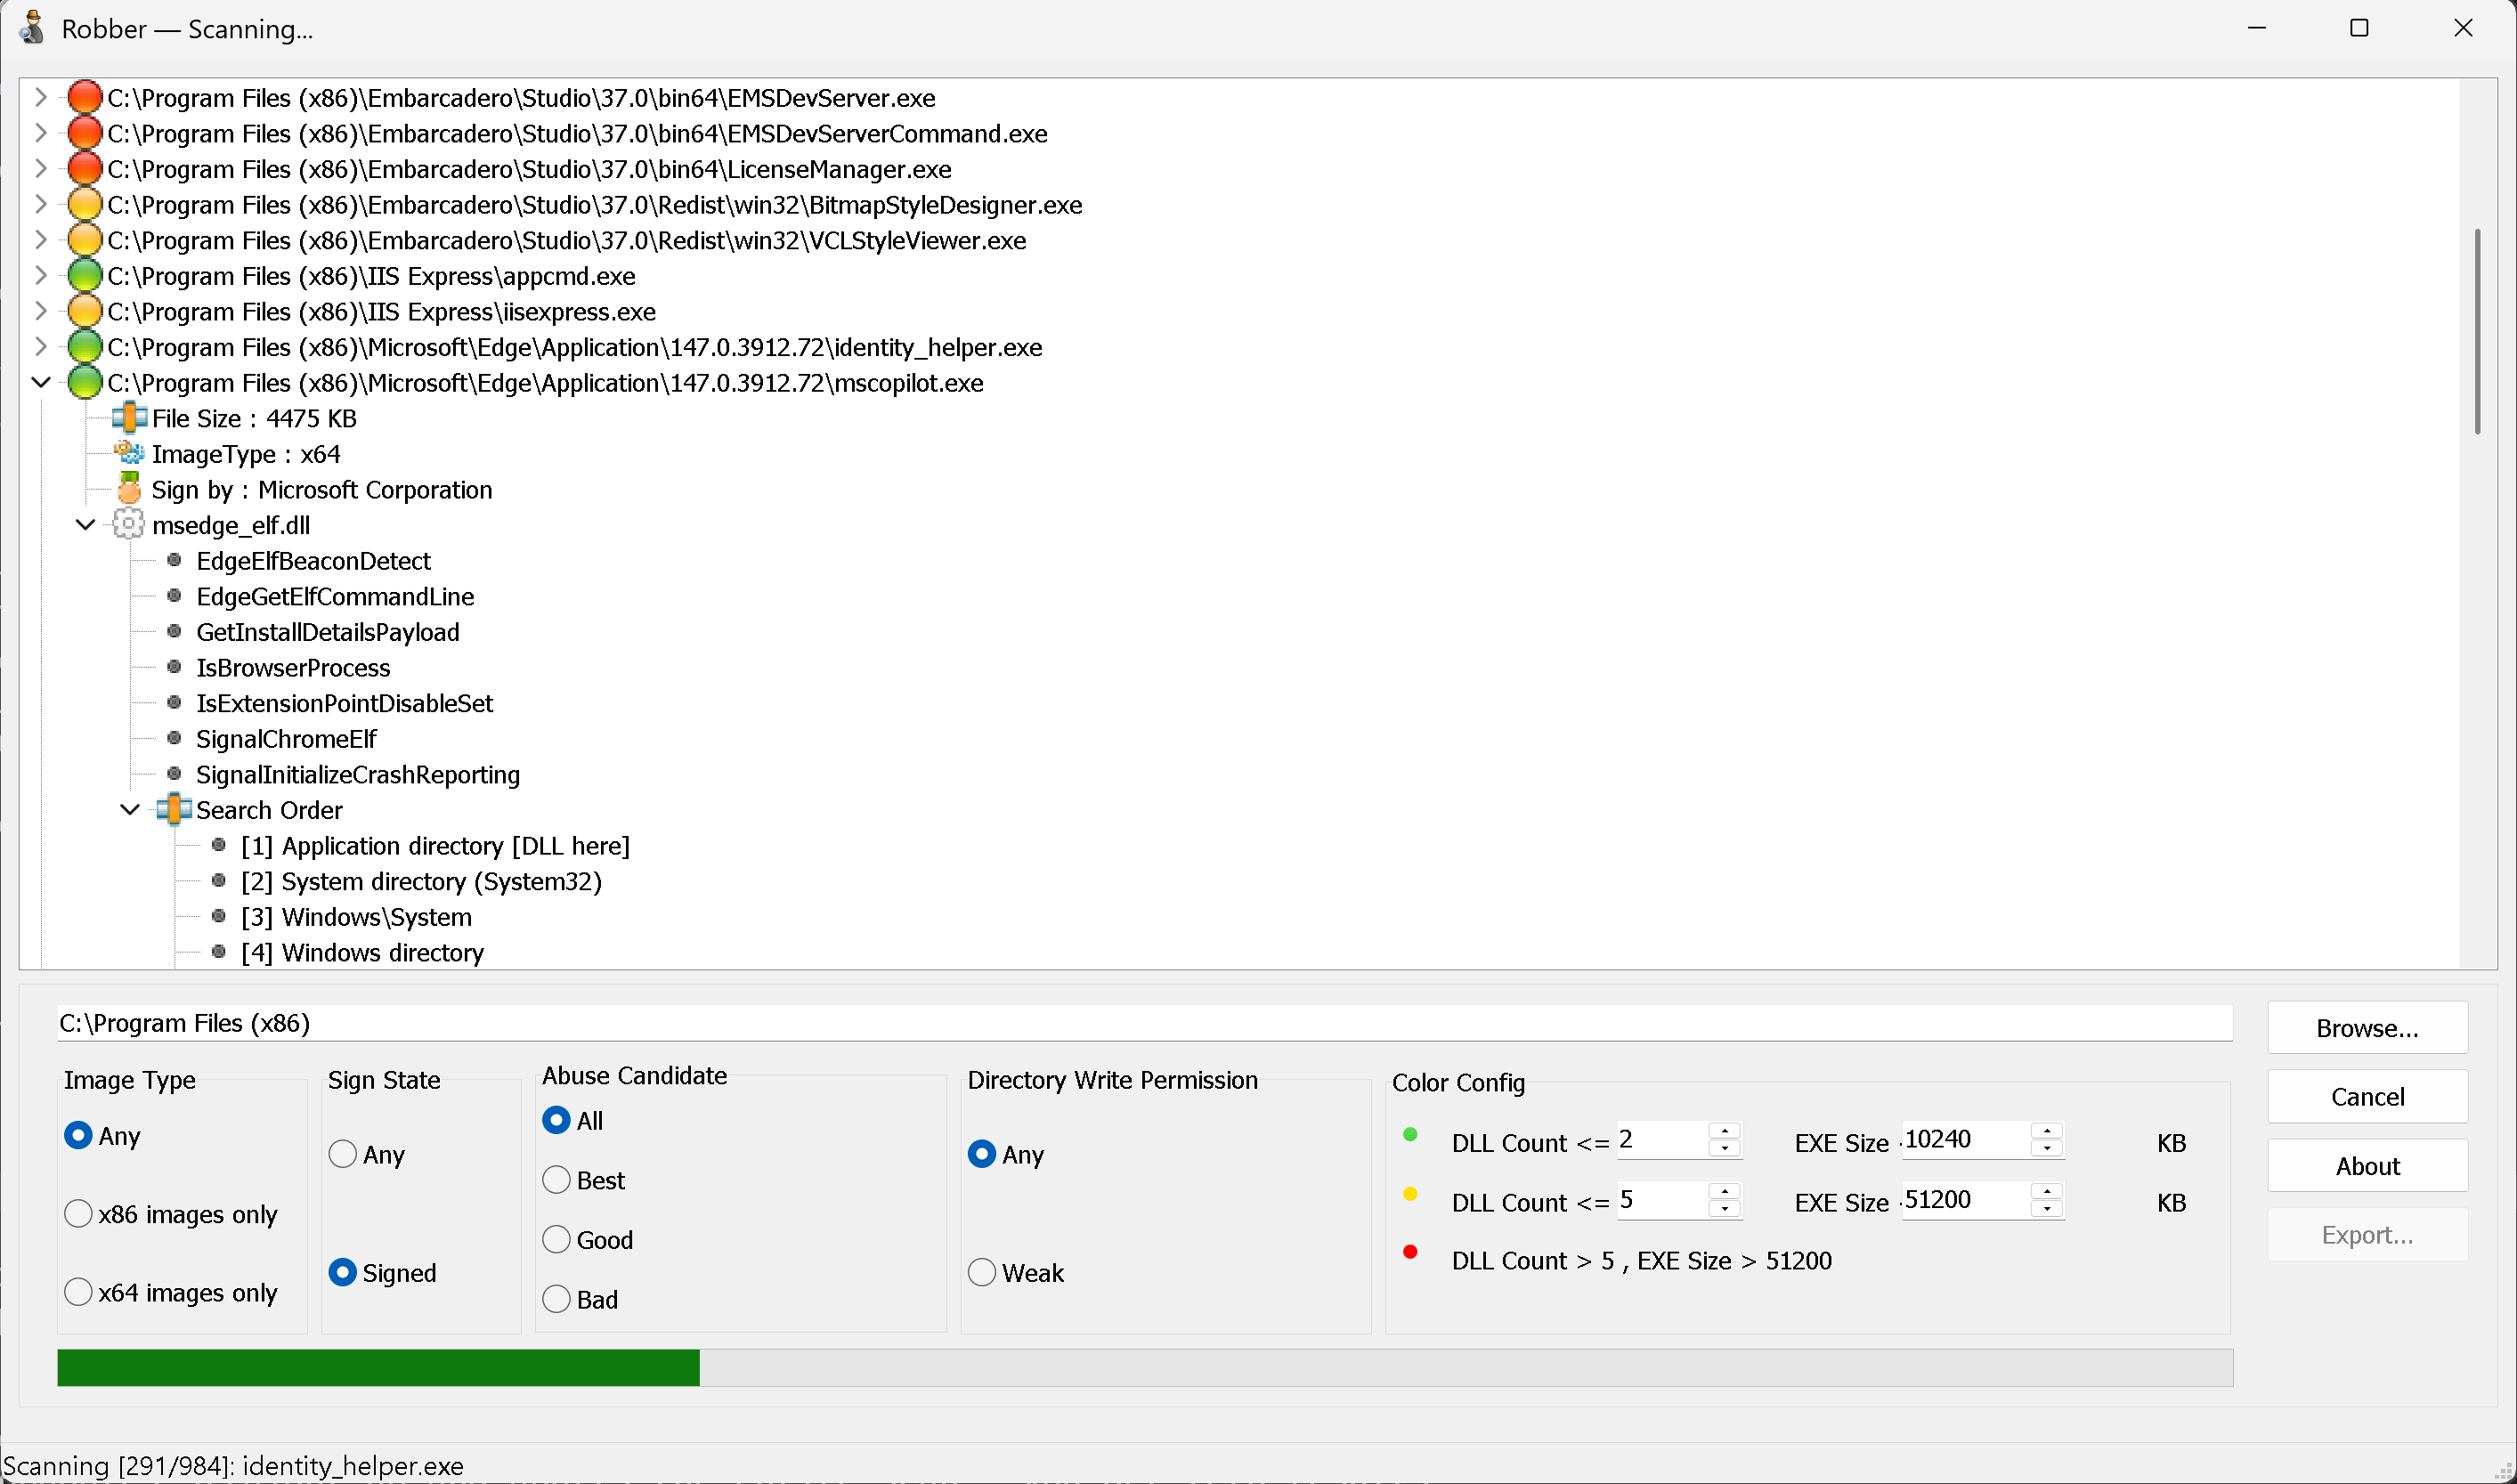 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
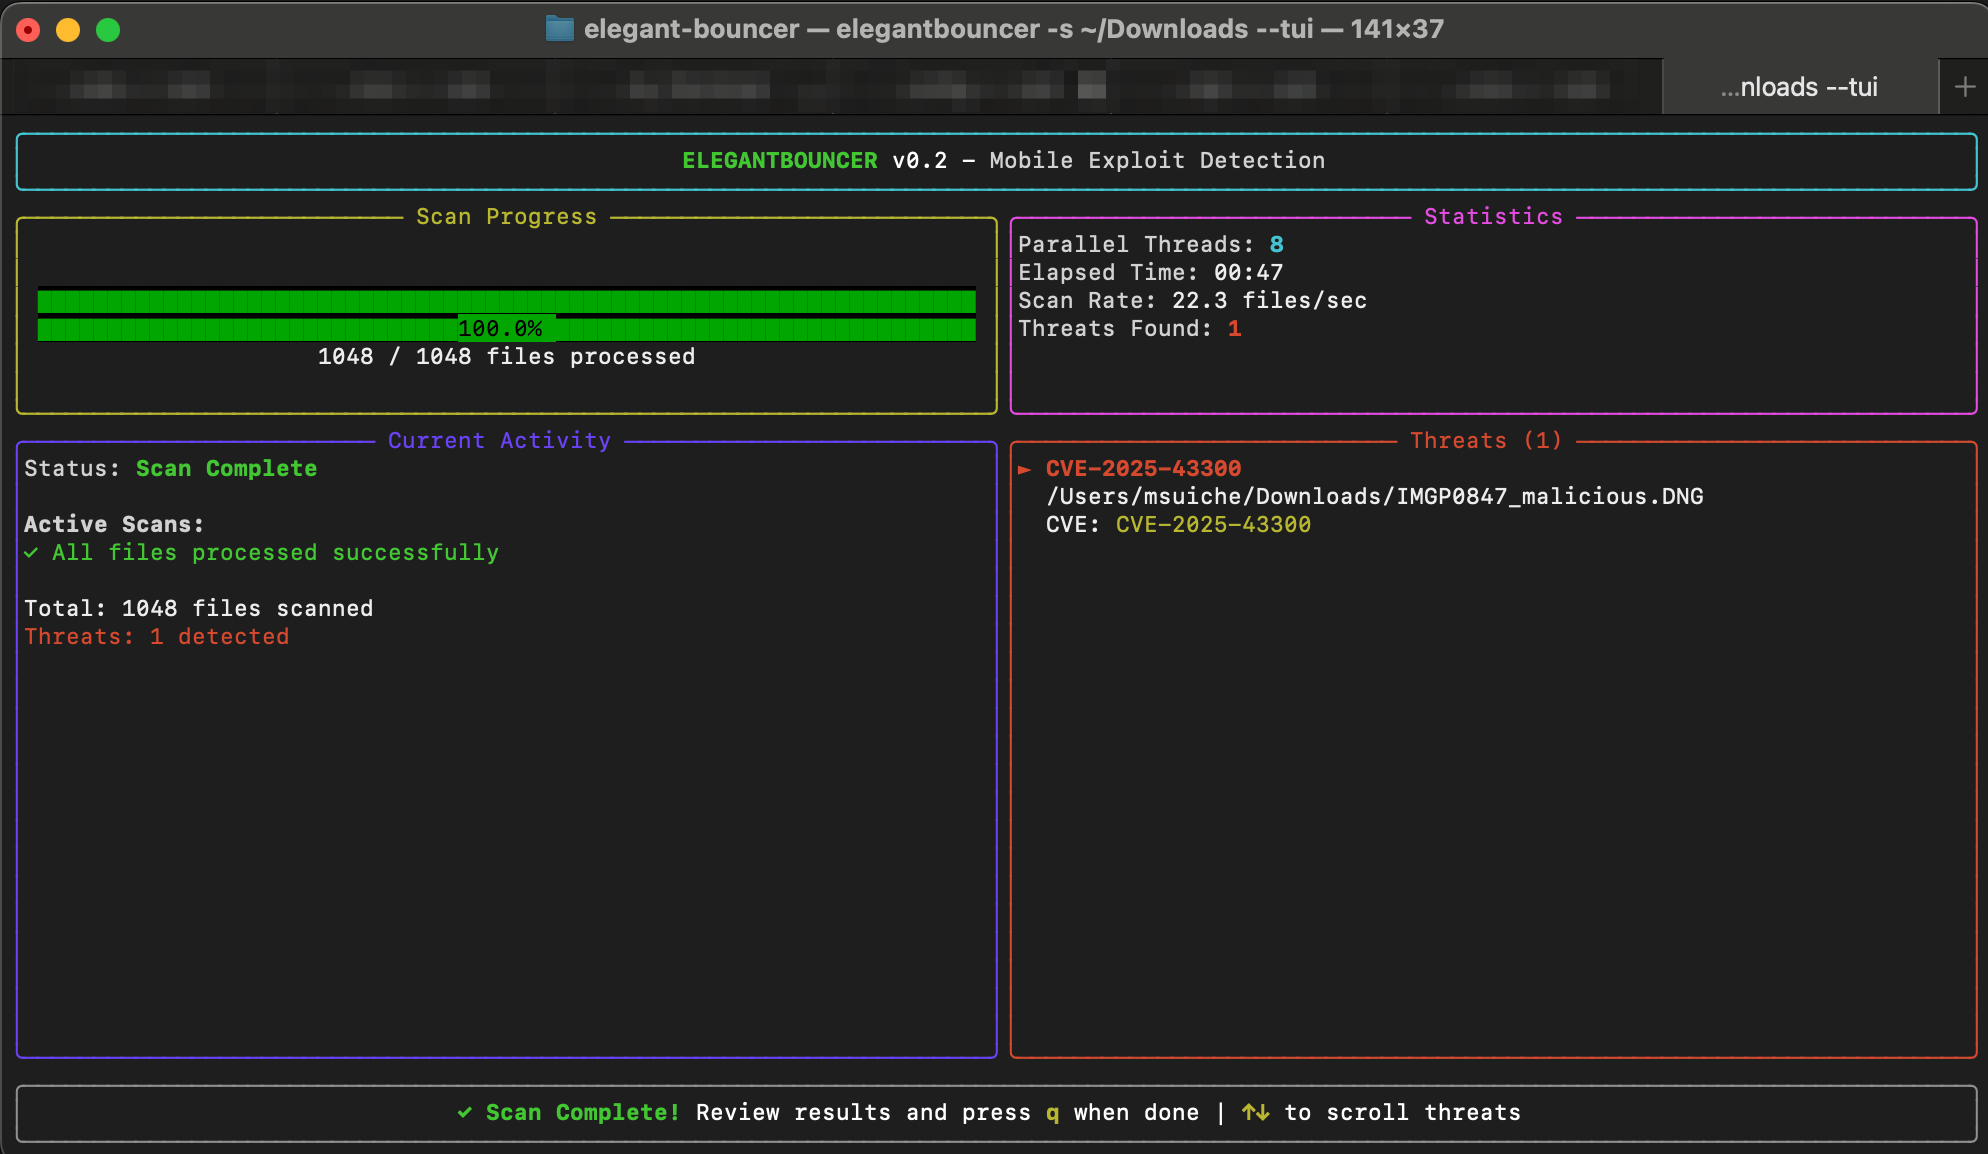 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.
