
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1171 results
go_parser preview

go_parser

GitHub0xjiayu/go_parser

Yet Another Golang binary parser for IDAPro

binary-analysisdebuggersmalware-analysis+1
1.3k2 years ago
Nimcrypt2 preview

Nimcrypt2

GitHubicyguider/nimcrypt2

.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
binary-analysisdefensive-toolsencryption-decryption-tools+6
8254 years ago
rematch preview

rematch

GitHubnirizr/rematch

REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
binary-analysisreverse-engineeringutilities-frameworks
1567 years ago
SusanRTTI preview

SusanRTTI

GitHubnccgroup/susanrtti

Another RTTI Parsing IDA plugin
binary-analysisreverse-engineeringstatic-analysis+1
3123 years ago
decomp2dbg preview

decomp2dbg

GitHubmahaloz/decomp2dbg

A plugin to introduce interactive symbols into your debugger from your decompiler
binary-analysisbinary-exploitationdebuggers+3
8212 months ago
flare-floss preview

flare-floss

GitHubmandiant/flare-floss

FLARE Obfuscated String Solver - Automatically extract obfuscated strings from malware.
ai-assisted-reversingbinary-analysisdigital-forensics+8
4.2k3 days ago
malware-samples preview

malware-samples

GitHubfabrimagic72/malware-samples

A collection of malware samples caught by several honeypots i manage
binary-analysiscurated-resourcesdigital-forensics+4
1.9k5 years ago
VX-API preview

VX-API

GitHubvxunderground/vx-api

Collection of various malicious functionality to aid in malware development

anti-botbinary-analysiscryptography+5
1.9k3 years ago
malware-samples preview

malware-samples

GitHubjstrosch/malware-samples

Malware samples, analysis exercises and other interesting resources.
binary-analysiscurated-resourceseducation+3
1.7k2 years ago
flare-learning-hub preview

flare-learning-hub

GitHubmandiant/flare-learning-hub

Free educational content on reverse engineering and malware analysis from the FLARE team
binary-analysisdebuggerseducation+4
1.5k5 months ago
dumpulator preview

dumpulator

GitHubmrexodia/dumpulator

An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
8852 years ago
engine preview

engine

GitHubdroidefense/engine

Droidefense: Advance Android Malware Analysis Framework
android-securitybinary-analysisdynamic-analysis-sandboxing+4
4806 years ago
PEpper preview

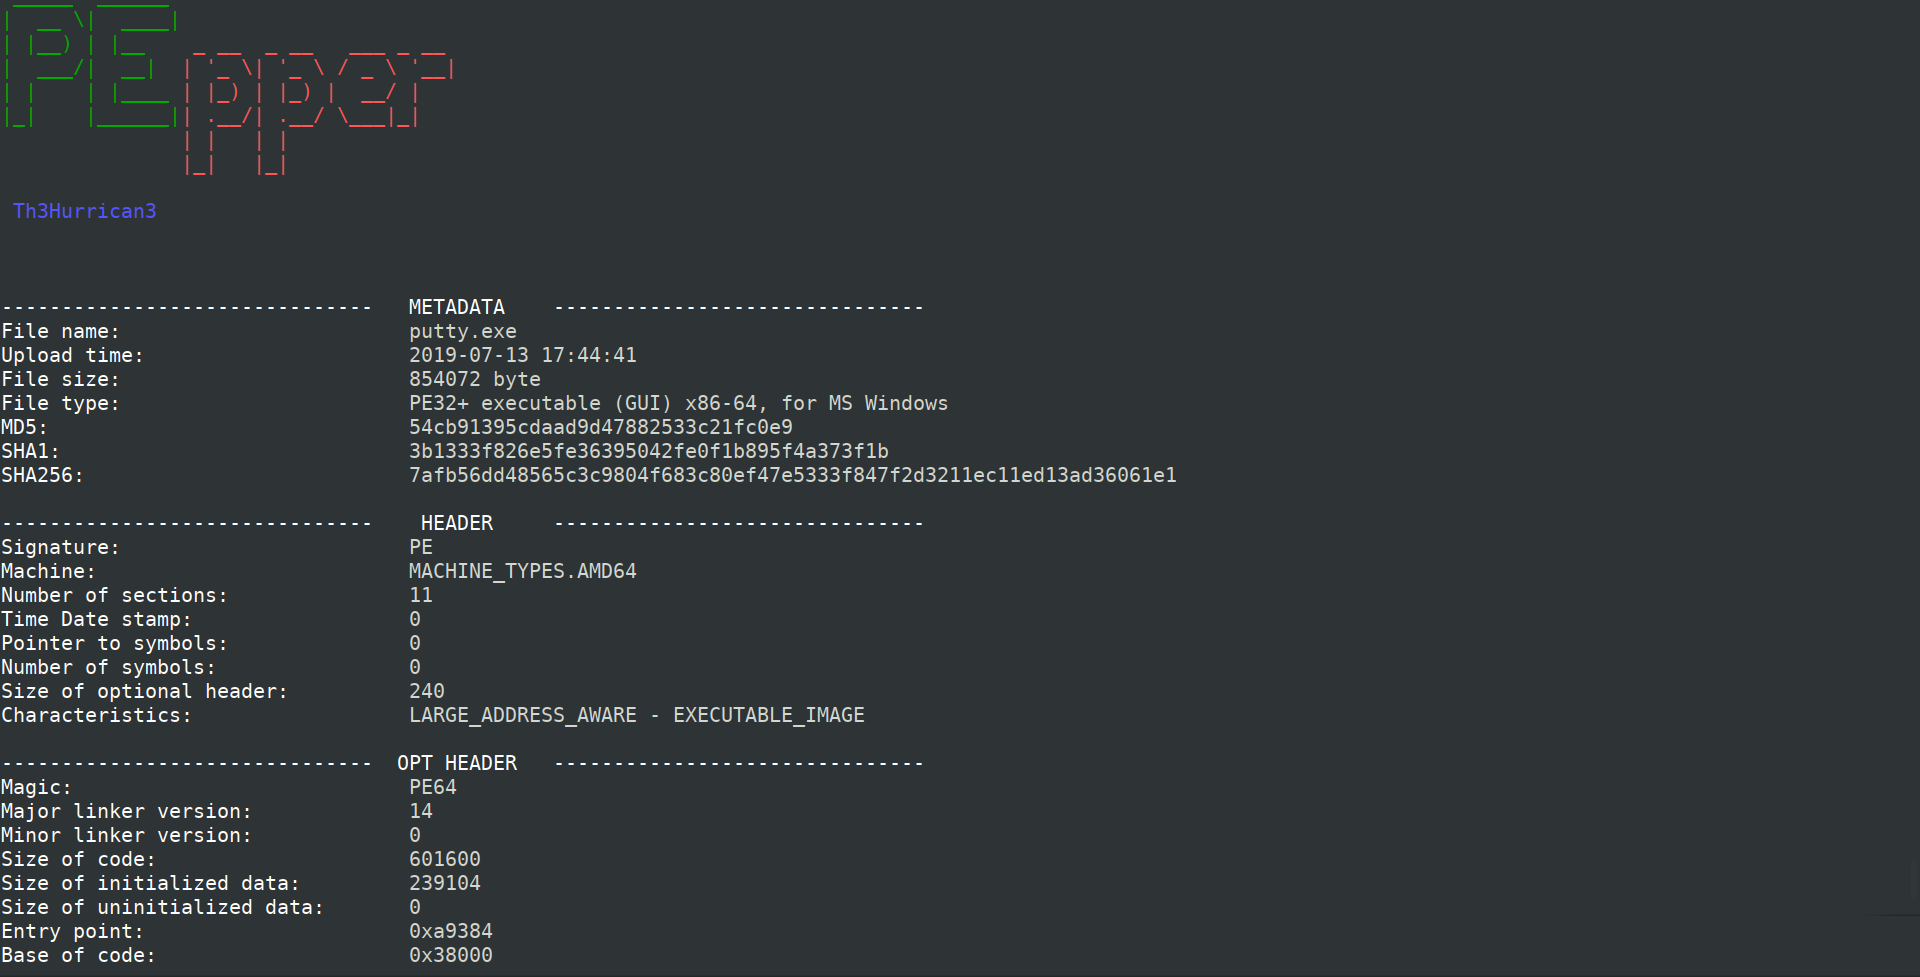
PEpper

GitHub0x0be/pepper

An open source script to perform malware static analysis on Portable Executable

binary-analysisforensicsmalware-analysis+1
3344 years ago
freki preview

freki

GitHubcristianzsh/freki

Open-source malware analysis platform with static PE analysis, YARA pattern matching, VirusTotal integration, REST API, and Docker deployment for…
binary-analysismalware-analysisreverse-engineering+2
4452 years ago
hacksguard preview

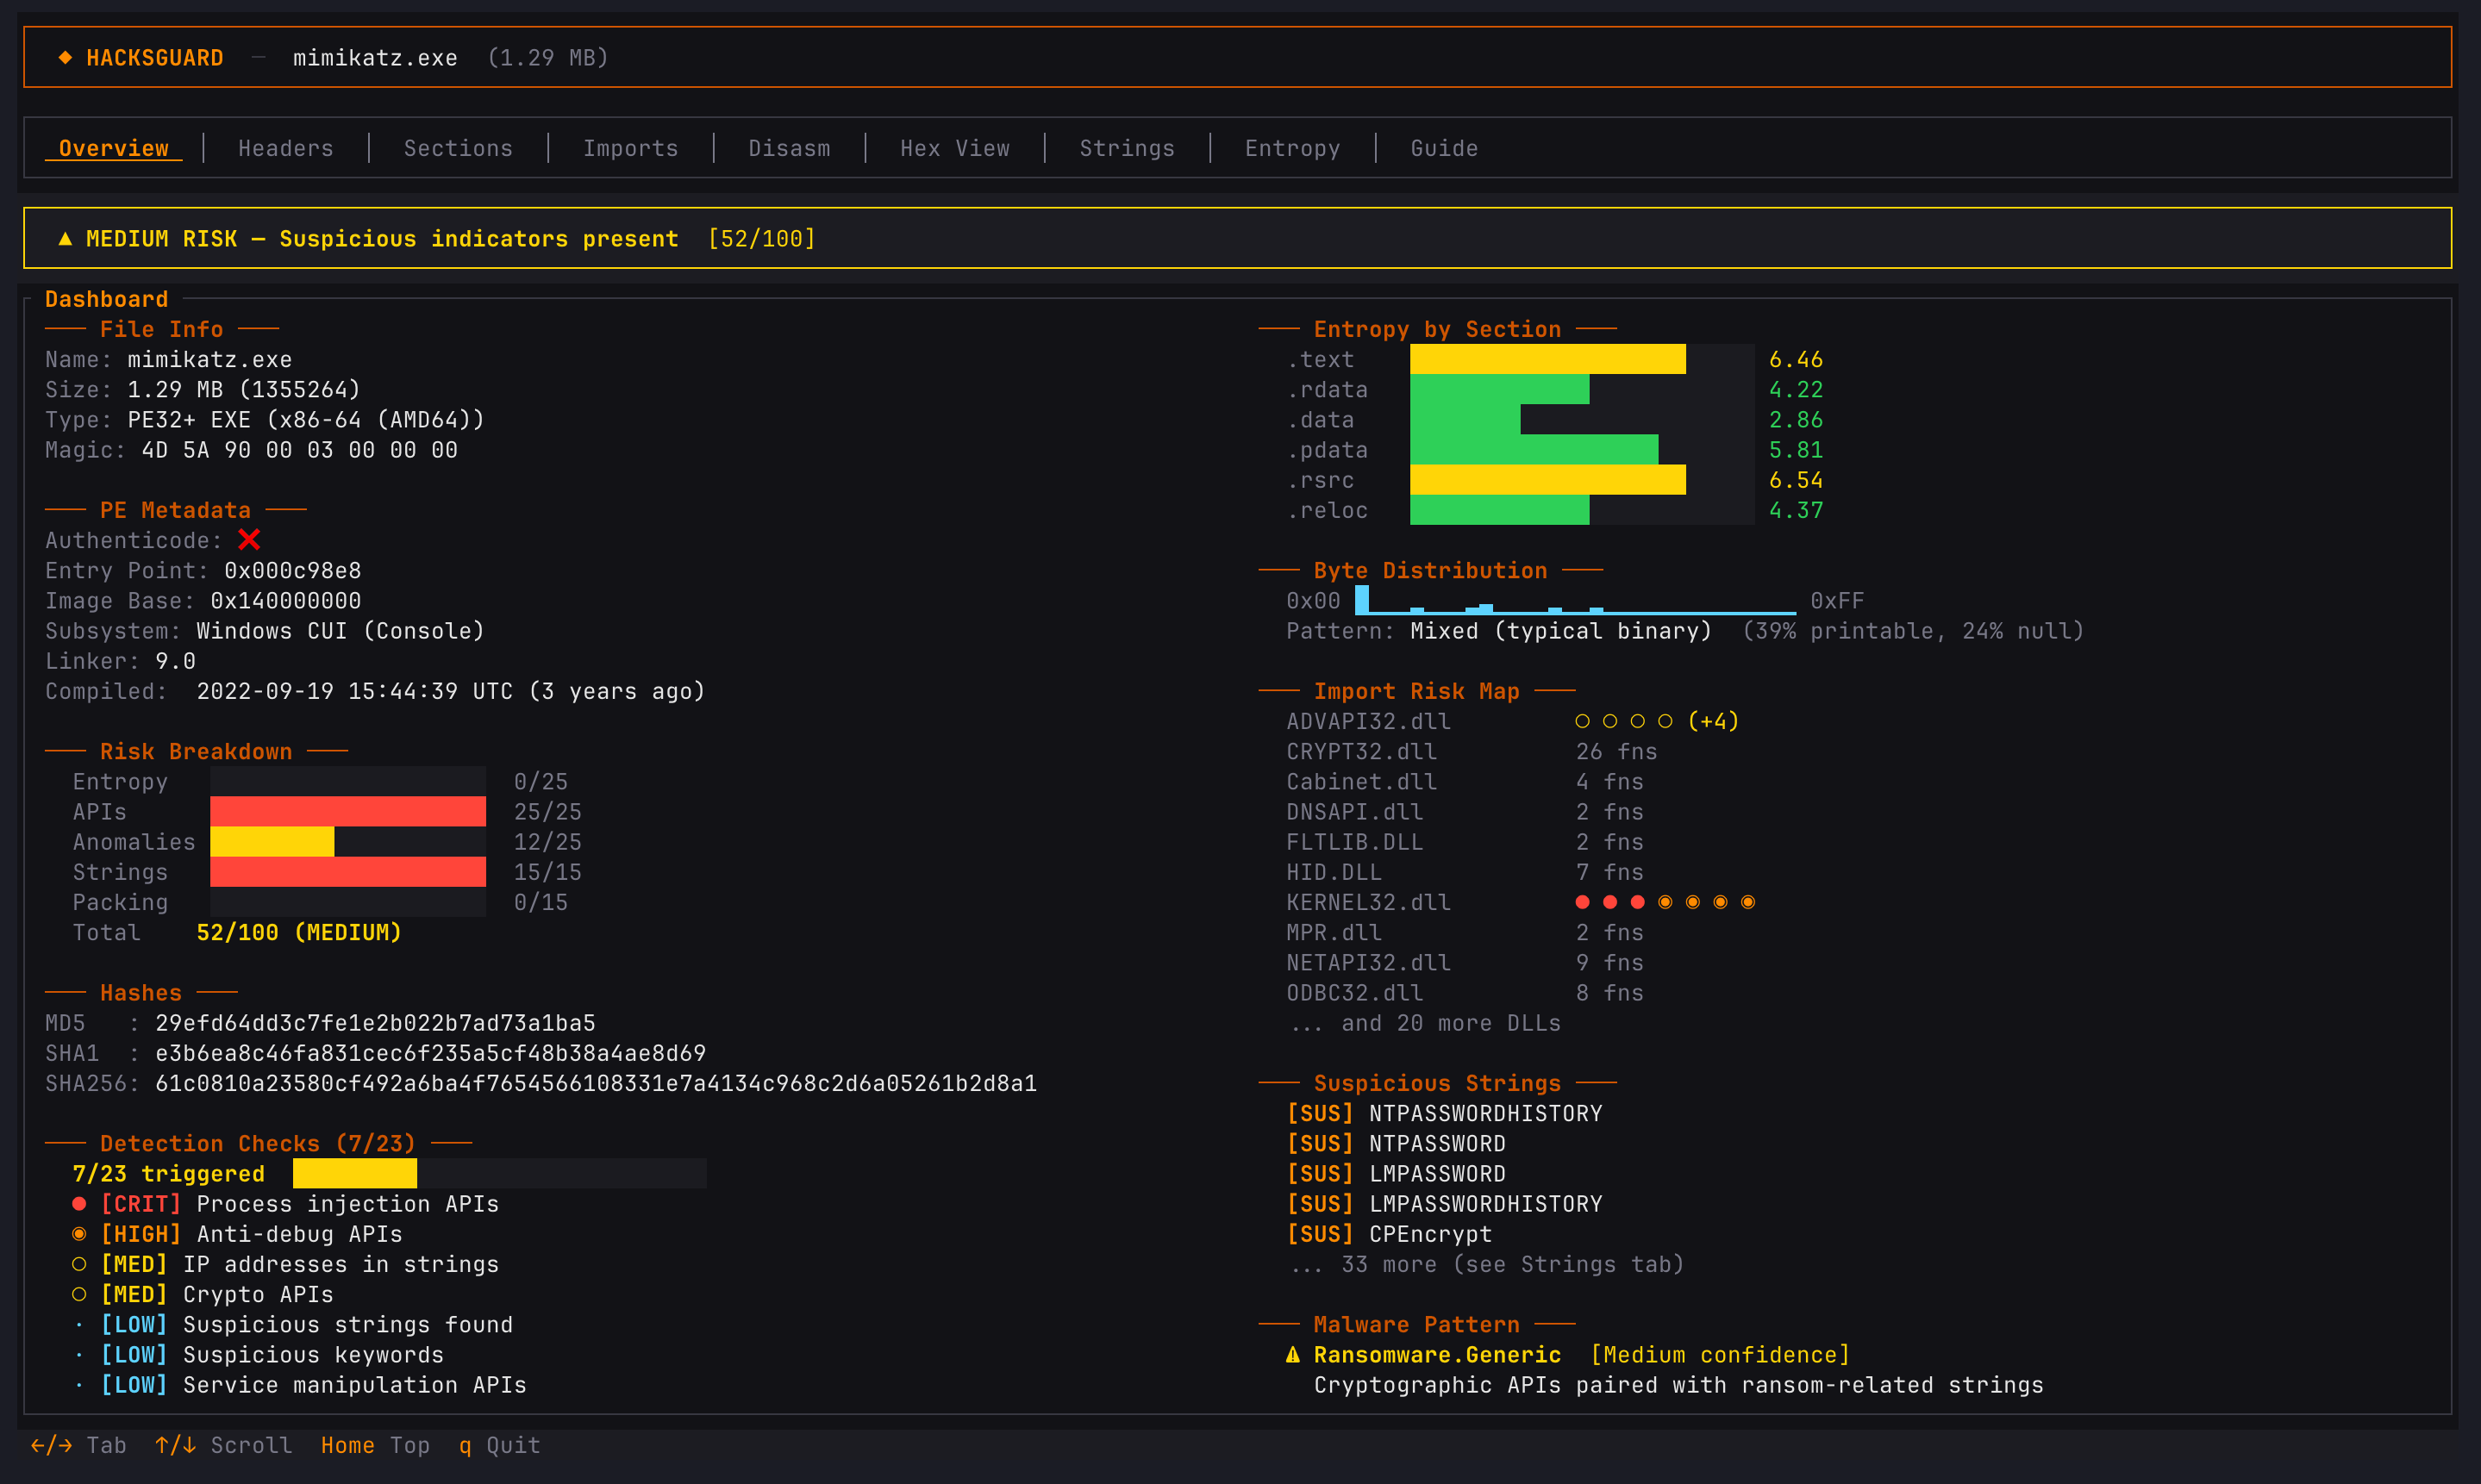
hacksguard

GitHubrhacknarok/hacksguard

A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
binary-analysisforensicsmalware-analysis+2
21416 days ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
16517h 54m ago
awesome-reverse-engineering-and-malware-analysis preview

awesome-reverse-engineering-and-malware-analysis

GitHubzx41r/awesome-reverse-engineering-and-malware-analysis

A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…

binary-analysisbinary-exploitationctf+8
8927 days ago
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…

binary-analysisforensicsincident-response+1
1702 years ago
Previous12…66Next