
CVE-2022-4510
 electr0sm0g/cve-2022-4510
Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
binary-analysisexploitationfirmware-analysis+2
9
electr0sm0g/cve-2022-4510Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
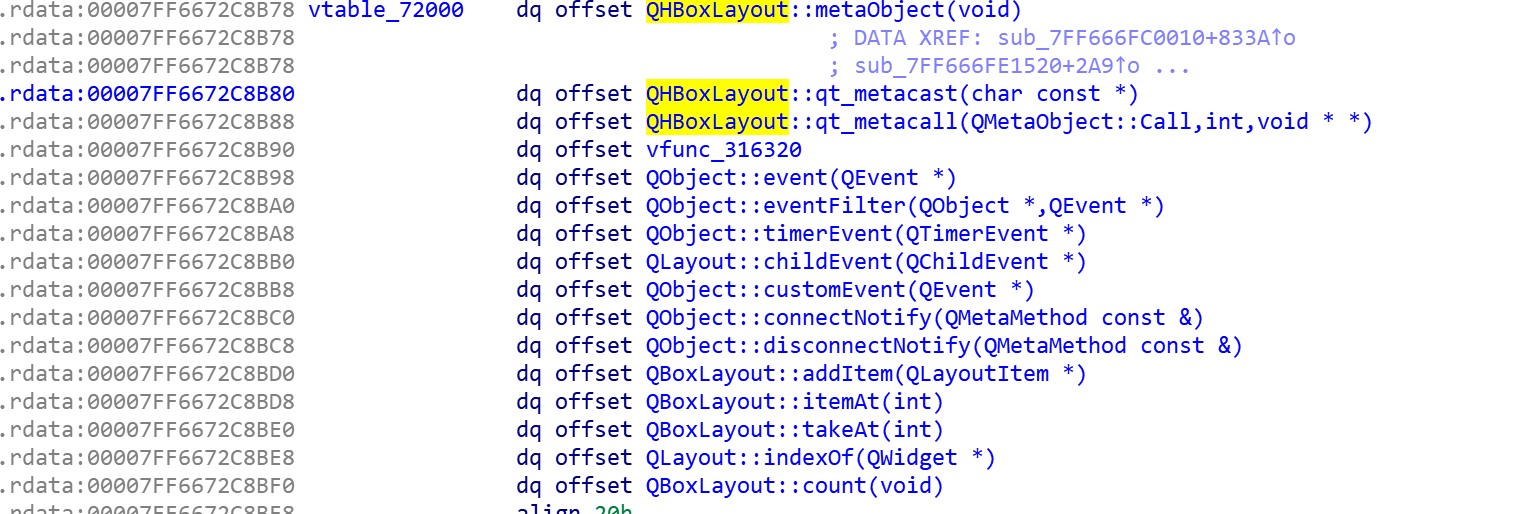 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 steven-michaud/hookcase
Tool for reverse engineering macOS/OS X
 ucsb-seclab/dr_checker
DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers
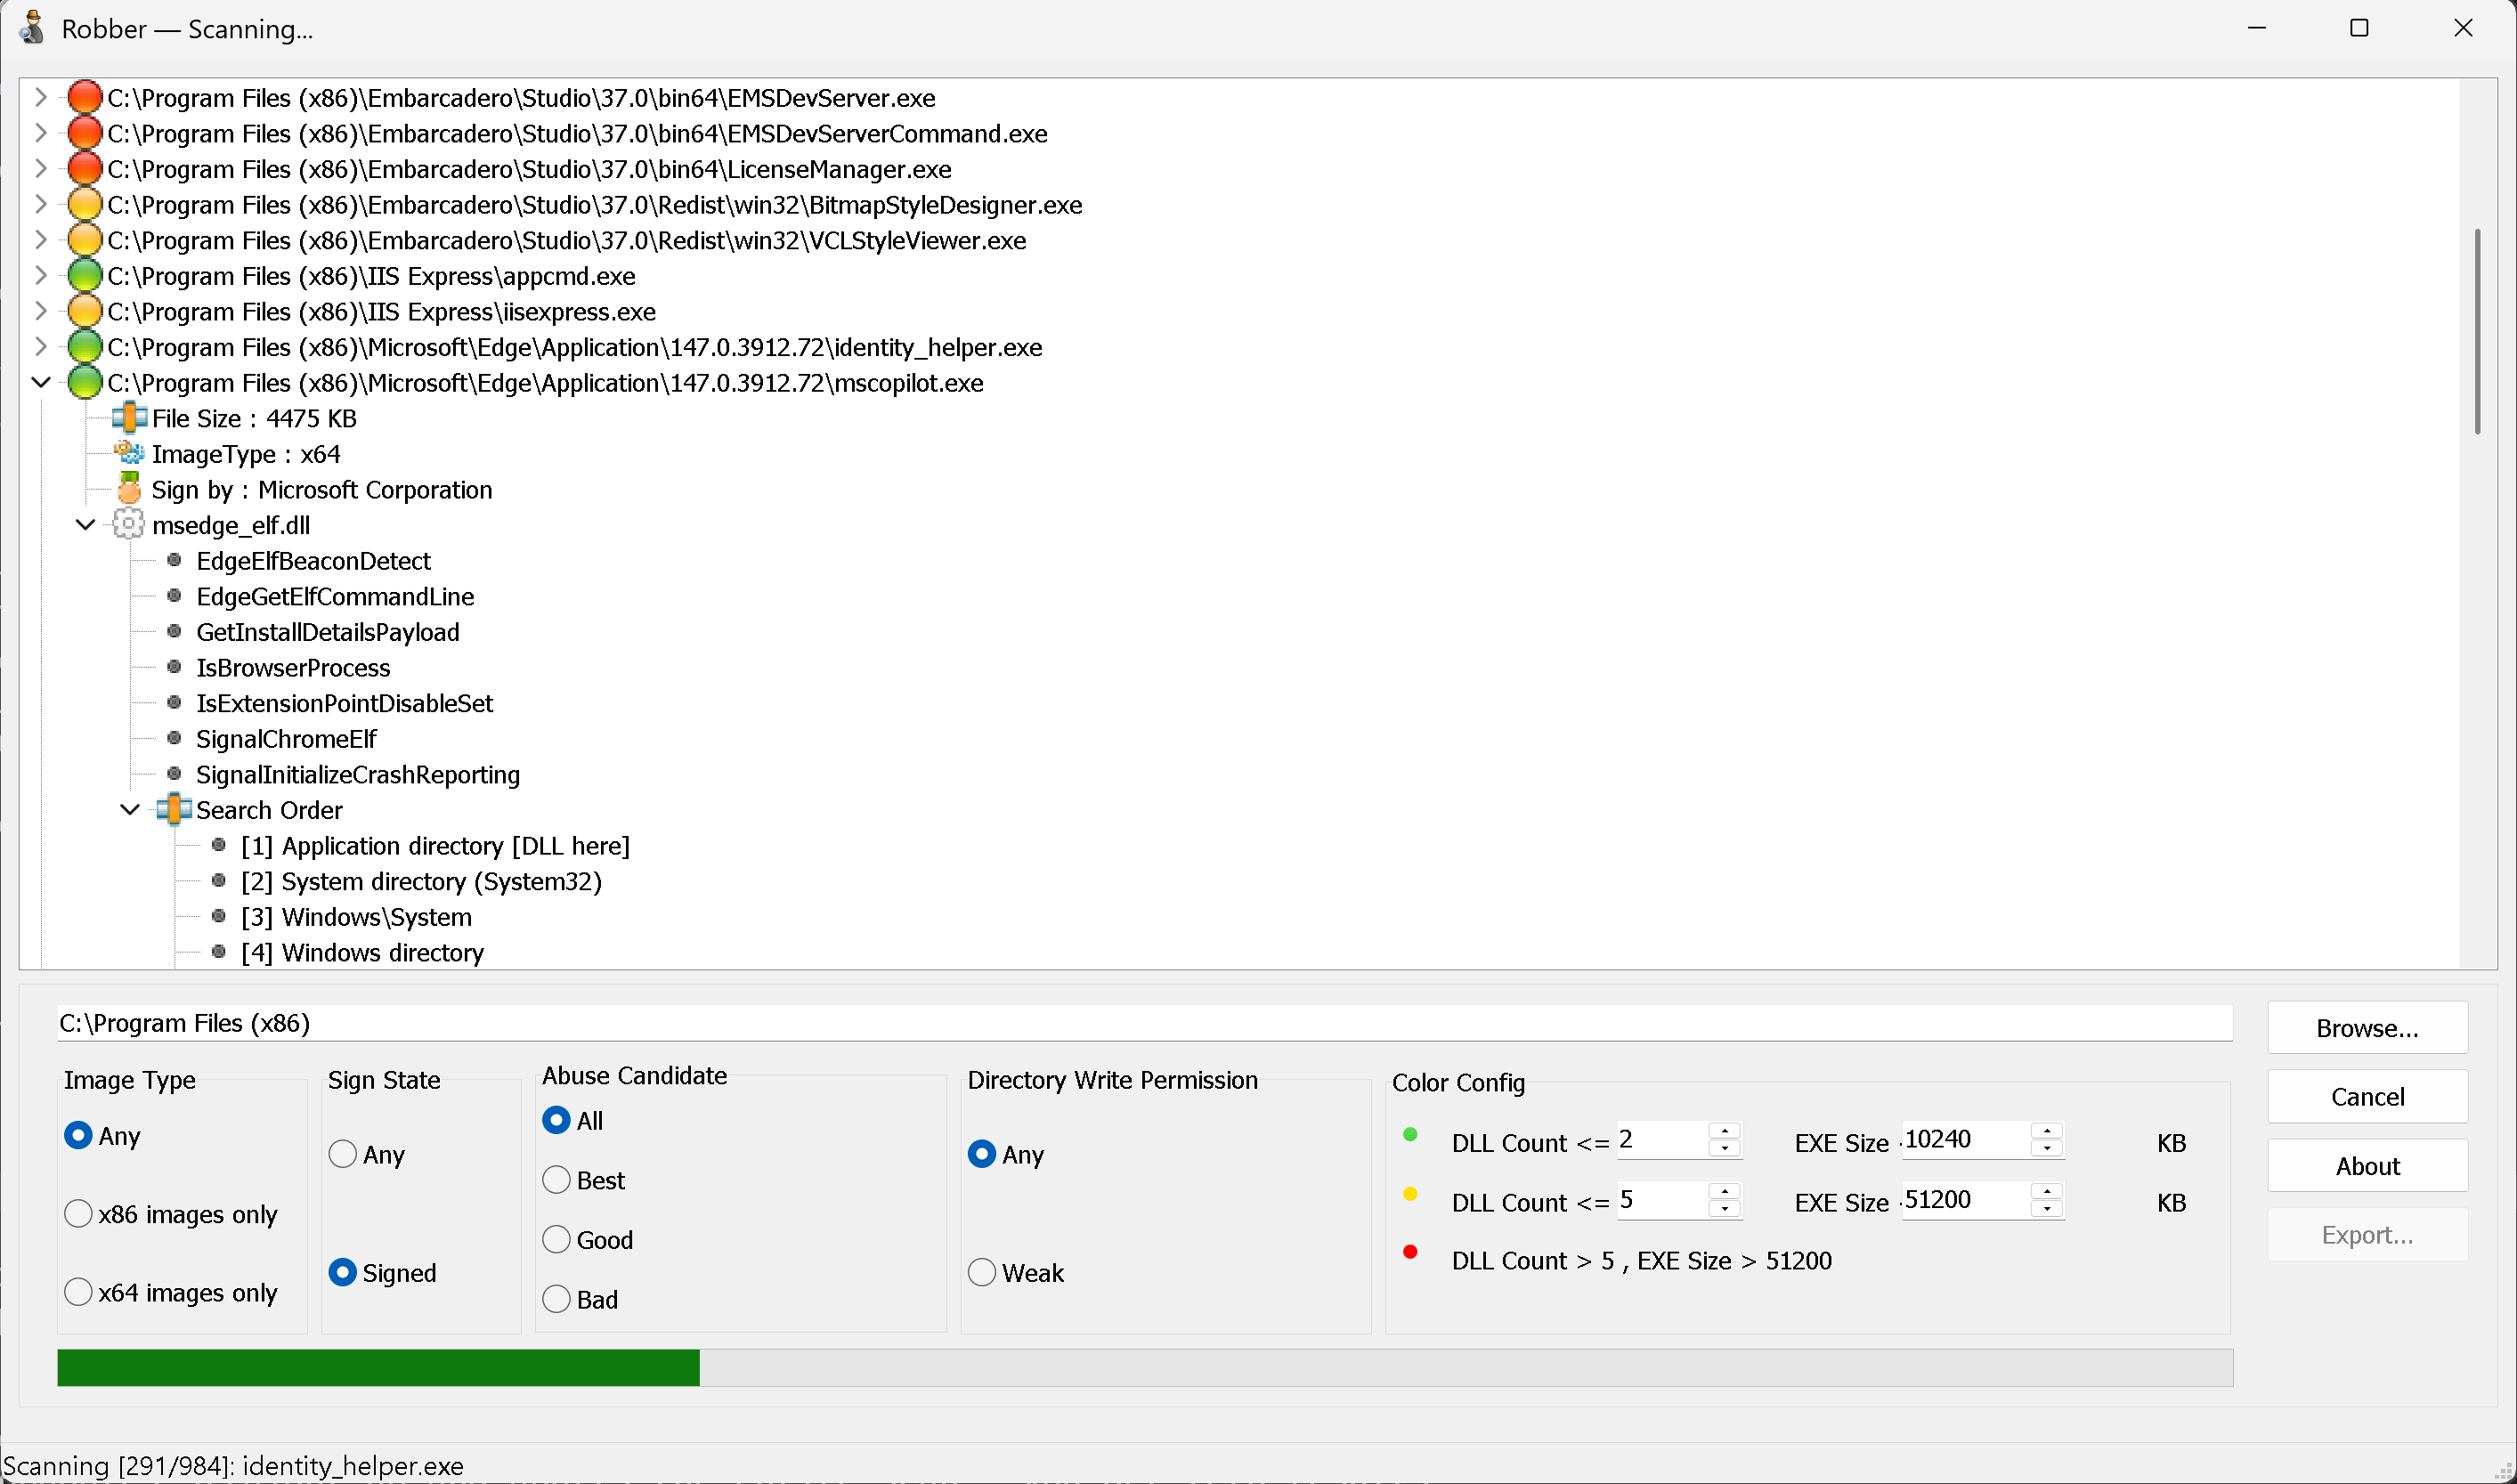 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
 squiblydoo/debloat
A GUI and CLI tool for removing bloat from executables
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 leandrofroes/gftrace
A command line Windows API tracing tool for Golang binaries.