CVE-2024-54916
 sahalll/cve-2024-54916
Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
android-securityauthenticationbinary-analysis+4
sahalll/cve-2024-54916Frida-based proof-of-concept demonstrating authentication bypass in Telegram Android by hooking SharedConfig.checkPasscode to always return true,…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
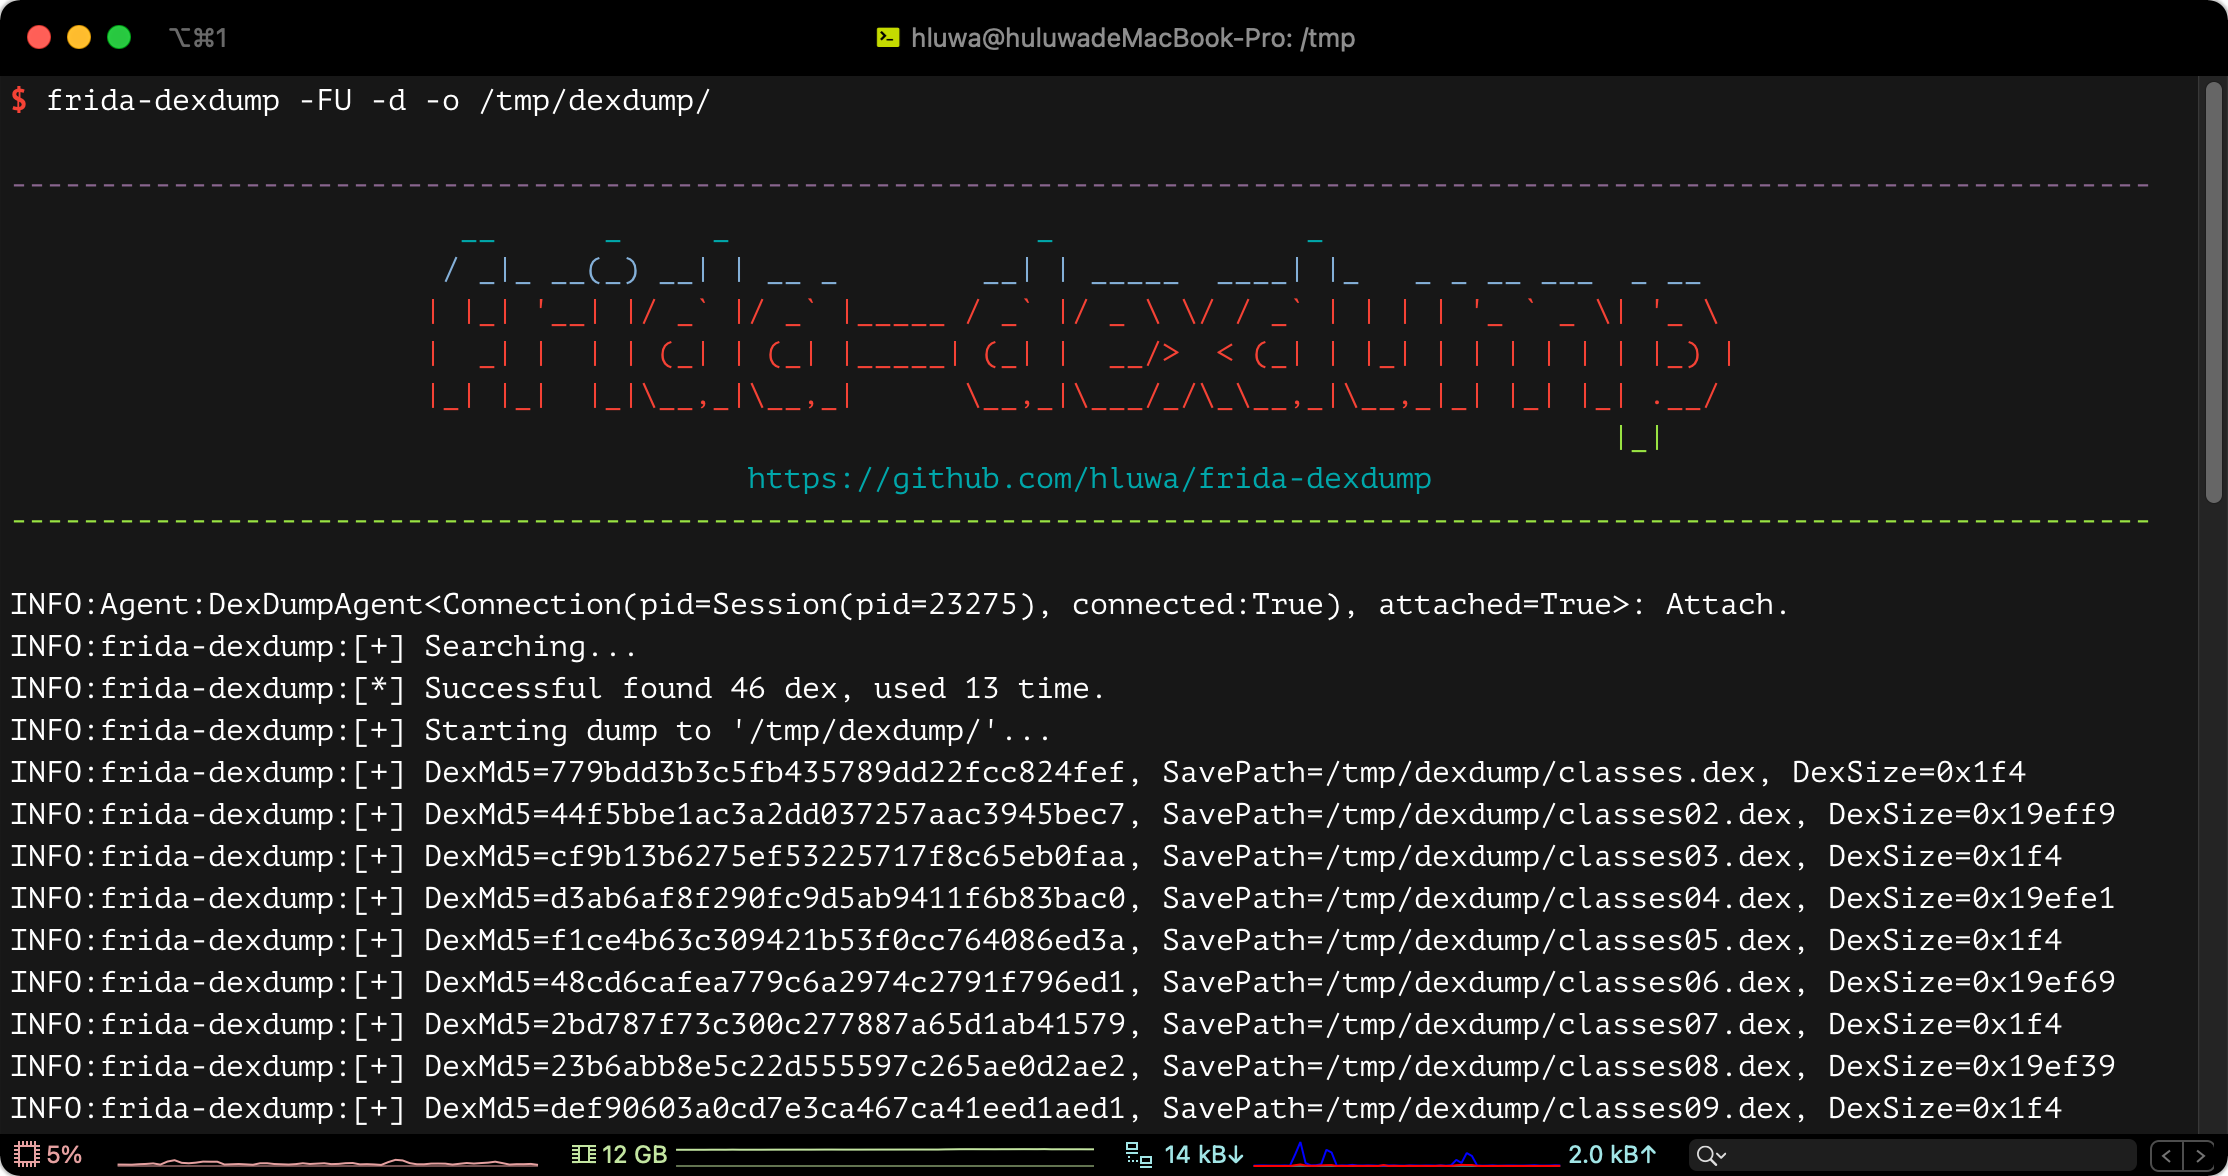 hluwa/frida-dexdump
A frida tool to dump dex in memory to support security engineers analyzing malware.
 ptswarm/reflutter
Flutter Reverse Engineering Framework
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)