
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
258 results
ROPgadget preview

ROPgadget

GitHubjonathansalwan/ropgadget

Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
binary-analysisbinary-exploitationctf+3
4.5k
3 months ago
pharos preview

pharos

GitHubcmu-sei/pharos

Automated static analysis tools for binary programs
binary-analysiseducationmalware-analysis+4
1.7k1 month ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

binary-analysismalware-analysisreverse-engineering+2
1.1k1 month ago
DefenderCheck preview

DefenderCheck

GitHubmatterpreter/defendercheck

Identifies the bytes that Microsoft Defender flags on.

binary-analysisdefensive-toolsmalware-analysis
2.6k3 years ago
yara-x preview

yara-x

GitHubvirustotal/yara-x

A rewrite of YARA in Rust.

binary-analysisdata-recoverydefensive-tools+14
1.3k3h 30m ago
tiny_tracer preview

tiny_tracer

GitHubhasherezade/tiny_tracer

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k4 months ago
AllTools preview

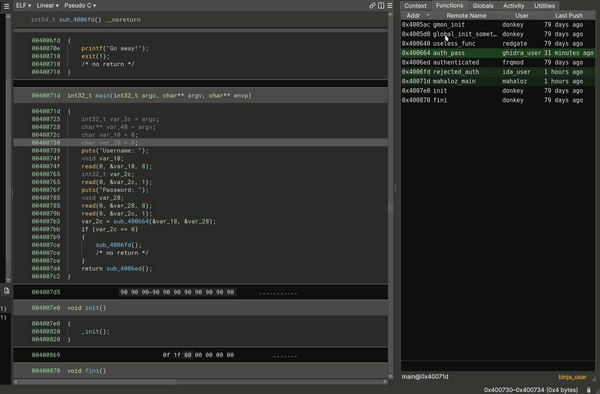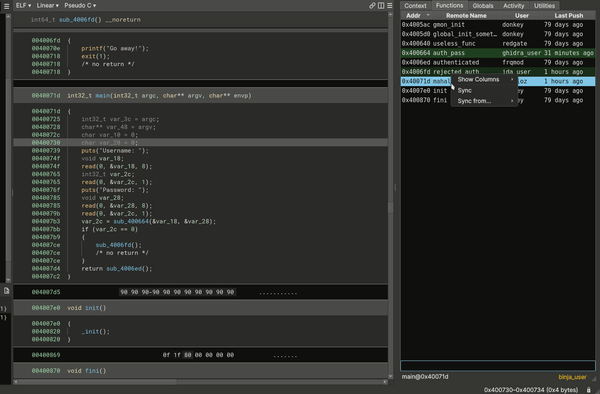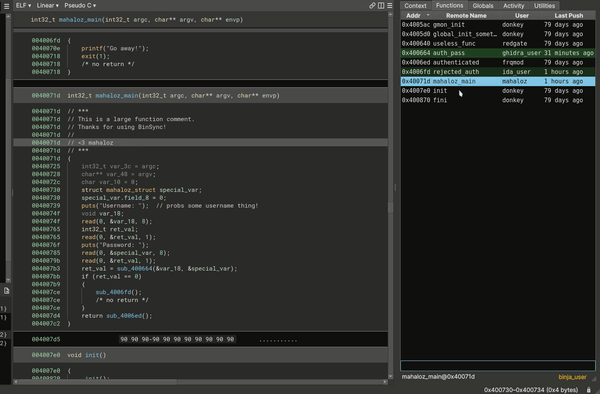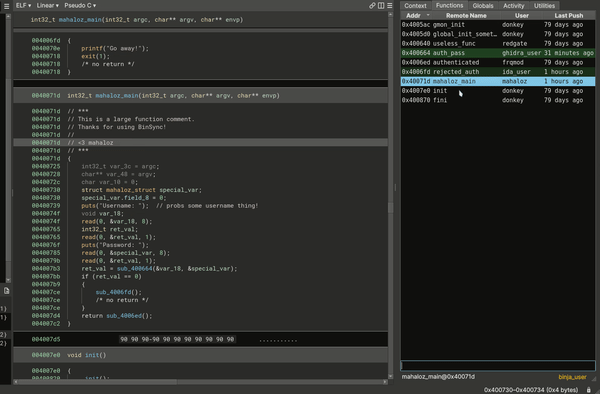
AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.4k3 months ago
binsync preview

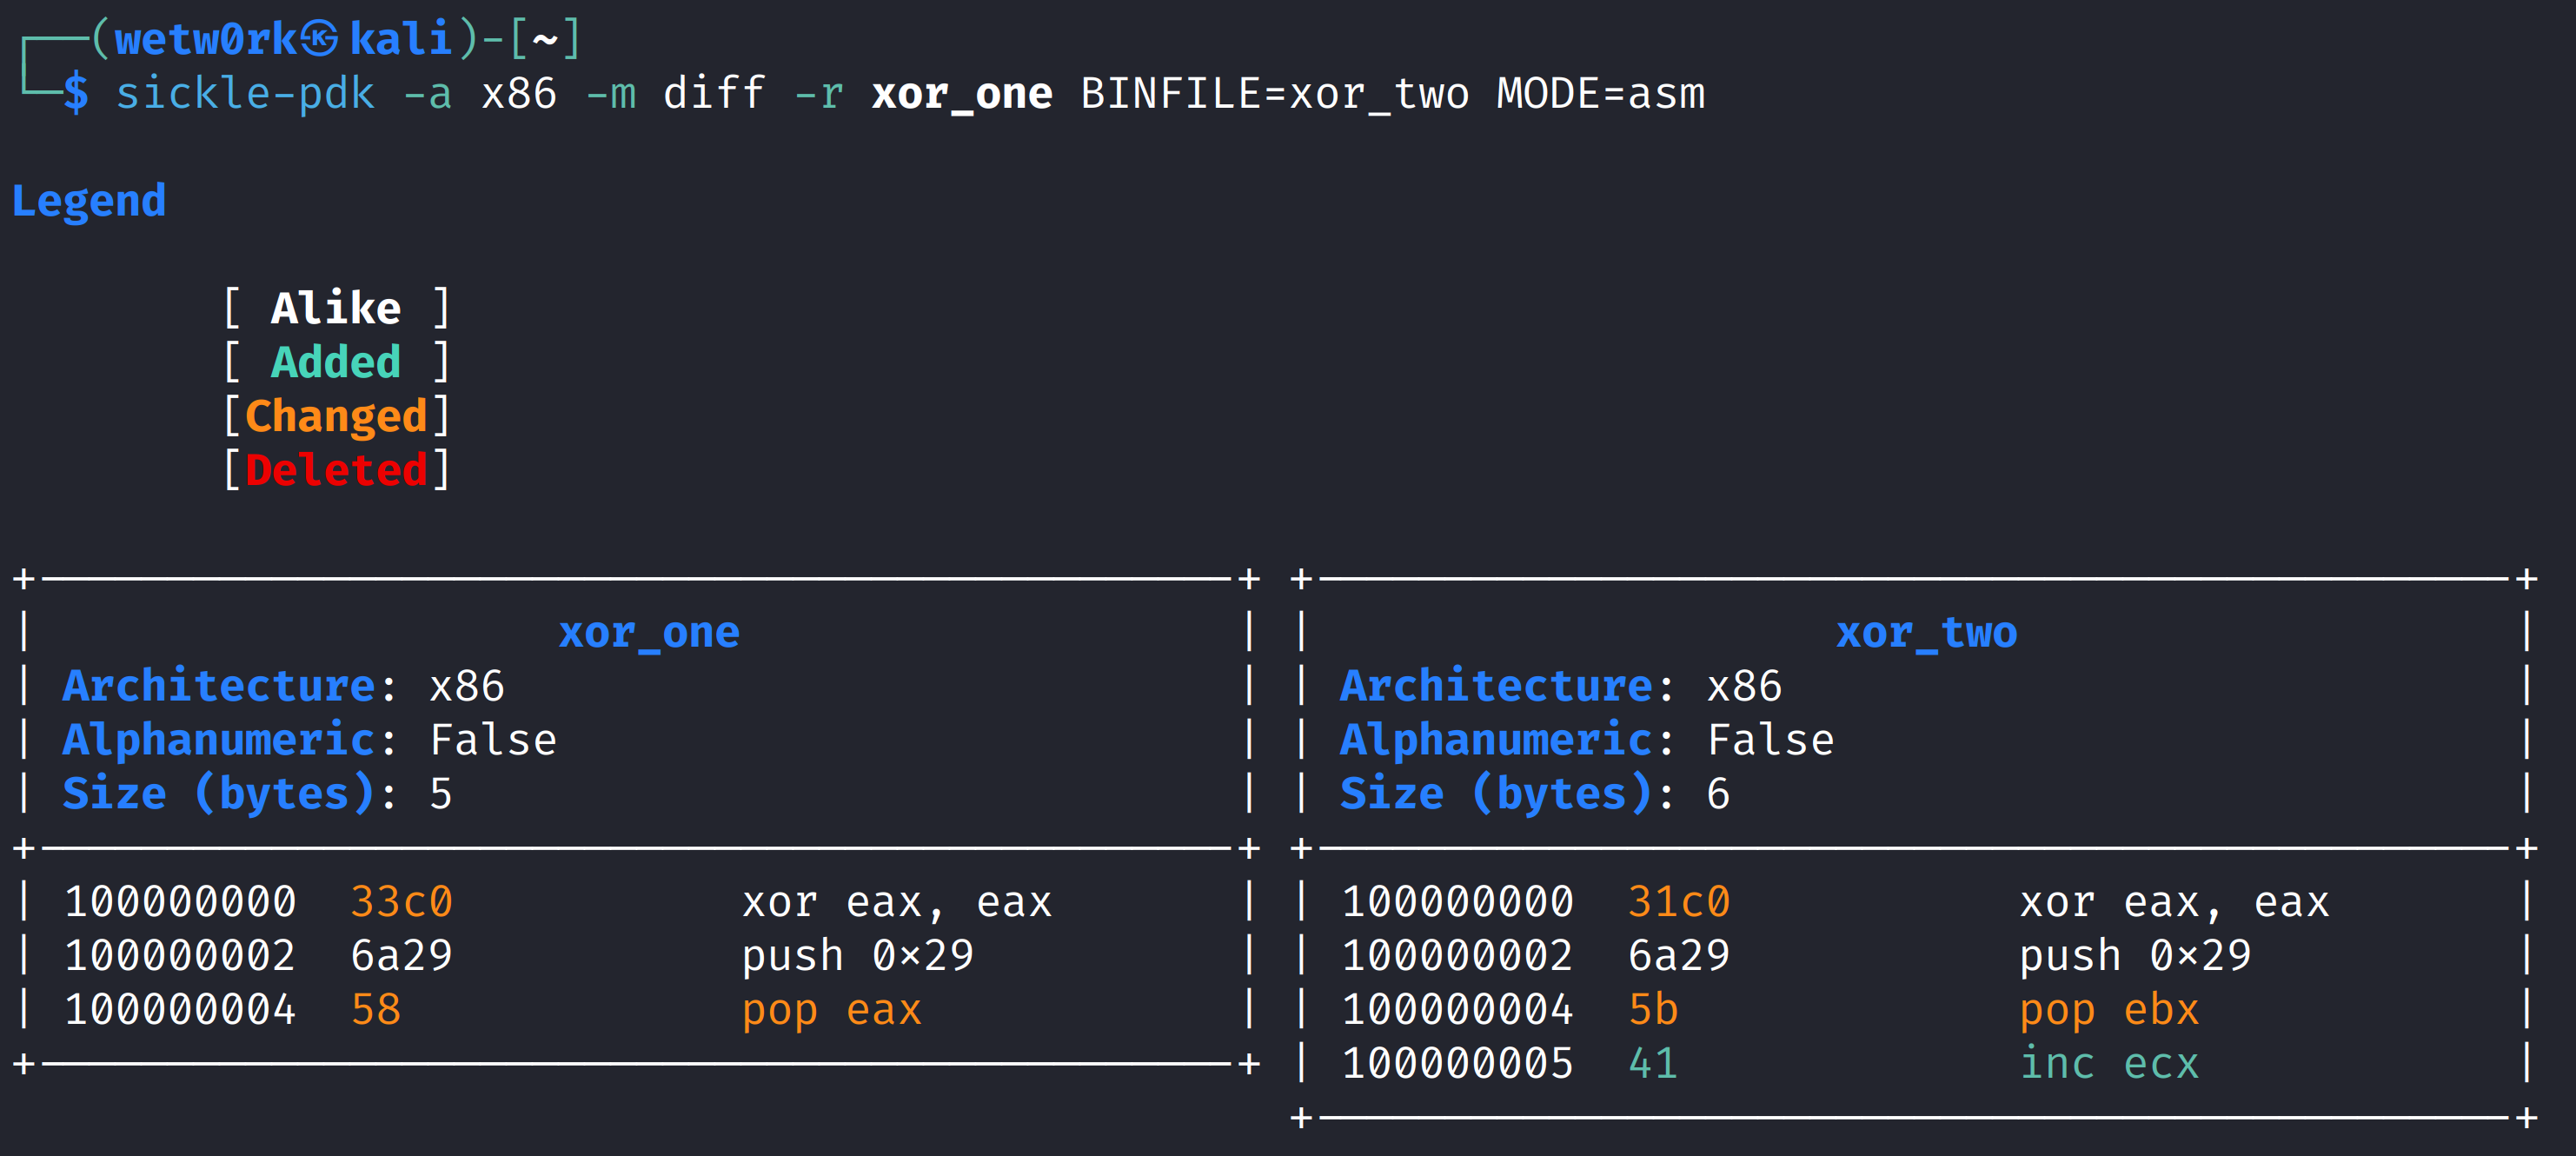
binsync

GitHubbinsync/binsync

A reversing plugin for cross-decompiler collaboration, built on git.
binary-analysisreverse-engineeringstatic-analysis+1
7451 month ago
sickle-pdk preview

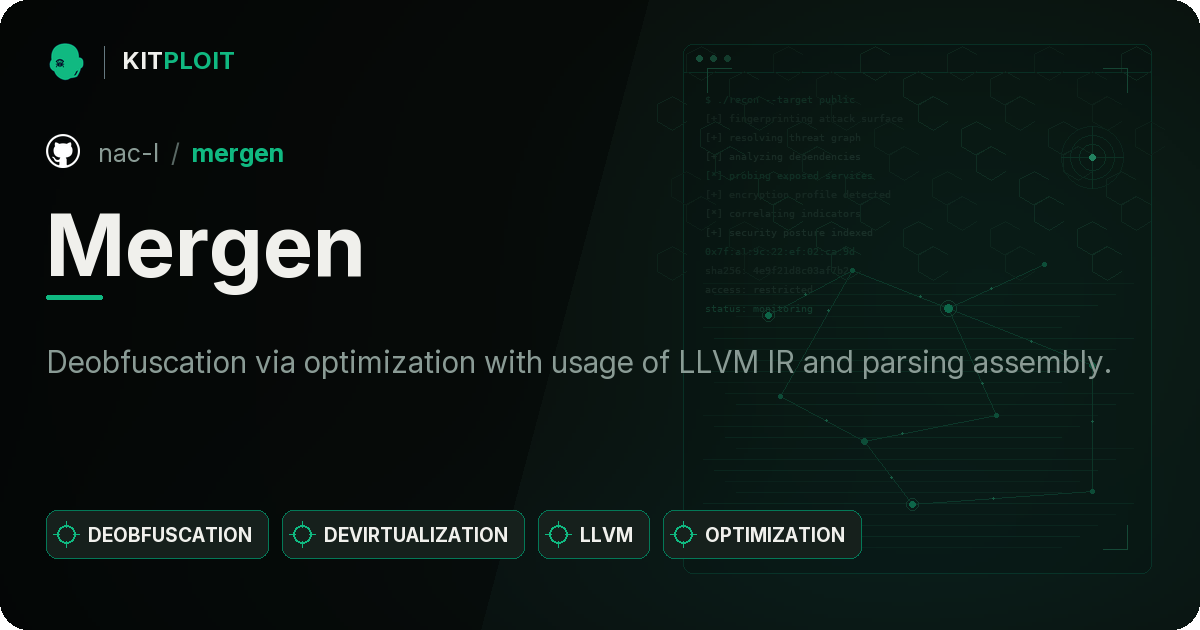
sickle-pdk

GitHubwetw0rk/sickle-pdk

Sickle - Payload Development Kit
binary-analysisexploitationexploit-frameworks+3
8702 months ago
Mergen preview

Mergen

GitHubnac-l/mergen

Deobfuscation via optimization with usage of LLVM IR and parsing assembly.
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+2
9064 months ago
ecdsa-private-key-recovery preview

ecdsa-private-key-recovery

GitHubyadyvazifeh1oz92/ecdsa-private-key-recovery

Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…
binary-analysiscryptographyeducation+1
52111 days ago
CallObfuscator preview

CallObfuscator

GitHubd35ha/callobfuscator

Obfuscate specific windows apis with different apis

binary-analysisdefensive-toolsdynamic-analysis-sandboxing+4
1.0k5 years ago
Introspy-iOS preview

Introspy-iOS

GitHubisecpartners/introspy-ios

Security profiling for blackbox iOS
binary-analysisdebuggersdynamic-analysis-sandboxing+5
7409 years ago
awesome-rust-security preview

awesome-rust-security

GitHubosirislab/awesome-rust-security

Curated list of awesome projects and resources related to Rust and computer security
binary-analysiscloud-securitycryptography+9
6082 years ago
shellen preview

shellen

GitHubkonatabrk/shellen

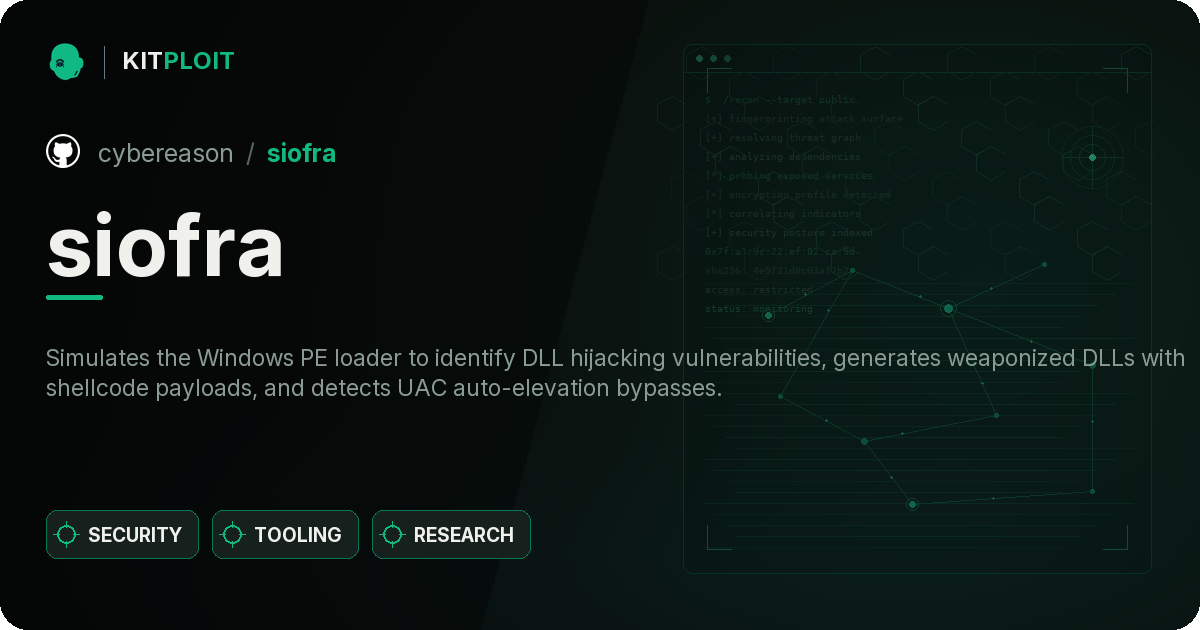
:cherry_blossom: Interactive shellcoding environment to easily craft shellcodes
binary-analysisctfeducation+5
9085 years ago
siofra preview

siofra

GitHubcybereason/siofra

Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
binary-analysisbinary-exploitationpayload-generation+4
5138 years ago
pe-bear-old preview

pe-bear-old

GitHubhasherezade/pe-bear-old

PE-bear (builds only)

binary-analysismalware-analysisreverse-engineering
7763 years ago
Previous1…8910…15Next