

CVE-2024-20154
 harbingerse7en/cve-2024-20154
Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…
binary-analysiseducationembedded-systems-security+8
harbingerse7en/cve-2024-20154Technical writeup analyzing CVE-2024-20154, a stack-based buffer overflow in MediaTek MT6769 NB-IoT baseband firmware, covering reverse engineering…

 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 owenpawl/cerberus-re-skill
cerberus-re is a local Apple-focused reverse-engineering workbench for building a repeatable three-headed static/dynamic/instrumentation loop around…
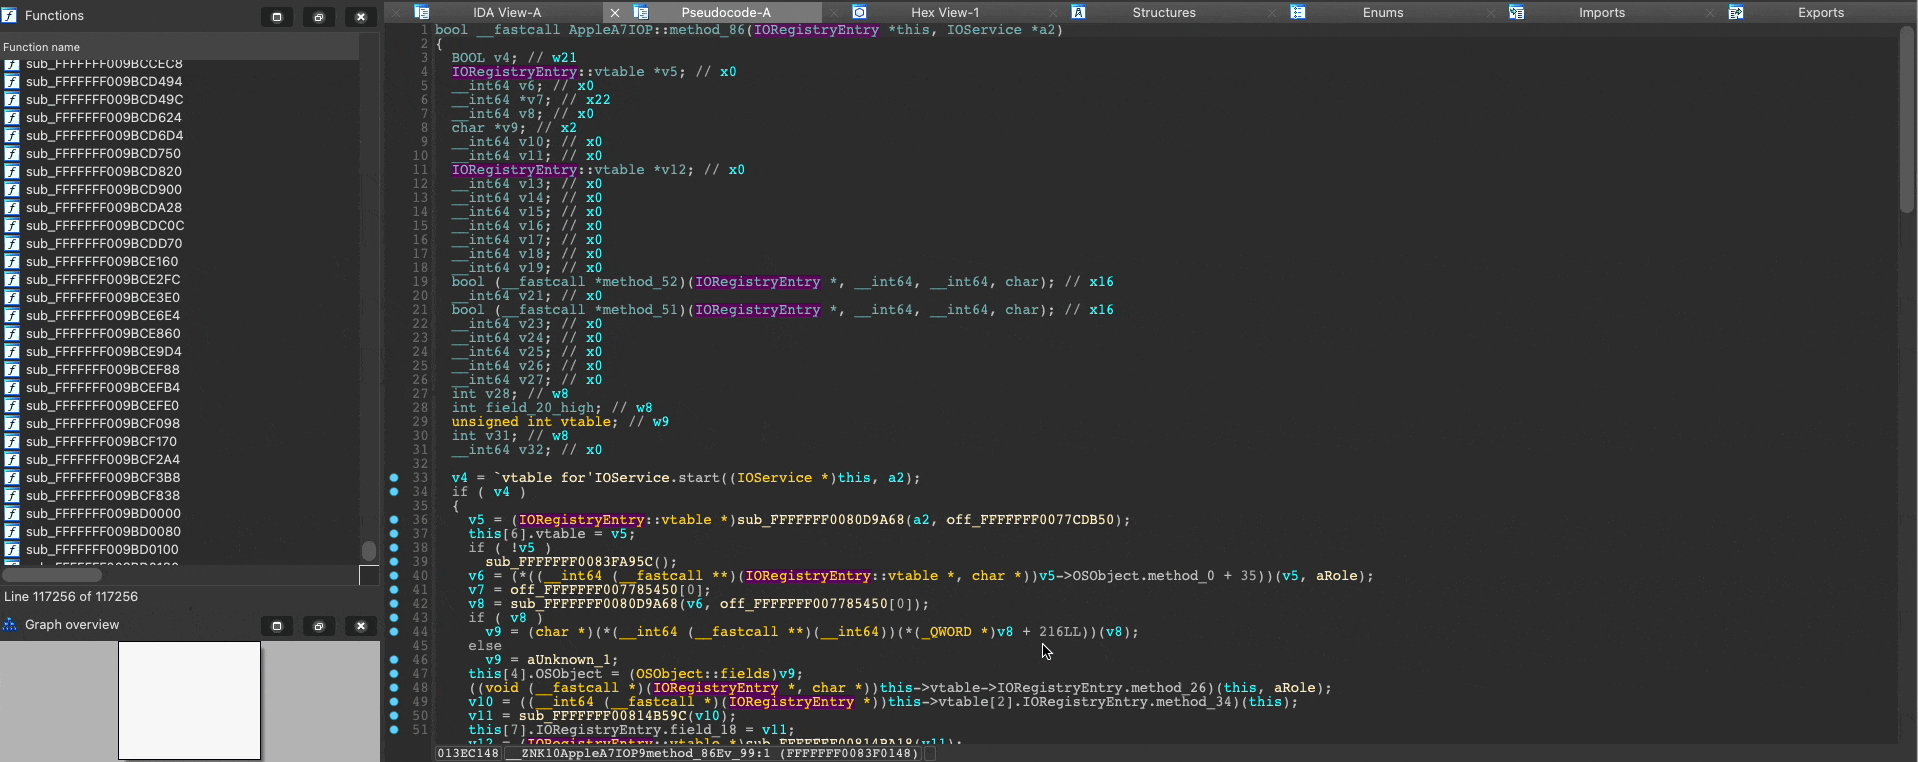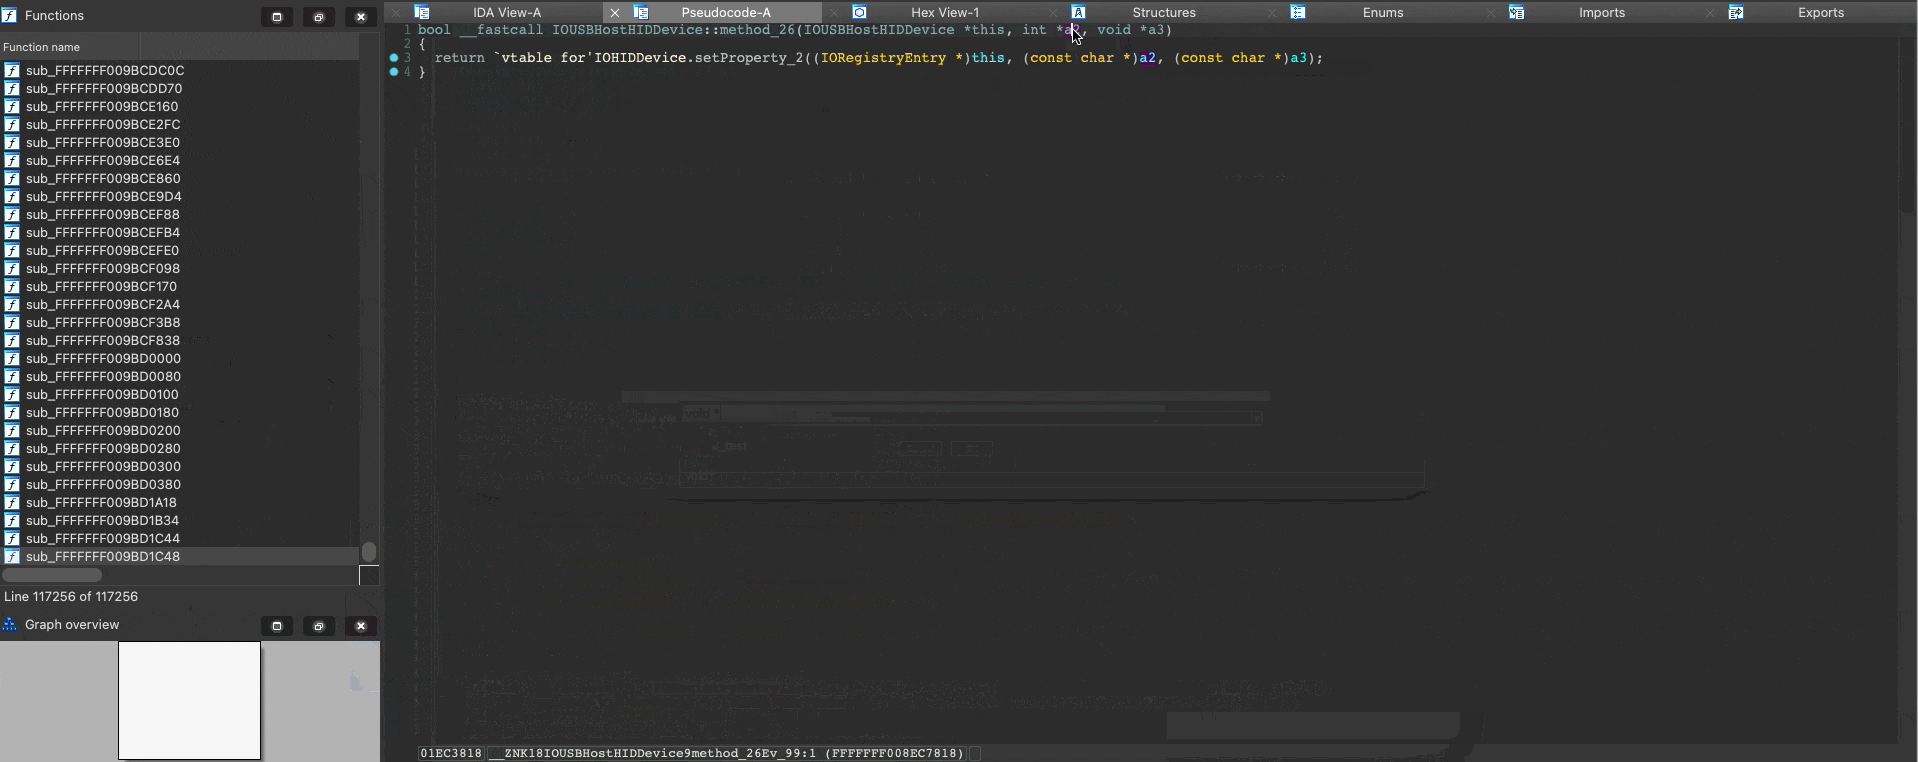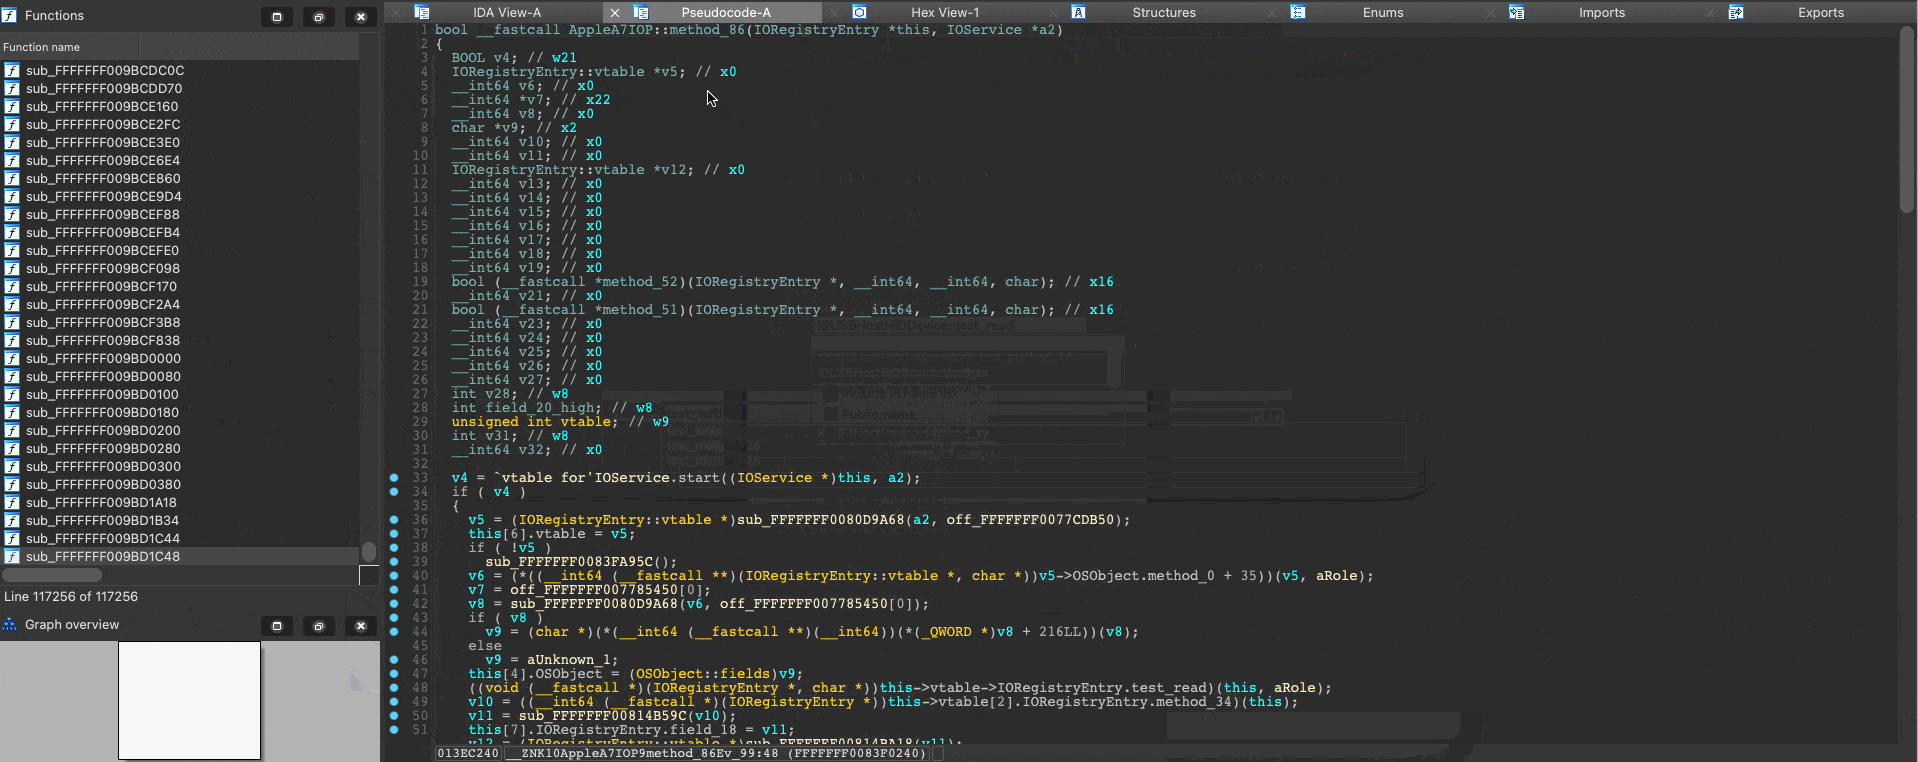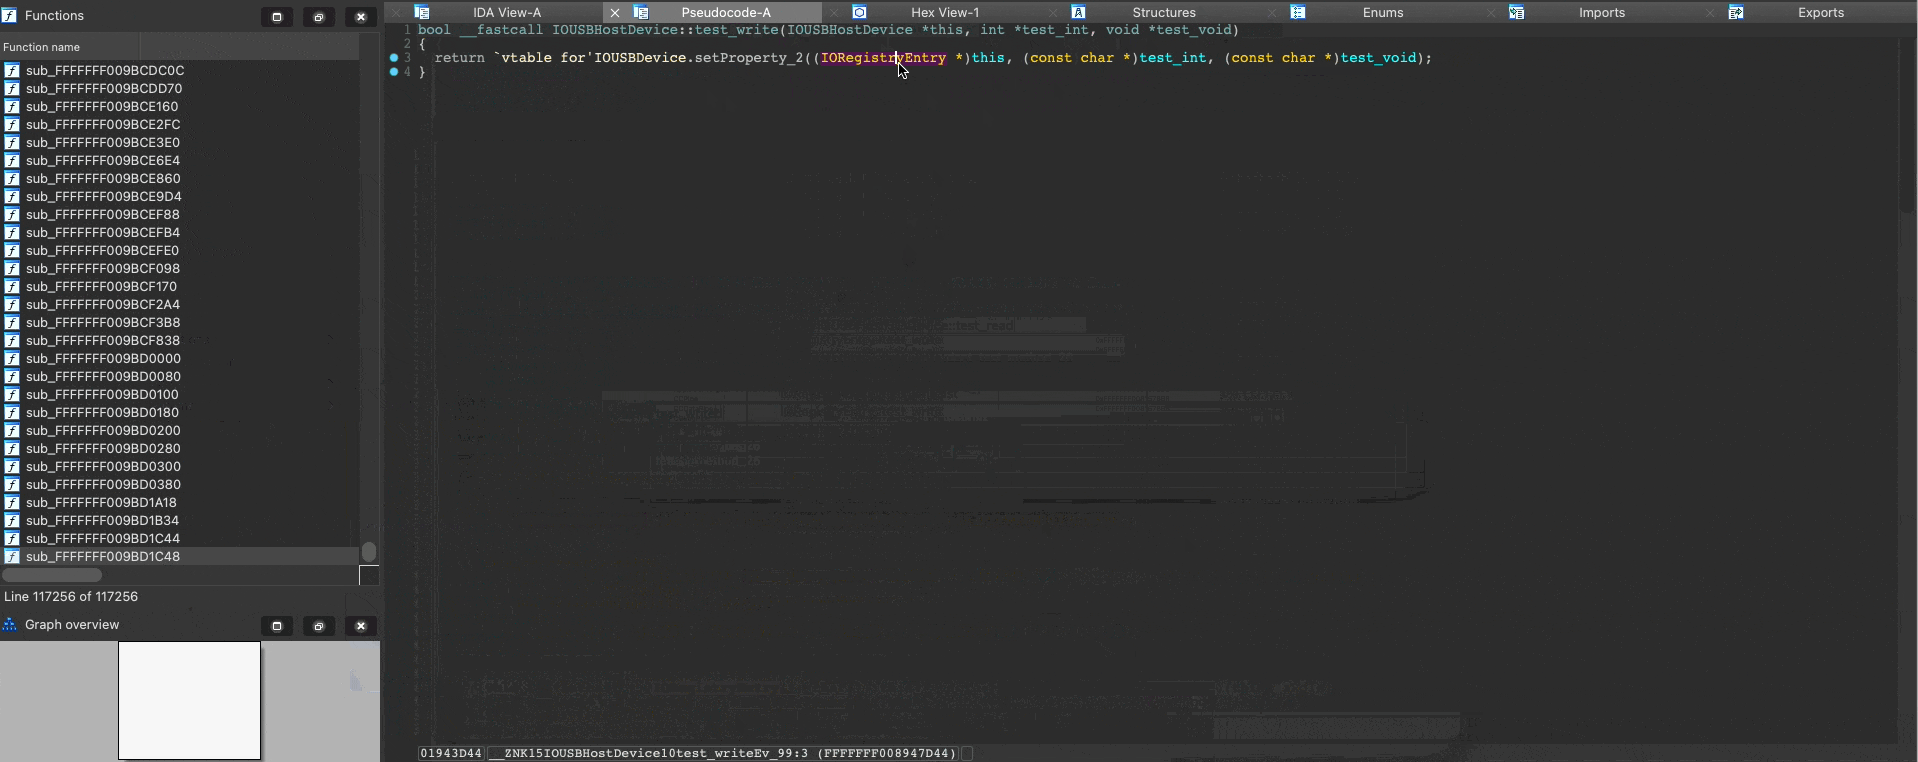 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
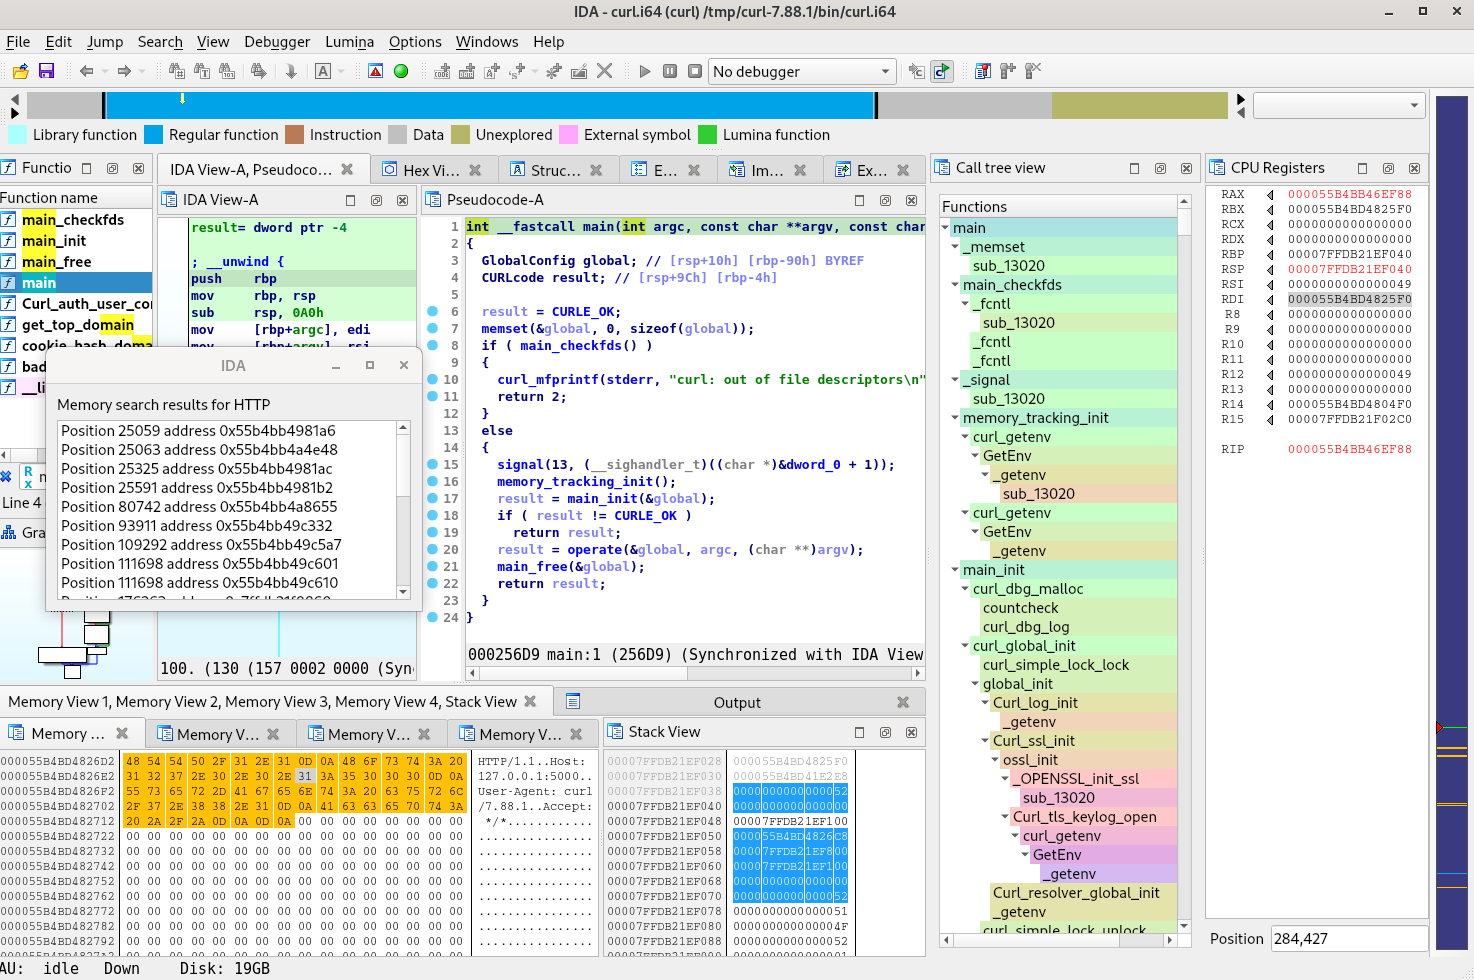 synacktiv/frinet
Frida-based tracer for easier reverse-engineering on Android, iOS, Linux, Windows and most related architectures.
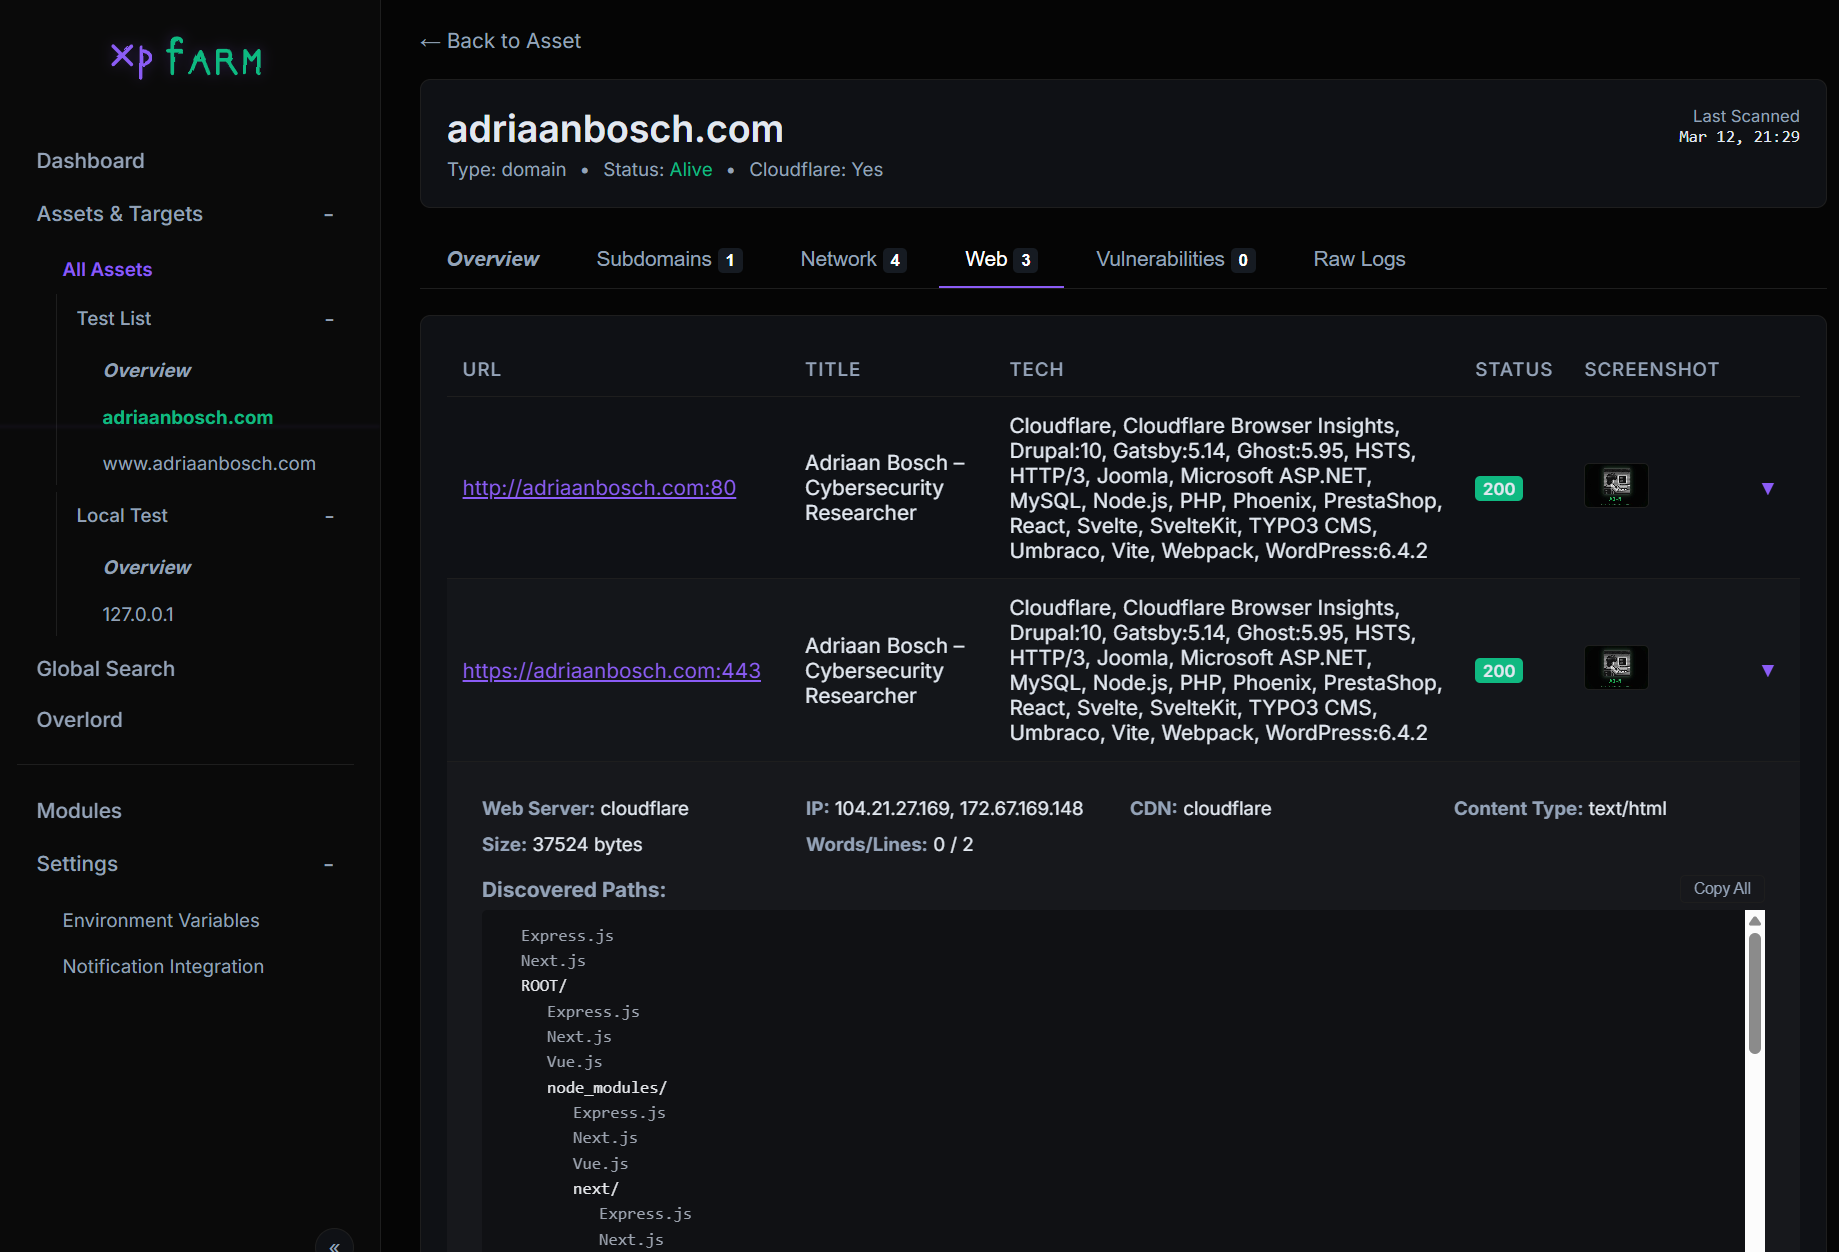 a3-n/xpfarm
Free XP on bug bounty, vulnerability scanning by wrapping well maintained tools, to perform automated tests. Alongside AI agents for binary analysis,…
 abrarkhan/external_sonivox_cve-2024-23709
Proof-of-concept for CVE-2024-23709, an out-of-bounds write vulnerability in Android's Sonivox audio synthesis library, demonstrating exploitation on…
 renukaselvar/system_bt_aosp10_cve-2022-20140
Android Bluetooth stack (Fluoride) with a proof-of-concept for CVE-2022-20140, demonstrating a Bluetooth vulnerability and providing build…
 pazhanivelmani/libexif_android10_r33_cve-2016-6328
C-based library for parsing, editing, and saving EXIF metadata from JPEG images, with a focus on exploiting CVE-2016-6328 for Android 10.
 pazhanivelmani/webp_android10_r33_cve-2023-1999
Proof-of-concept exploit for CVE-2023-1999 targeting the WebP codec library on Android 10 (r33). Demonstrates a heap buffer overflow vulnerability in…
 trinadh465/external_aac_aosp10_r33_cve-2023-21282
Analyzes and patches a specific Android vulnerability (CVE-2023-21282) in the AAC audio codec, providing a patched AOSP10 source tree for security…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
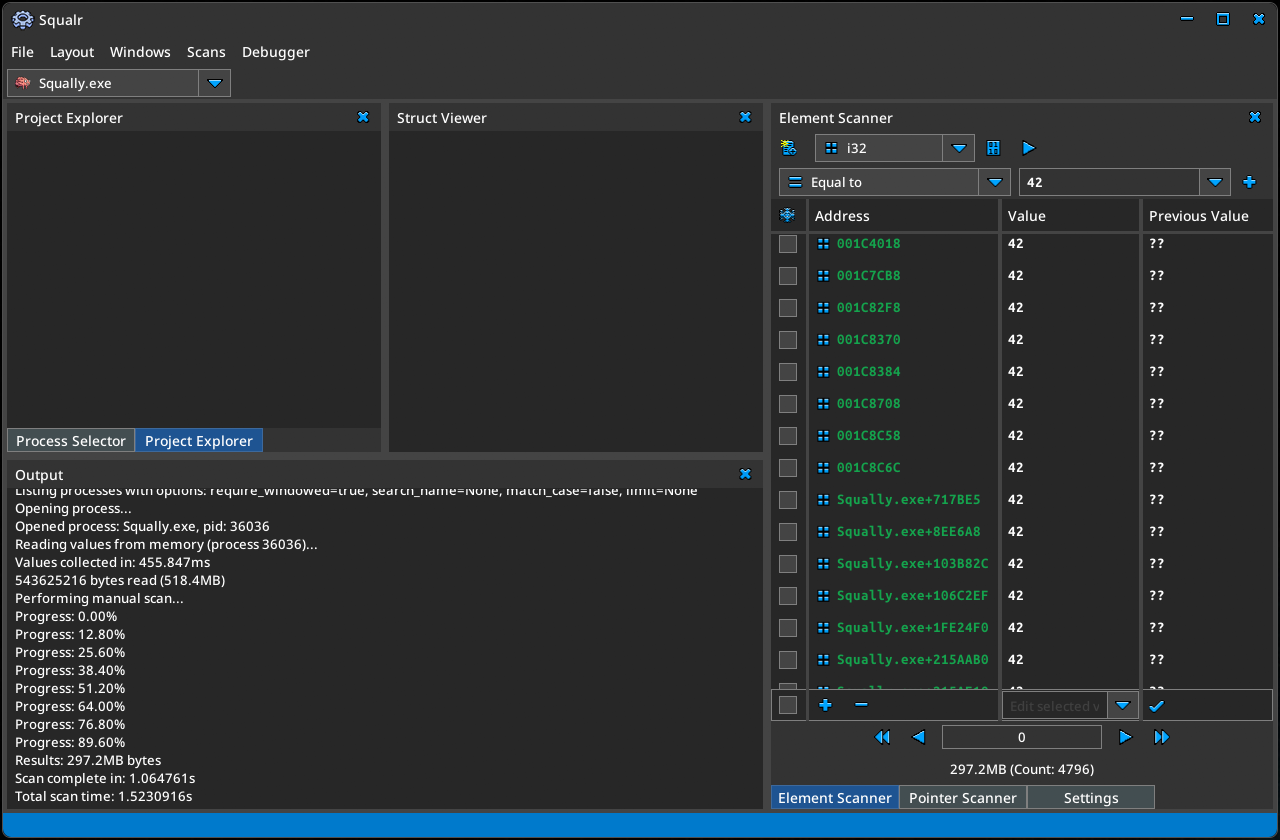 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
 vichhka-git/universal-flutter-ssl-pinning
Automated SSL pinning bypass for any Flutter & Shorebird version — PyGhidra static analysis auto-discovers BoringSSL and generates ready-to-run Frida…