
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1424 results
pwn-hisilicon-dvr preview

pwn-hisilicon-dvr

GitHubtothi/pwn-hisilicon-dvr

Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
binary-analysisembedded-systems-securityexploitation+8
384
3 years ago
iblessing preview

iblessing

GitHubsoulghost/iblessing

iblessing is an iOS security exploiting toolkit, it mainly includes application information gathering, static analysis and dynamic analysis. It can…
binary-analysisdynamic-analysis-sandboxingexploitation+5
6874 years ago
idasql preview

idasql

GitHuballthingsida/idasql

Vibe Reverse Engineer with IDA Pro: An interface for IDA in SQL via live virtual tables. Don't let appearances deceive you! :)
ai-assisted-reversingbinary-analysisdebuggers+4
4242 days ago
ane preview

ane

GitHubeiln/ane

Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
ai-securitybinary-analysisembedded-systems-security+3
5382 years ago
applepie preview

applepie

GitHubgamozolabs/applepie

A hypervisor for fuzzing built with WHVP and Bochs
binary-analysisdynamic-analysis-sandboxingfuzzing+2
3857 years ago
antidbg preview

antidbg

GitHubnotrequiem/antidbg

A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
anti-botbinary-analysisdefensive-tools+4
33820 days ago
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

A multi-platform GUI for bit-based analysis, processing, and visualization
binary-analysisdata-recoveryforensics+1
7541 year ago
View8 preview

View8

GitHubsuleram/view8

Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
binary-analysismalware-analysisreverse-engineering+2
3812 months ago
metame preview

metame

GitHuba0rtega/metame

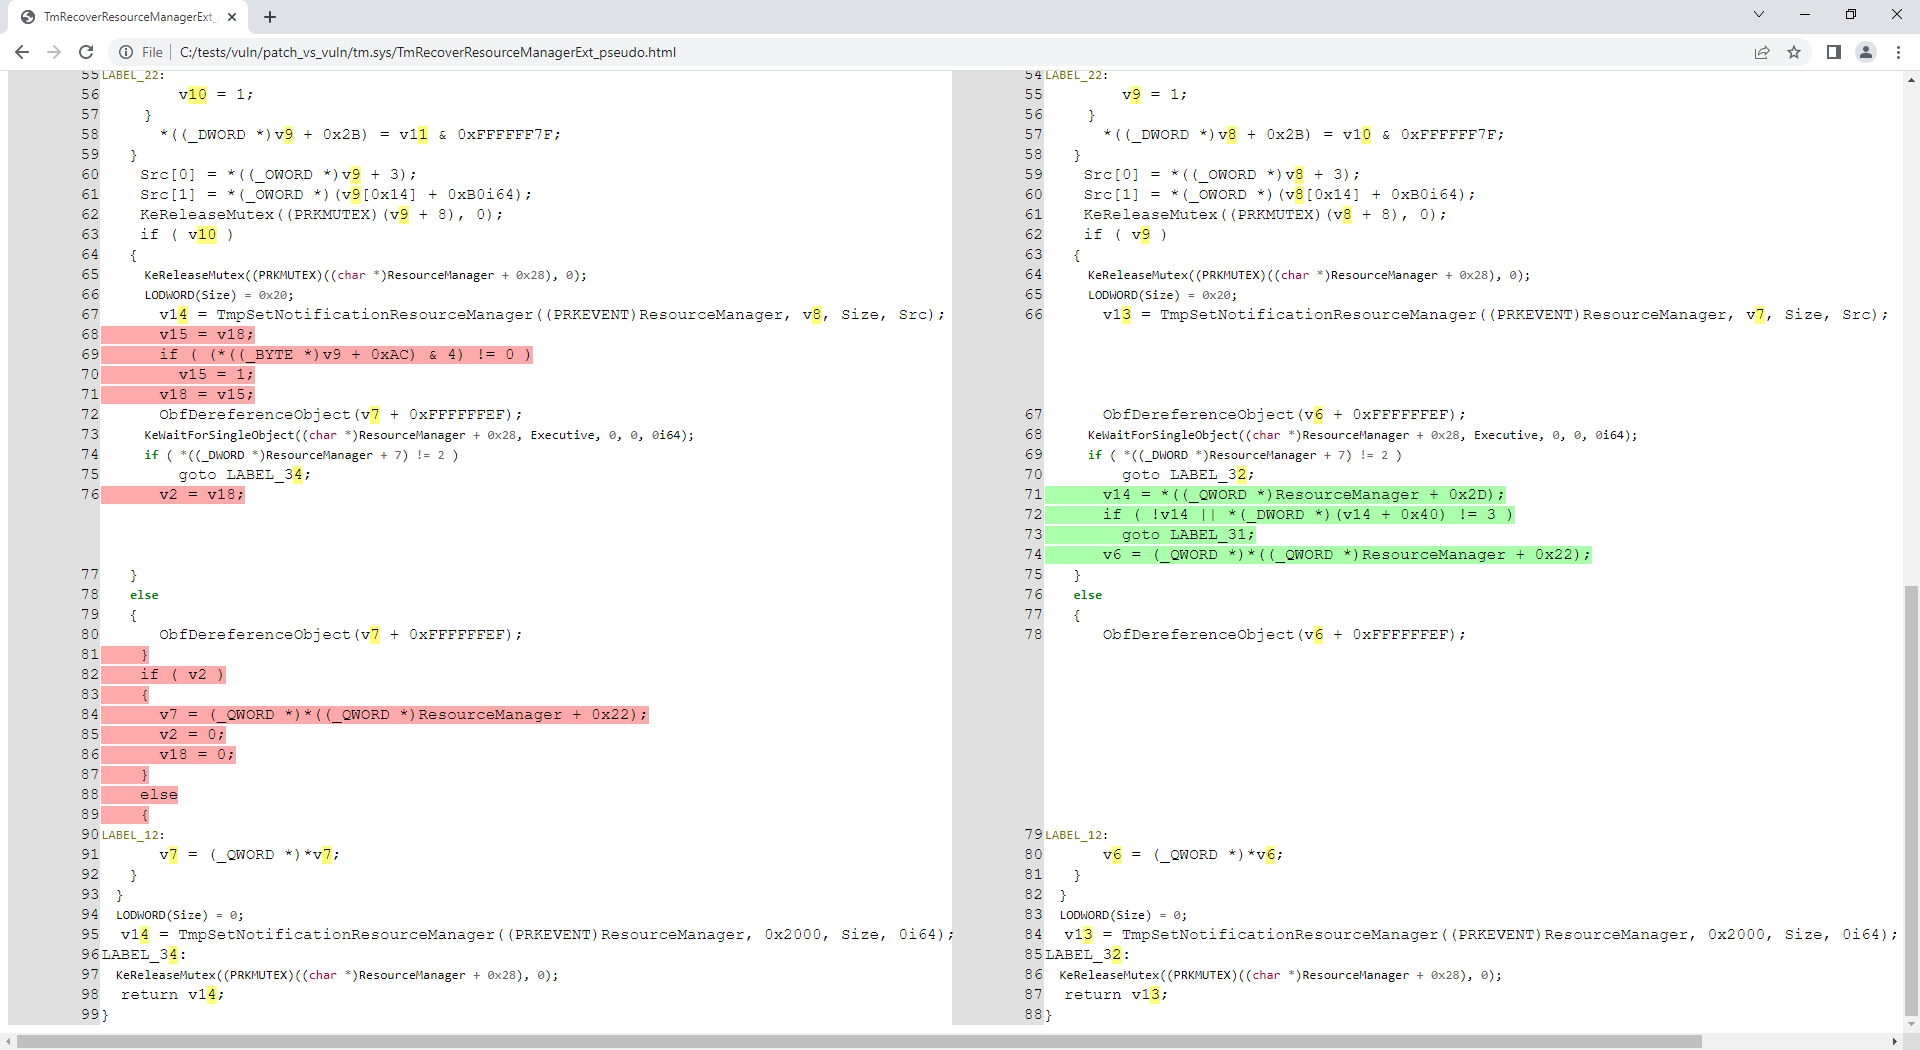
metame is a metamorphic code engine for arbitrary executables
binary-analysisbinary-exploitationmalware-analysis+2
6057 years ago
idahunt preview

idahunt

GitHubnccgroup/idahunt

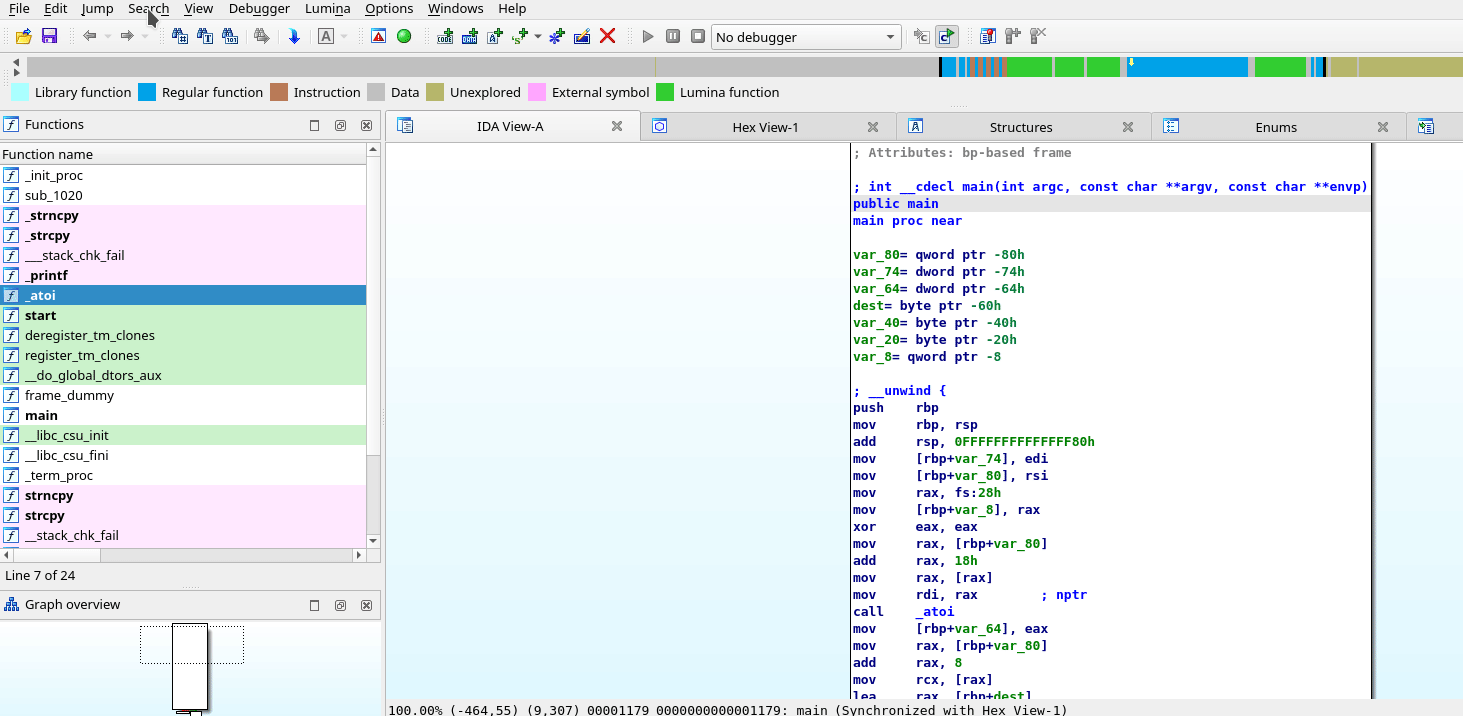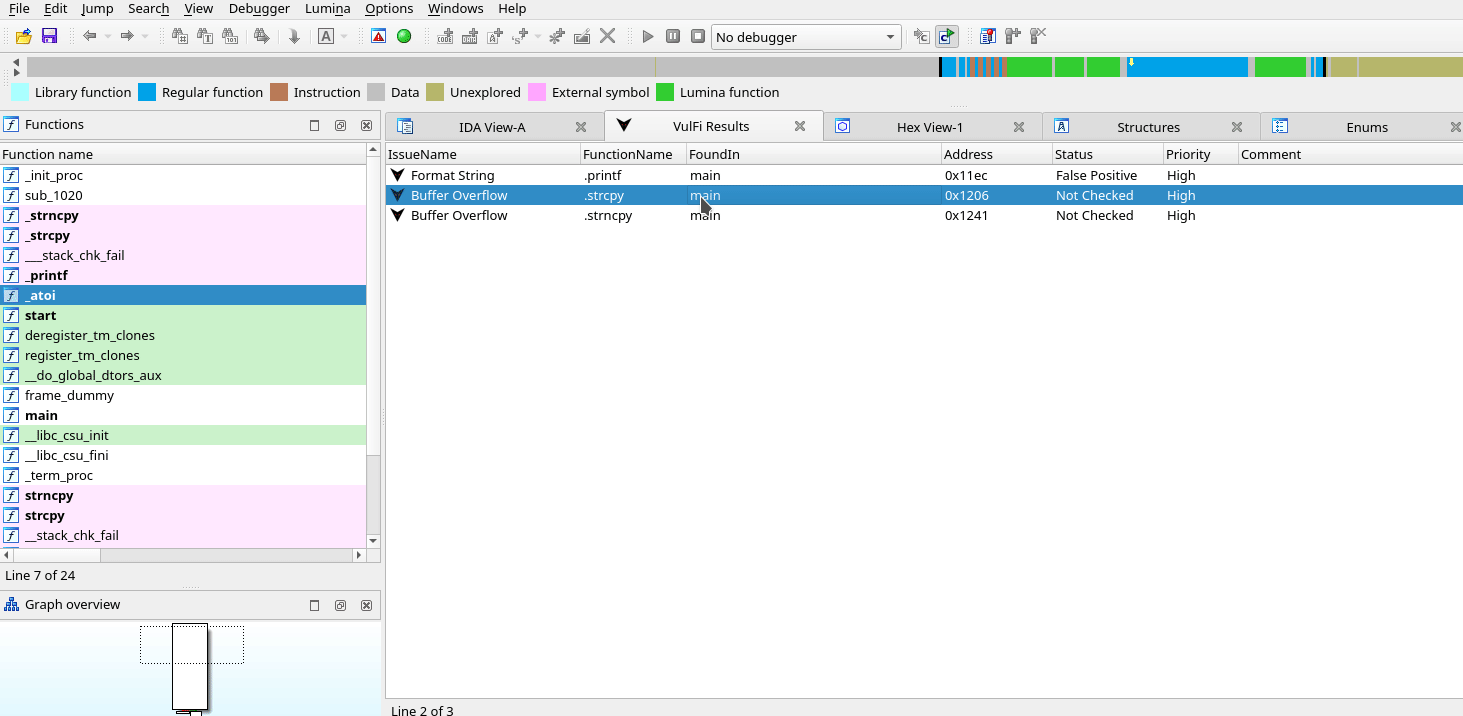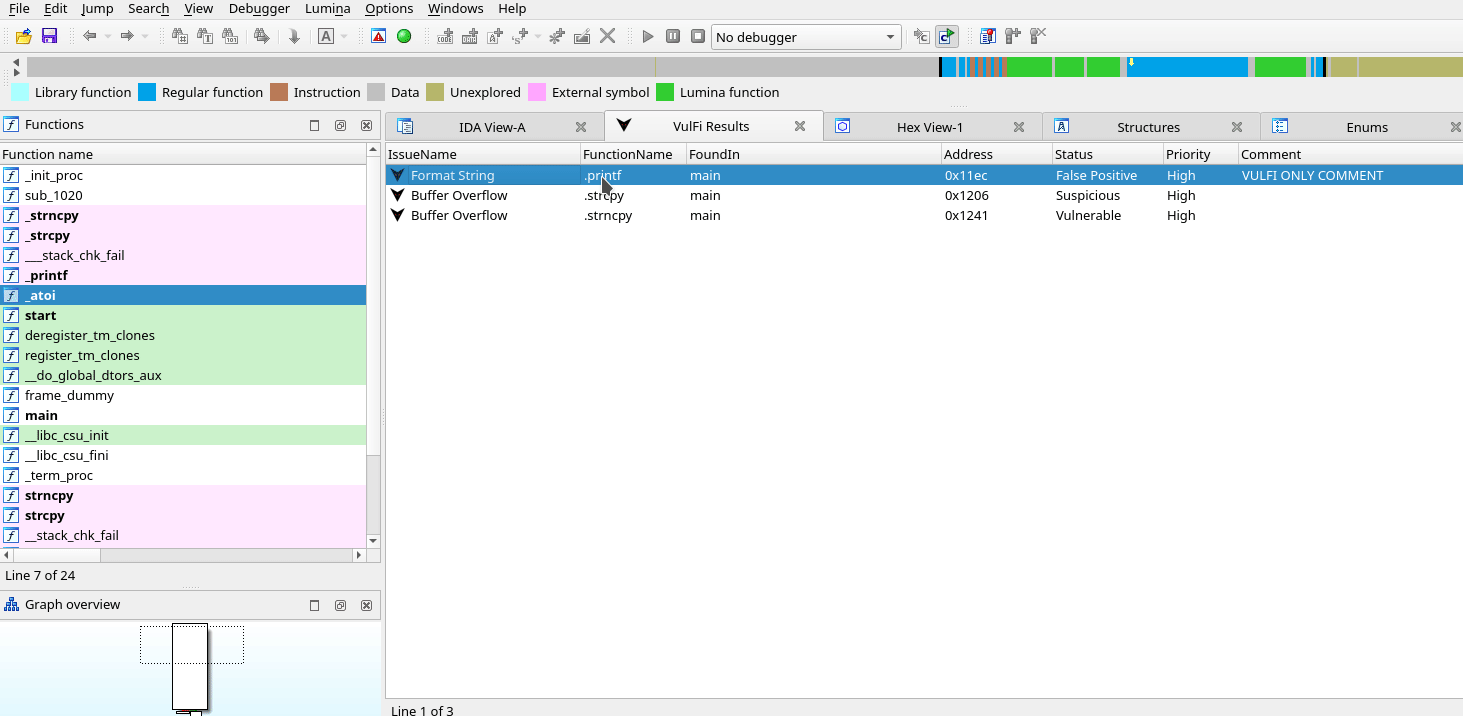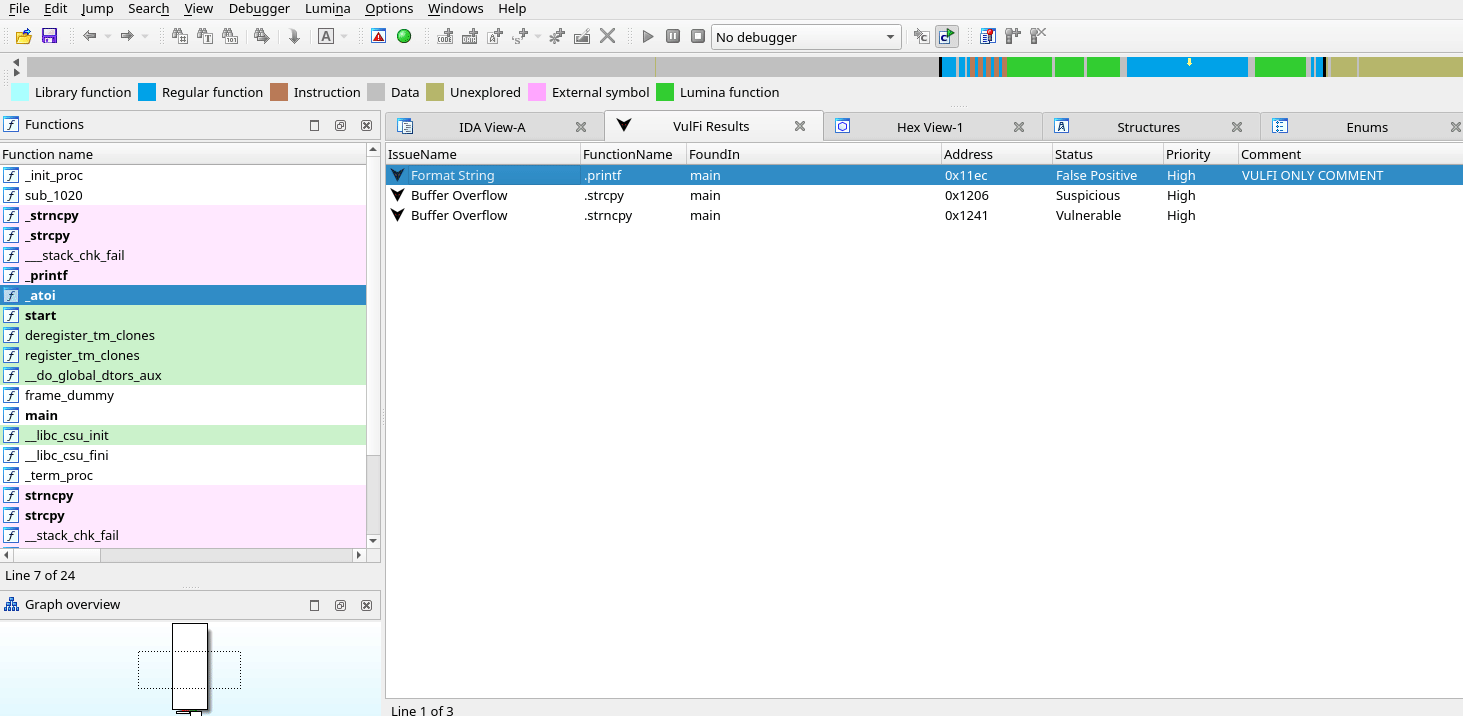
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
binary-analysisembedded-systems-securityfirmware-analysis+4
3943 years ago
VulFi preview

VulFi

GitHubaccenture/vulfi

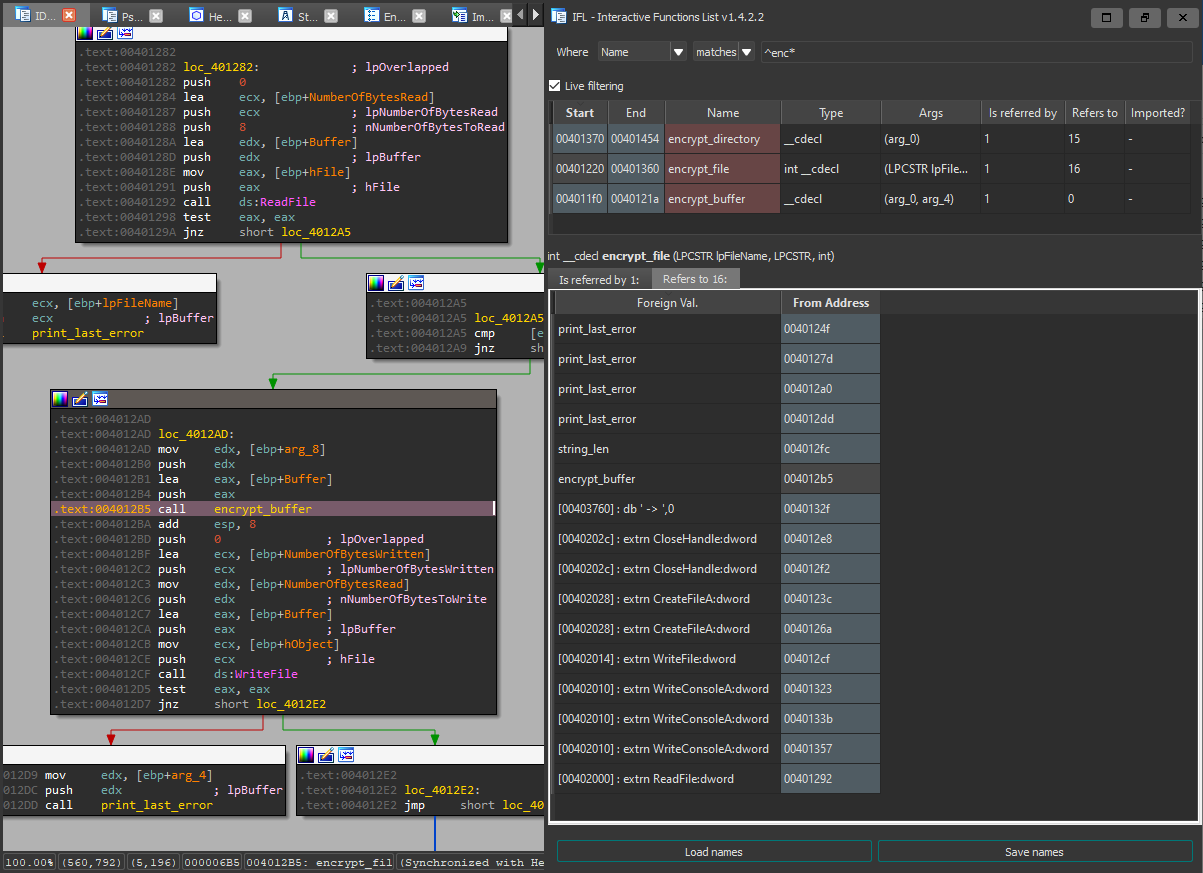
IDA Pro plugin for query based searching within the binary useful mainly for vulnerability research.
binary-analysisreverse-engineeringstatic-analysis+1
6711 year ago
ida_ifl preview

ida_ifl

GitHubhasherezade/ida_ifl

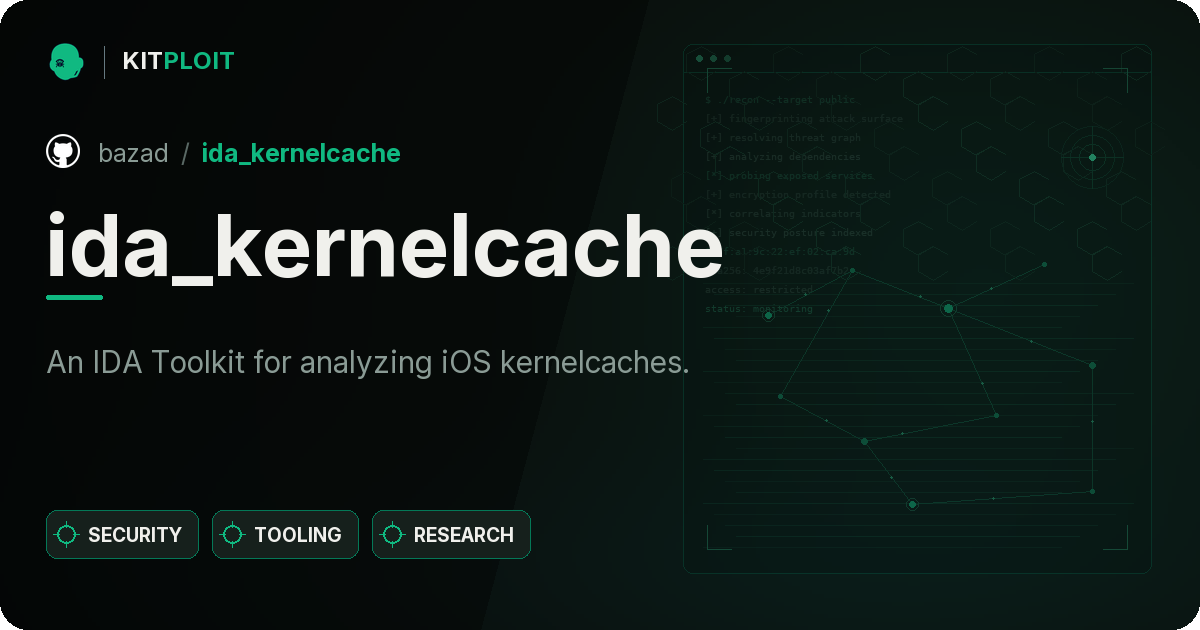
IFL - Interactive Functions List (plugin for IDA Pro)
binary-analysiscode-analysismalware-analysis+2
5013 months ago
ida_kernelcache preview

ida_kernelcache

GitHubbazad/ida_kernelcache

An IDA Toolkit for analyzing iOS kernelcaches.
binary-analysisdebuggersembedded-systems-security+6
3057 years ago
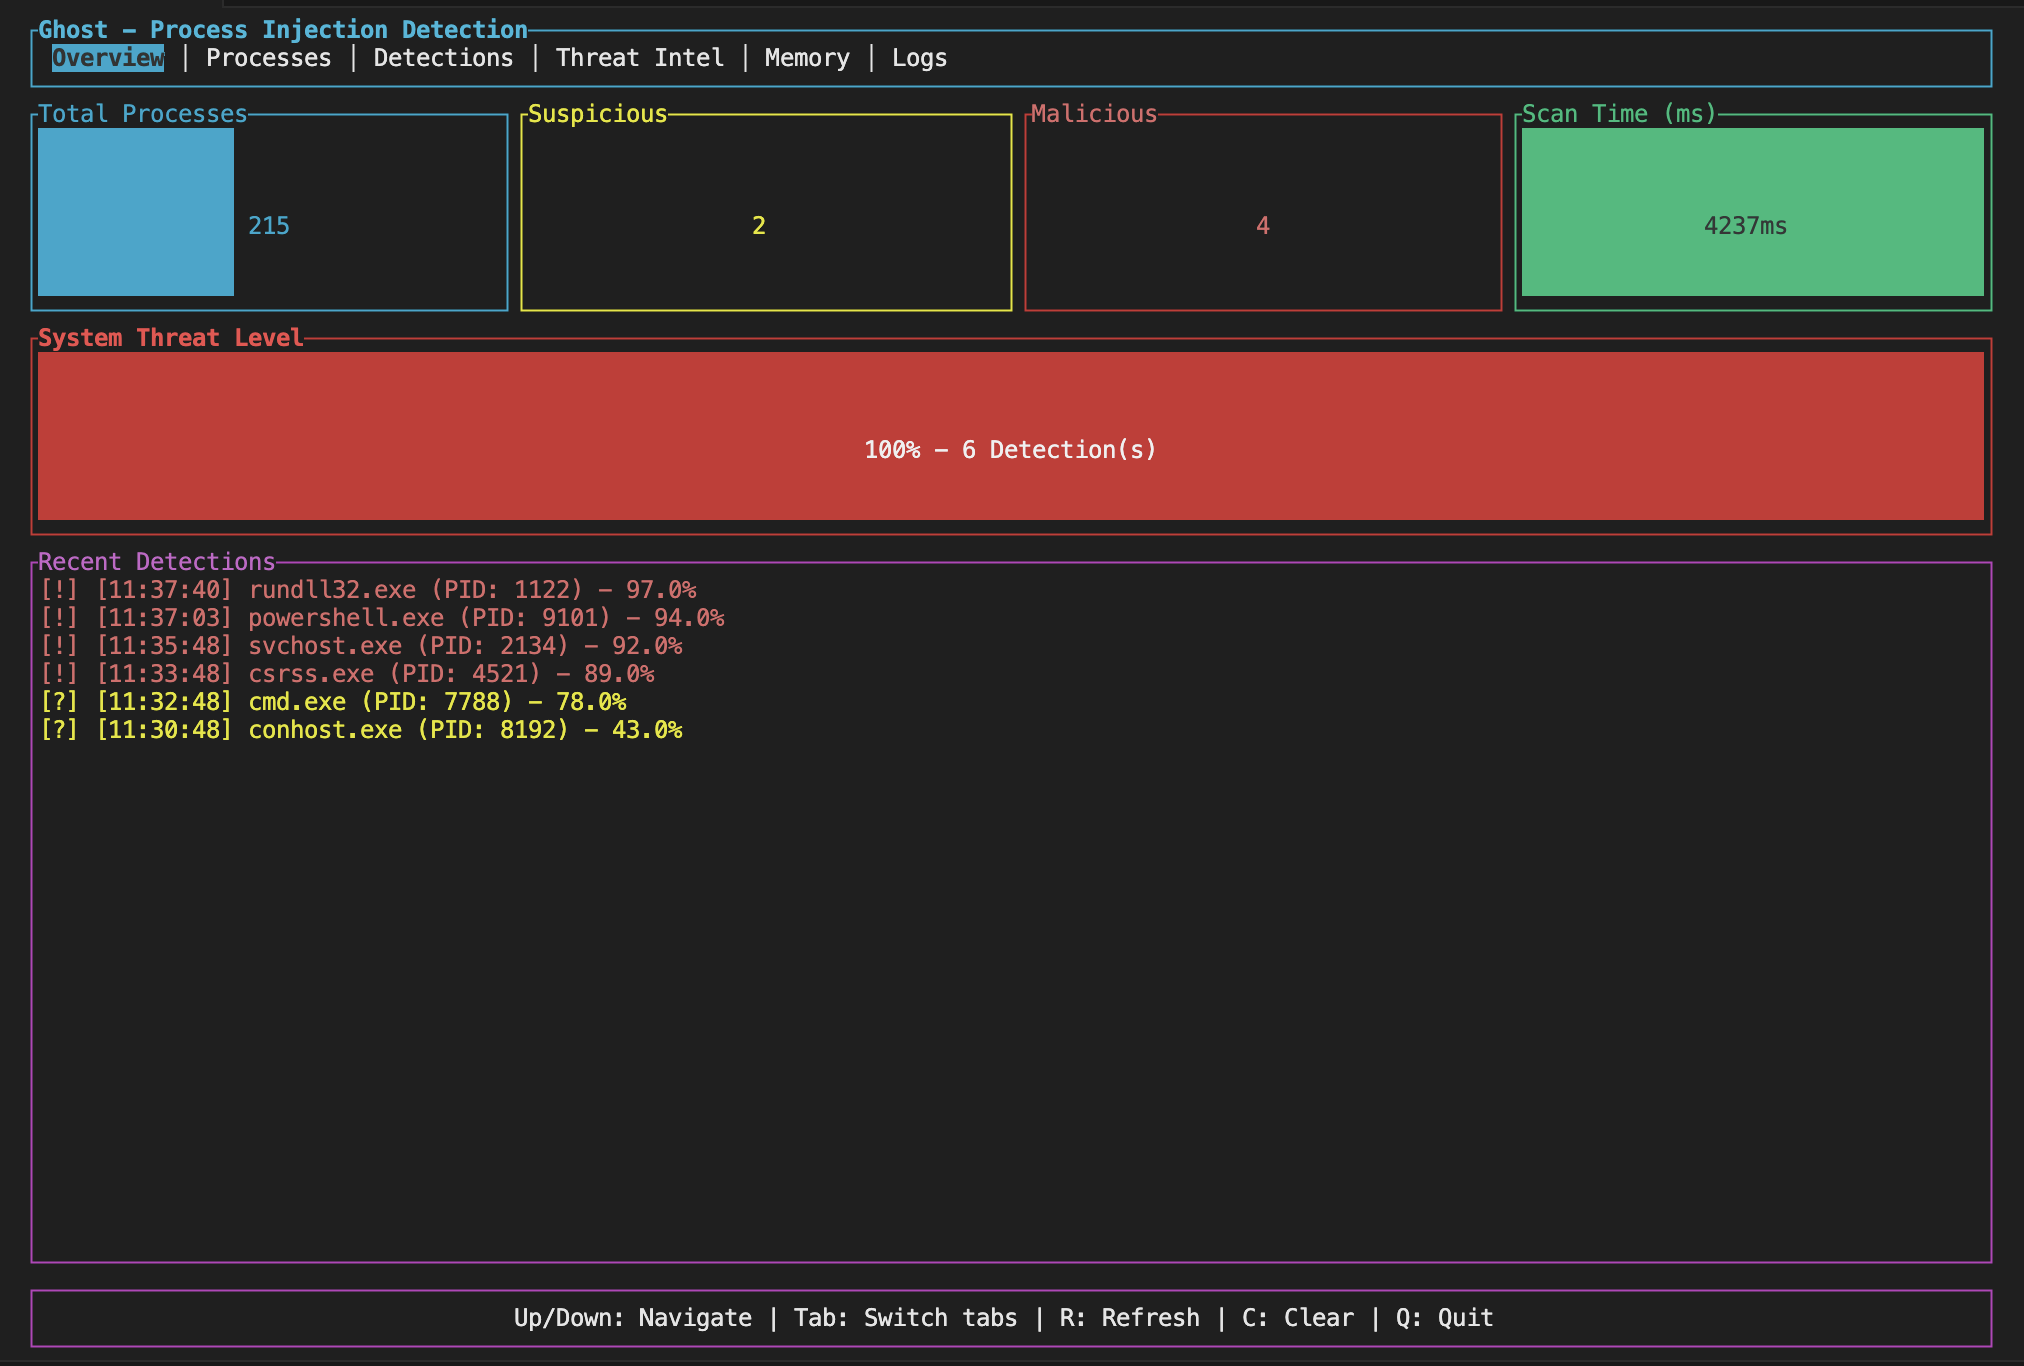
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
binary-analysisdefensive-toolsforensics+6
3902 months ago
CVE-2022-0778 preview

CVE-2022-0778

GitHubdrago-96/cve-2022-0778

Proof-of-concept exploit for CVE-2022-0778, demonstrating an infinite loop in OpenSSL's BN_mod_sqrt via a crafted X.509 certificate with non-prime…
binary-analysiscryptographyeducation+3
1814 years ago
Macrome preview

Macrome

GitHubmichaelweber/macrome

Excel Macro Document Reader/Writer for Red Teamers & Analysts

binary-analysisexploitationmalware-analysis+5
5225 years ago
Windows-PE-Packer preview

Windows-PE-Packer

GitHubczs108/windows-pe-packer

🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
binary-analysisexploitationpayload-generation+1
3671 year ago
ida-efiutils preview

ida-efiutils

GitHubsnare/ida-efiutils

Some scripts for IDA Pro to assist with reverse engineering EFI binaries

binary-analysisembedded-systems-securityfirmware-analysis+2
3097 years ago
Previous1…8910…80Next