
Citrix-Bleed-Buffer-Overread-Demo
 scottzxor/citrix-bleed-buffer-overread-demo
This code functionally approximates the Citrix Bleed vulnerability (CVE-2023-4699).
binary-analysiscode-analysiseducation+2
1
scottzxor/citrix-bleed-buffer-overread-demoThis code functionally approximates the Citrix Bleed vulnerability (CVE-2023-4699).
 george0papasotiriou/cve-2026-22187-bio-formats-unsafe-java-deserialization-via-.bfmemo
Bio-Formats ≤ 8.3.0 performs unsafe Java deserialization of attacker-controlled .bfmemo cache files during image processing; crafted .bfmemo can…
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 johanneslks/cve-2026-32945
PJSIP DNS Compression Pointer Heap OOB Read (Remote DoS)
 satheesh575555/linux-4.1.15_cve-2023-28772
Analyzes and demonstrates the Linux kernel vulnerability CVE-2023-28772, providing a patched or vulnerable kernel source for security research and…
 k0n9-log/cve-2025-60854
D-link AX1500 Vulnerability

 wise-security/cve-2025-69599
Proof-of-concept exploit for CVE-2025-69599, demonstrating uncontrolled search path element in RayVentory Scan Engine's rvia and ndtrack binaries,…
 3dluvr/new-lib3mf.dll-for-meshmixer
Precompiled lib3mf.dll for MeshMixer which includes a backported patch for CVE-2021-21772 and zlib 1.3.1
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 furyutei/cve-2015-0235_ghost
C exploit for the GHOST glibc vulnerability (CVE-2015-0235) enabling remote code execution via buffer overflow in gethostbyname functions.
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 tiran/cve-2018-8970
Demo for https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2018-8970
 leorivass/jq-els-backport-cve-2025-48060
Backported the upstream fix for CVE-2025-48060 (heap buffer overflow in jv_string_empty) to jq 1.6.
 tronciuvlad/cve-2024-26475
An issue in radareorg radare2 v.0.9.7 through v.5.8.6 and fixed in v.5.8.8 allows a local attacker to cause a denial of service via the…
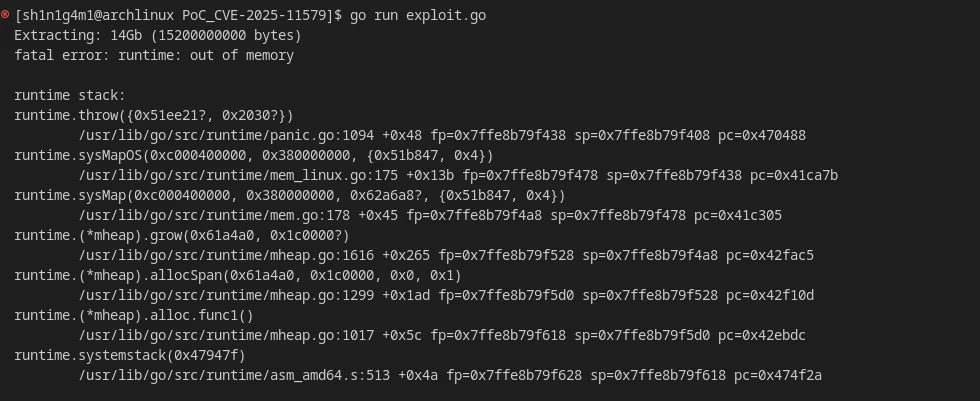 shinigami-777/poc_cve-2025-11579
Proof-of-concept exploit for CVE-2025-11579, a denial-of-service vulnerability in rardecode that triggers an out-of-memory crash via a crafted RAR…
 bilalclicksafe/cve-2025-60595
SPH Engineering UgCS 5.13.0 is vulnerable to Arbitary code execution. This is the public refrence to be used on CVE site