
Archived
path-auditor
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
binary-analysisdynamic-code-analysisexploitation+3
google/path-auditorRuntime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 viper-framework/viper
Binary analysis and management framework
 anerruption/logic.net
A free and open-source .NET obfuscator using dnlib.
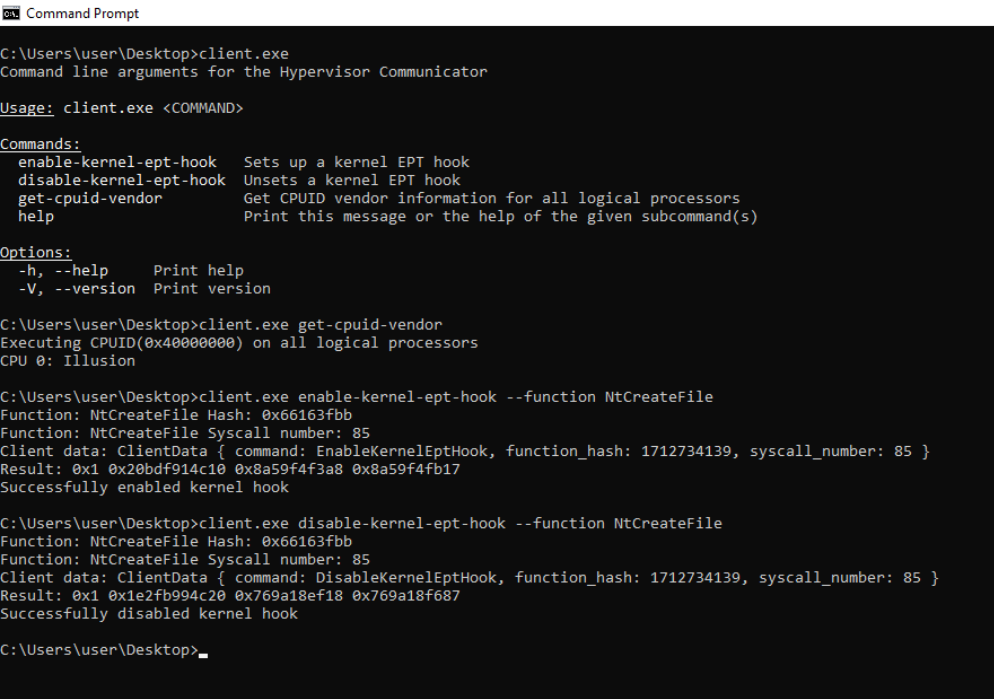 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 adrienthebo/cve-2014-2734
I think this CVE is full of lies and deceit and very confusing code.
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 0xade1a1de/mastik
C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…