
px-vm
 b9ph0met/px-vm
Reverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
anti-botbinary-analysiscryptography+8
557 months ago
b9ph0met/px-vmReverse engineering toolkit for PerimeterX's bytecode VM, featuring a CFG-based disassembler, 5-layer decryption pipeline, opcode table…
 kashithecomfy/comfyengine
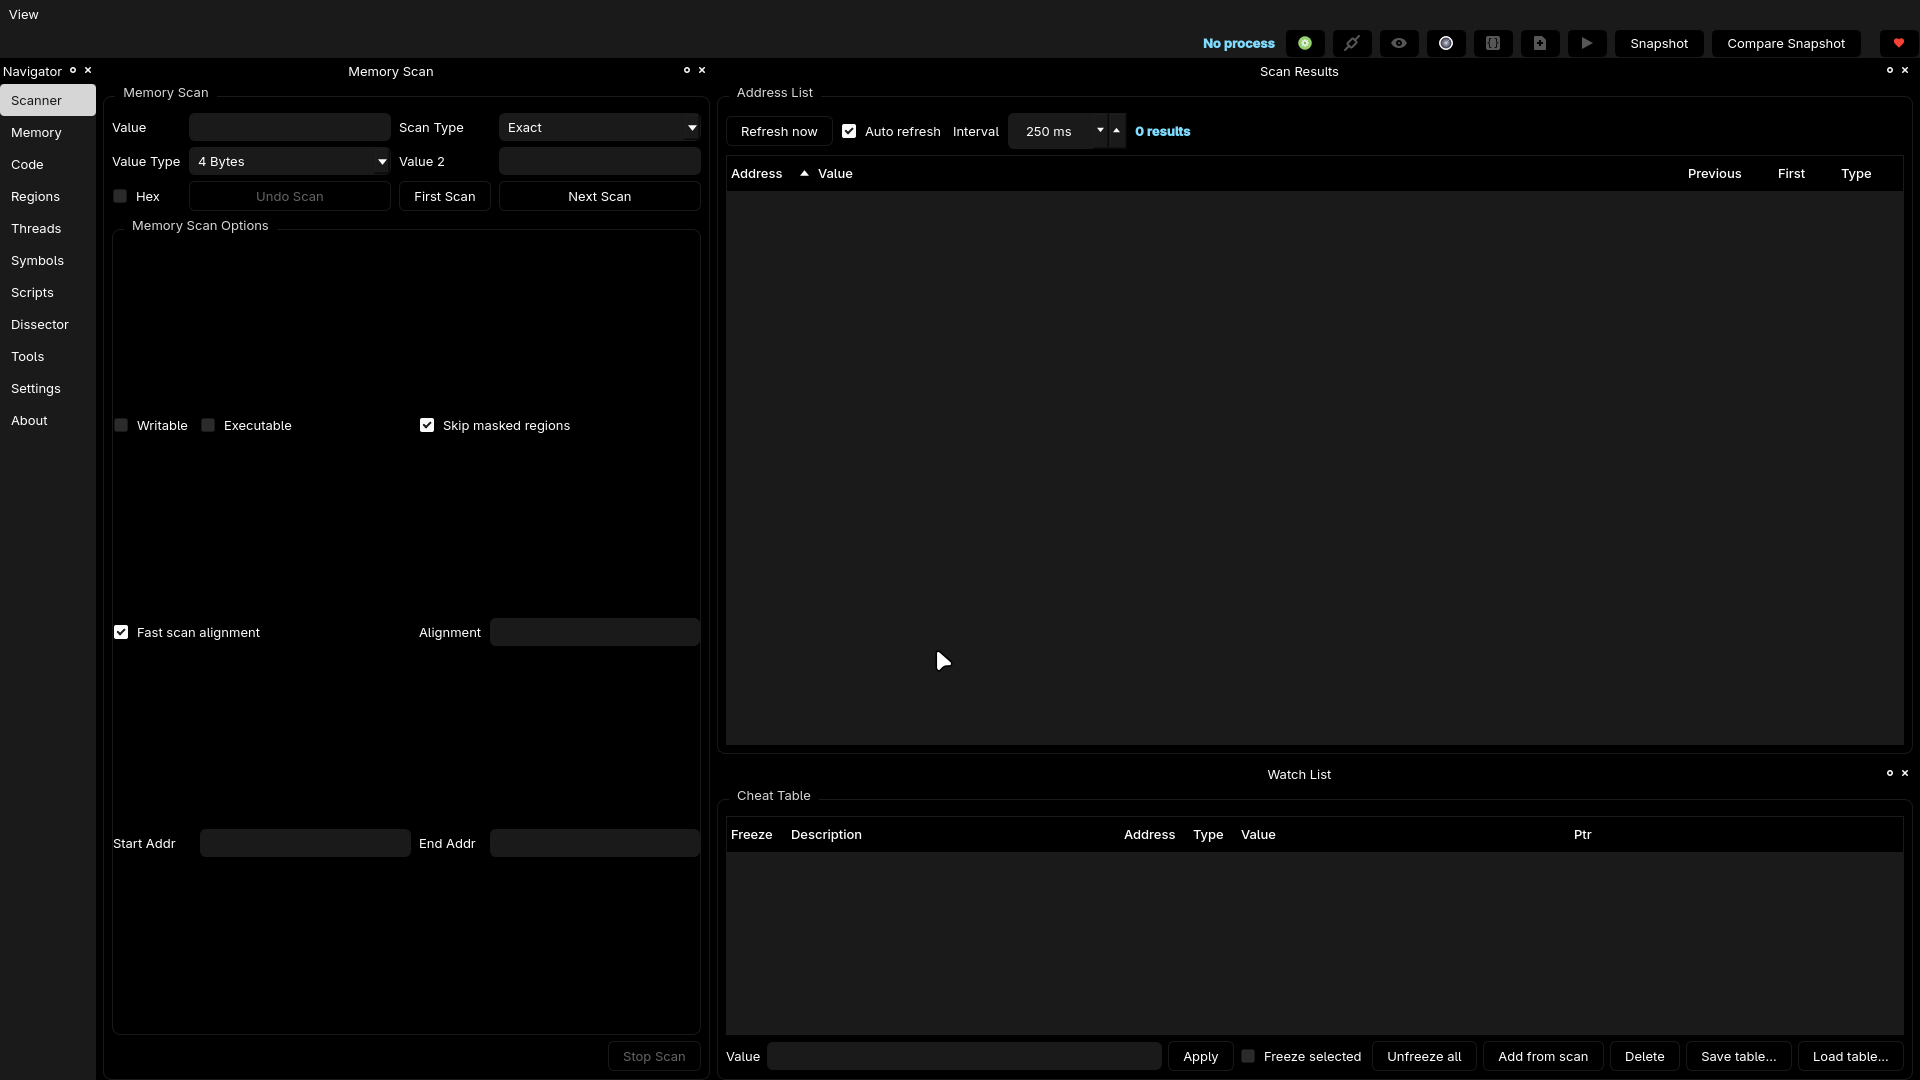
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 zhuowei/cve-2025-27363-proof-of-concept
Proof-of-concept for CVE-2025-27363 demonstrating a heap buffer overflow in FreeType 2.13.0 via a crafted variable font, with ASAN-verified crash…
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 kaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis
Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 jvidhan/autofs-cve-2026-84568
Reverse engineering notes and working PoC for CVE-2026-84568, a macOS automountd trust-boundary violation allowing mounts from localhost or the…
 yonathanpy/cve-2025-65320
CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…
 desmondsanctity/cve-2022-44311
Out-Of-Bounds Read in html2xhtml : CVE-2022-44311
 kpatsakis/cve-2026-36834
Reproducible CVE-2026-36834 proof-of-concept demonstrating an out-of-bounds array read in LibRaw's Panasonic RW2 decoder, with mutation script and…