

unicorn
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.5k
unicorn-engine/unicornUnicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 worawit/blutter
Flutter Mobile Application Reverse Engineering Tool
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 jonathansalwan/triton
Triton is a dynamic binary analysis library. Build your own program analysis tools, automate your reverse engineering, perform software verification…
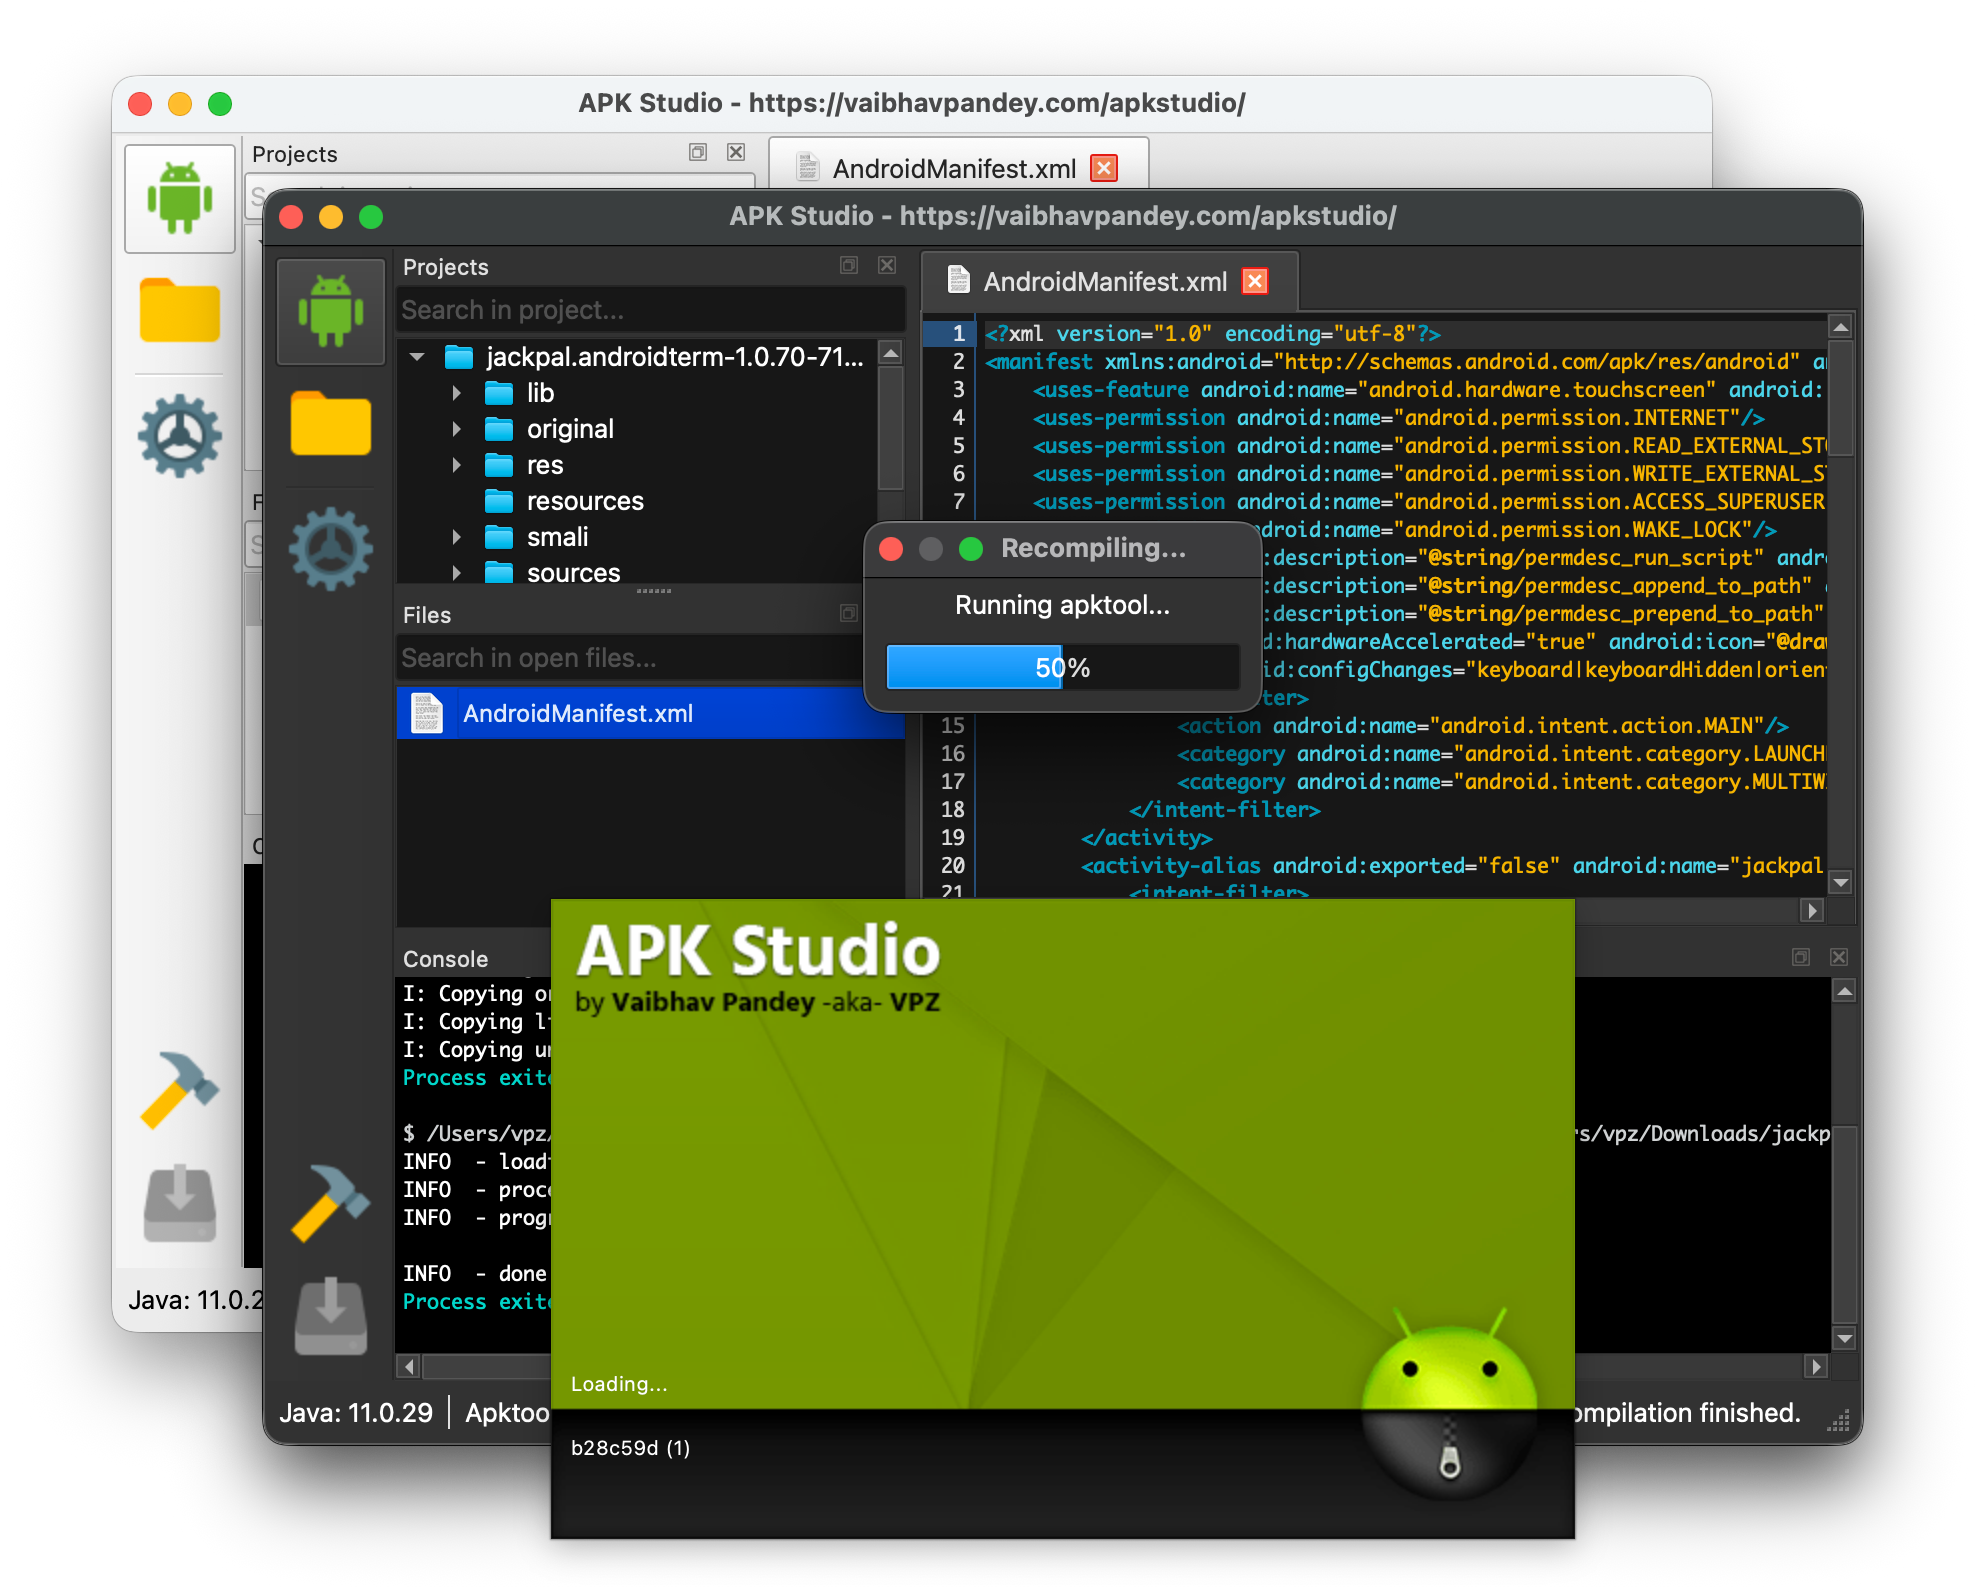 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
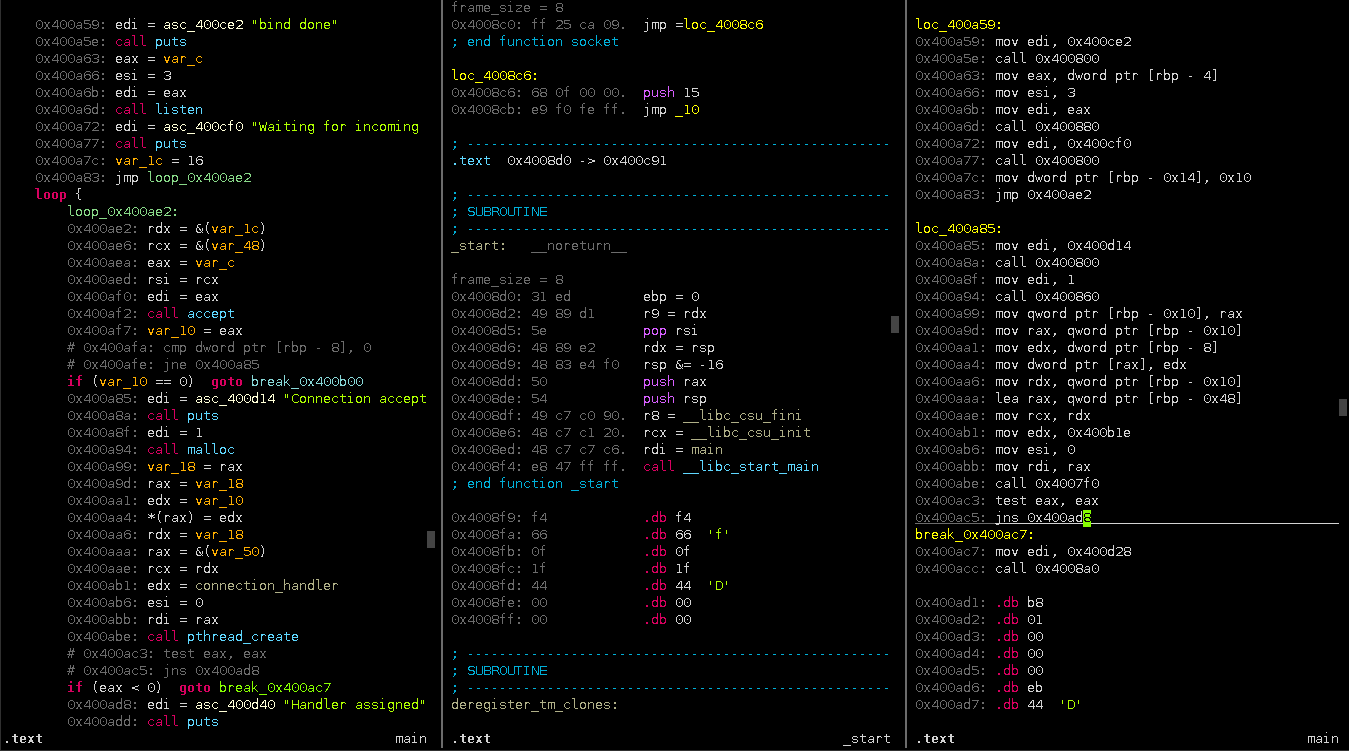 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
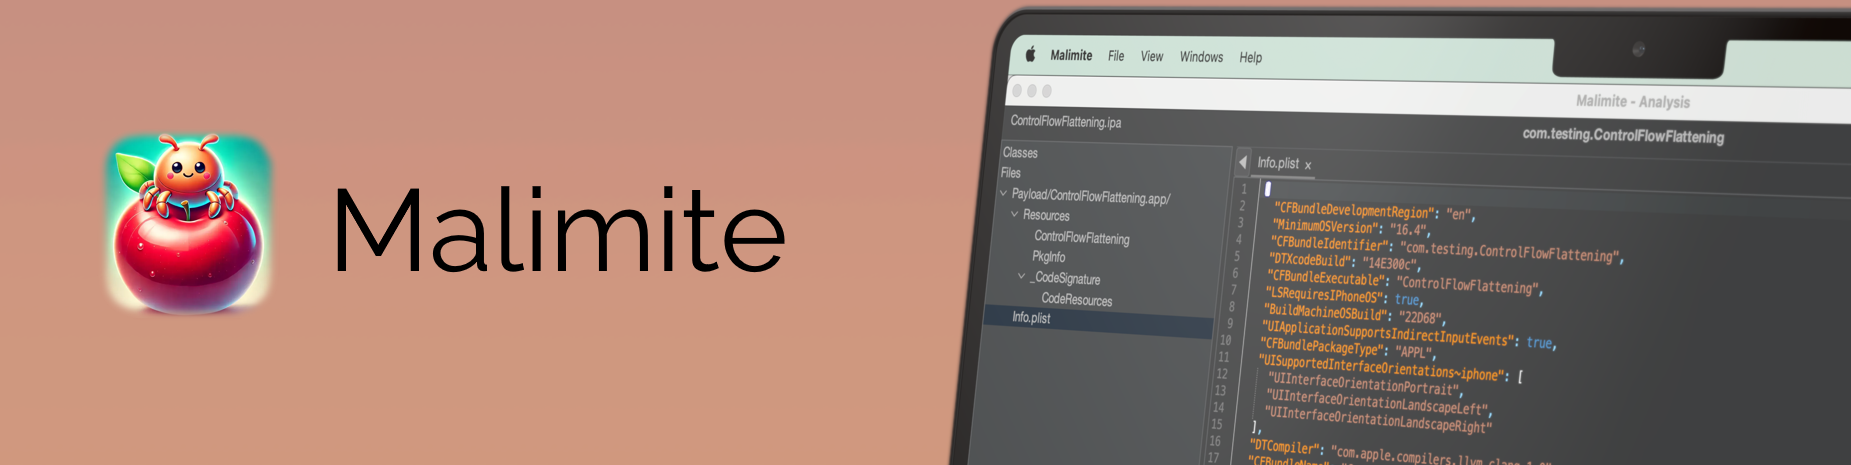 lauriewired/malimite
iOS and macOS Decompiler
 hasherezade/tiny_tracer
Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
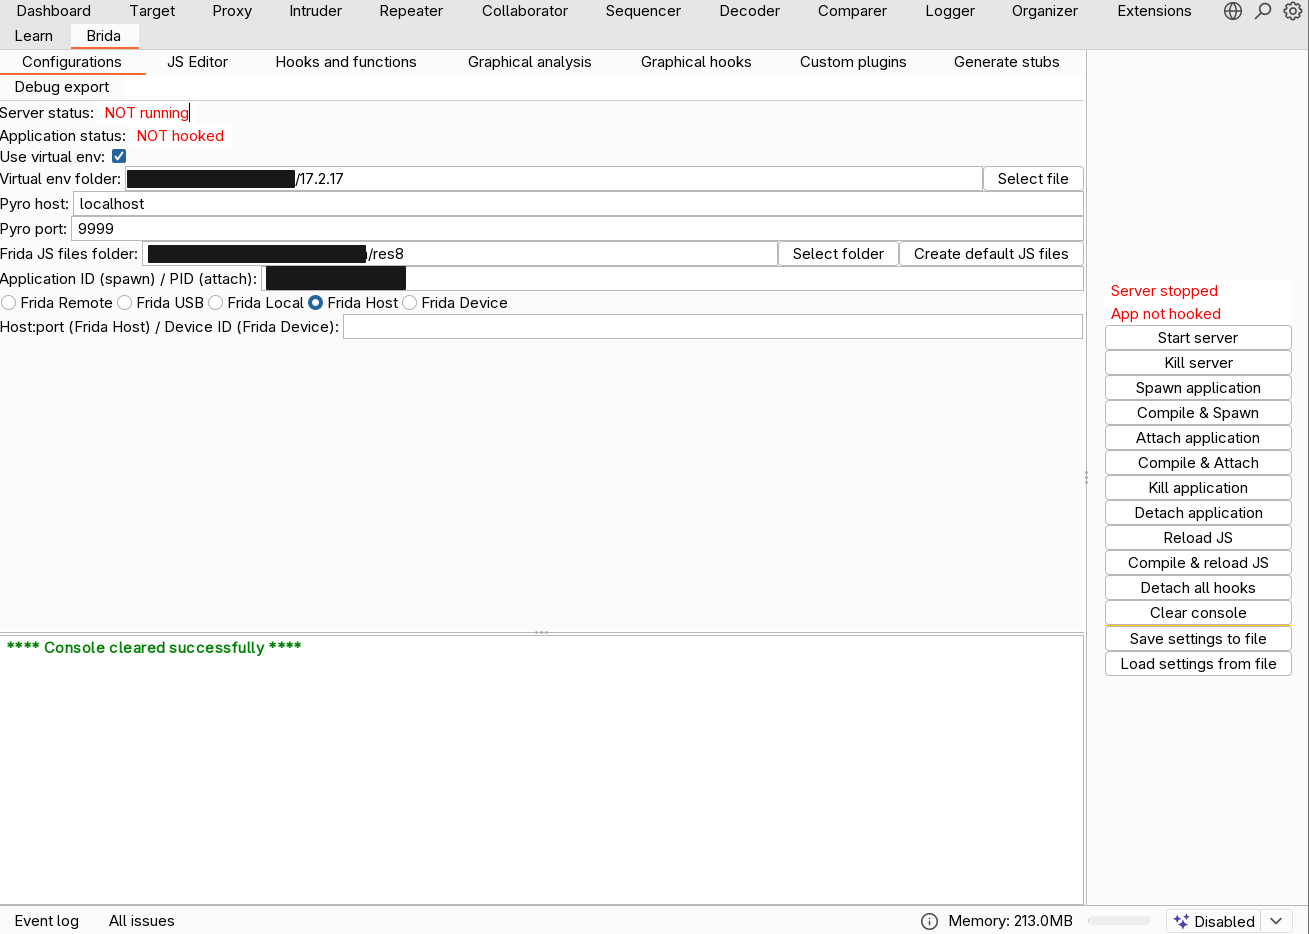 federicodotta/brida
The new bridge between Burp Suite and Frida!
 grammatech/ddisasm
Datalog-based disassembler producing reassemblable assembly from ELF/PE binaries, with GTIRB intermediate representation for binary analysis and…