Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
159 results
Driver-SoulExtraction preview

Driver-SoulExtraction

GitHubgmh5225/driver-soulextraction

SoulExtraction is a windows driver library for extracting cert information in windows drivers
binary-analysismalware-analysisreverse-engineering
243 years ago
file-unpumper preview

file-unpumper

GitHub0x11dfe/file-unpumper

Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
binary-analysismalware-analysisreverse-engineering+1
301 year ago
NOP_Plugin preview

NOP_Plugin

GitHubpandare9x/nop_plugin

Plugin for NOPing instructions in IDA
binary-analysismalware-analysisreverse-engineering
212 years ago
certgraveyard_yara preview

certgraveyard_yara

GitHubtjnel/certgraveyard_yara

Automated YARA rule generation from the Cert Central compromised certificate database.
binary-analysisdefensive-toolsforensics+2
153 days ago
eps-CVE-2017-0261 preview

eps-CVE-2017-0261

GitHubkcufid/eps-cve-2017-0261

Analysis and PoC exploit for EPS vulnerability CVE-2017-0261, including IDA disassembly, intermediate documents, and original exploit files.
binary-analysisexploitationmalware-analysis+2
107 years ago
xz-cve-2024-3094 preview

xz-cve-2024-3094

GitHub0xlane/xz-cve-2024-3094

XZ Backdoor Extract(Test on Ubuntu 23.10)
binary-analysisexploitationforensics+3
172 years ago
NeuroCore preview

NeuroCore

GitHubfarukalpay/neurocore

NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
binary-analysisdigital-forensicsforensics+3
289 months ago
deobf-Arxan-Deob-C preview

deobf-Arxan-Deob-C

GitHubgmh5225/deobf-arxan-deob-c

Simple C program to quickly deobfuscate windows executables protected with Arxan.
binary-analysisdefensive-toolsmalware-analysis+1
153 years ago
Icedid-file-decryptor preview

Icedid-file-decryptor

GitHubembee-research/icedid-file-decryptor

Static Decryptor for IcedID Malware
binary-analysiscryptographymalware-analysis+2
184 years ago
agent preview

agent

GitHubbinref/agent

Language Model Agent Instructions for Binary Refinery
ai-assisted-reversingbinary-analysismalware-analysis+2
1322 days ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex
binary-analysisforensicsmalware-analysis+3
1910 months ago
zeek-elf preview

zeek-elf

GitHubcorelight/zeek-elf

A Zeek ELF File Analyzer
binary-analysisintrusion-detectionmalware-analysis+2
92 years ago
sc2elf preview

sc2elf

GitHubdump-guy/sc2elf

Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF

binary-analysismalware-analysisreverse-engineering+1
103 years ago
Driver-HideKernelThread-IoCancelIrp preview

Driver-HideKernelThread-IoCancelIrp

GitHubgmh5225/driver-hidekernelthread-iocancelirp

Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…
binary-analysisdefensive-toolsmalware-analysis+1
94 years ago
zombieguard preview

zombieguard

GitHubmdshoaibuddinchanda/zombieguard

ML-based detection of Zombie ZIP archive header evasion attacks (CVE-2026-0866)
binary-analysisdefensive-toolsmachine-learning+4
529 days ago
BiBi-Windows-Wiper-Analysis preview

BiBi-Windows-Wiper-Analysis

GitHubknight0x07/bibi-windows-wiper-analysis

Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
binary-analysisdigital-forensicsincident-response+3
92 years ago
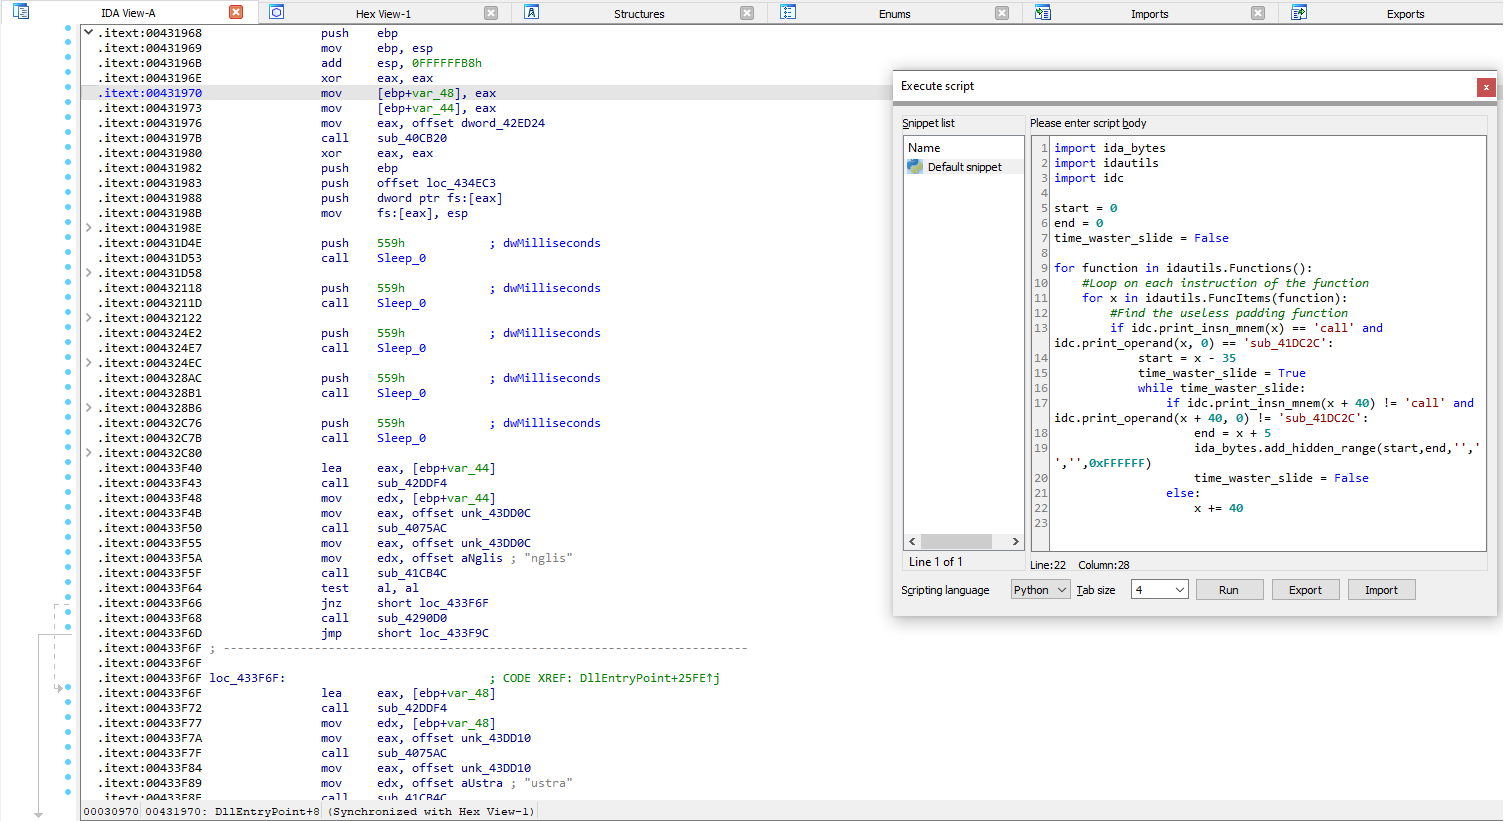
astaroth-deobfuscator preview

astaroth-deobfuscator

GitHubdodo-sec/astaroth-deobfuscator

IDA python script for deobfuscating Astaroth/Guildma injector DLL
binary-analysismalware-analysisreverse-engineering+1
83 years ago
CVE-2018-8090 preview

CVE-2018-8090

GitHubkernelm0de/cve-2018-8090

DLL Hijacking in Quickheal Total Security/ Internet Security/ Antivirus Pro (Installers)

binary-analysisexploitationmalware-analysis+2
38 years ago
Previous1…789Next